 zerodayevil/cve-2026-20817
Repository dedicated to CVE-2026-20817, providing vulnerability details and exploitation material for this specific security flaw.

🛡️ AI Security Tool Module
CVE-2026-20817: Windows Error Reporting (WER) ALPC Local Privilege Escalation
Official Security Audit & Exploitation Module for AI Security Tool Ecosystem





🌐 Web Demo • 📚 Project Website • 💬 Community Chat
Website Navigation: Home • Updates • Downloads • Modules
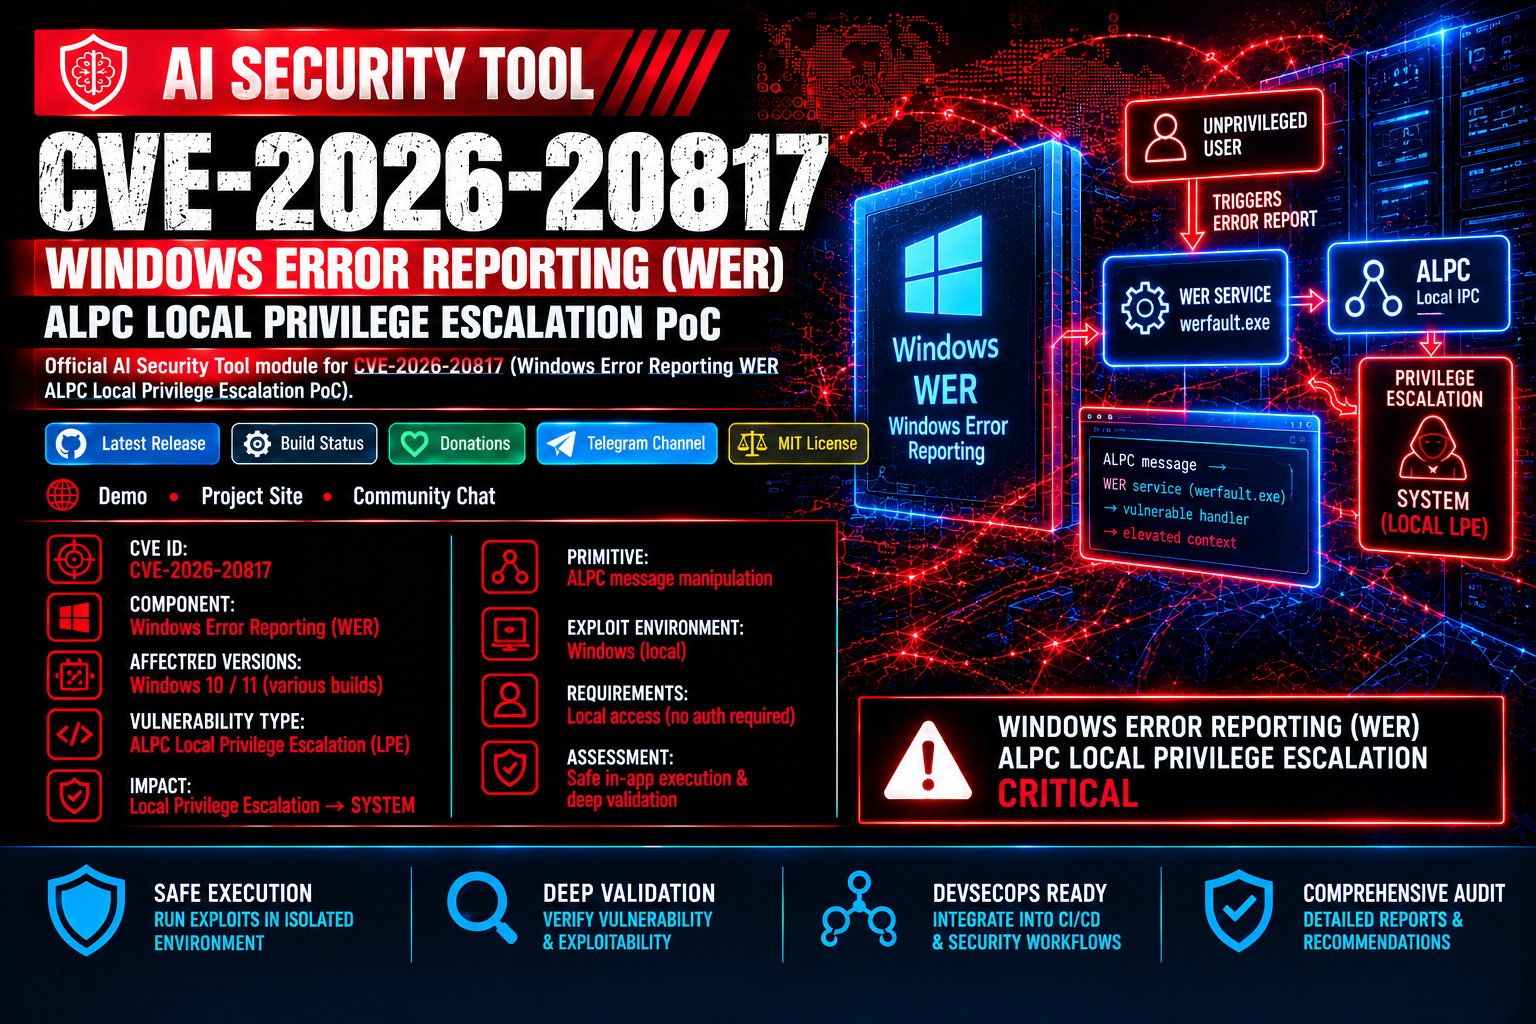
This module provides diagnostic tools and a Proof-of-Concept (PoC) for CVE-2026-20817, a local privilege escalation vulnerability in the Windows Error Reporting (WER) service. The vulnerability allows an authenticated low-privileged user to execute arbitrary code with SYSTEM privileges by sending specially crafted ALPC messages to the WER service.



| Specification | Assigned Value | Notes |
|---|---|---|
| CVE Identifier | CVE-2026-20817 |
Windows Error Reporting ALPC LPE |
| Component | Windows Error Reporting (WER) Service | ALPC port \WindowsErrorReportingService |
| Attack Vector | Local (ALPC) | Authenticated low-privileged user |
| Vulnerable Method | SvcElevatedLaunch (0x0D) |
Fails to validate caller privileges before launch |
| Impact & Vector | Elevation to SYSTEM | Executes WerFault.exe with user-supplied command line |
| Affected Systems | Windows 10/11 & Server 2019/2022 | All versions prior to January 2026 Security Update |
The WER service exposes an ALPC port named \WindowsErrorReportingService. The flaw exists in the SvcElevatedLaunch method (0x0D), where the service fails to properly validate the caller's privileges before launching WerFault.exe with user-supplied command line parameters from shared memory.
0x0D, including client process ID, shared memory handle, and command line length.WerFault.exe with the provided command line.The spawned WerFault.exe process runs with a SYSTEM token containing:
Note: The token does NOT include
SeTcbPrivilege(Act as part of the operating system).
# Using Visual Studio Developer Command Prompt (C++17)
cl /EHsc CVE-2026-20817_PoC.cpp⚠️ IMPORTANT: This module is built specifically for safe execution and diagnostics within the AI Security Tool ecosystem. Always use verified modules sourced from official repositories.
To execute the monitoring and diagnostic scripts, ensure the AI Security Tool core engine is installed either via pre-built binaries or by building from source:
