
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
23 results
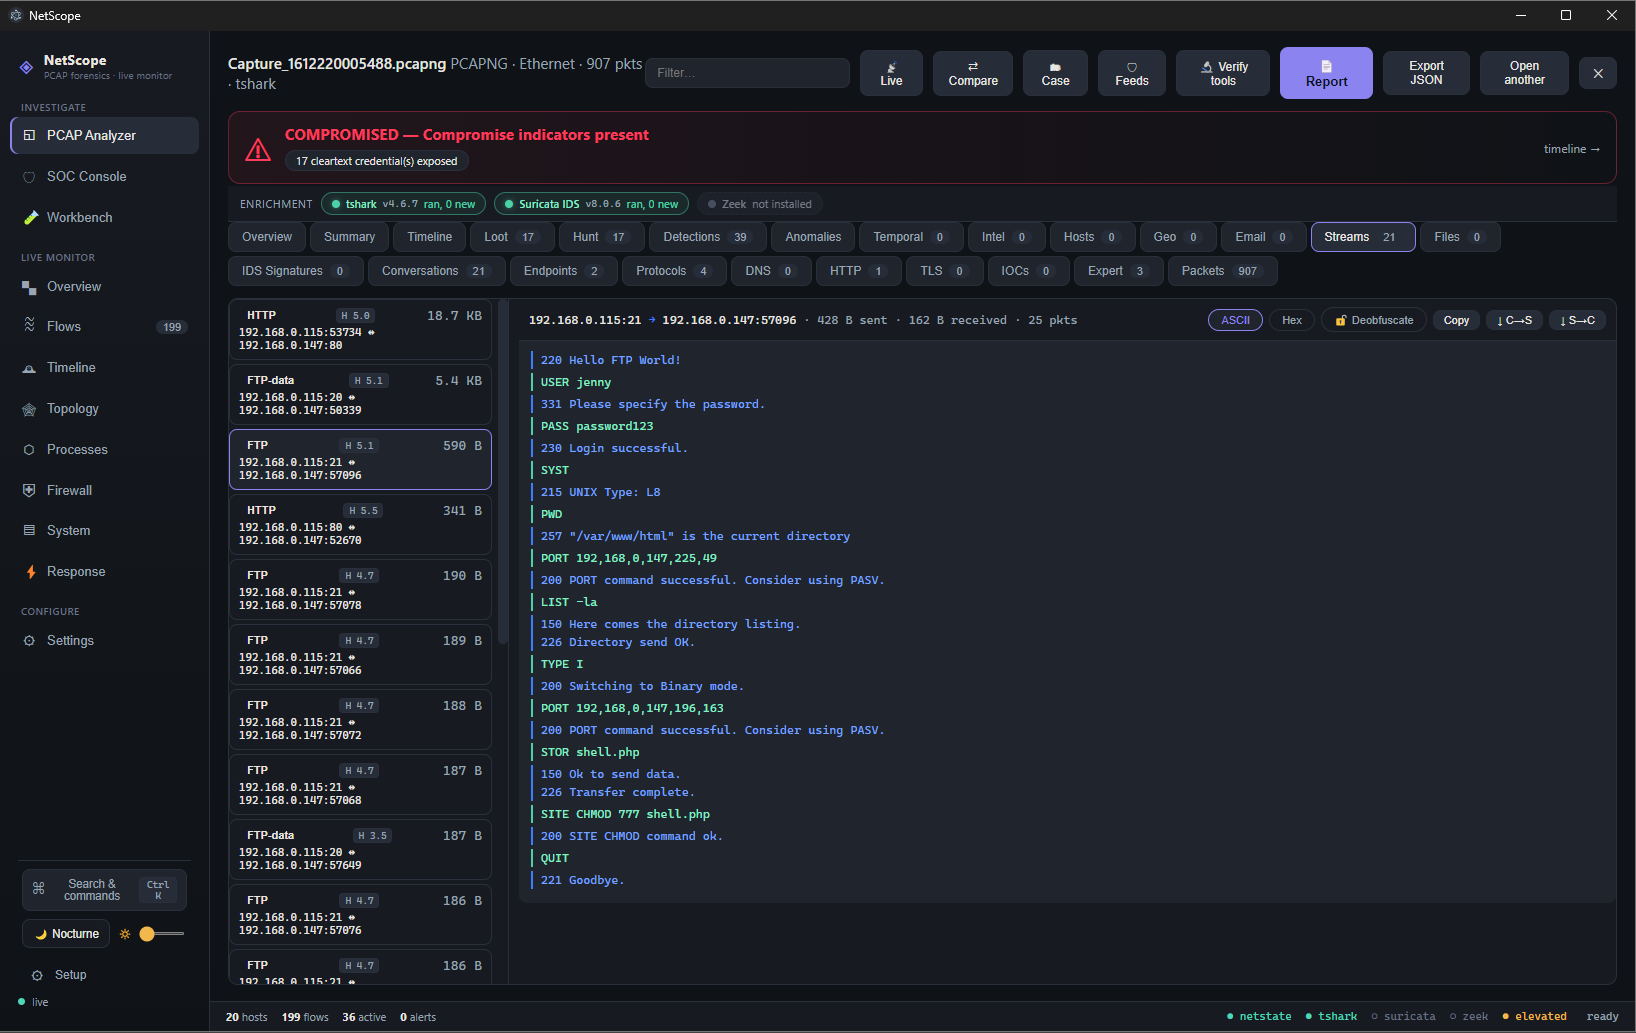
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
anomaly-detectiondigital-forensicsincident-response+5
3
1 month ago
fatt preview

fatt

GitHub0x4d31/fatt

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
network-forensicspacket-sniffing-analysisthreat-intelligence
6854 years ago
gopassivedns preview

gopassivedns

GitHubphillipmartin/gopassivedns

Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…
dns-analysisinformation-gatheringnetwork-security+2
1267 months ago
PortDog preview

PortDog

GitHubpuniaze/portdog

Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
anomaly-detectiondefensive-toolsintrusion-detection+3
13411 years ago
pacmap preview

pacmap

GitHubm0vi0/pacmap

Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
dns-analysisforensicsincident-response+4
1320 days ago
netsentryx preview

netsentryx

GitHubaman-sharma-dev/netsentryx

An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
anomaly-detectioncloud-securitydefensive-tools+6
1 month ago
rustnet preview

rustnet

GitHubdomcyrus/rustnet

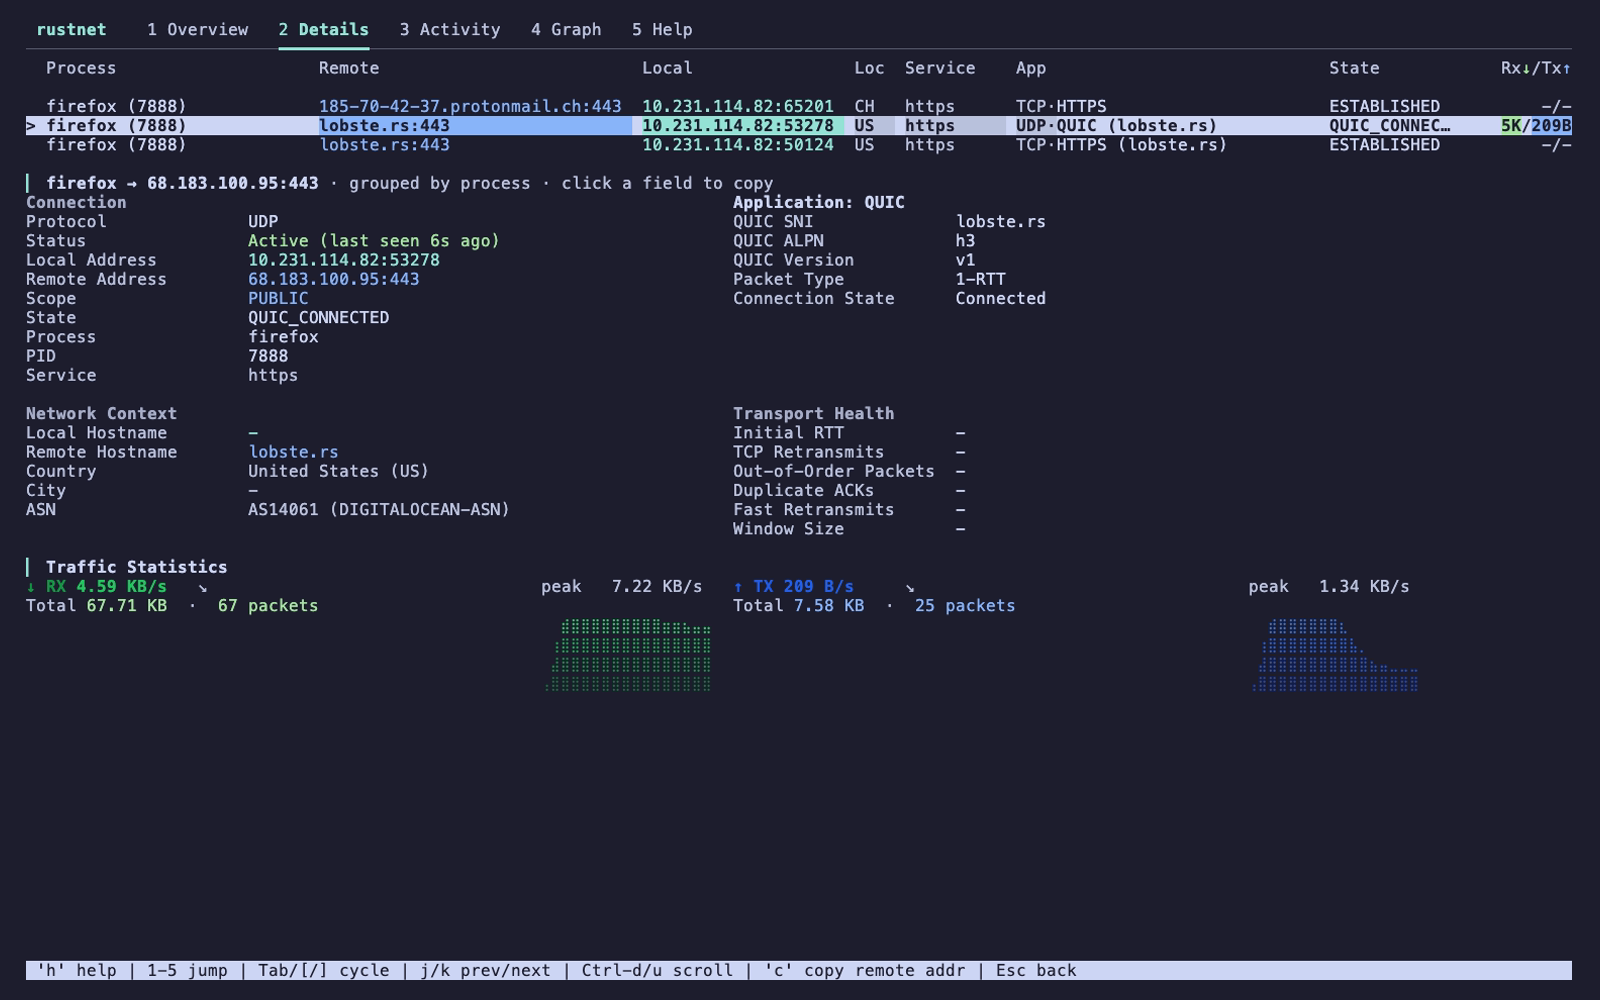
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
cloud-securitycontainer-securitydns-analysis+5
5.1k12h 10m ago
tpotce preview

tpotce

GitHubtelekom-security/tpotce

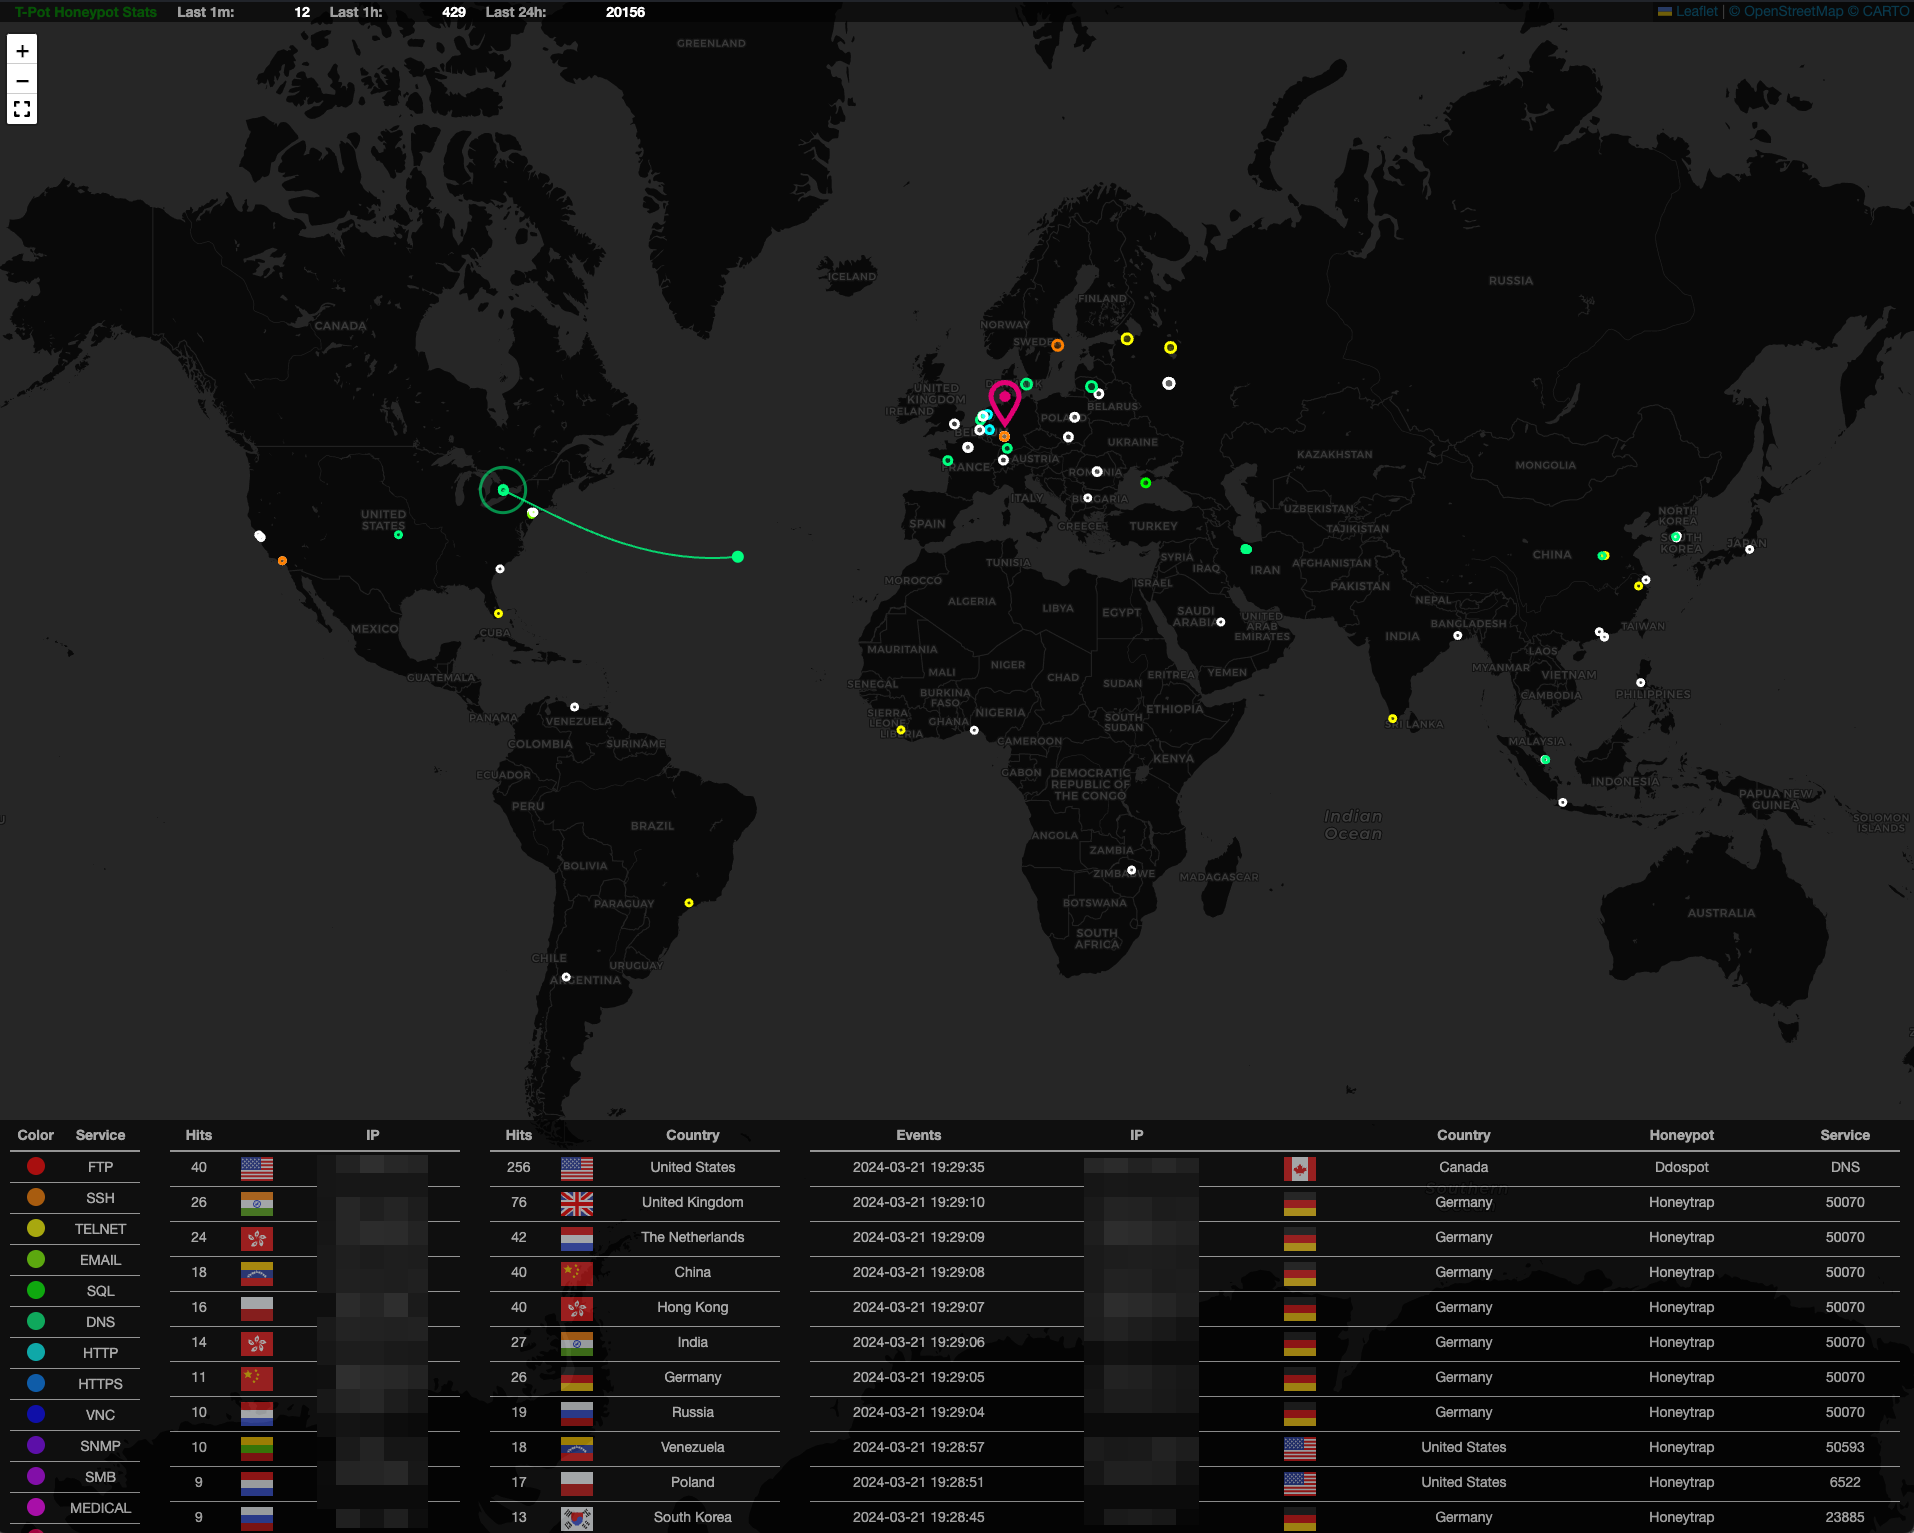
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
9.5k1 day ago
PCredz preview

PCredz

GitHublgandx/pcredz

This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
forensicsinformation-gatheringnetwork-security+3
2.6k6 months ago
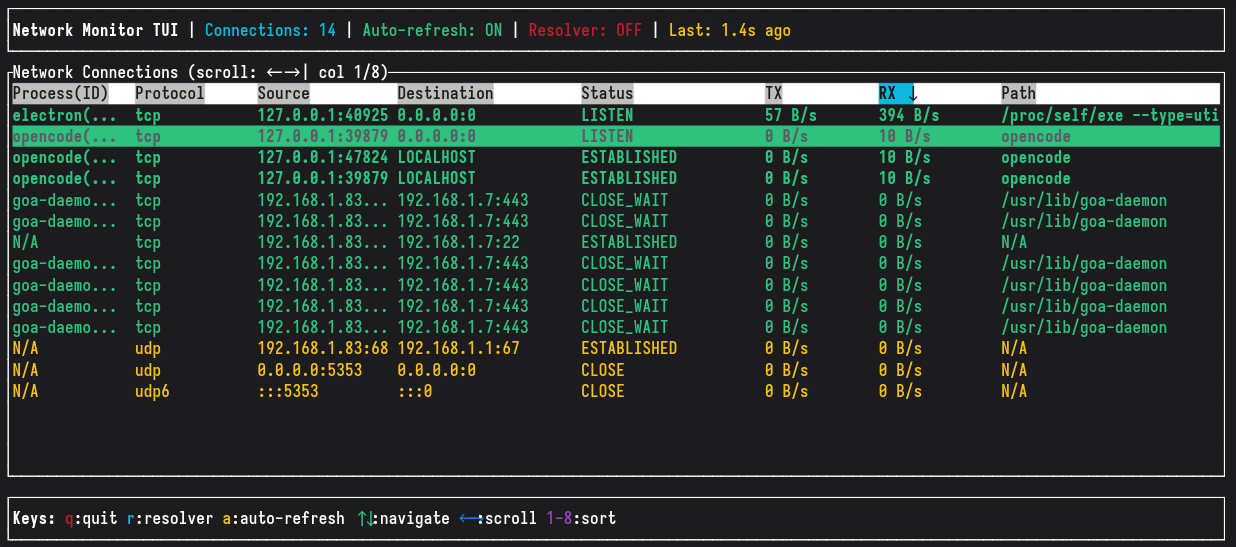
network-monitor preview

network-monitor

GitHubgrigio/network-monitor

A real-time network connection monitoring tool built with Rust and GTK4, displaying active connections with live I/O statistics in a modern graphical…
general-purpose-utilitiesinformation-gatheringnetwork-mapping+2
3134 days ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1024 years ago
airpydump preview

airpydump

GitHubhash3lizer/airpydump

Analyze Wireless Packets on the fly. Currently supporting three working Modes (Reader, Live, Stealth)
information-gatheringnetwork-securitypacket-sniffing-analysis+1
538 years ago
usbsnoop preview

usbsnoop

GitHubyeet-src/usbsnoop

Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
debuggersdynamic-analysis-sandboxingembedded-systems-security+7
871 month ago
airtop preview

airtop

GitHubyeet-src/airtop

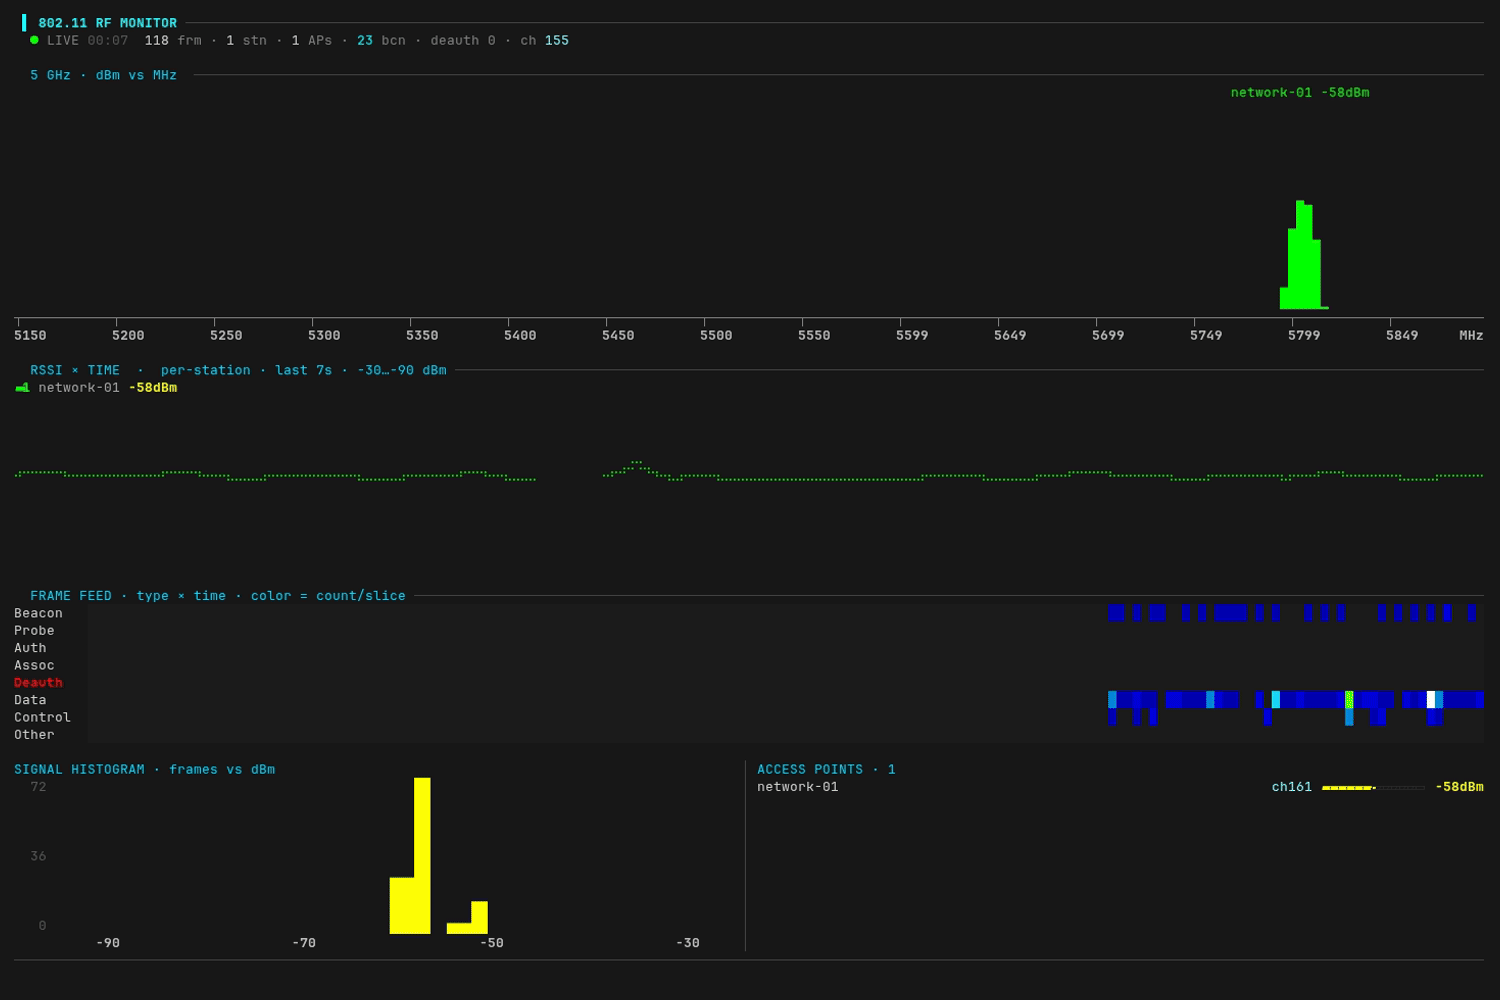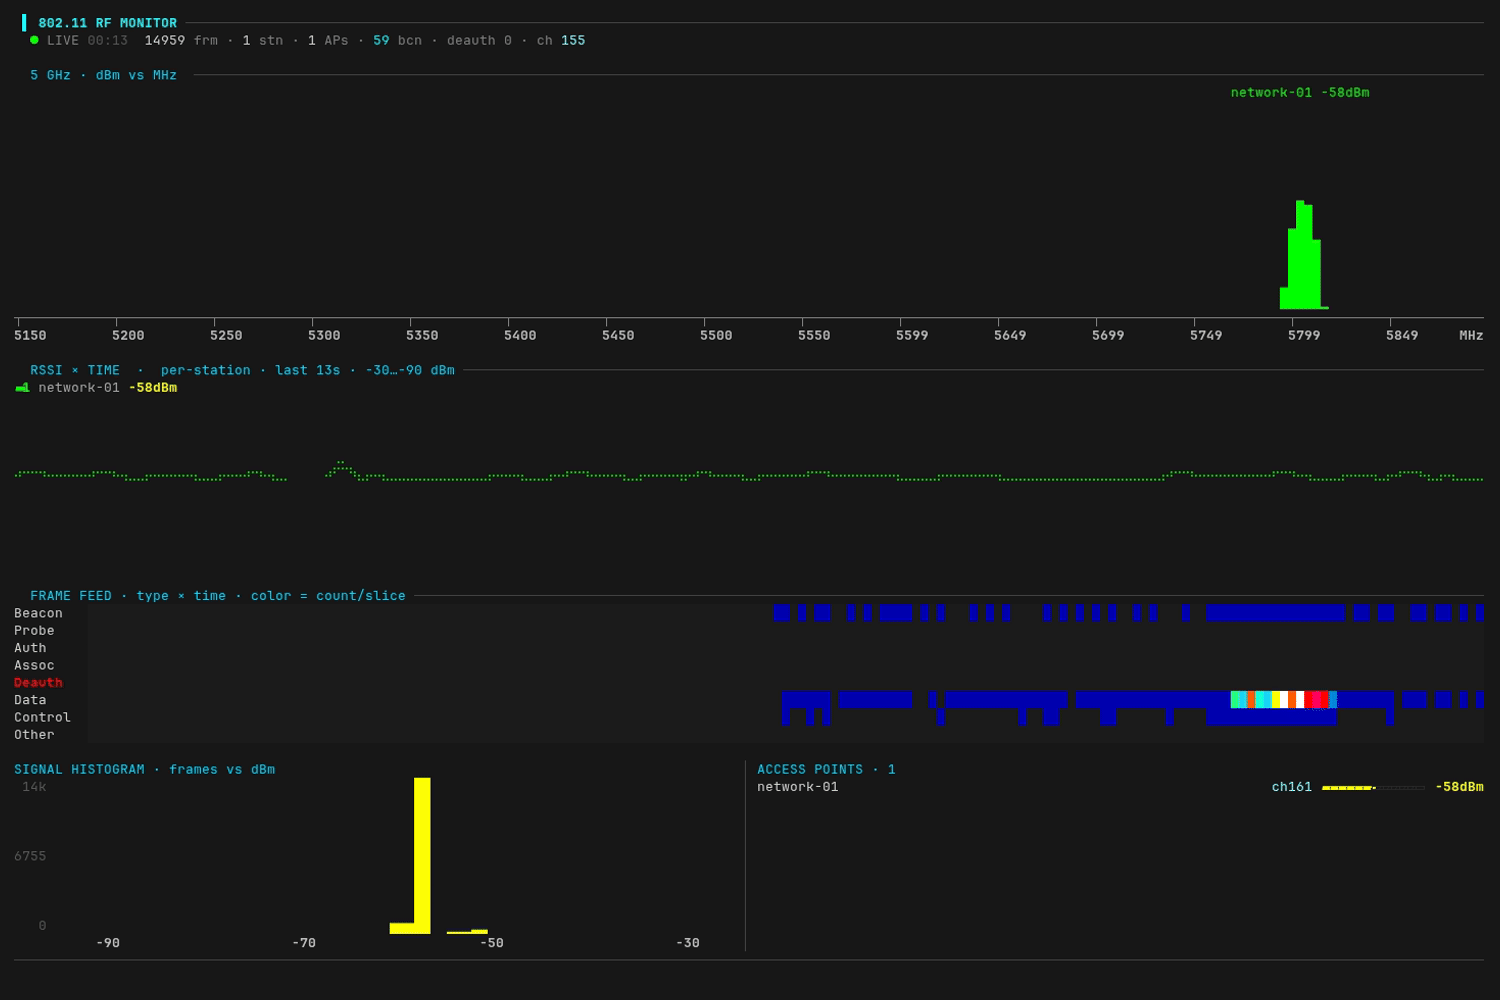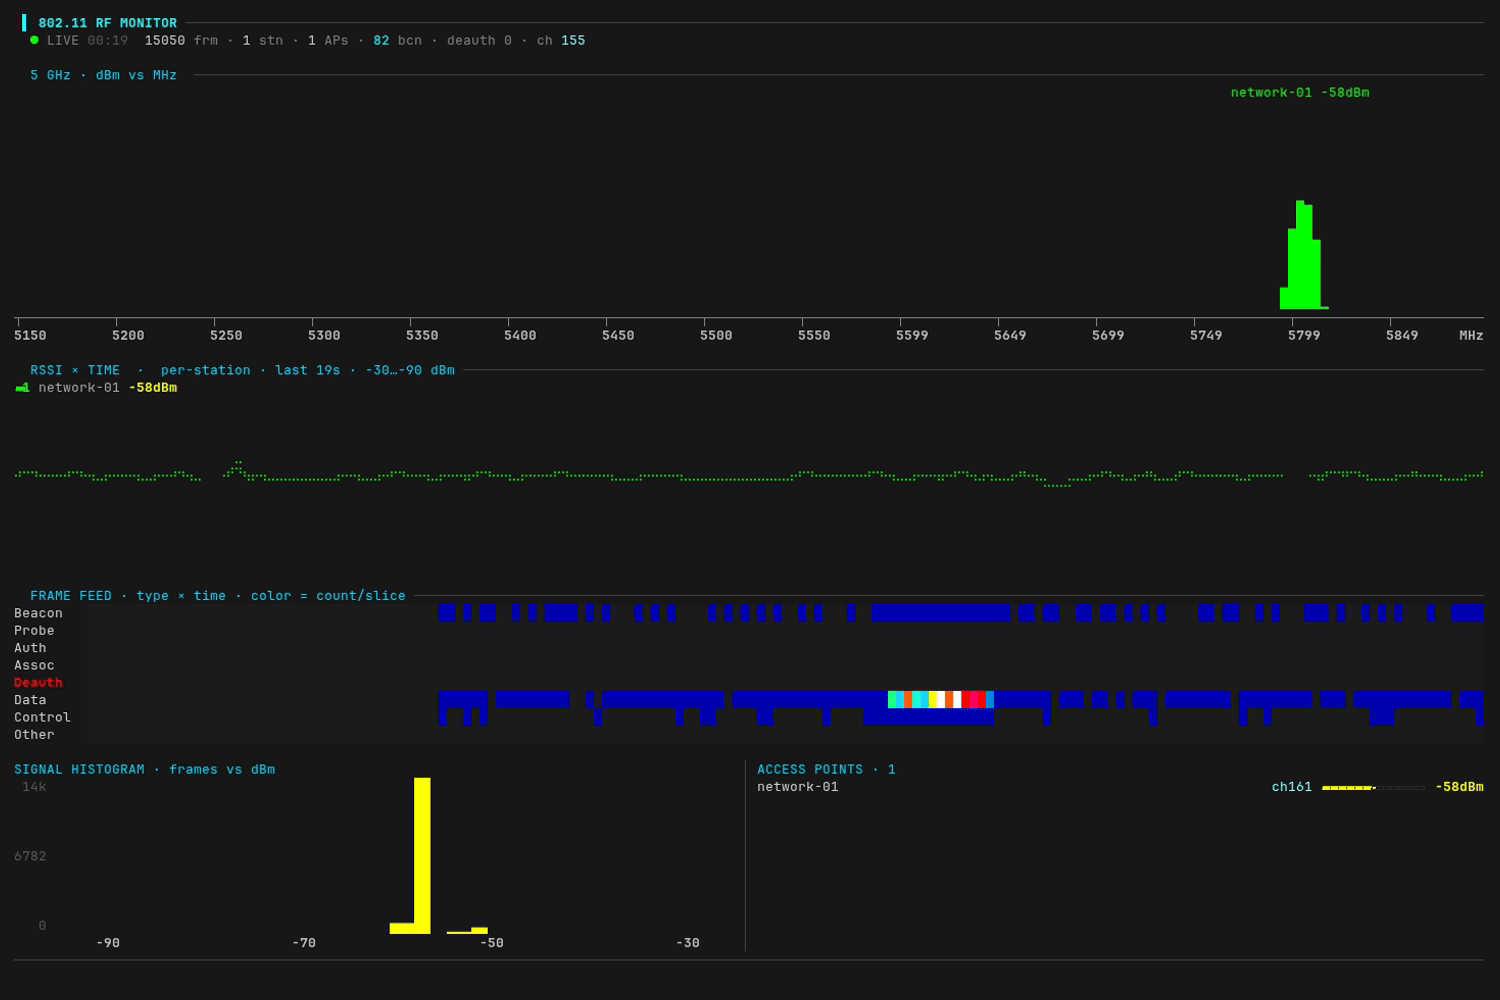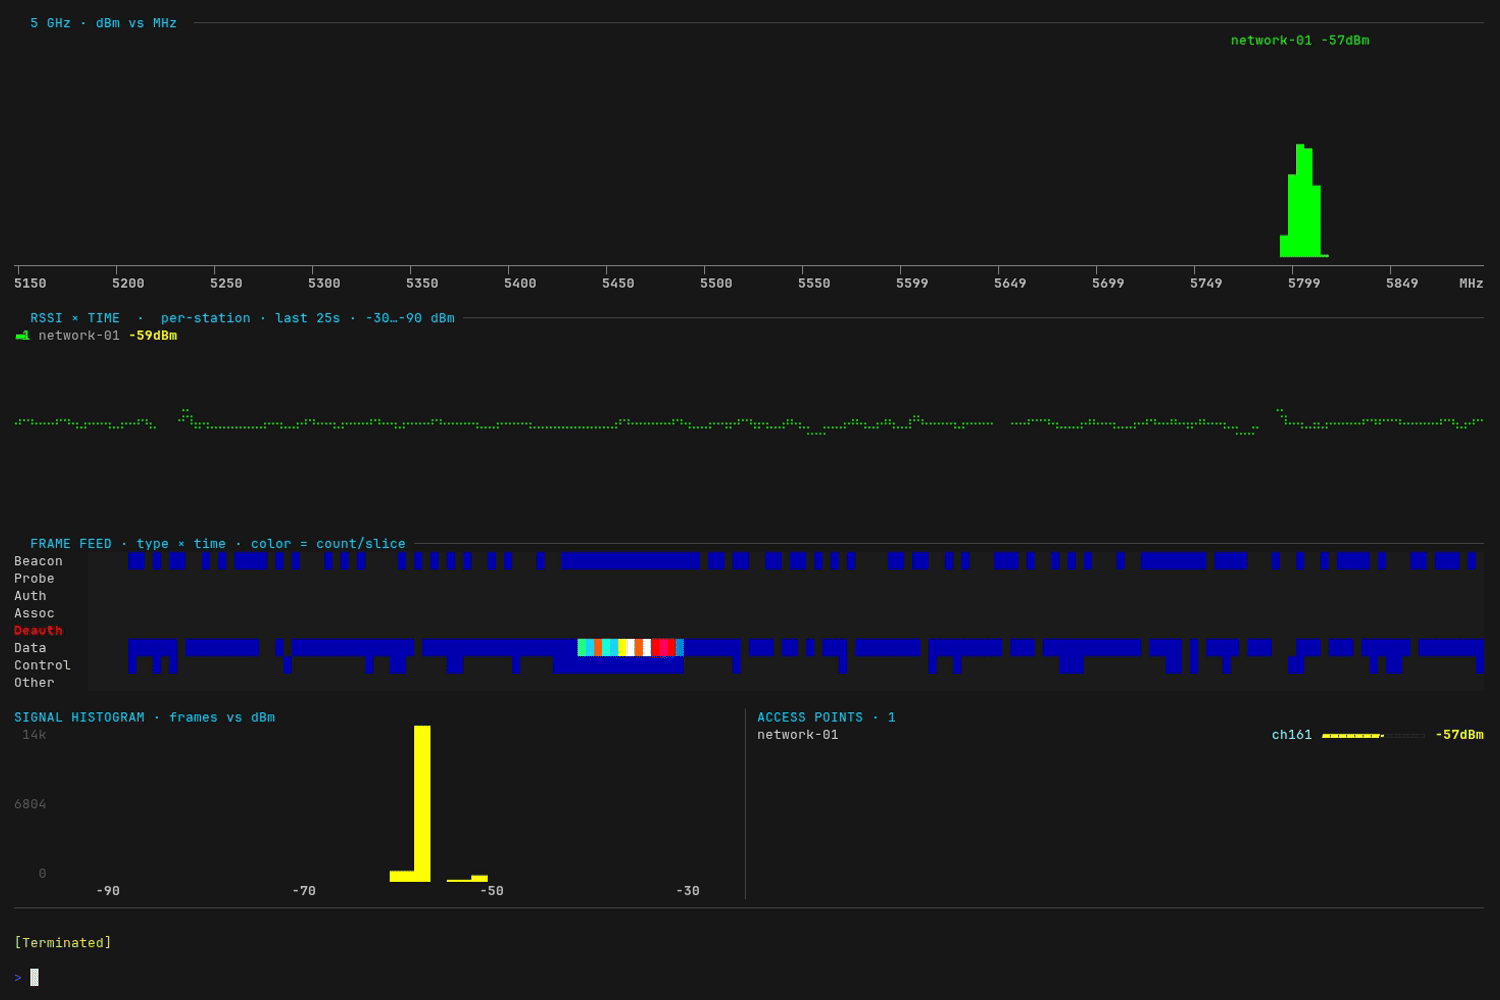
htop for the airwaves — a live 802.11 (Wi-Fi) RF dashboard in your terminal

dns-analysisinformation-gatheringpacket-sniffing-analysis+2
5925 days ago
NetworkAlarm preview

NetworkAlarm

GitHubyojiwatanabe/networkalarm

A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…

ids-ips-evasionintrusion-detectionnetwork-security+2
218 years ago
vm-homelab-log4shell-assessment preview

vm-homelab-log4shell-assessment

GitHubyili-soc/vm-homelab-log4shell-assessment

Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…

educationexploitationintrusion-detection+7
1 month ago
Network-Detection-Engine preview

Network-Detection-Engine

GitHubsiddharth2440/network-detection-engine

Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…

anomaly-detectionintrusion-detectionnetwork-security+3
16 months ago
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

ai-securitycloud-infrastructure-securitycloud-security+9
12.1k1 day ago
Previous12Next