

creds.py
 danmcinerney/creds.py
Harvest FTP/POP/IMAP/HTTP/IRC creds
information-gatheringnetwork-securityosint+3
danmcinerney/creds.pyHarvest FTP/POP/IMAP/HTTP/IRC creds
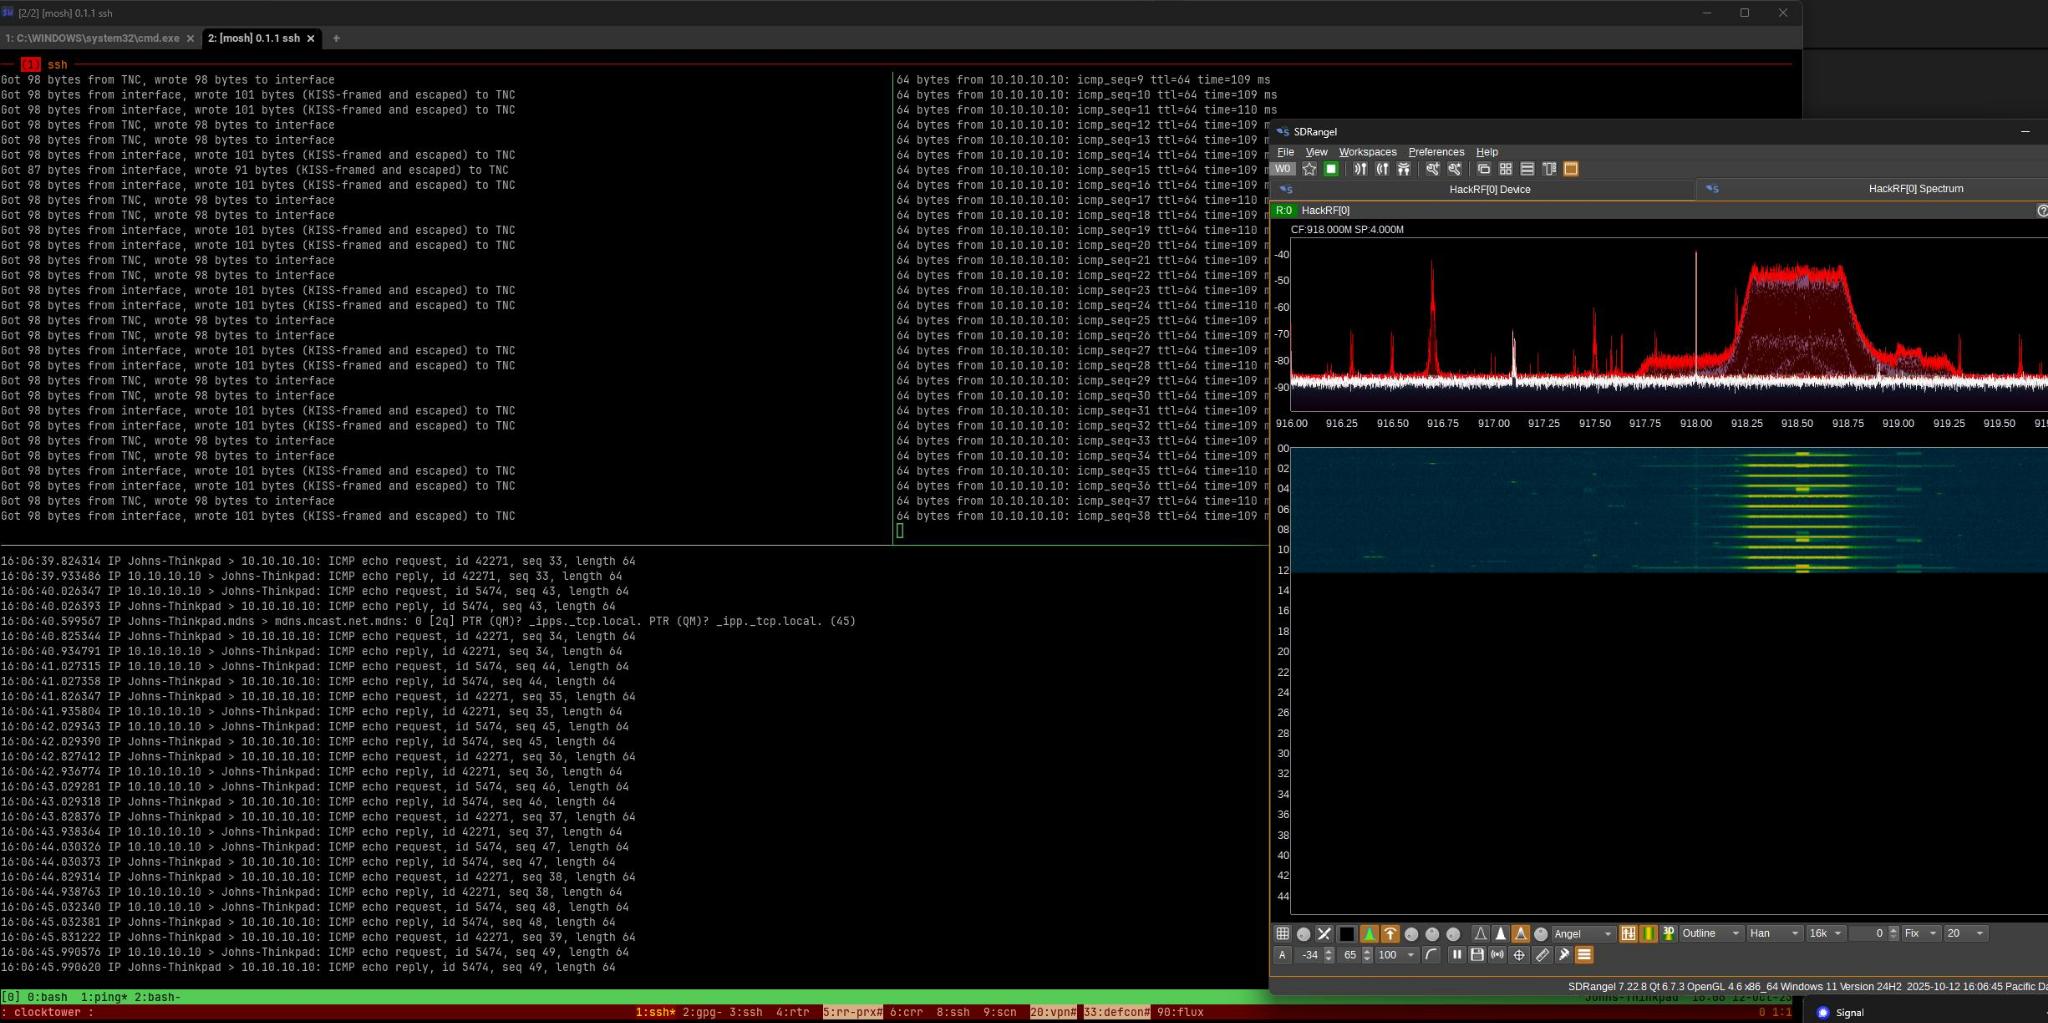 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
 adamlaurie/hdmi-sniff
sniff HDMI DDC (I2C) traffic
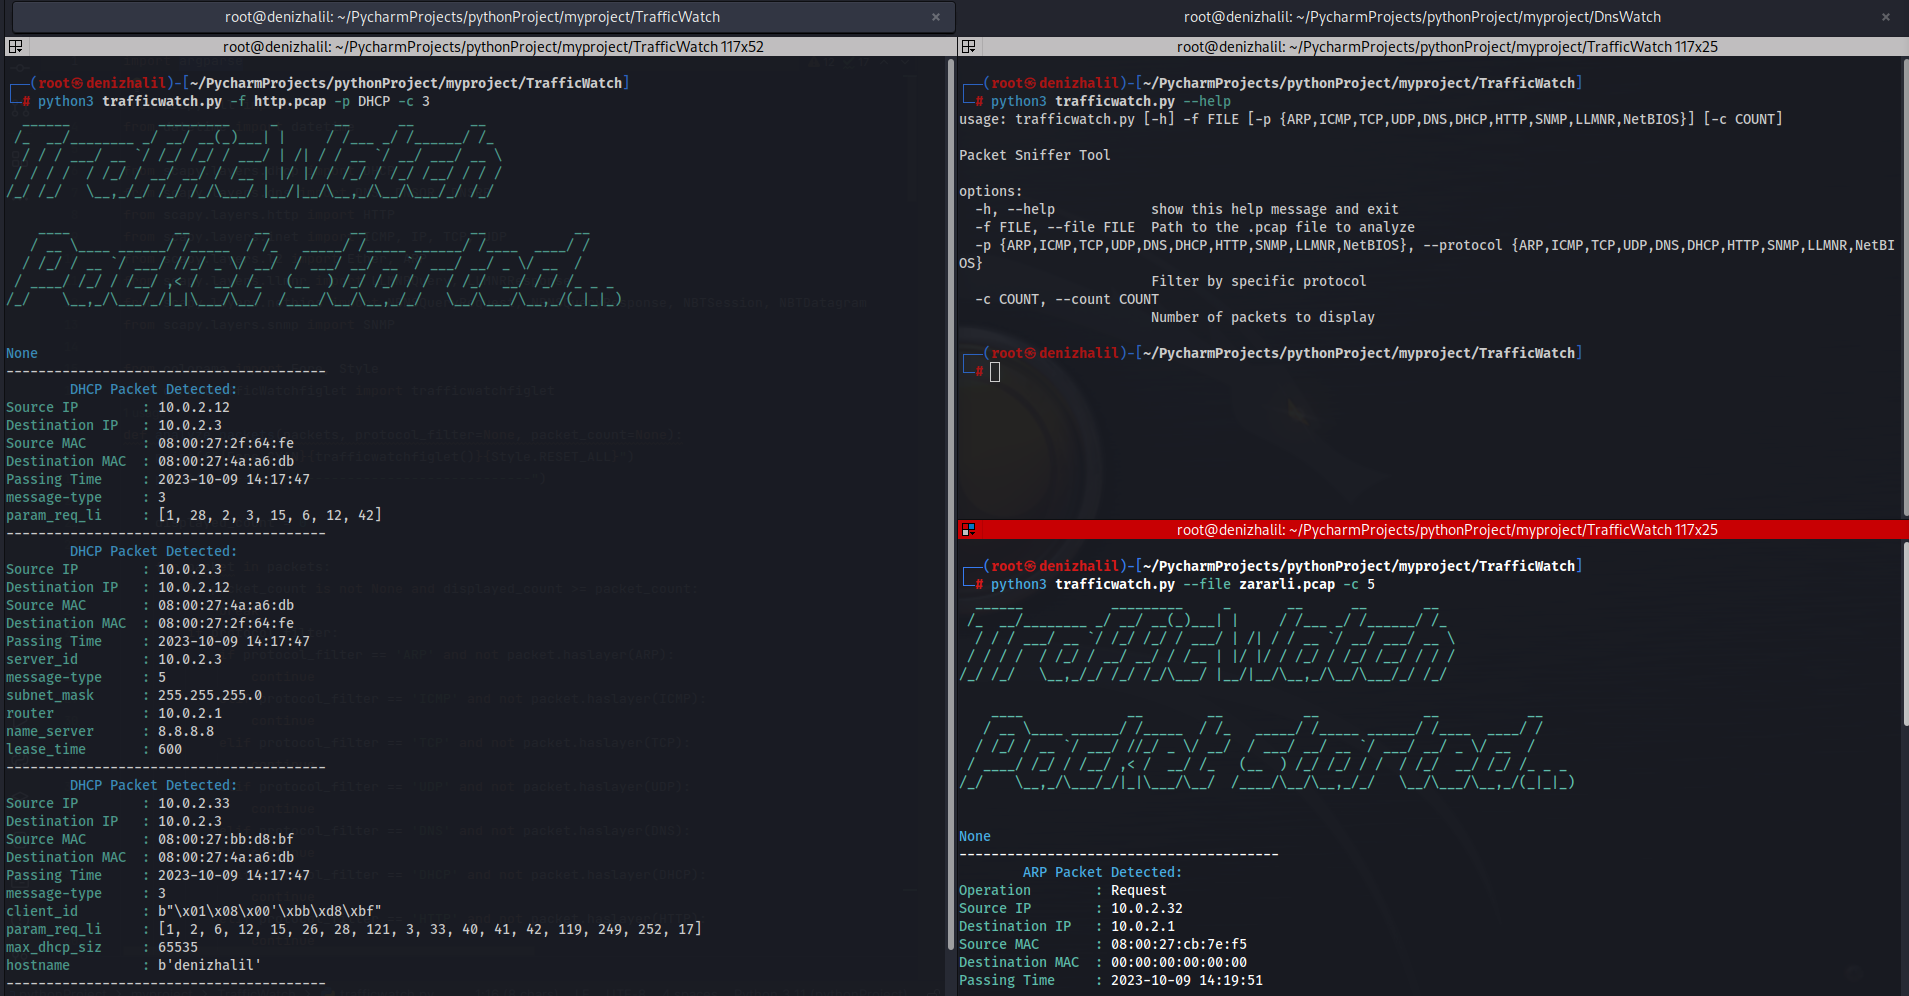 halildeniz/trafficwatch
PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
 unixpickle/cve-2018-4407
Crash macOS and iOS devices with one packet
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
 arax-zaeimi/docker-container-cve-2020-13401
Study on CVE-2020-13401 vulnerability of containers in dockers older than 19.03.11
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 mretallack/dronecamera
Drone HASAKEE FPV video app for Android
 xen0bit/netprobe-cve-2026-98432
Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
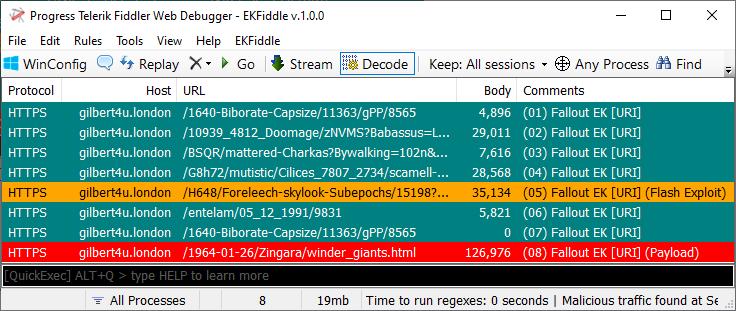 jeromesegura/ekfiddle
Your Swiss Army knife to analyze malicious web traffic based on the popular Fiddler web debugger.
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…