
AngryOxide
 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
exploitationinformation-gatheringpacket-sniffing-analysis+5
2.0k
ragnt/angryoxideOffensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 zapotek/cdpsnarf
CDPSnarf is a network sniffer exclusively written to extract information from CDP (Cisco Discovery Protocol) packets.
 thelightscope/thelightscope
TheLightScope
 galkan/flashlight
Pentesters spend too much time during information gathering phase. Flashlight (Fener) provides services to scan network/ports and gather information…
 ets-polito/esp32-sniffer
ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 offensive-hub/black-widow
GUI based offensive penetration testing tool (Open Source)
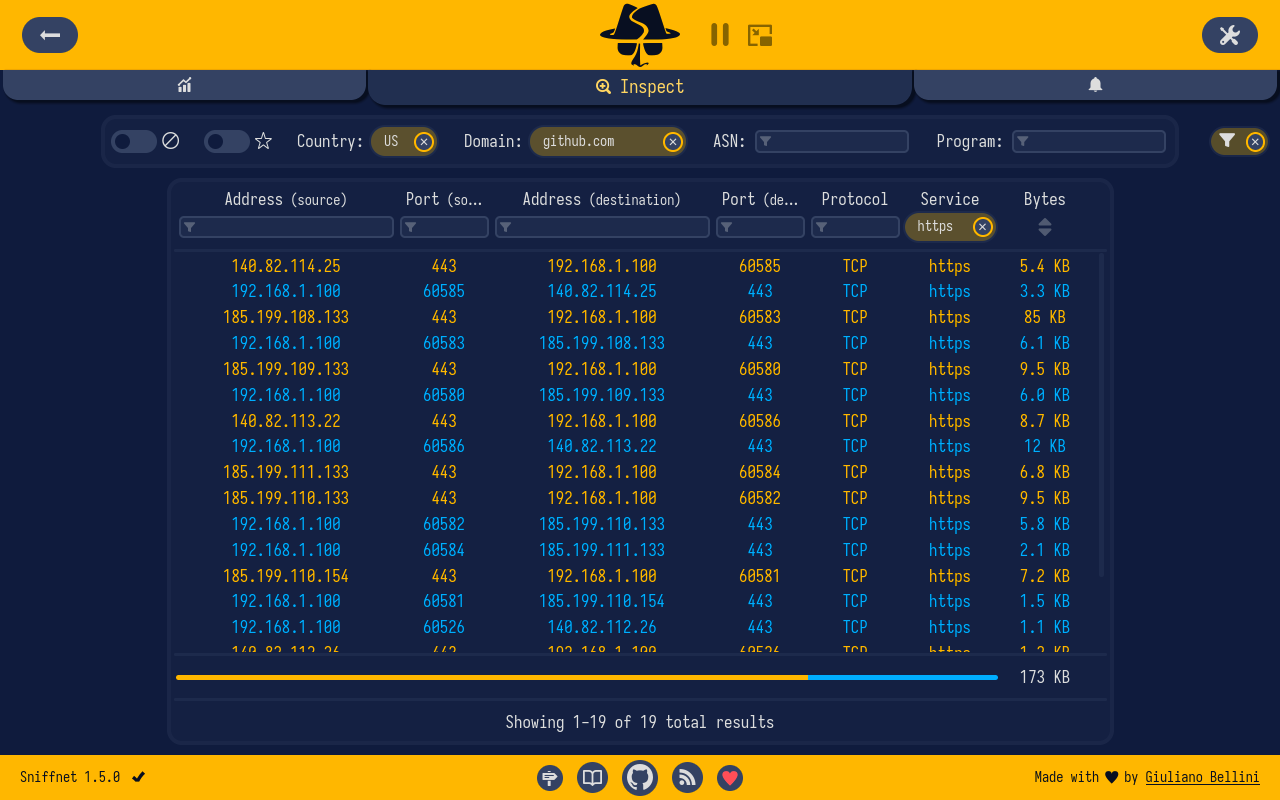 gyulyvgc/sniffnet
Comfortably monitor your network traffic 🕵️♂️
 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.
 borntoberoot/networkmanager
A powerful open-source tool for managing networks and troubleshooting network problems!
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…

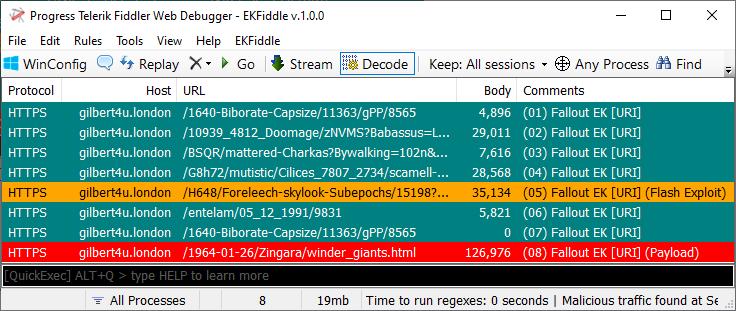 jeromesegura/ekfiddle
Your Swiss Army knife to analyze malicious web traffic based on the popular Fiddler web debugger.
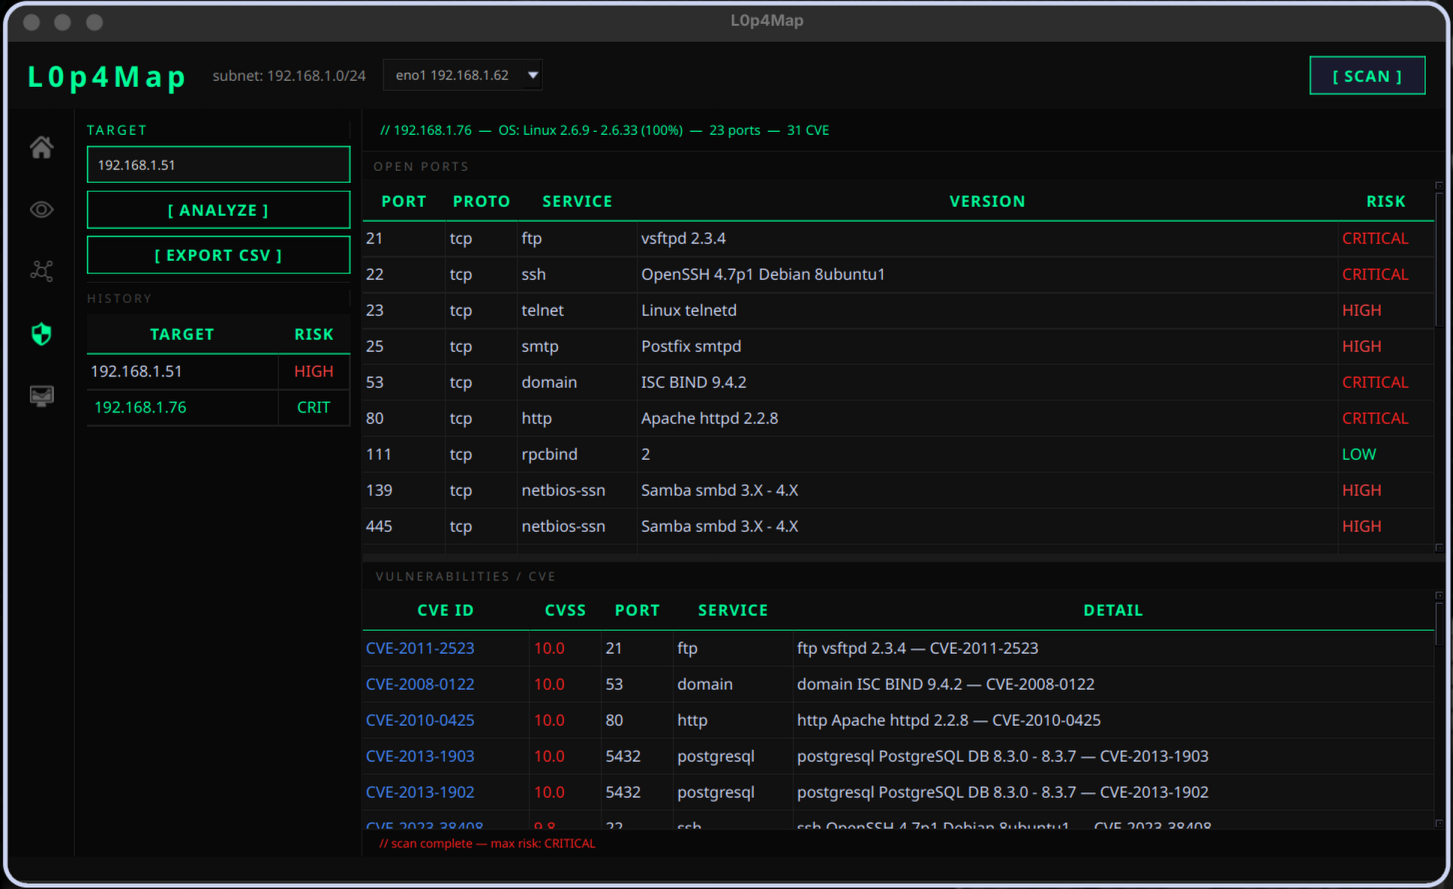 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 ooni/probe-cli
Go measurement engine and CLI for detecting Internet censorship and network interference, running OONI network tests and reporting results to the…
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…