
Wireshark
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
dns-analysisforensicsnetwork-forensics+3
1.6k
wireshark/wiresharkWireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
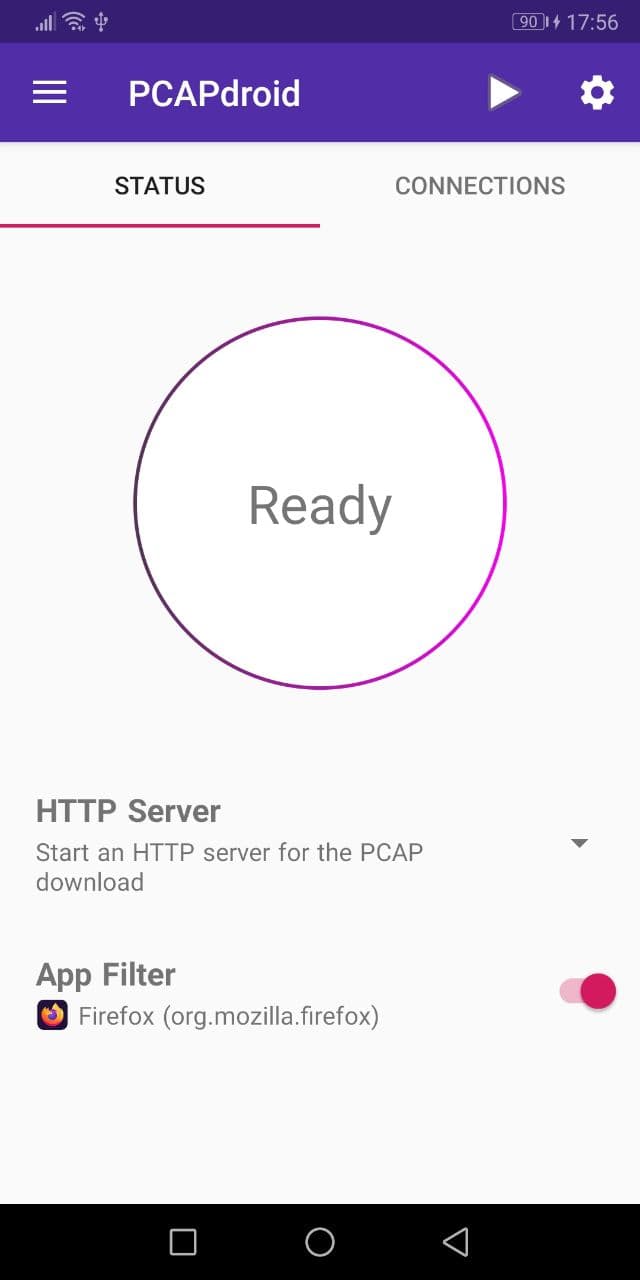 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 appneta/tcpreplay
Edit and replay captured network traffic at arbitrary speeds — a suite of pcap tools for *NIX and Windows.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
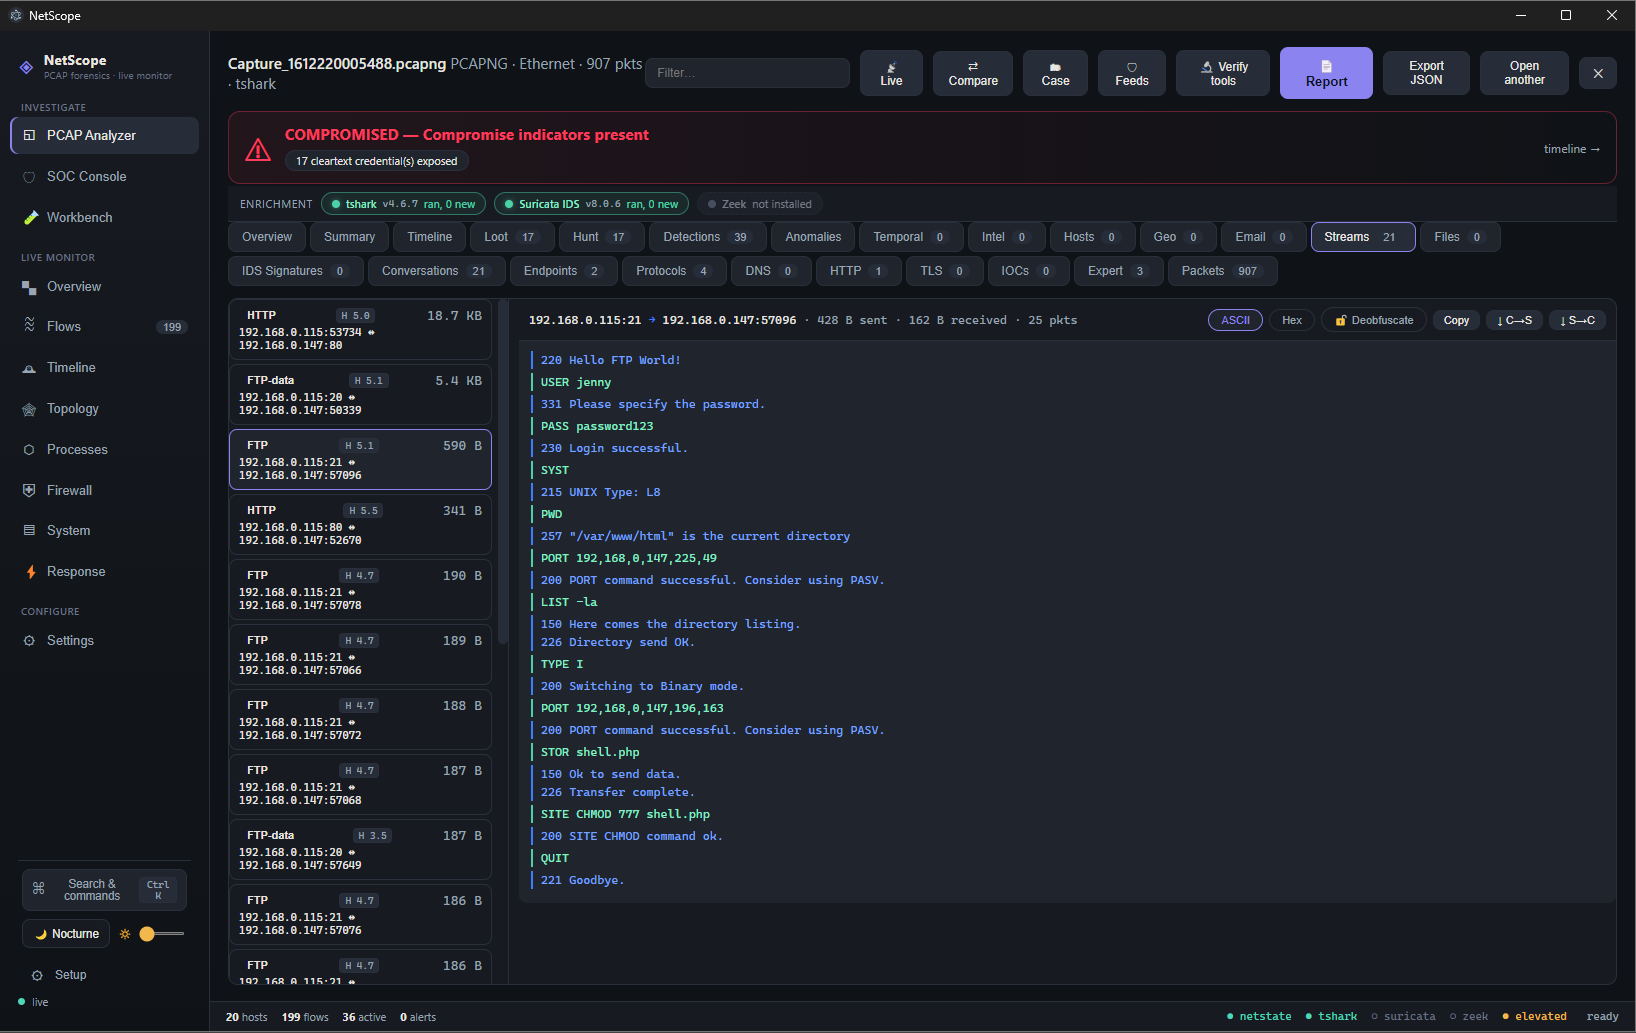 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
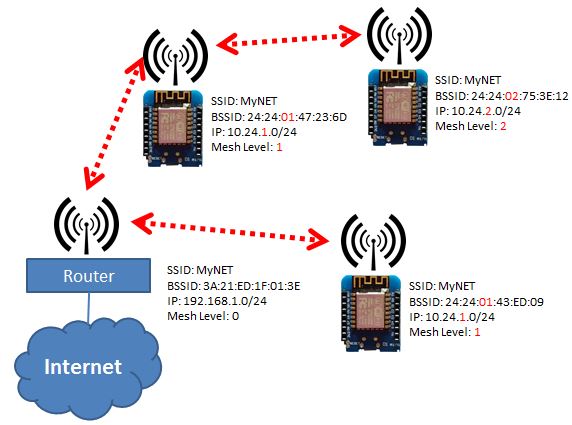 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
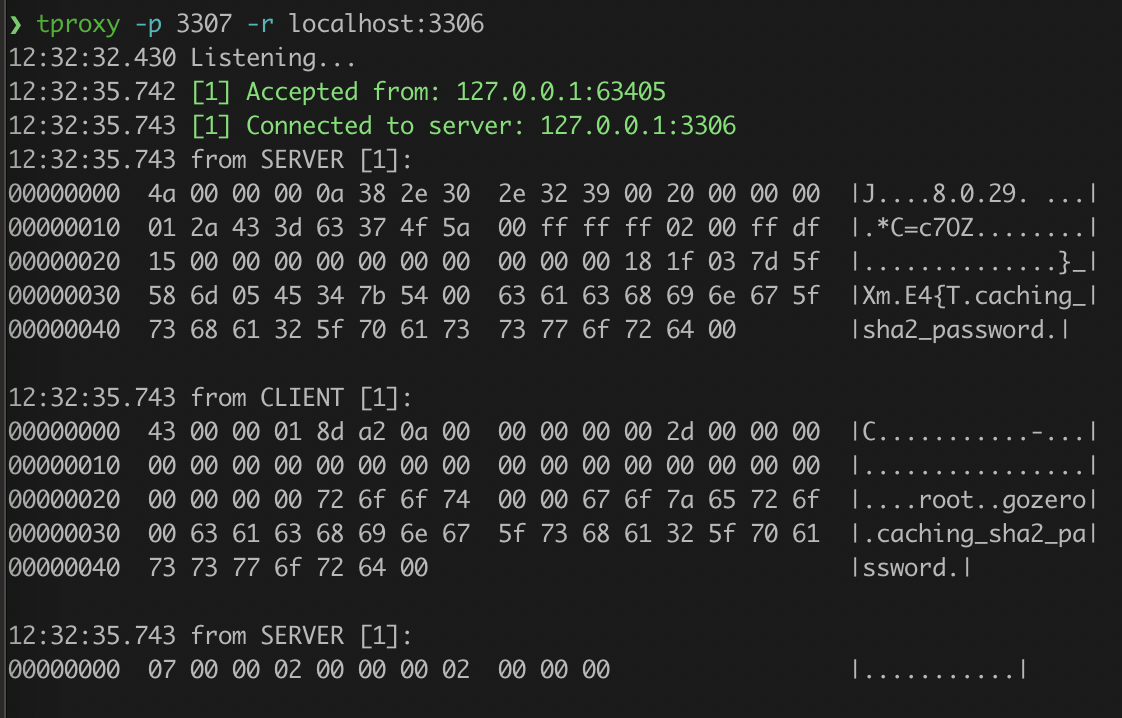 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors