

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
46.4k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
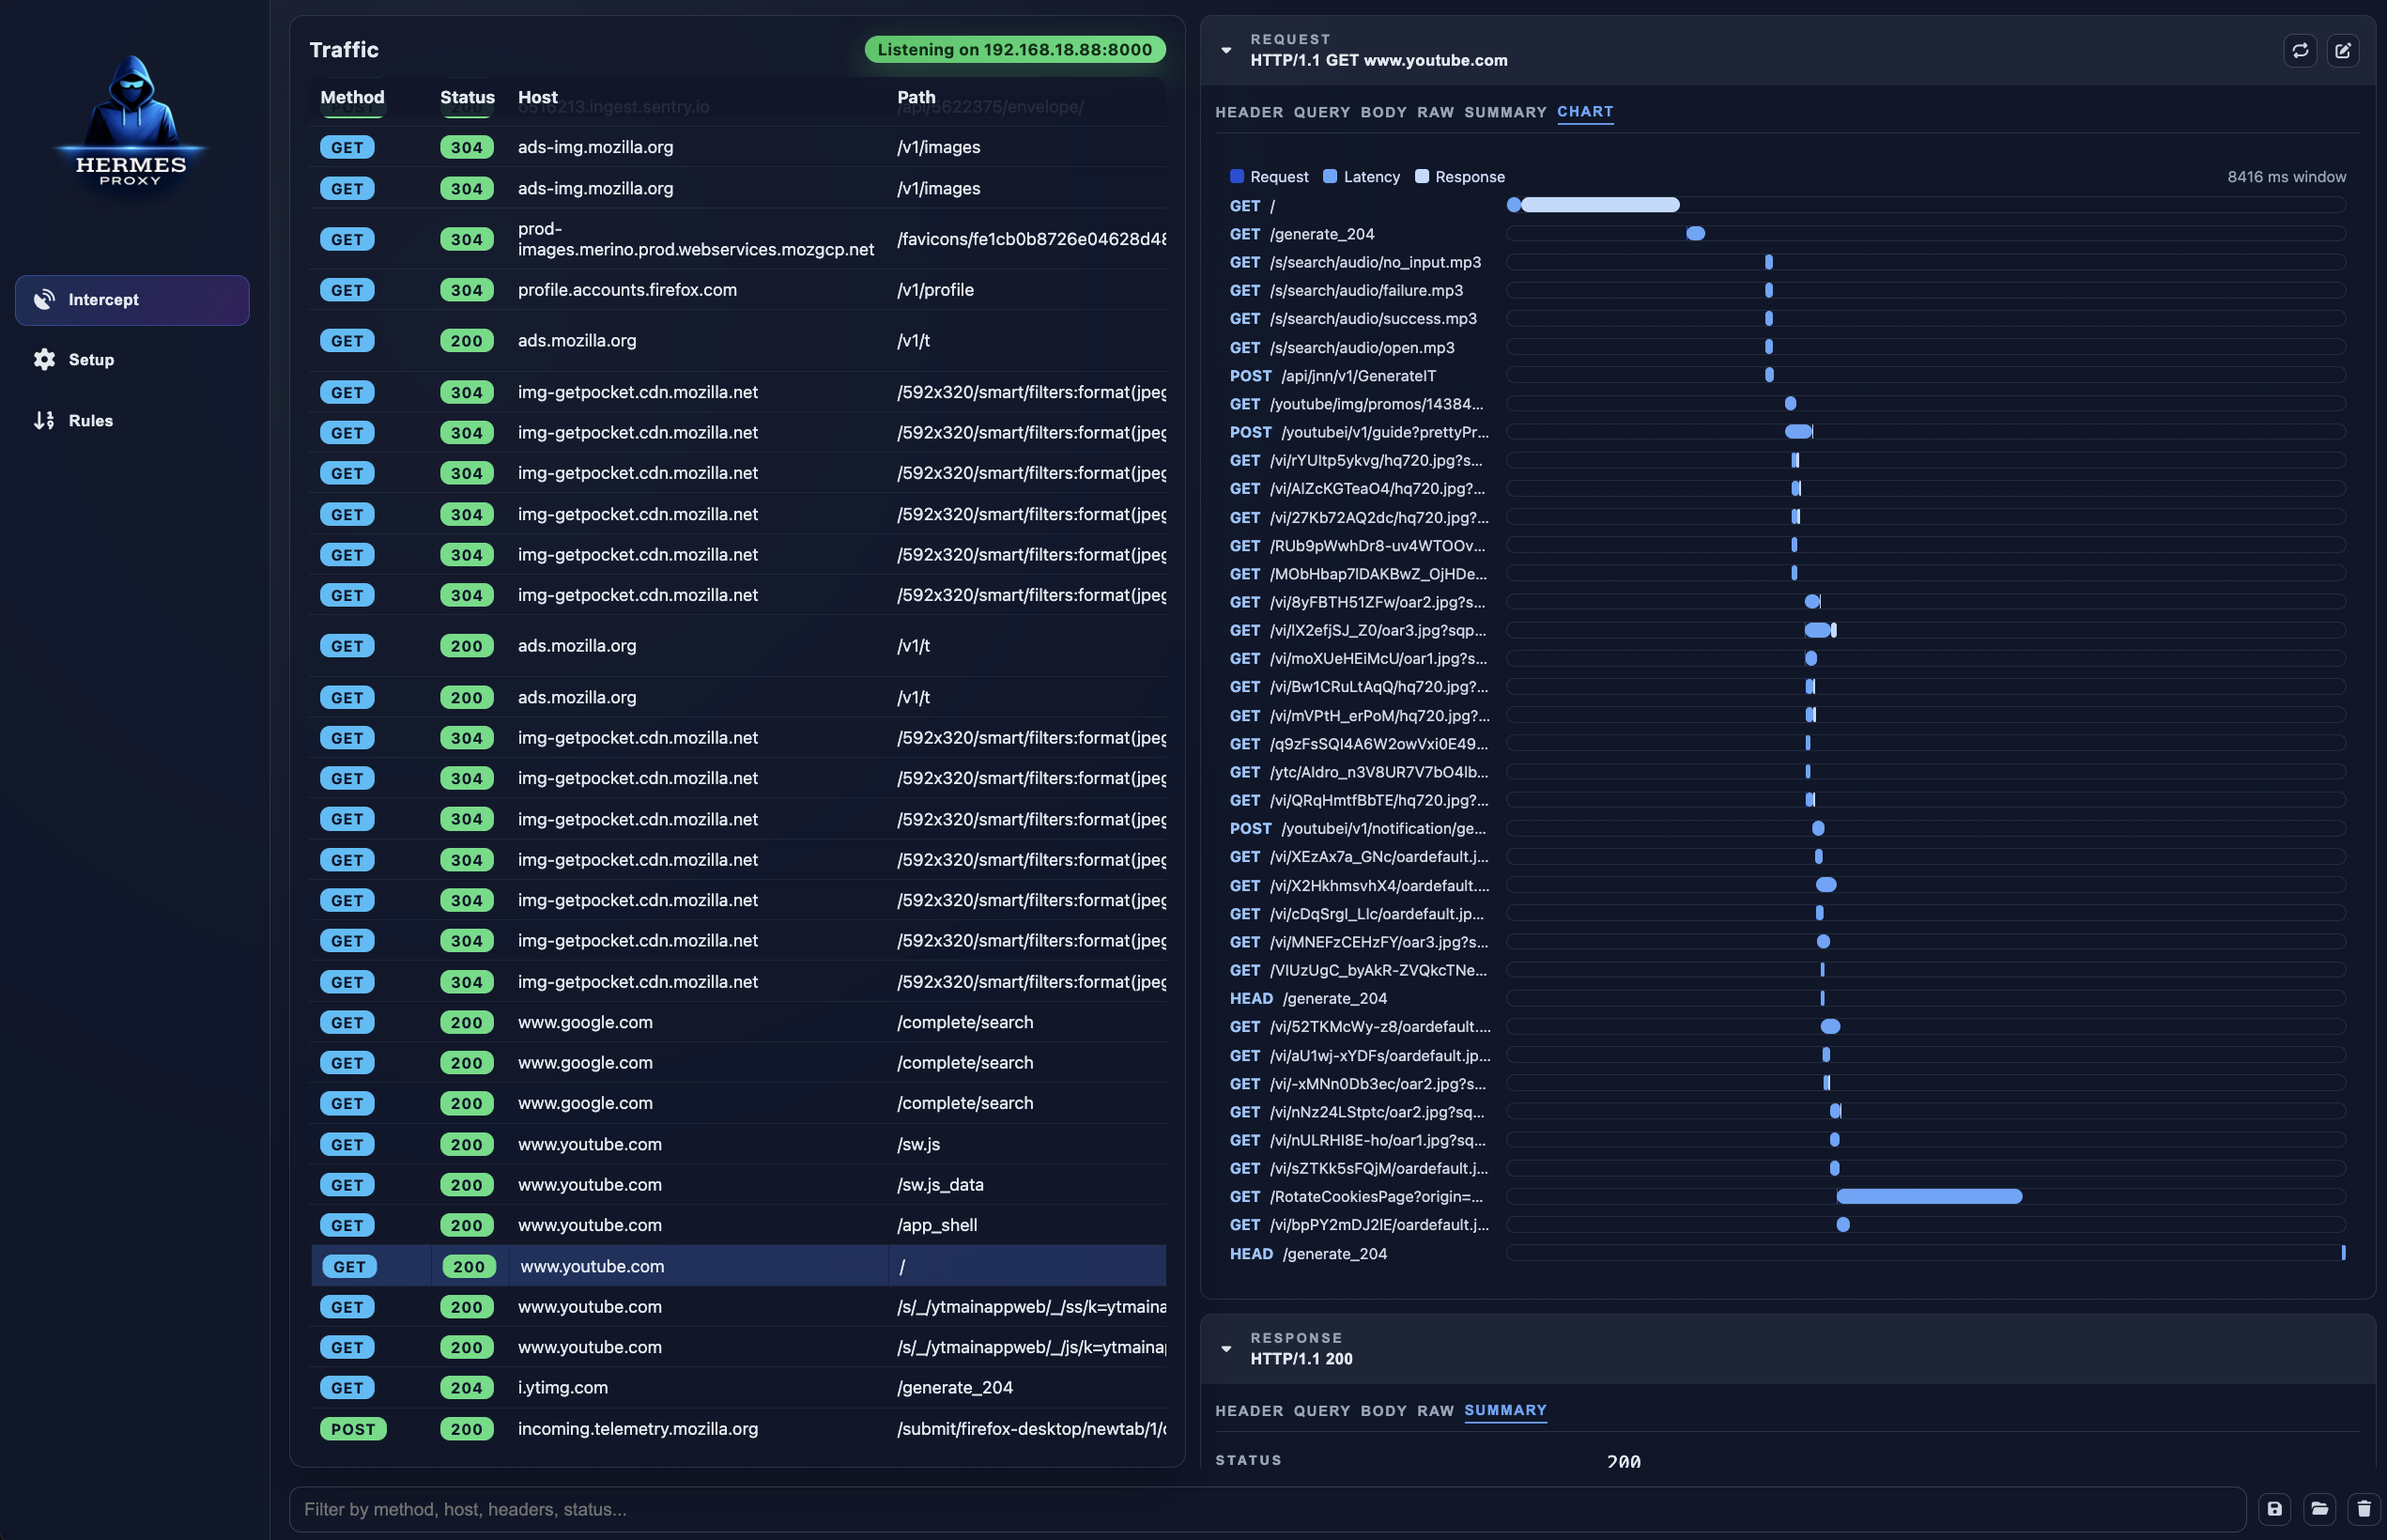 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 offensive-hub/black-widow
GUI based offensive penetration testing tool (Open Source)
 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
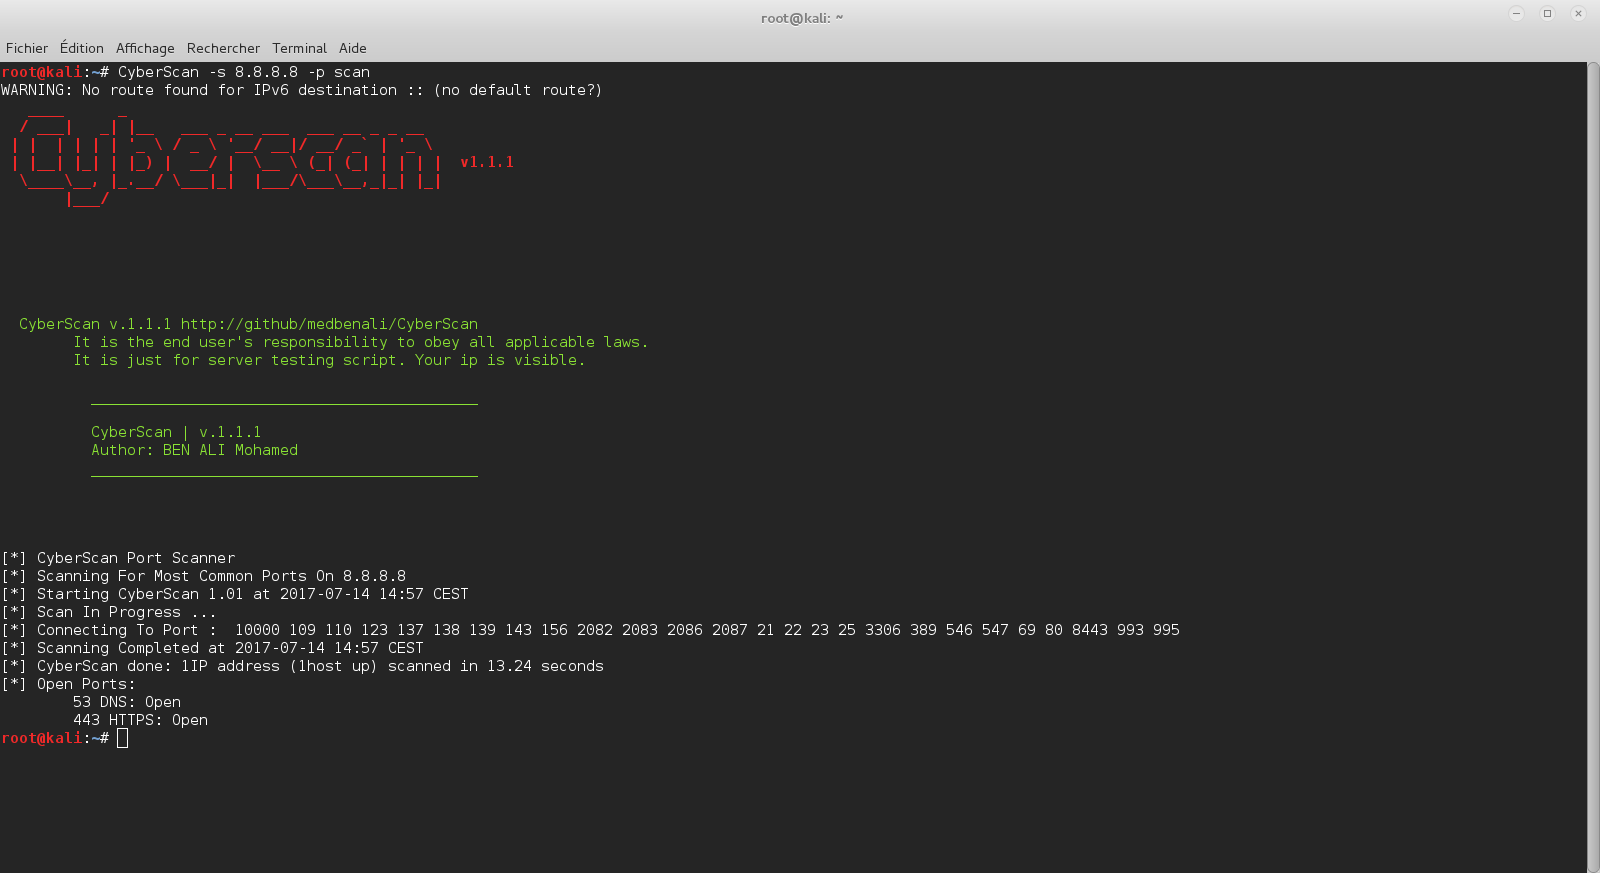 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 emilebarnard242/pentest-metasploitable2
Structured penetration testing lab documenting a full attack chain from network reconnaissance to root exploitation of vsftpd 2.3.4 backdoor, with…
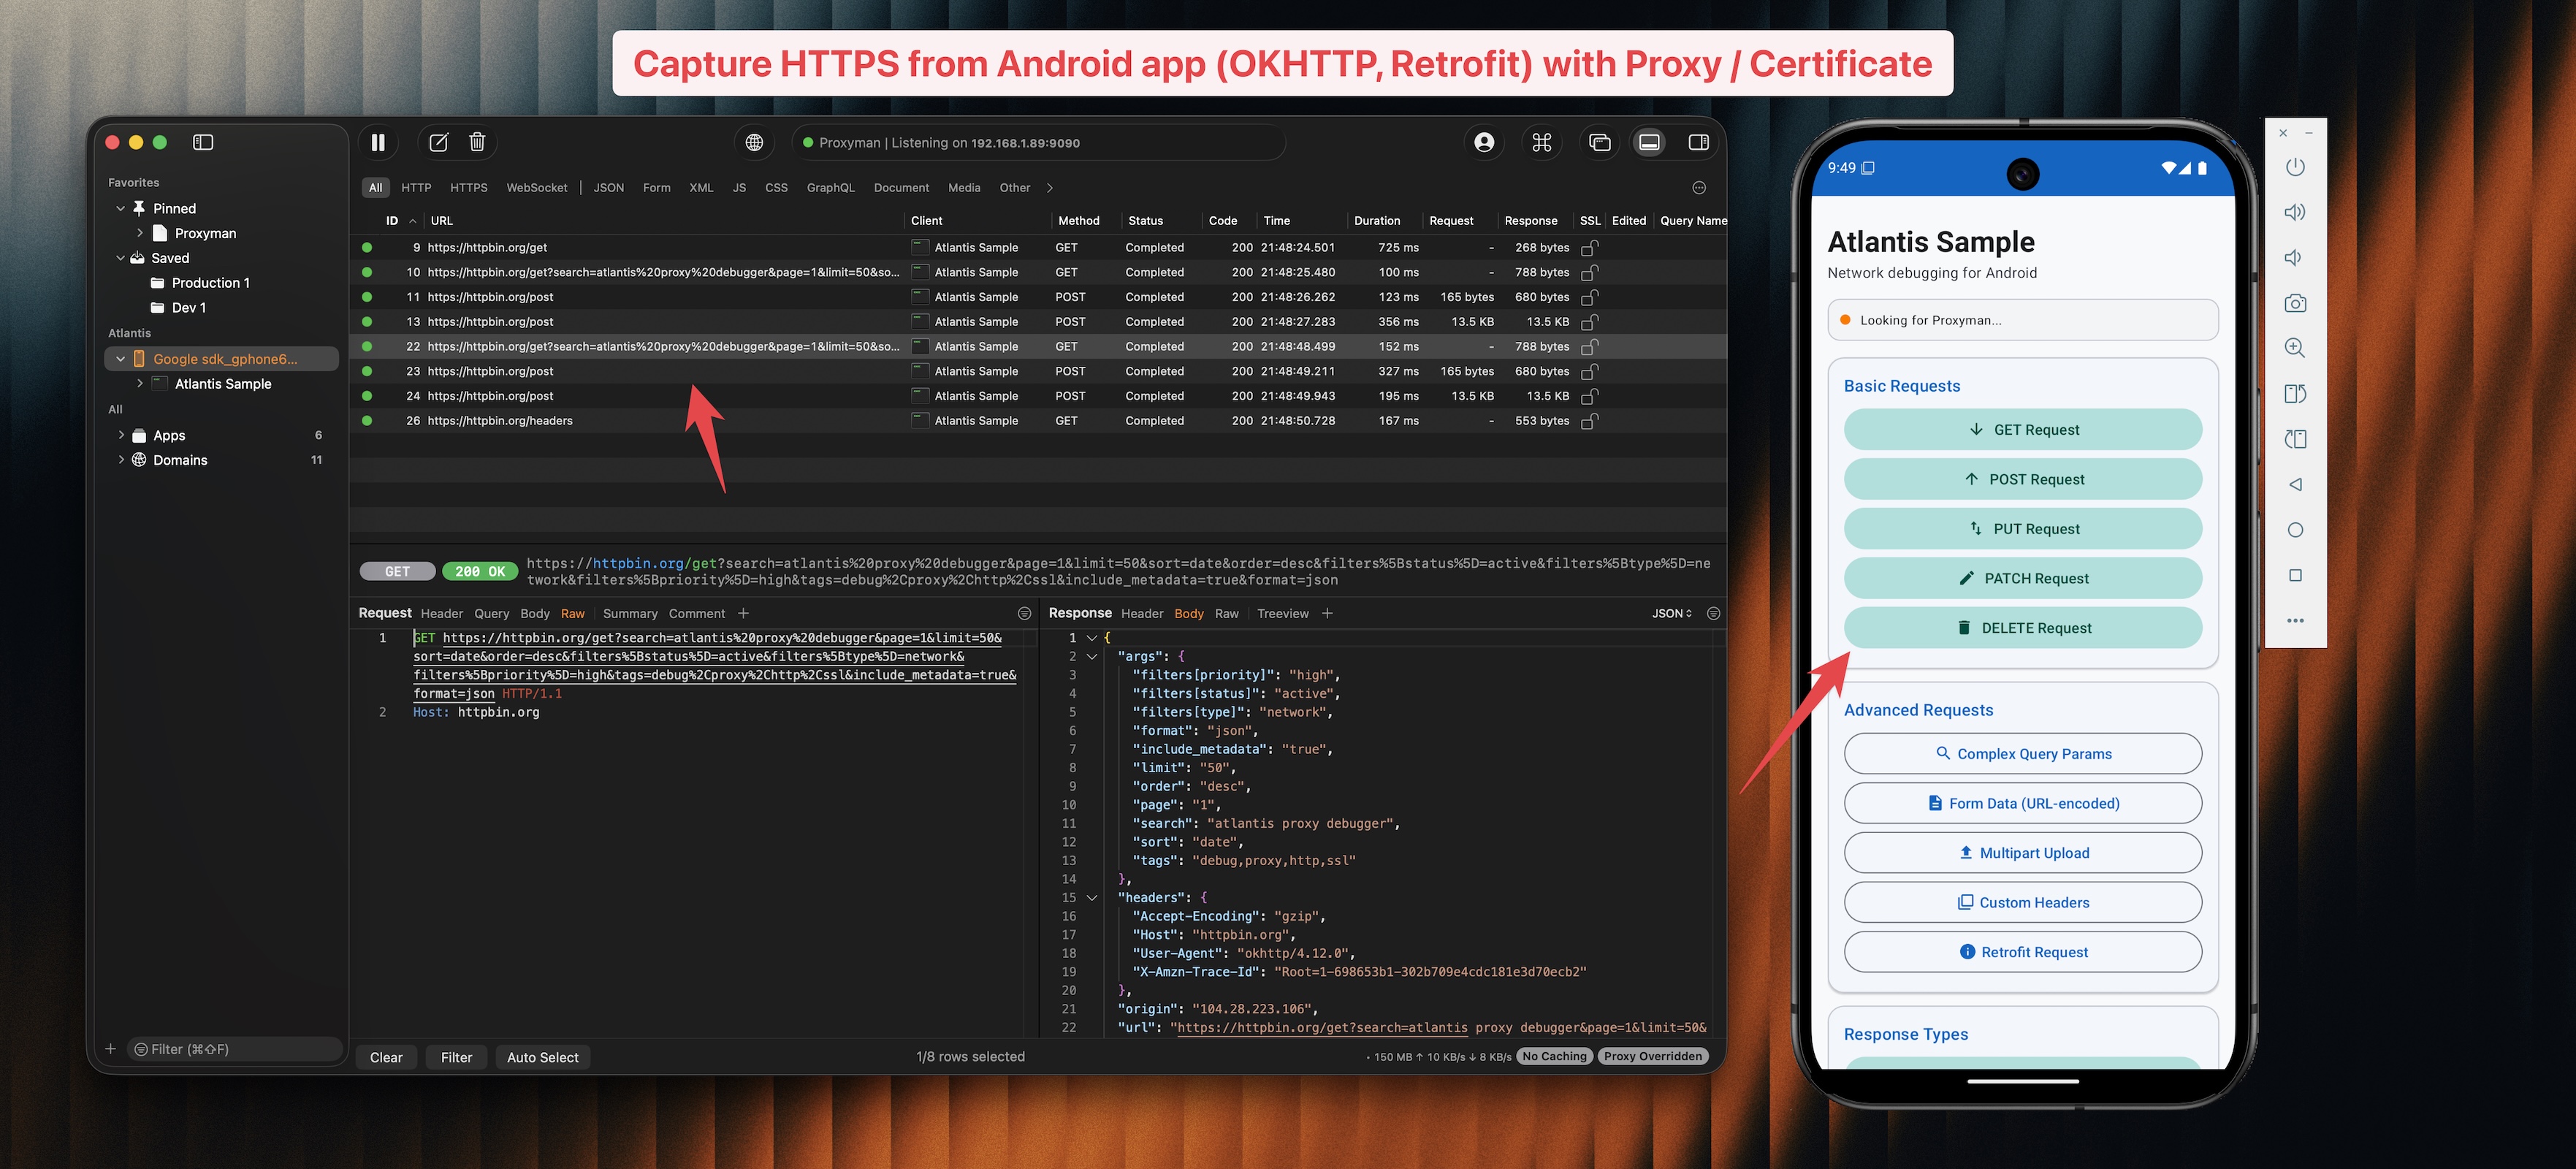 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.