
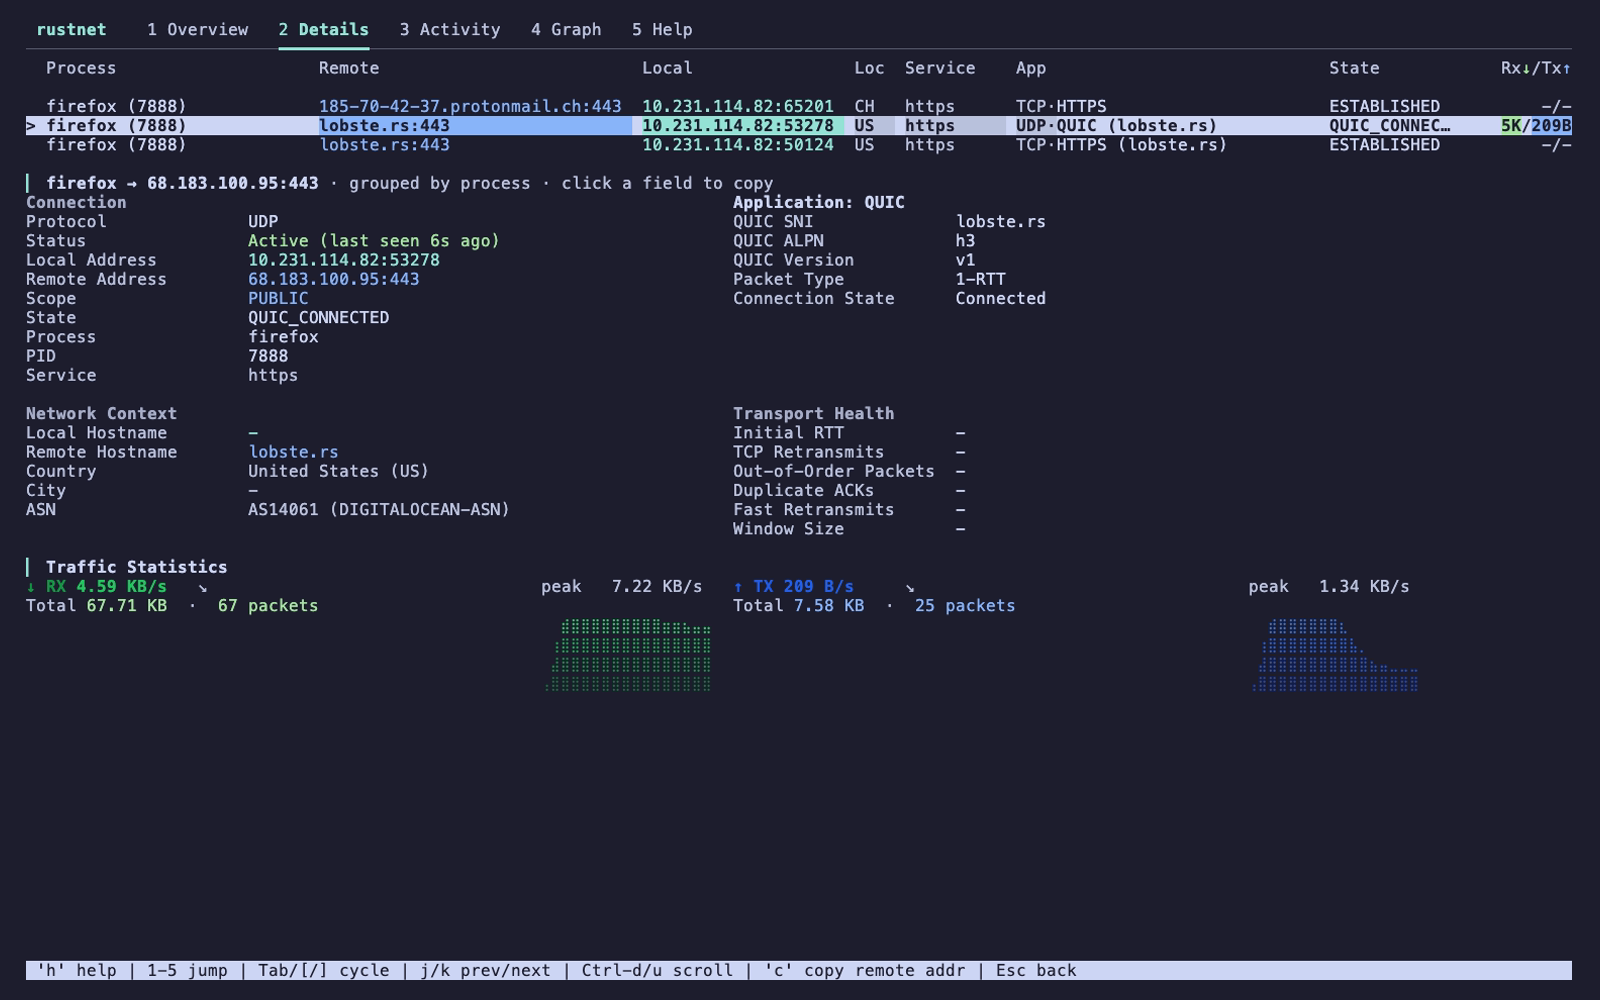
rustnet
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
cloud-securitycontainer-securitydns-analysis+5
4.8k12h 36m ago
domcyrus/rustnetPer-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 ut-dacs/anycast-census
Longitudinal anycast census system that probes IPv4/IPv6 prefixes via ICMP, TCP, and DNS to detect anycast deployments and geolocate PoPs, publishing…
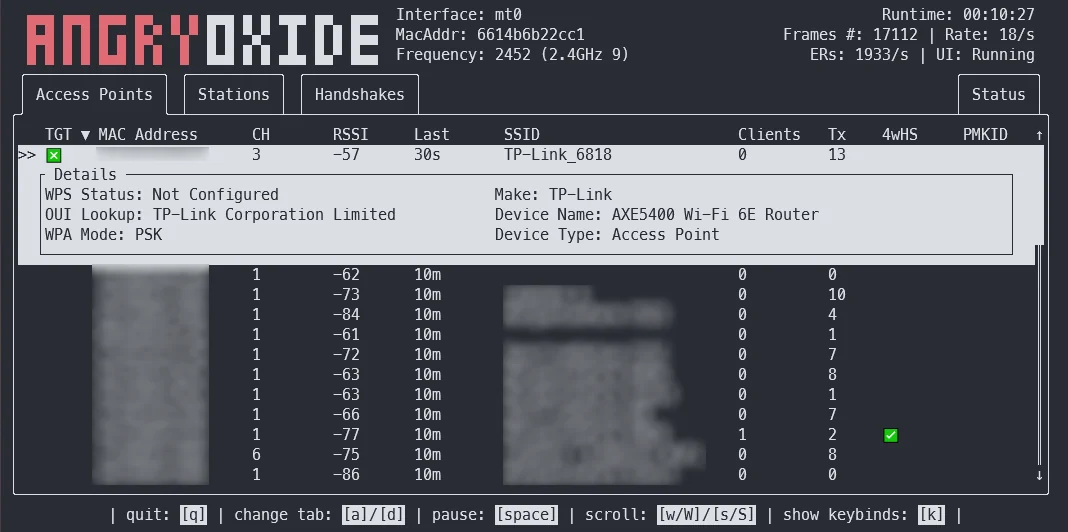 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
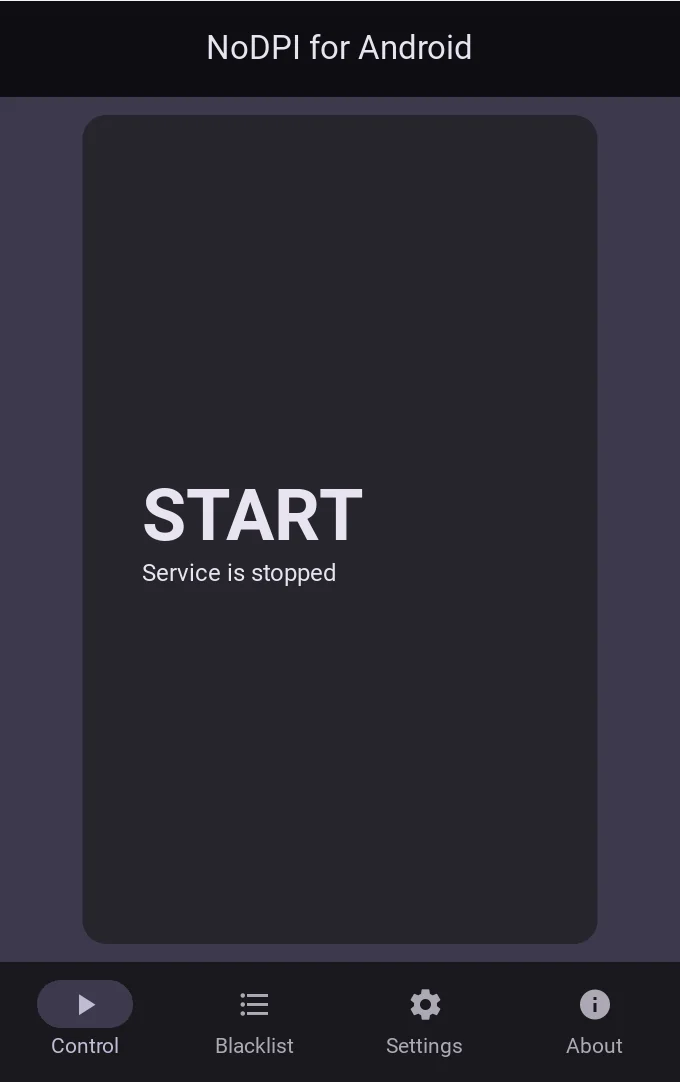 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 gary23w/hodometer
A single-file native Windows tray application (C, Win32, no runtime) that shows exactly which program is sending and receiving bytes and to which…
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 ntop/pf_ring
High-speed packet processing framework
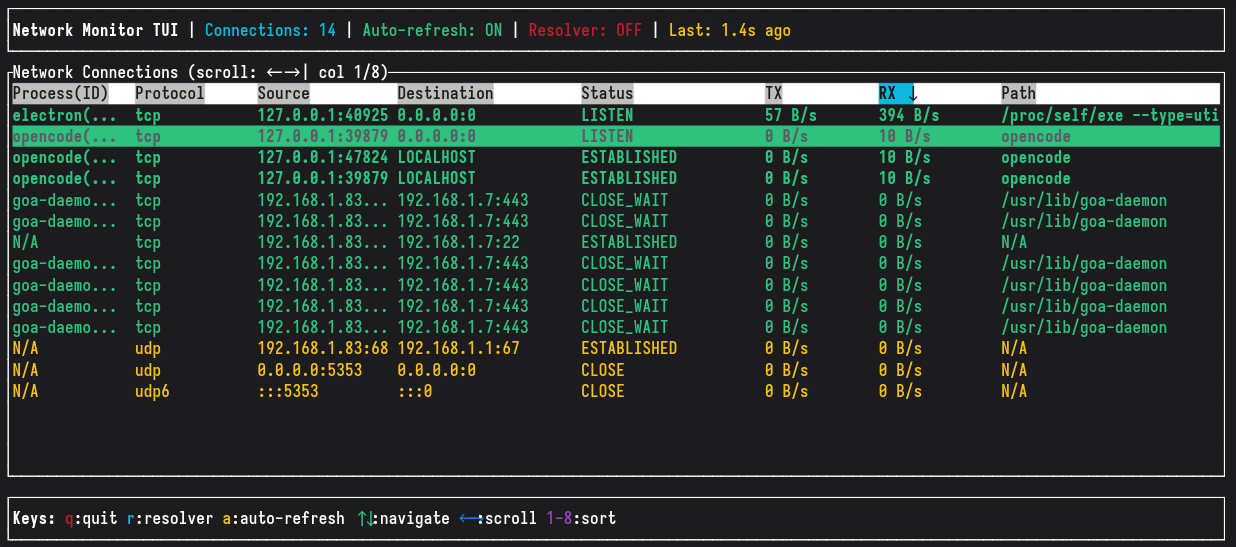 grigio/network-monitor
A real-time network connection monitoring tool built with Rust and GTK4, displaying active connections with live I/O statistics in a modern graphical…
 darkoperator/dnsrecon
DNS Enumeration Script
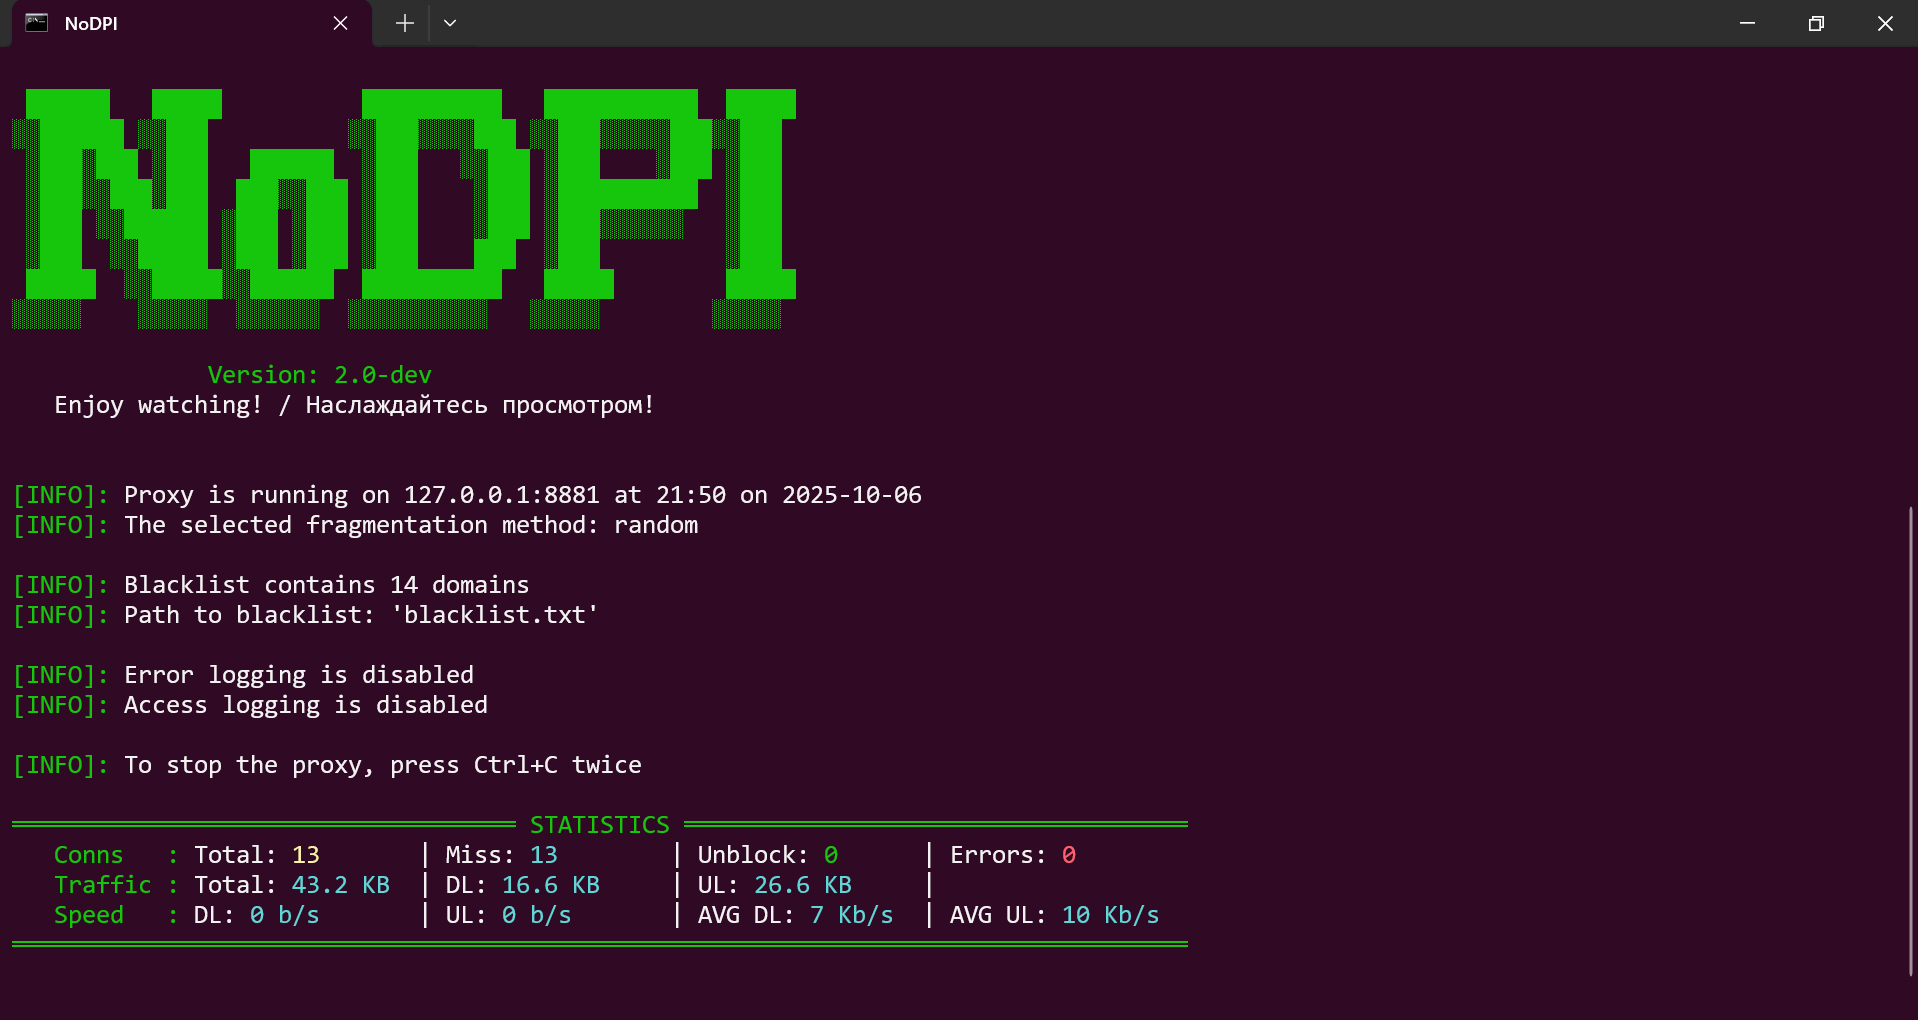 gvcoder09/nodpi
Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…
 corelight/emudhra-weak-keys
A Zeek package that detects when compromised eMudhra intermediate certificates are used in TLS 1.2 and below.
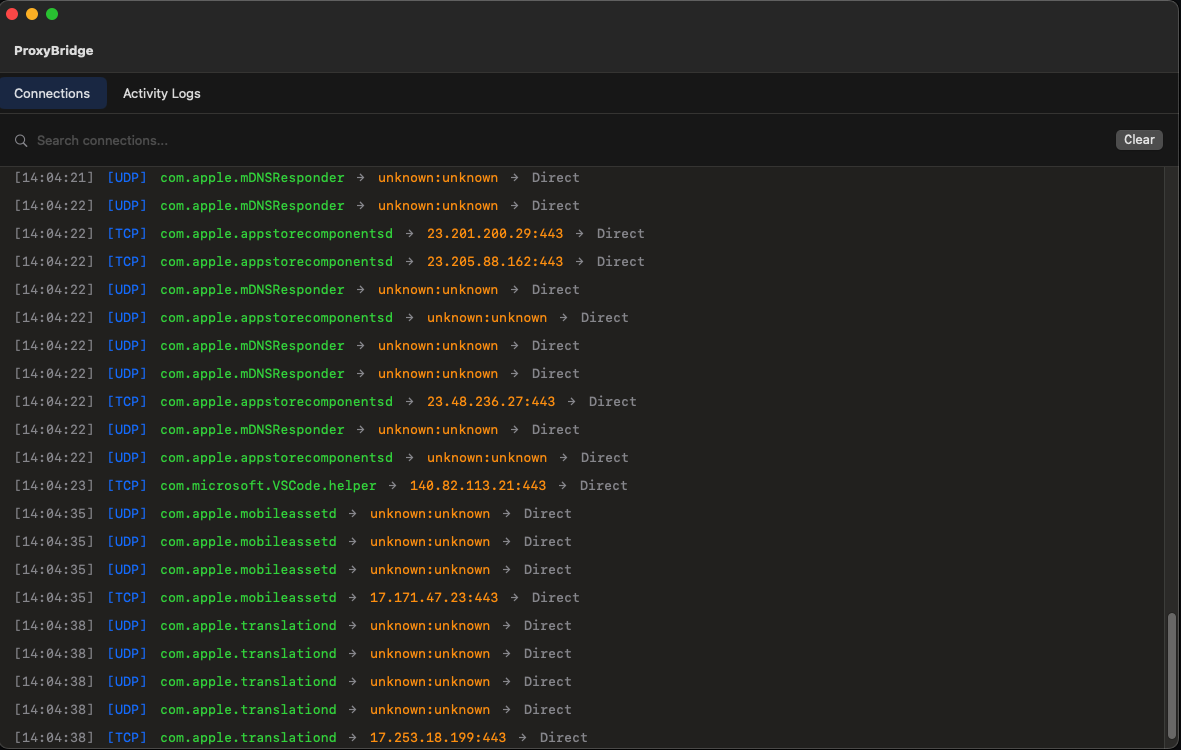 interceptsuite/proxybridge
Force Proxy to any Windows/MacOS/Linux Application TCP and UDP traffic
 owasp/pysap
pysap is an open source Python library that provides modules for crafting and sending packets using SAP's NI, Diag, Enqueue, Router, MS, SNC, IGS,…
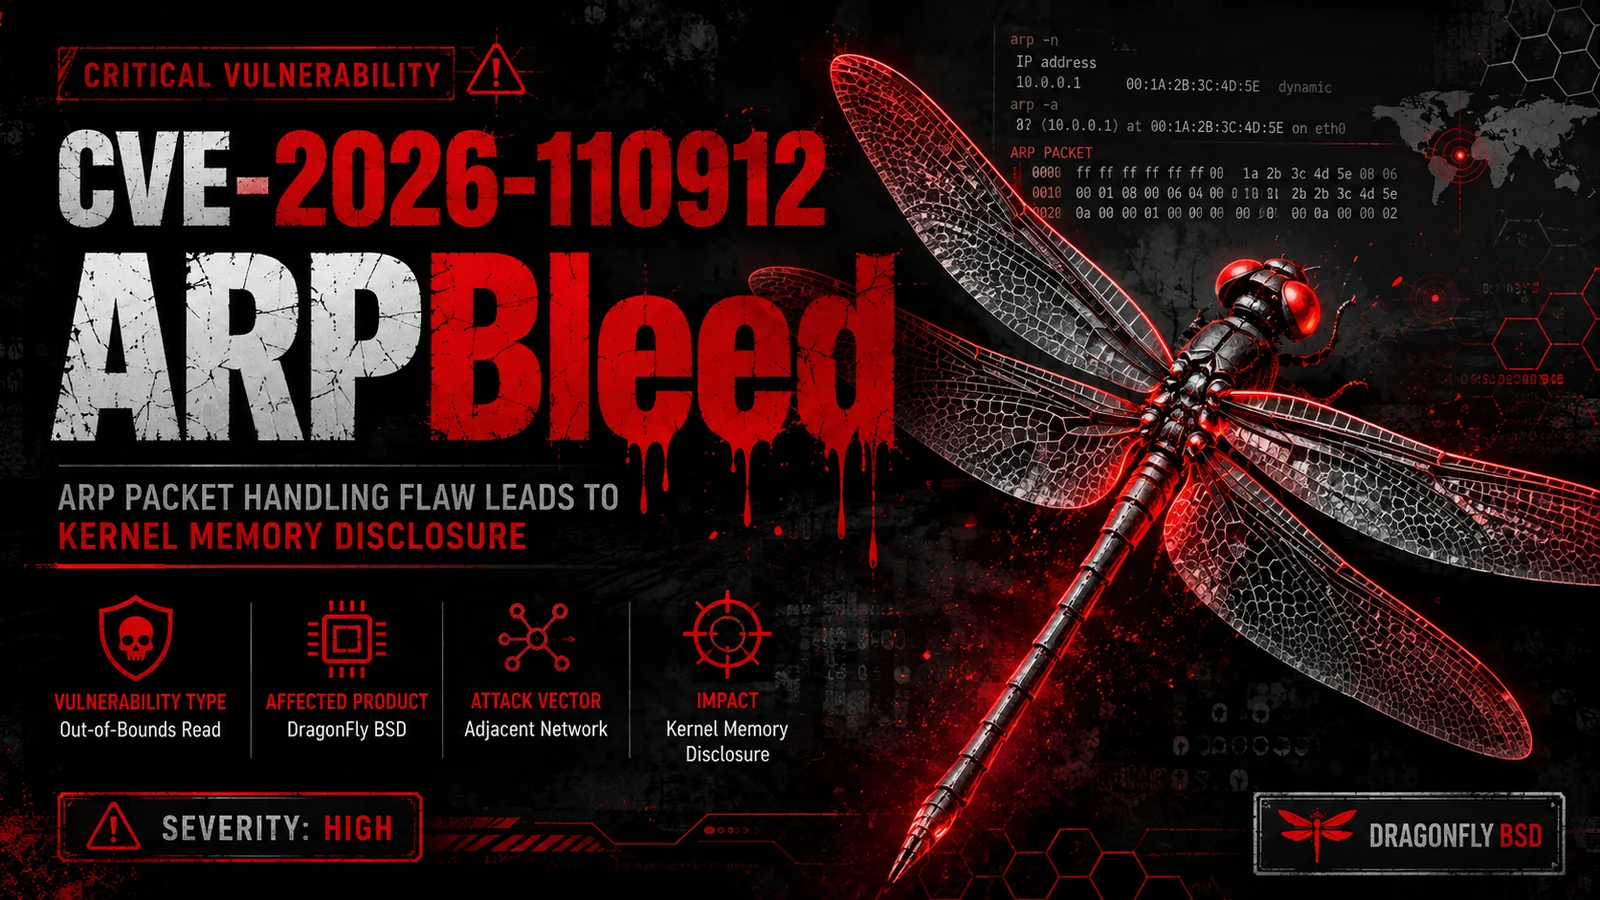 0xblackash/cve-2026-110912
Python/scapy proof-of-concept for CVE-2026-110912 (ARPBleed), an ARP ar_hln/ar_pln out-of-bounds read in DragonFly BSD that leaks kernel heap and…
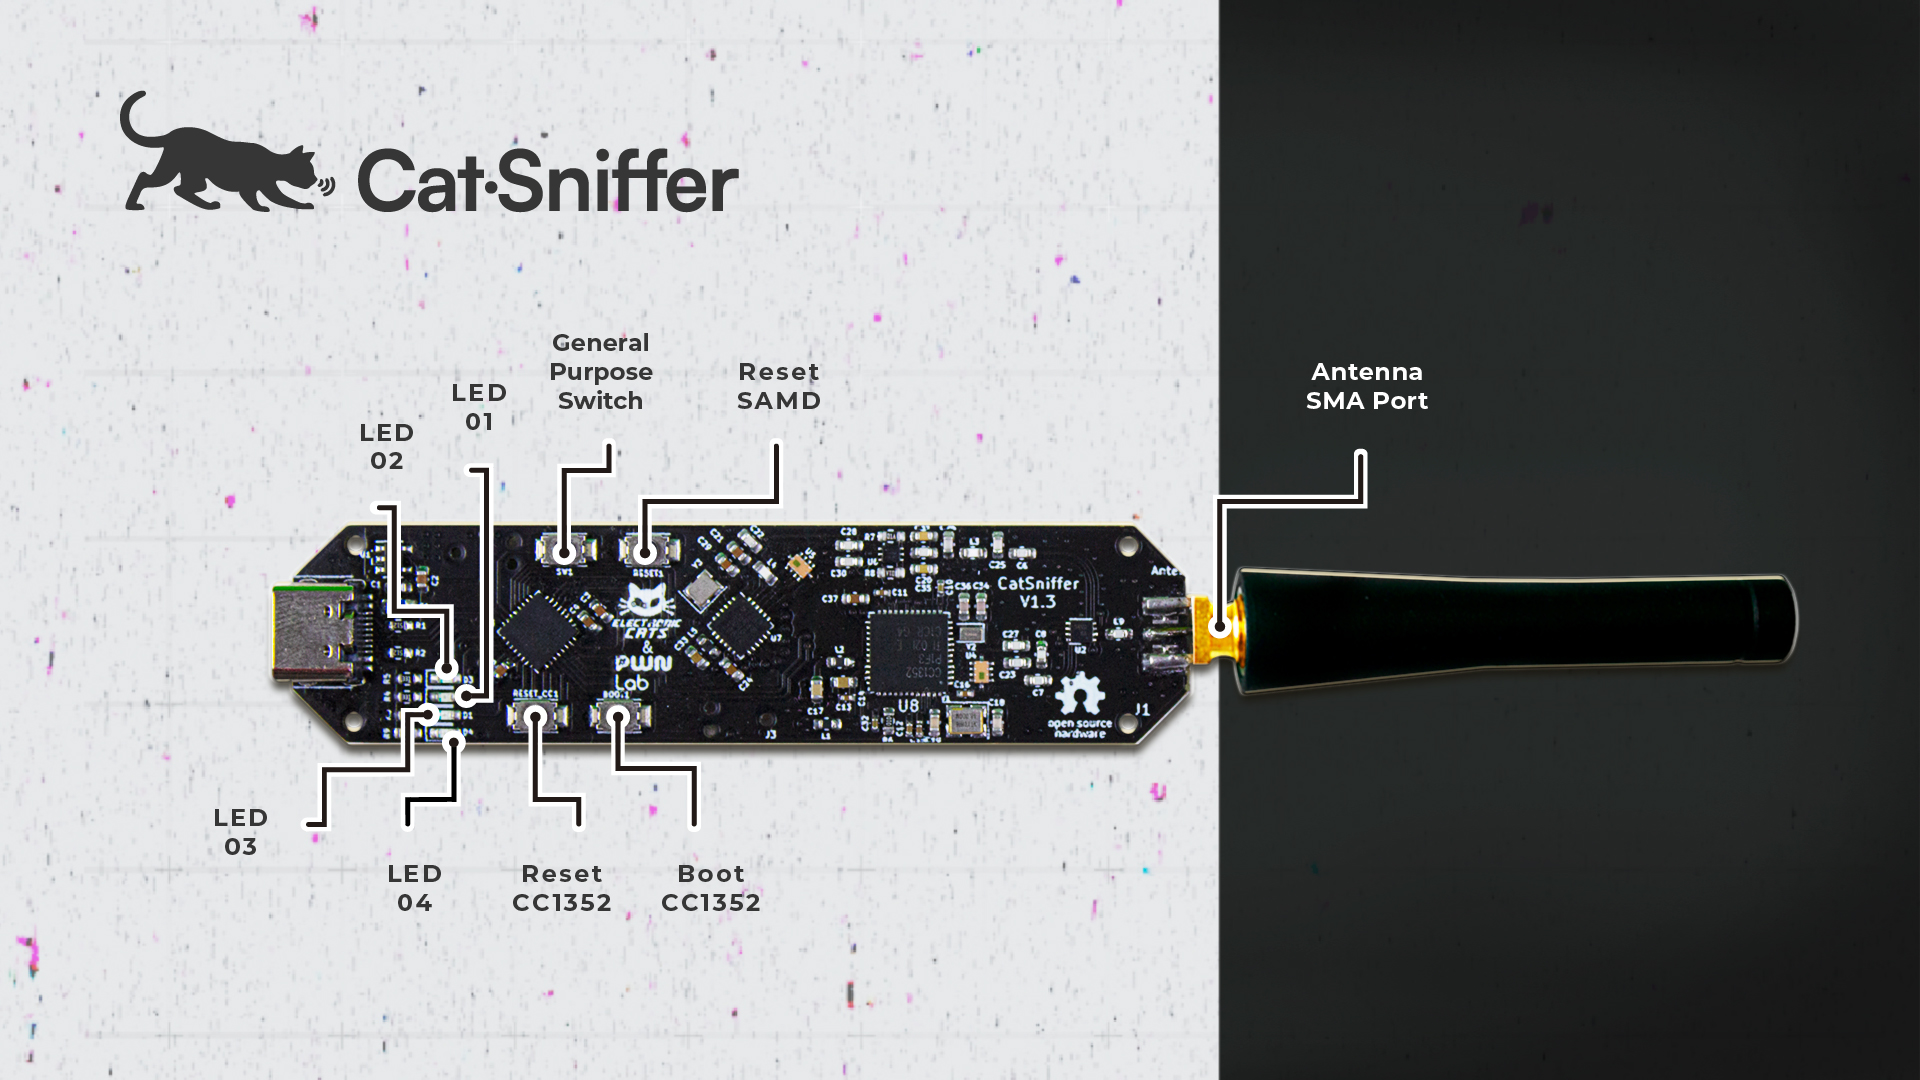 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…