

 mrtdlgc/goodoldsearch-oss
Local static query builder for precise search across web engines, Shodan, crt.sh, and Wayback Machine. Supports Google dorks, filetype filters, date…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
 anonymousplanetorg/thgtoa
Comprehensive, open-source guide teaching online anonymity, OpSec, and identity protection techniques for activists, journalists, and…
 josue87/metafinder
Search for documents in a domain through Search Engines (Google, Bing and Baidu). The objective is to extract metadata
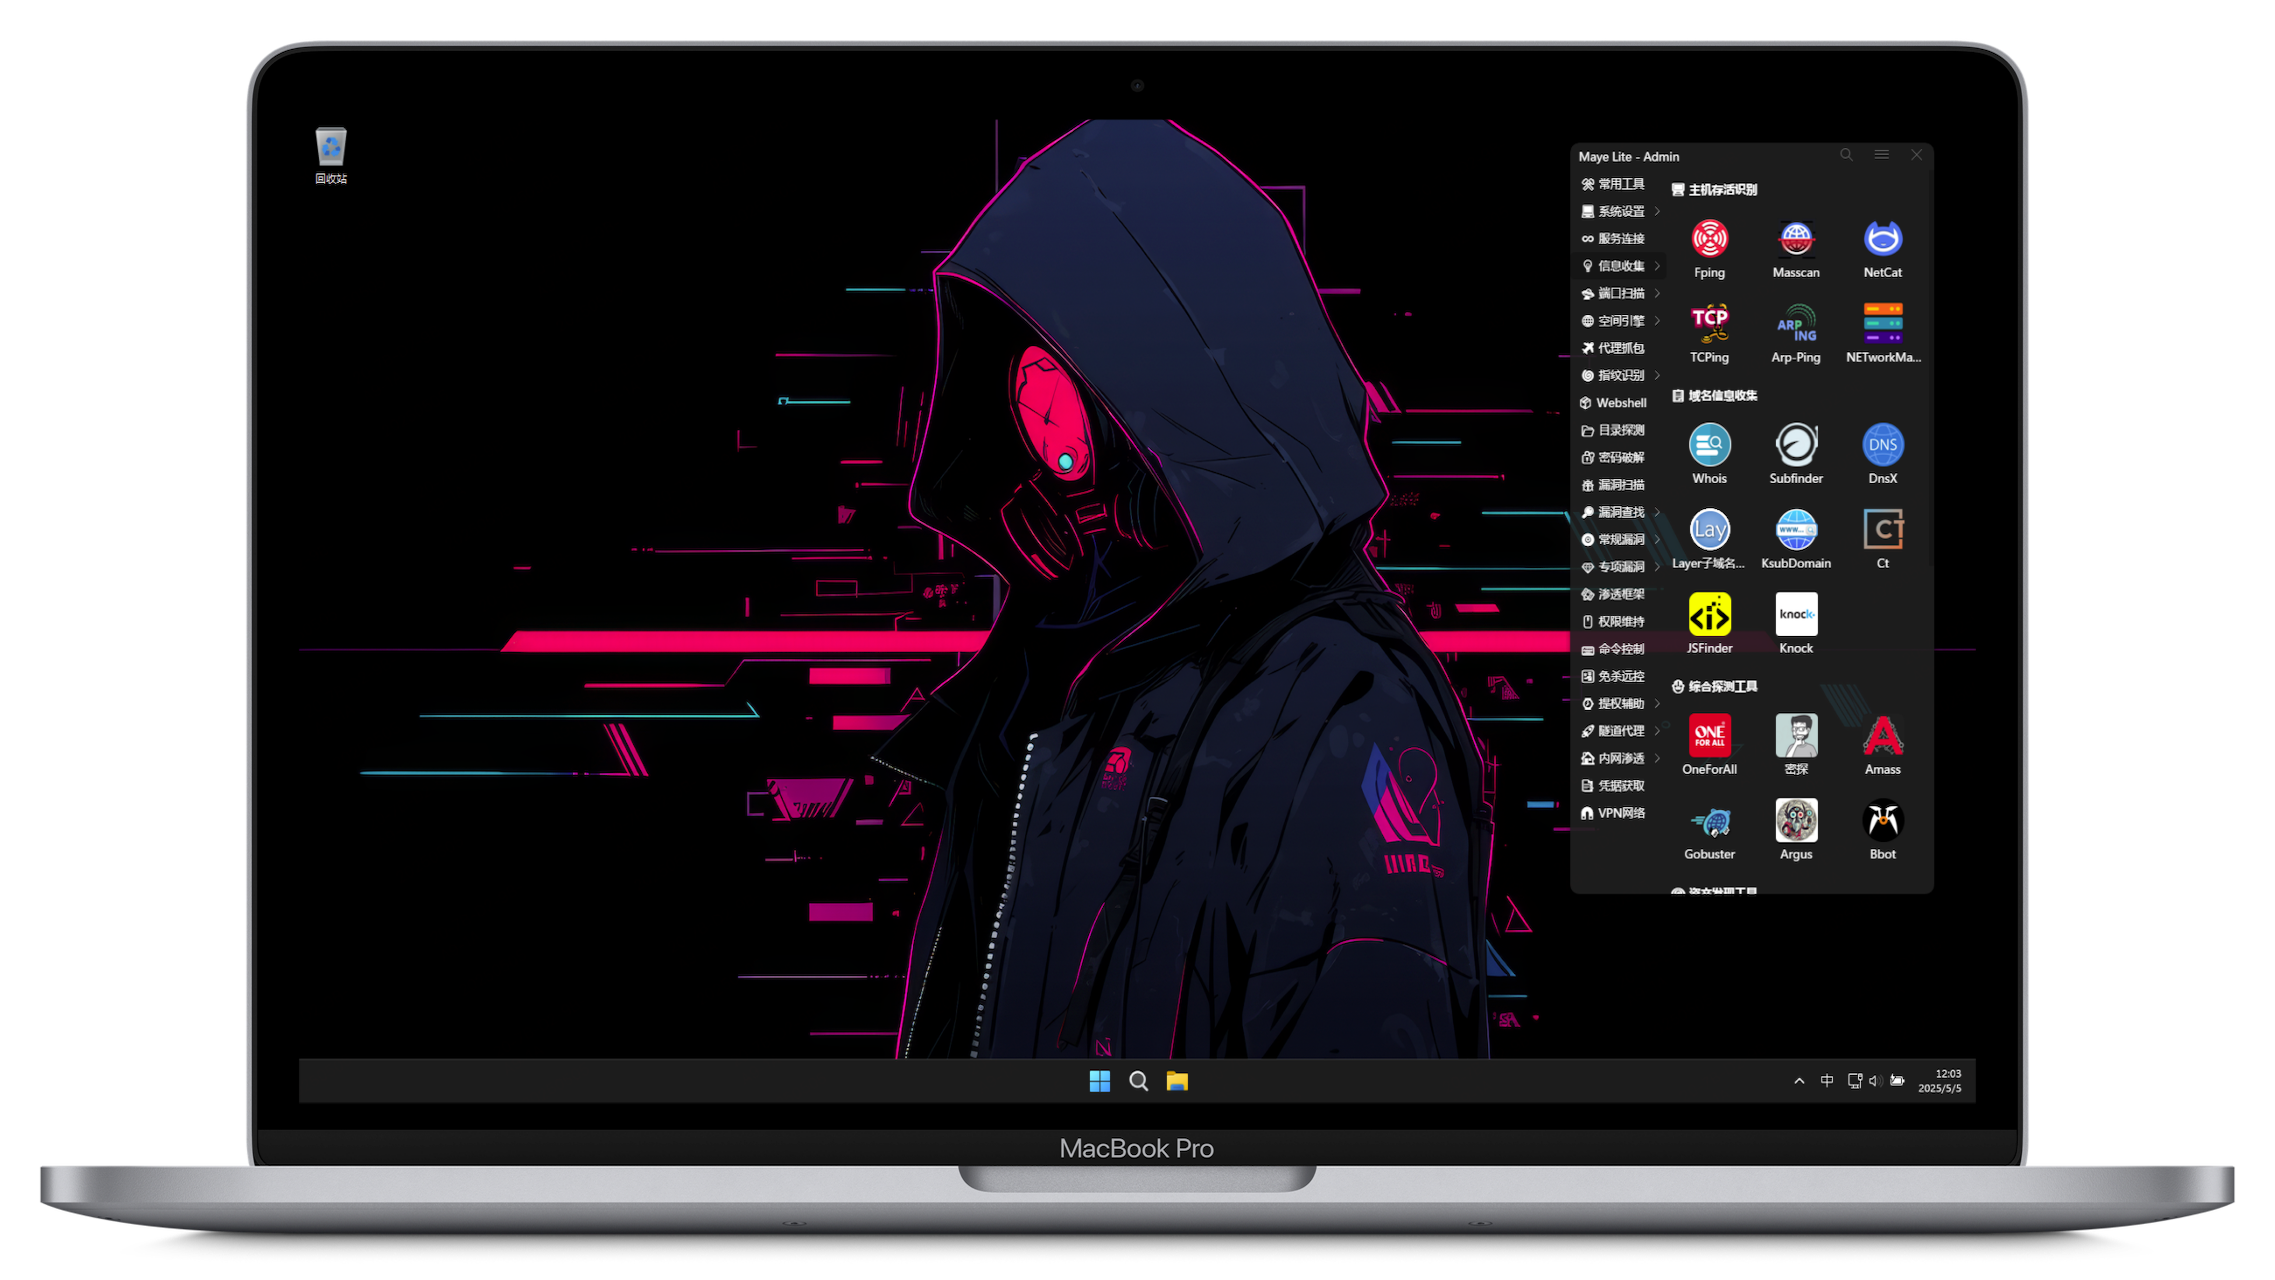 arch3rpro/pentest-windows
⚔️Windows11 Penetration Suite Toolkit 🔰 The First Windows Penetration Testing Environment on Mac M Chips
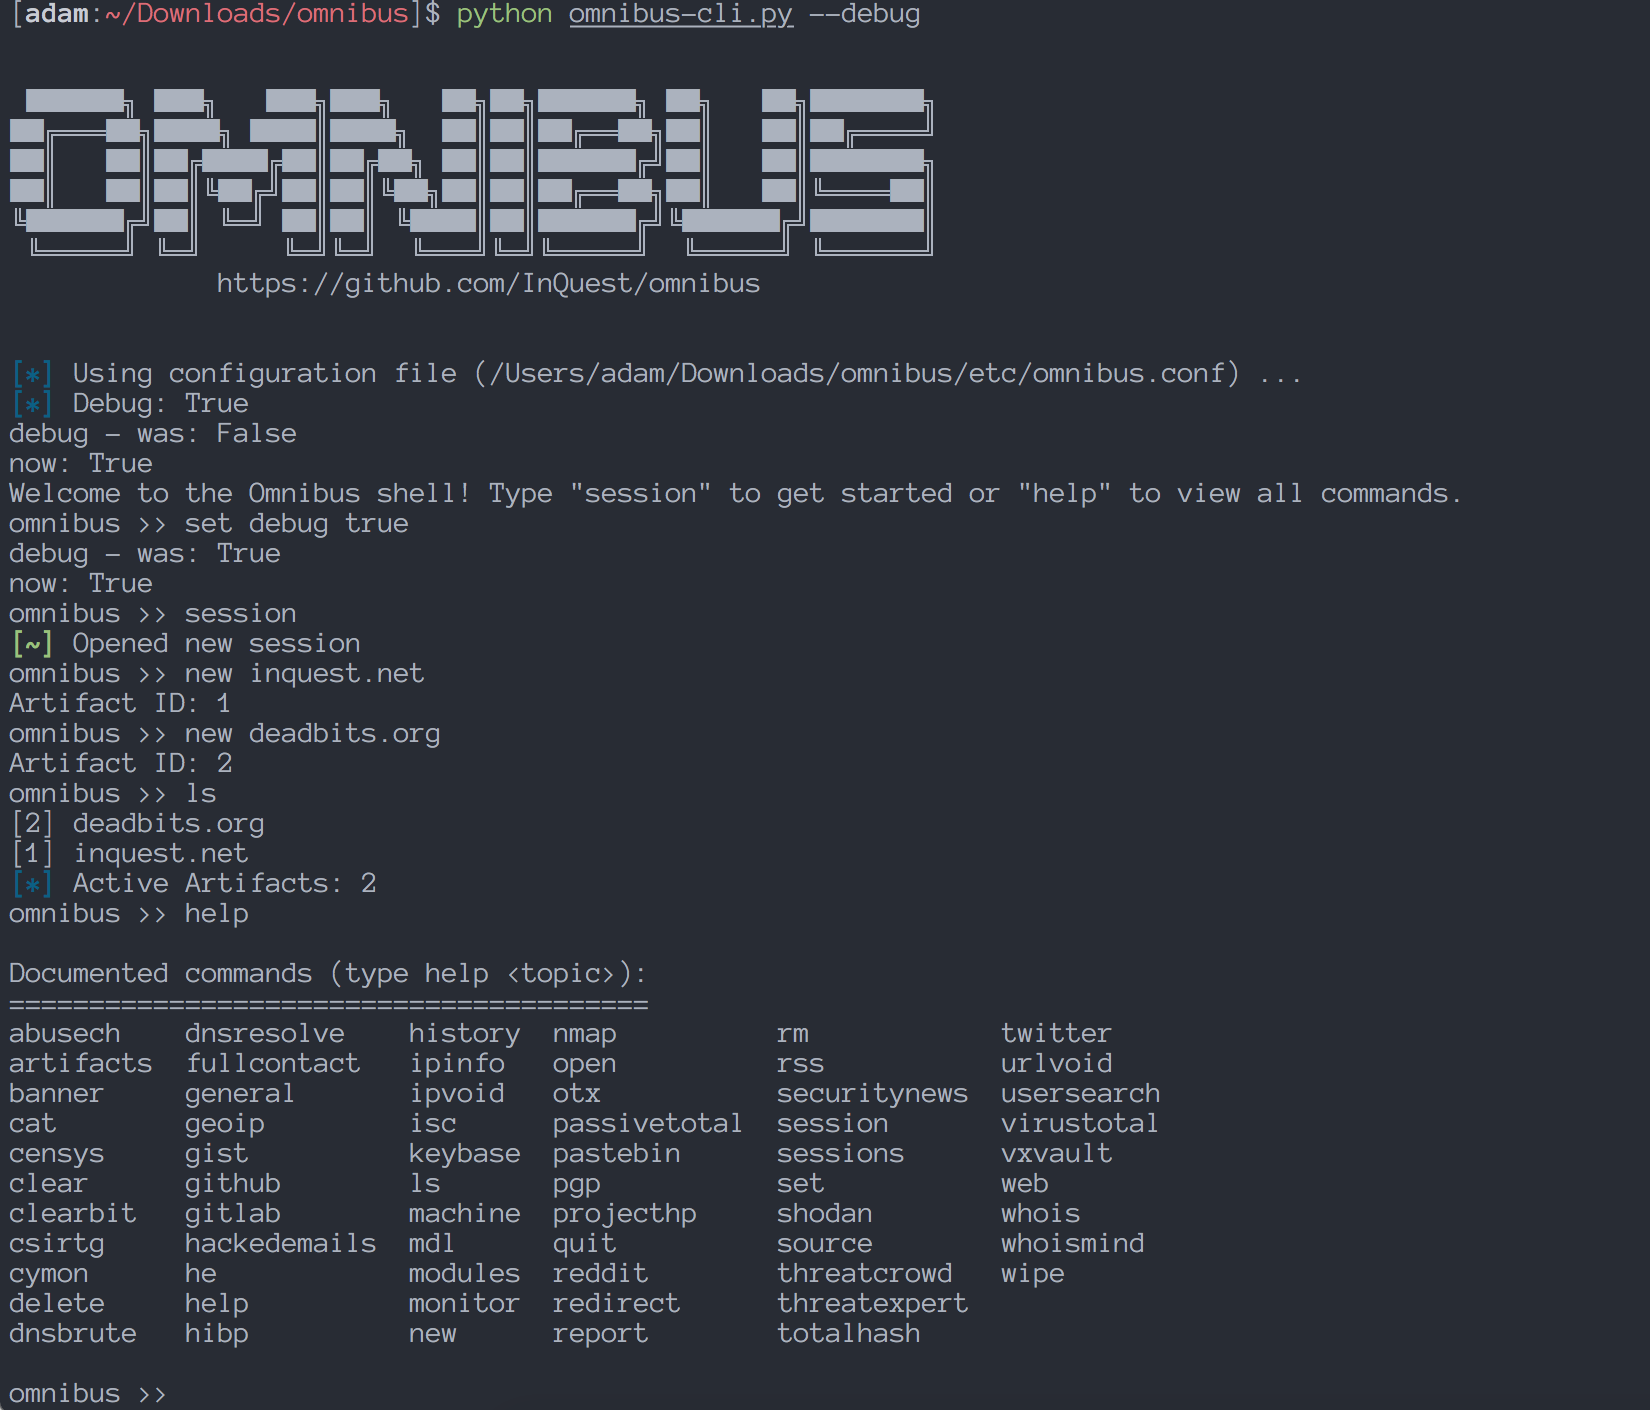
 ciscocsirt/gosint
The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 redhuntlabs/redhunt-os
Virtual Machine for Adversary Emulation and Threat Hunting
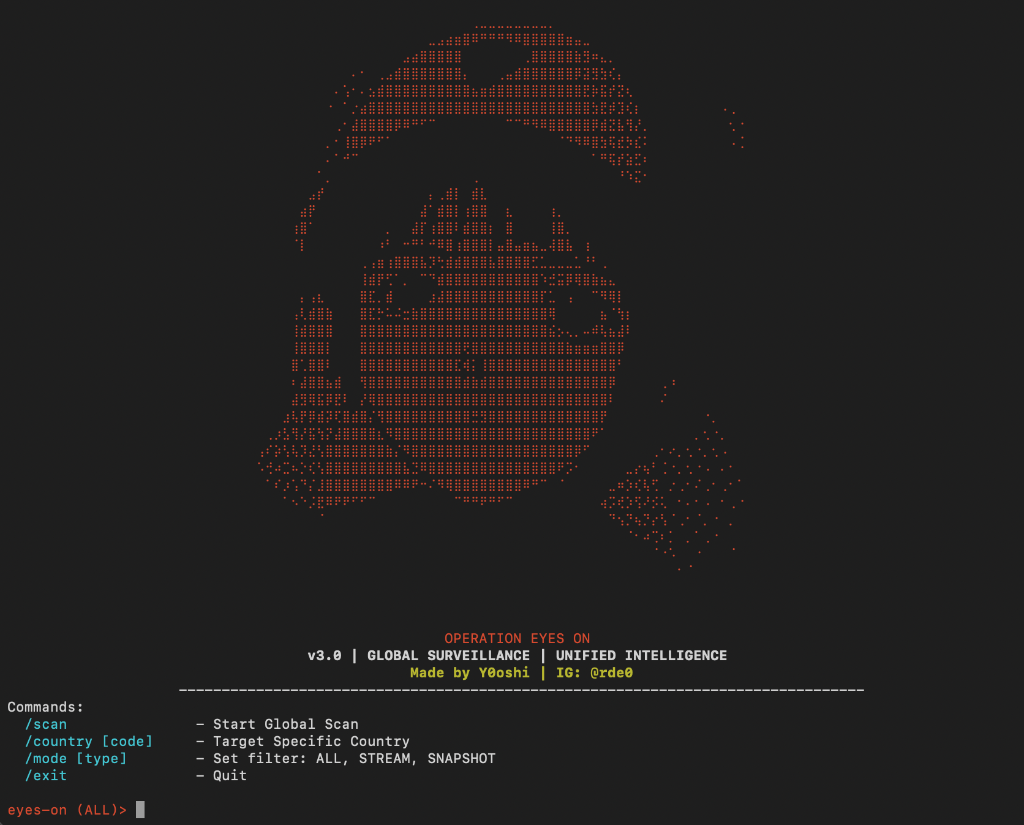 y0oshi/project-eyes-on
Project Eyes On is a high-speed, multi-threaded surveillance tool by Y0oshi (@rde0) for locating open IP cameras worldwide. Unifies Google Dorking…
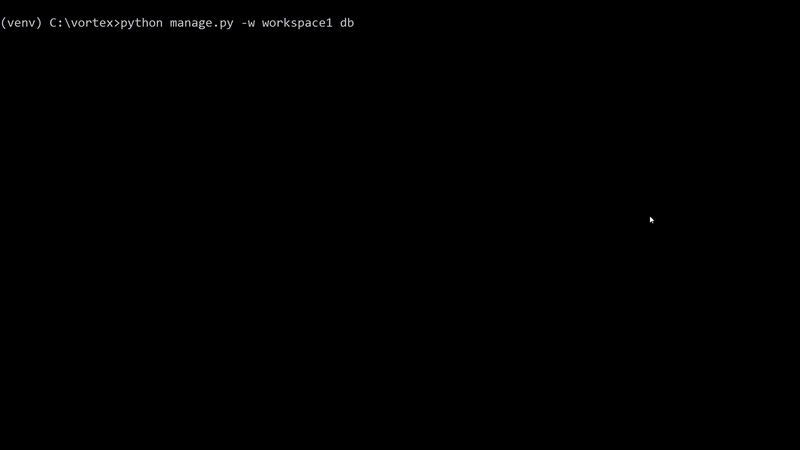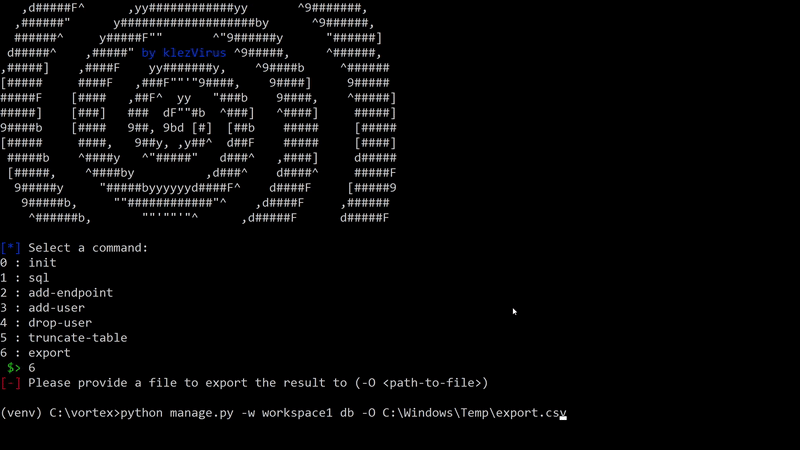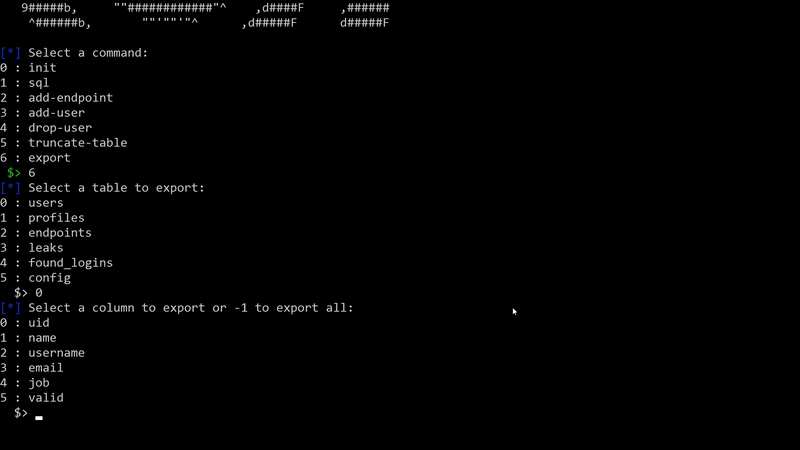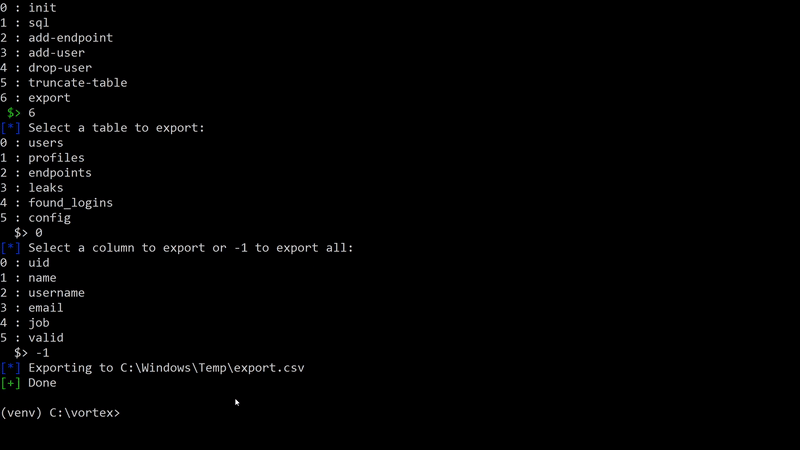 klezvirus/vortex
VPN Overall Reconnaissance, Testing, Enumeration and eXploitation Toolkit
 hackinglz/saas_enum
Command-line tool for discovering SaaS platforms a company uses via DNS enumeration
 hackinglz/saas_enum
Command-line tool for discovering SaaS platforms a company uses via DNS enumeration
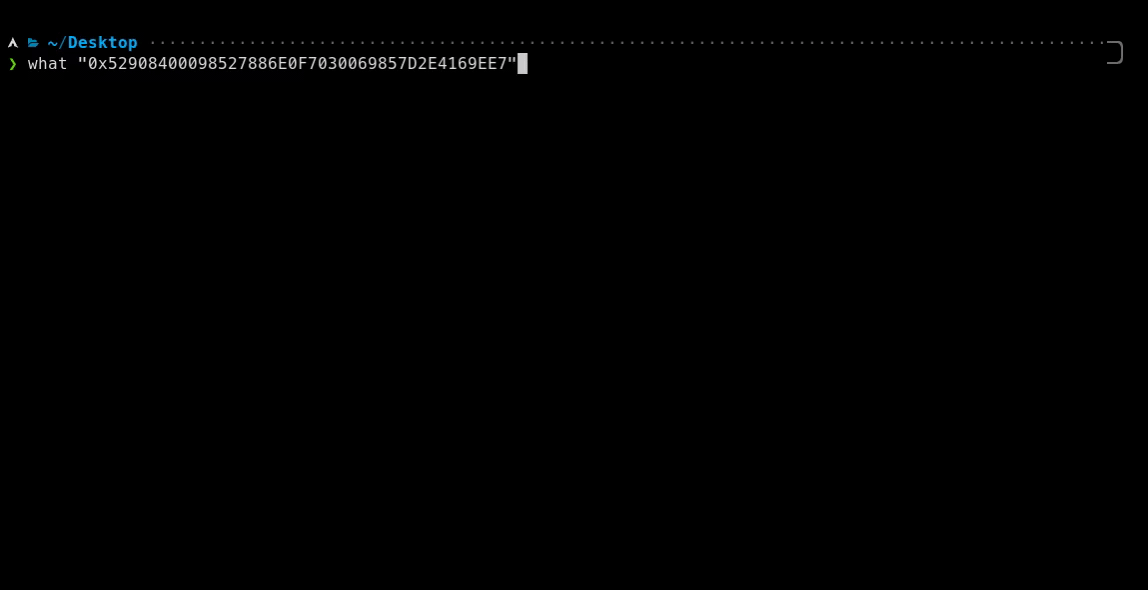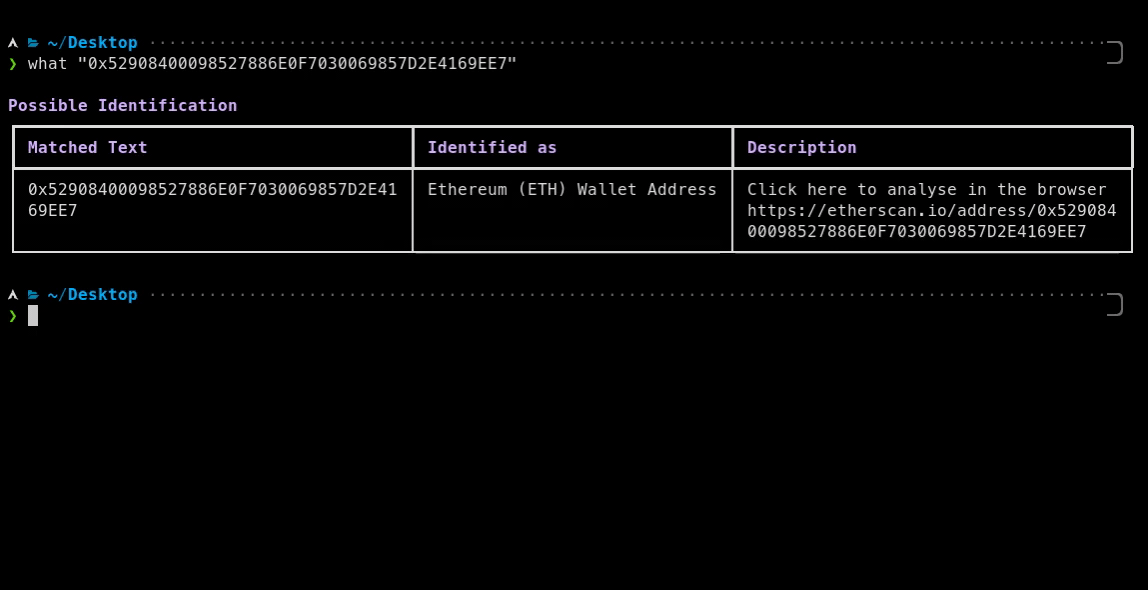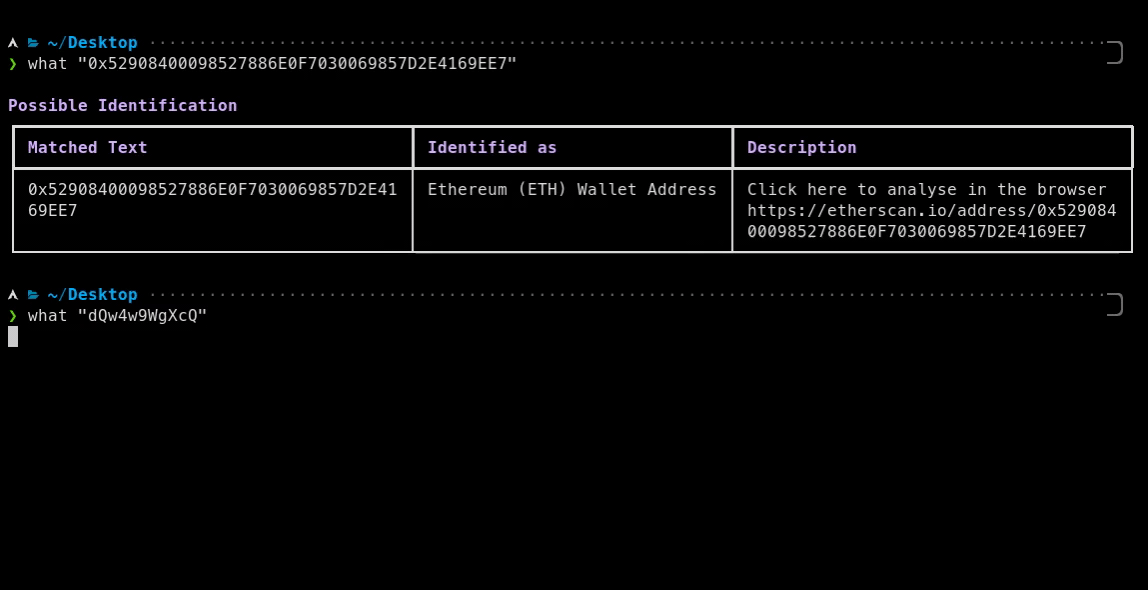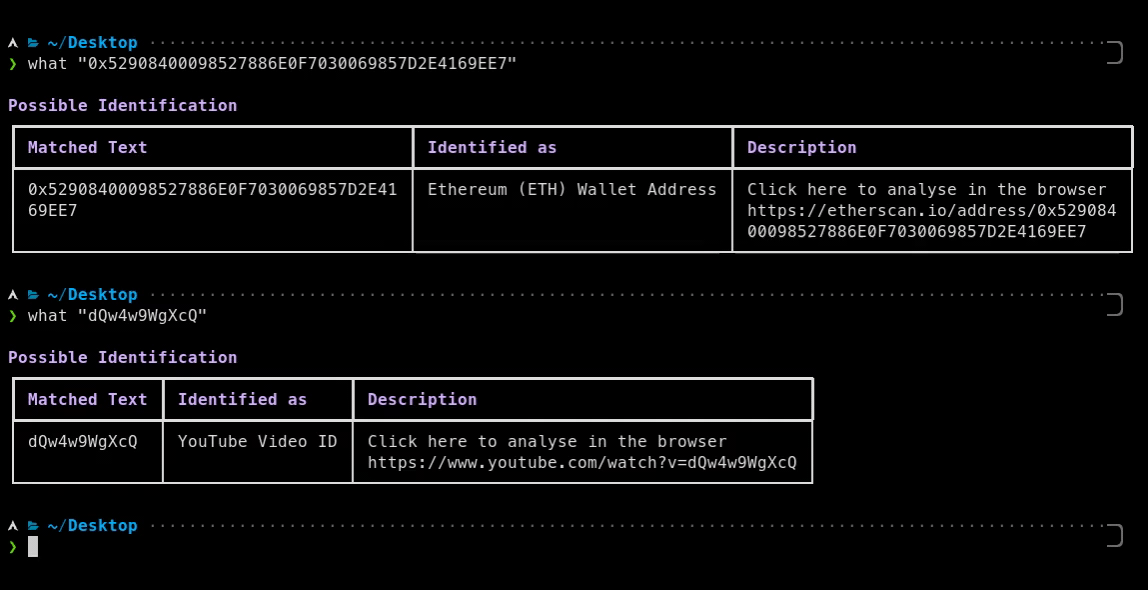 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
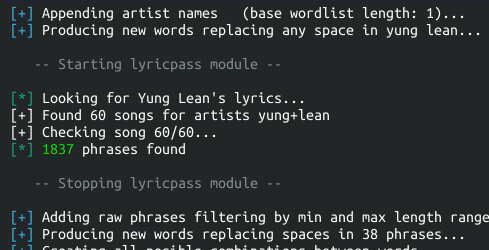 r3nt0n/bopscrk
Generates targeted password wordlists by combining personal info, applying case/leet transforms, and scraping artist lyrics for enhanced cracking…