ICS-TestBed-Framework

Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…

Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…

This repository contains a comprehensive security assessment of an enterprise LAN environment. The core focus of this project was the identification,…

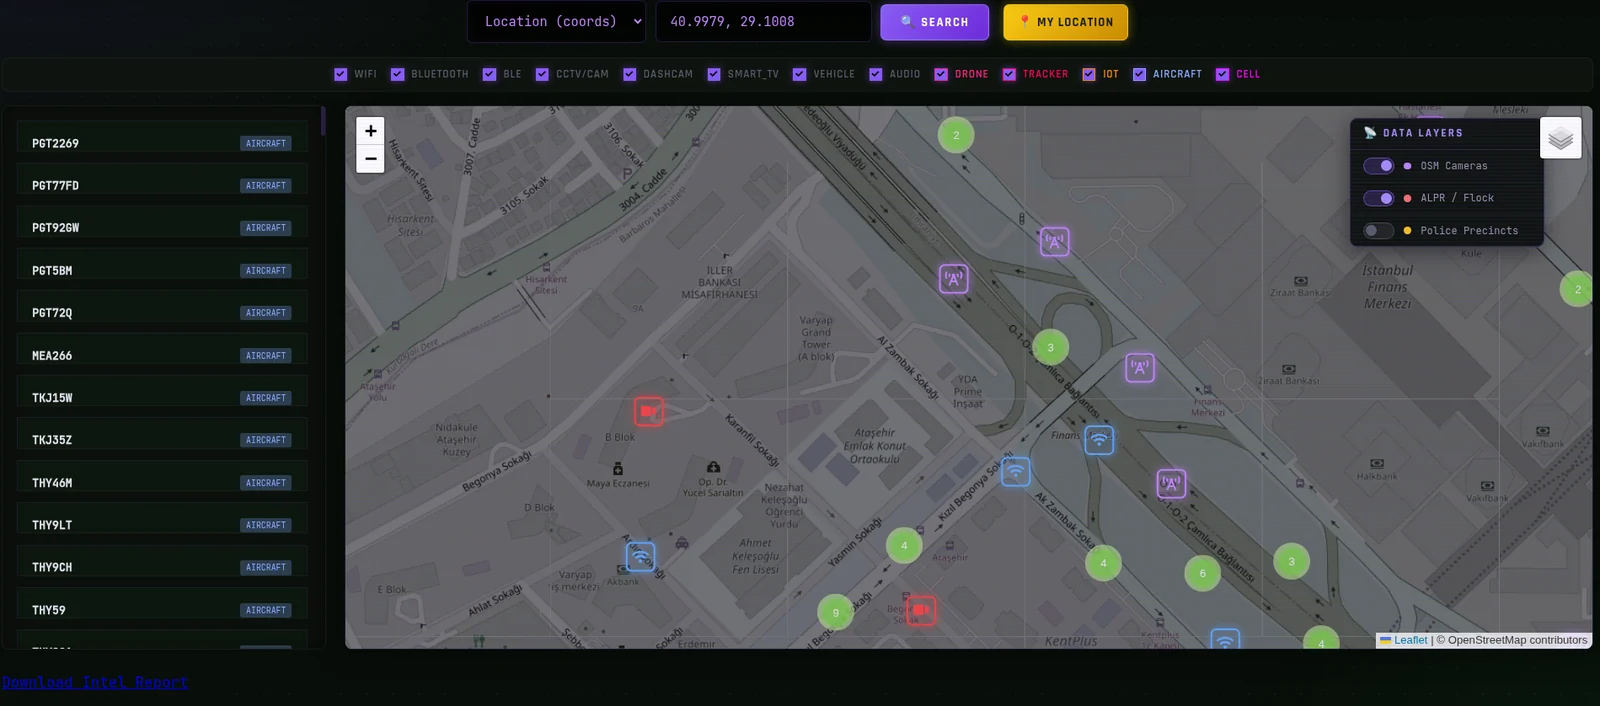
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…

Generates reproducible CORE network topologies from XML scenario files for cybersecurity training and experimentation. Provides Web GUI and CLI for…

Python script to detect CVE-2026-24061 telnetd vulnerability via NEW-ENVIRON injection, providing risk assessment and mitigation guidance.

Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…

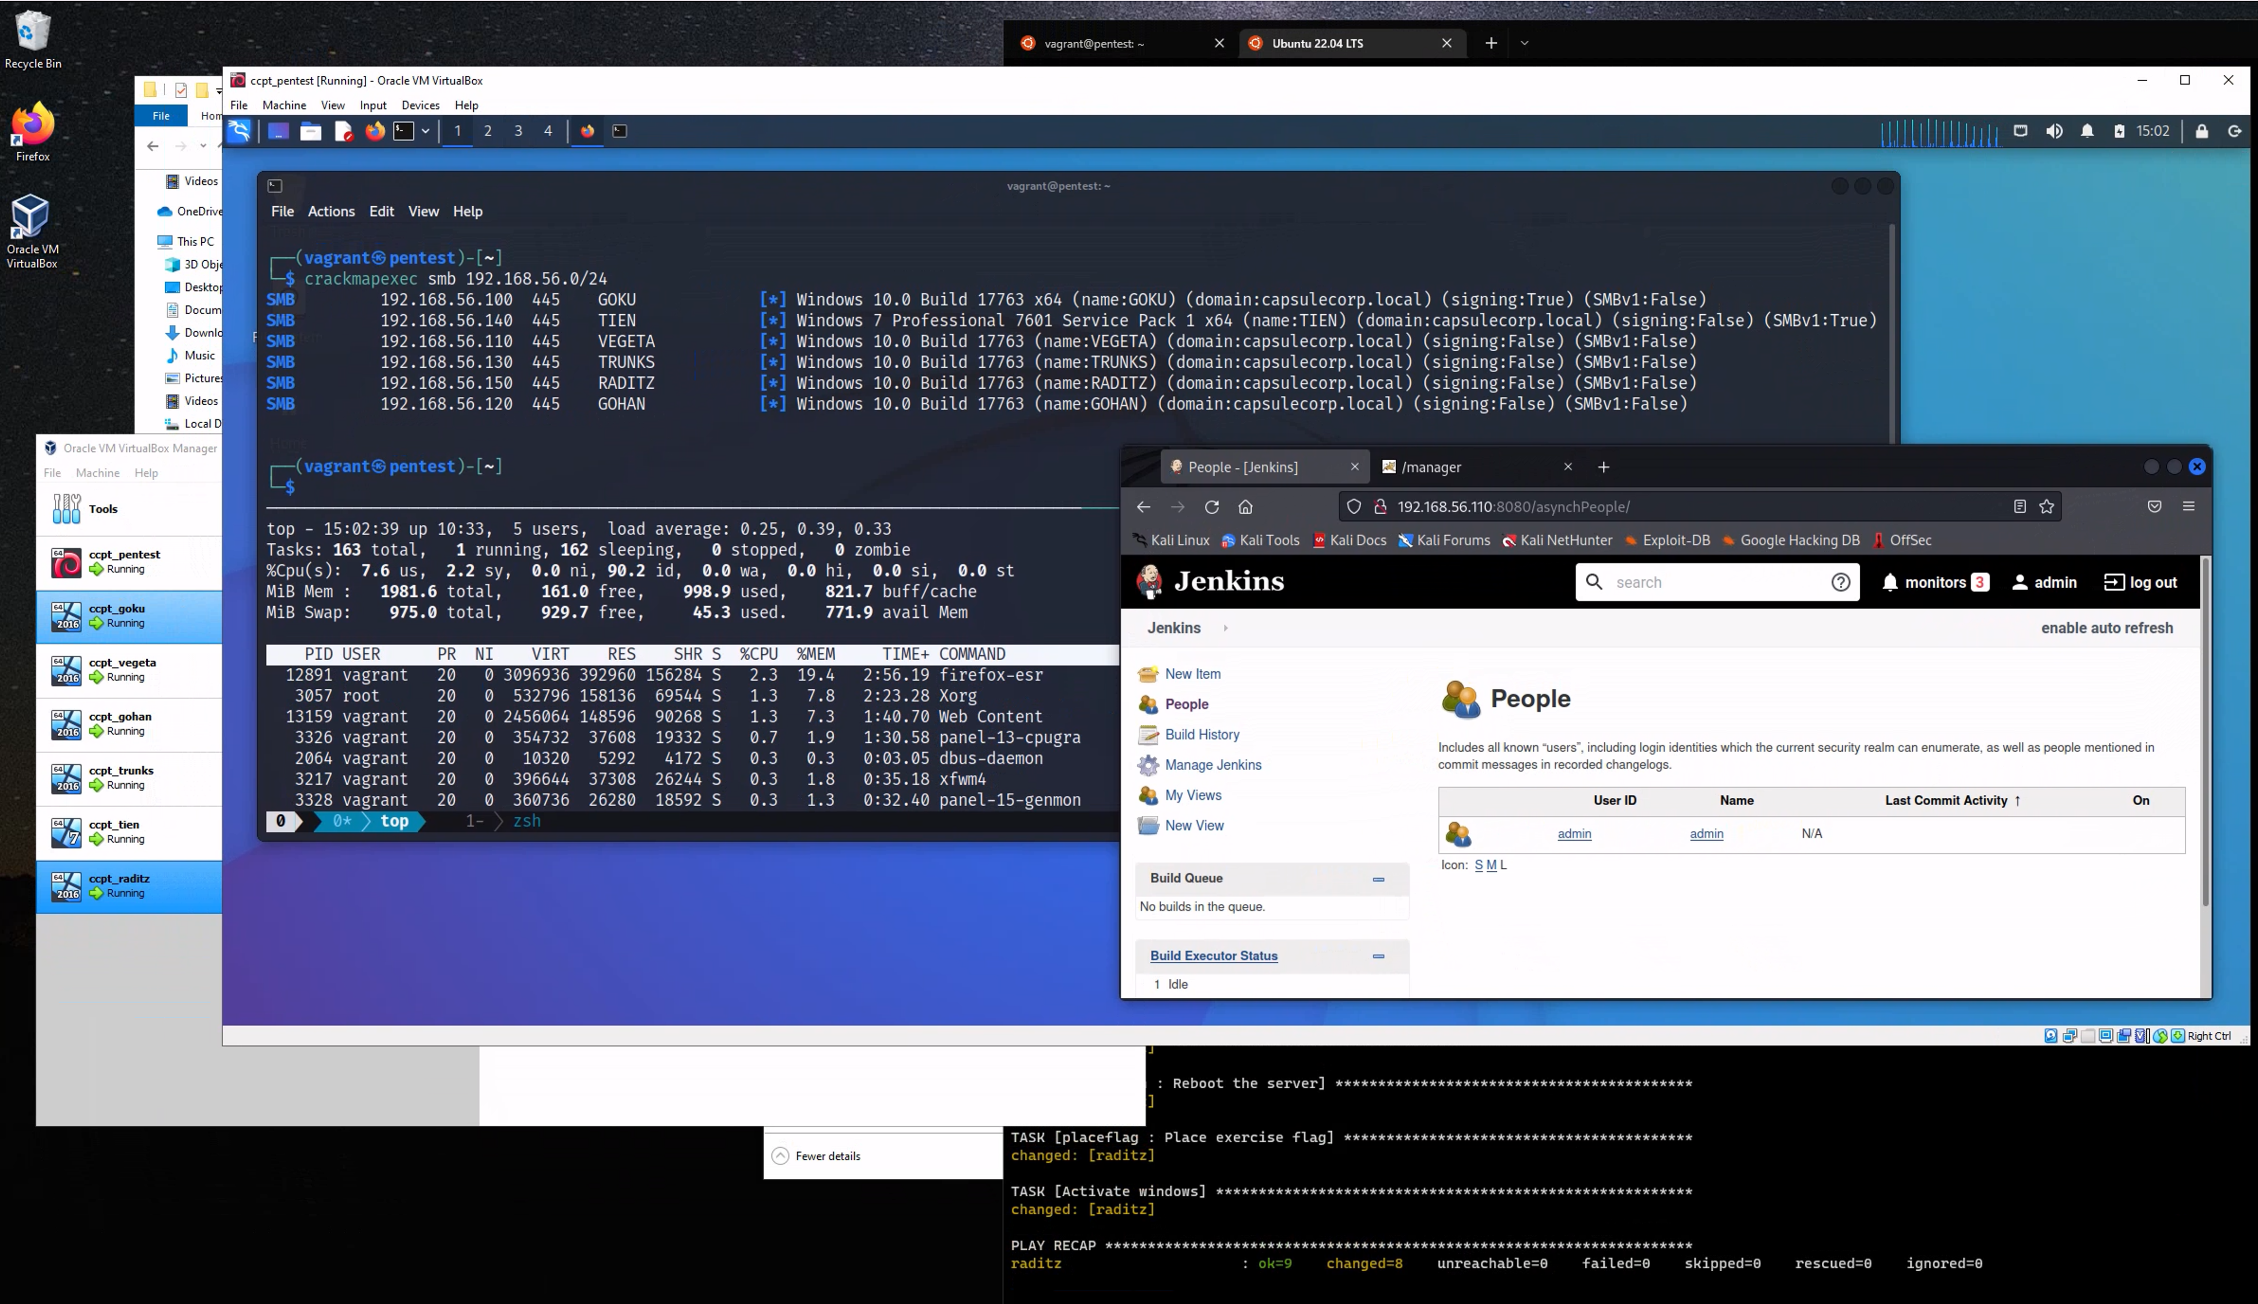
Vagrant VirtualBox environment for conducting an internal network penetration test

Tool to find common vulnerabilities in cryptographic public keys

Sets up a Docker-based Palo Alto firewall test environment and provides an exploit script to test CVE-2024-3400, enabling safe vulnerability…

Educational environment for LTAT.04.022 Homework 4.

Proof-of-concept exploit for CVE-2026-24061, a telnetd authentication bypass via argument injection in the USER environment variable, allowing…

A cybersecurity case study analysing CVE-2023-20198 in Cisco IOS XE, covering vulnerability exploitation, mitigation strategies, secure software…

BoNeSi - the DDoS Botnet Simulator

Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.

Controlled virtual attack & defense lab — CVE-2011-2523 exploitation, Nmap recon, Nikto scanning, UFW hardening on Metasploitable 2

Educational laboratory for studying CVE-2014-0160 (Heartbleed) and framing inconsistencies in TLS heartbeat handling.

IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.

Technical audit of Kioptrix Level 1. Focus: Samba 2.2.1a exploitation (CVE-2003-0201), manual enumeration, and internal infrastructure hardening.