cve-2026-32746-mitigation

Automated mitigation tool for CVE-2026-32746, providing atomic rollback, multi-firewall support (UFW, firewalld, nftables, iptables), and…

Automated mitigation tool for CVE-2026-32746, providing atomic rollback, multi-firewall support (UFW, firewalld, nftables, iptables), and…

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

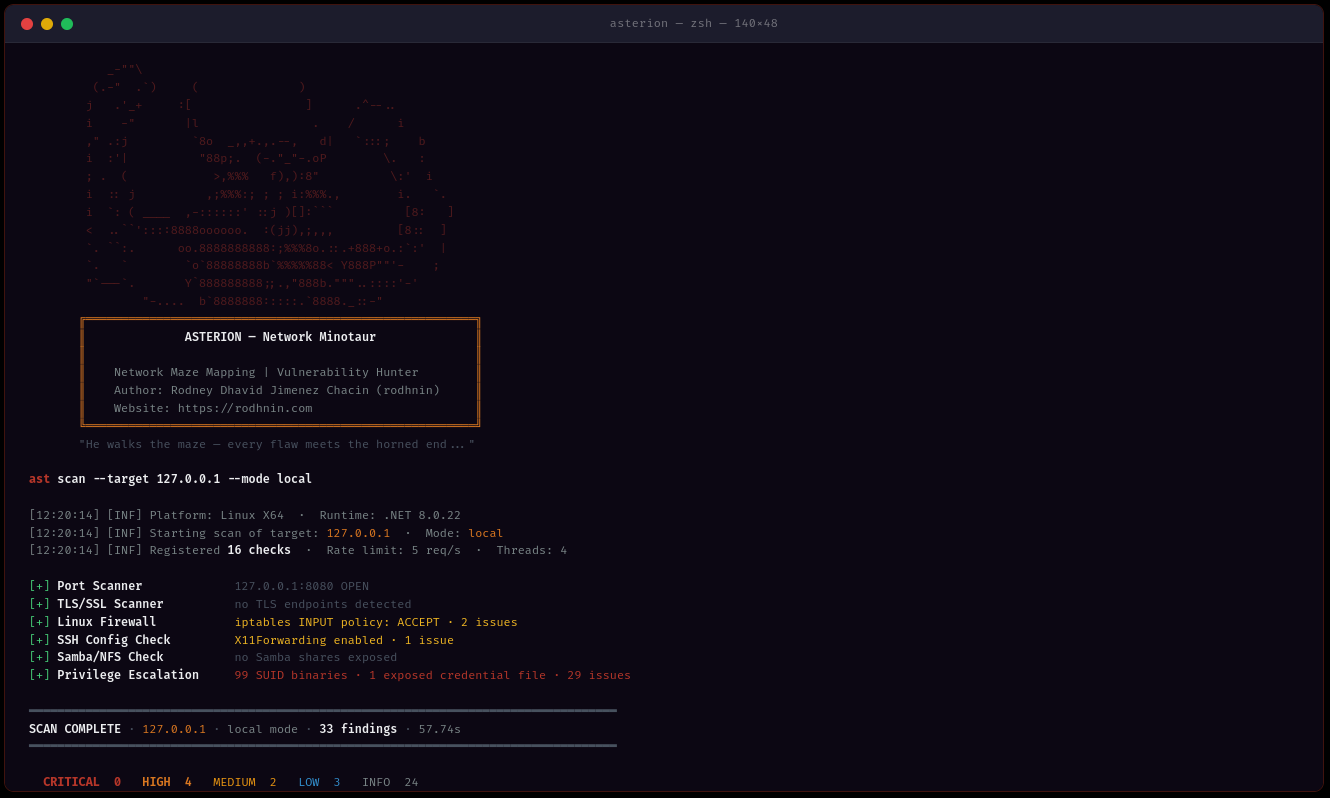
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…

Temporary eBPF/XDP mitigation for CVE-2026-98432 Linux TCP IPv4 header-options vulnerability. Helps protect unpatched systems and custom kernels…

Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…

ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.

CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

A Rust-based transparent Tor proxy that routes all system traffic through the Tor network enhanced security, proper DNS isolation, and modern Linux…

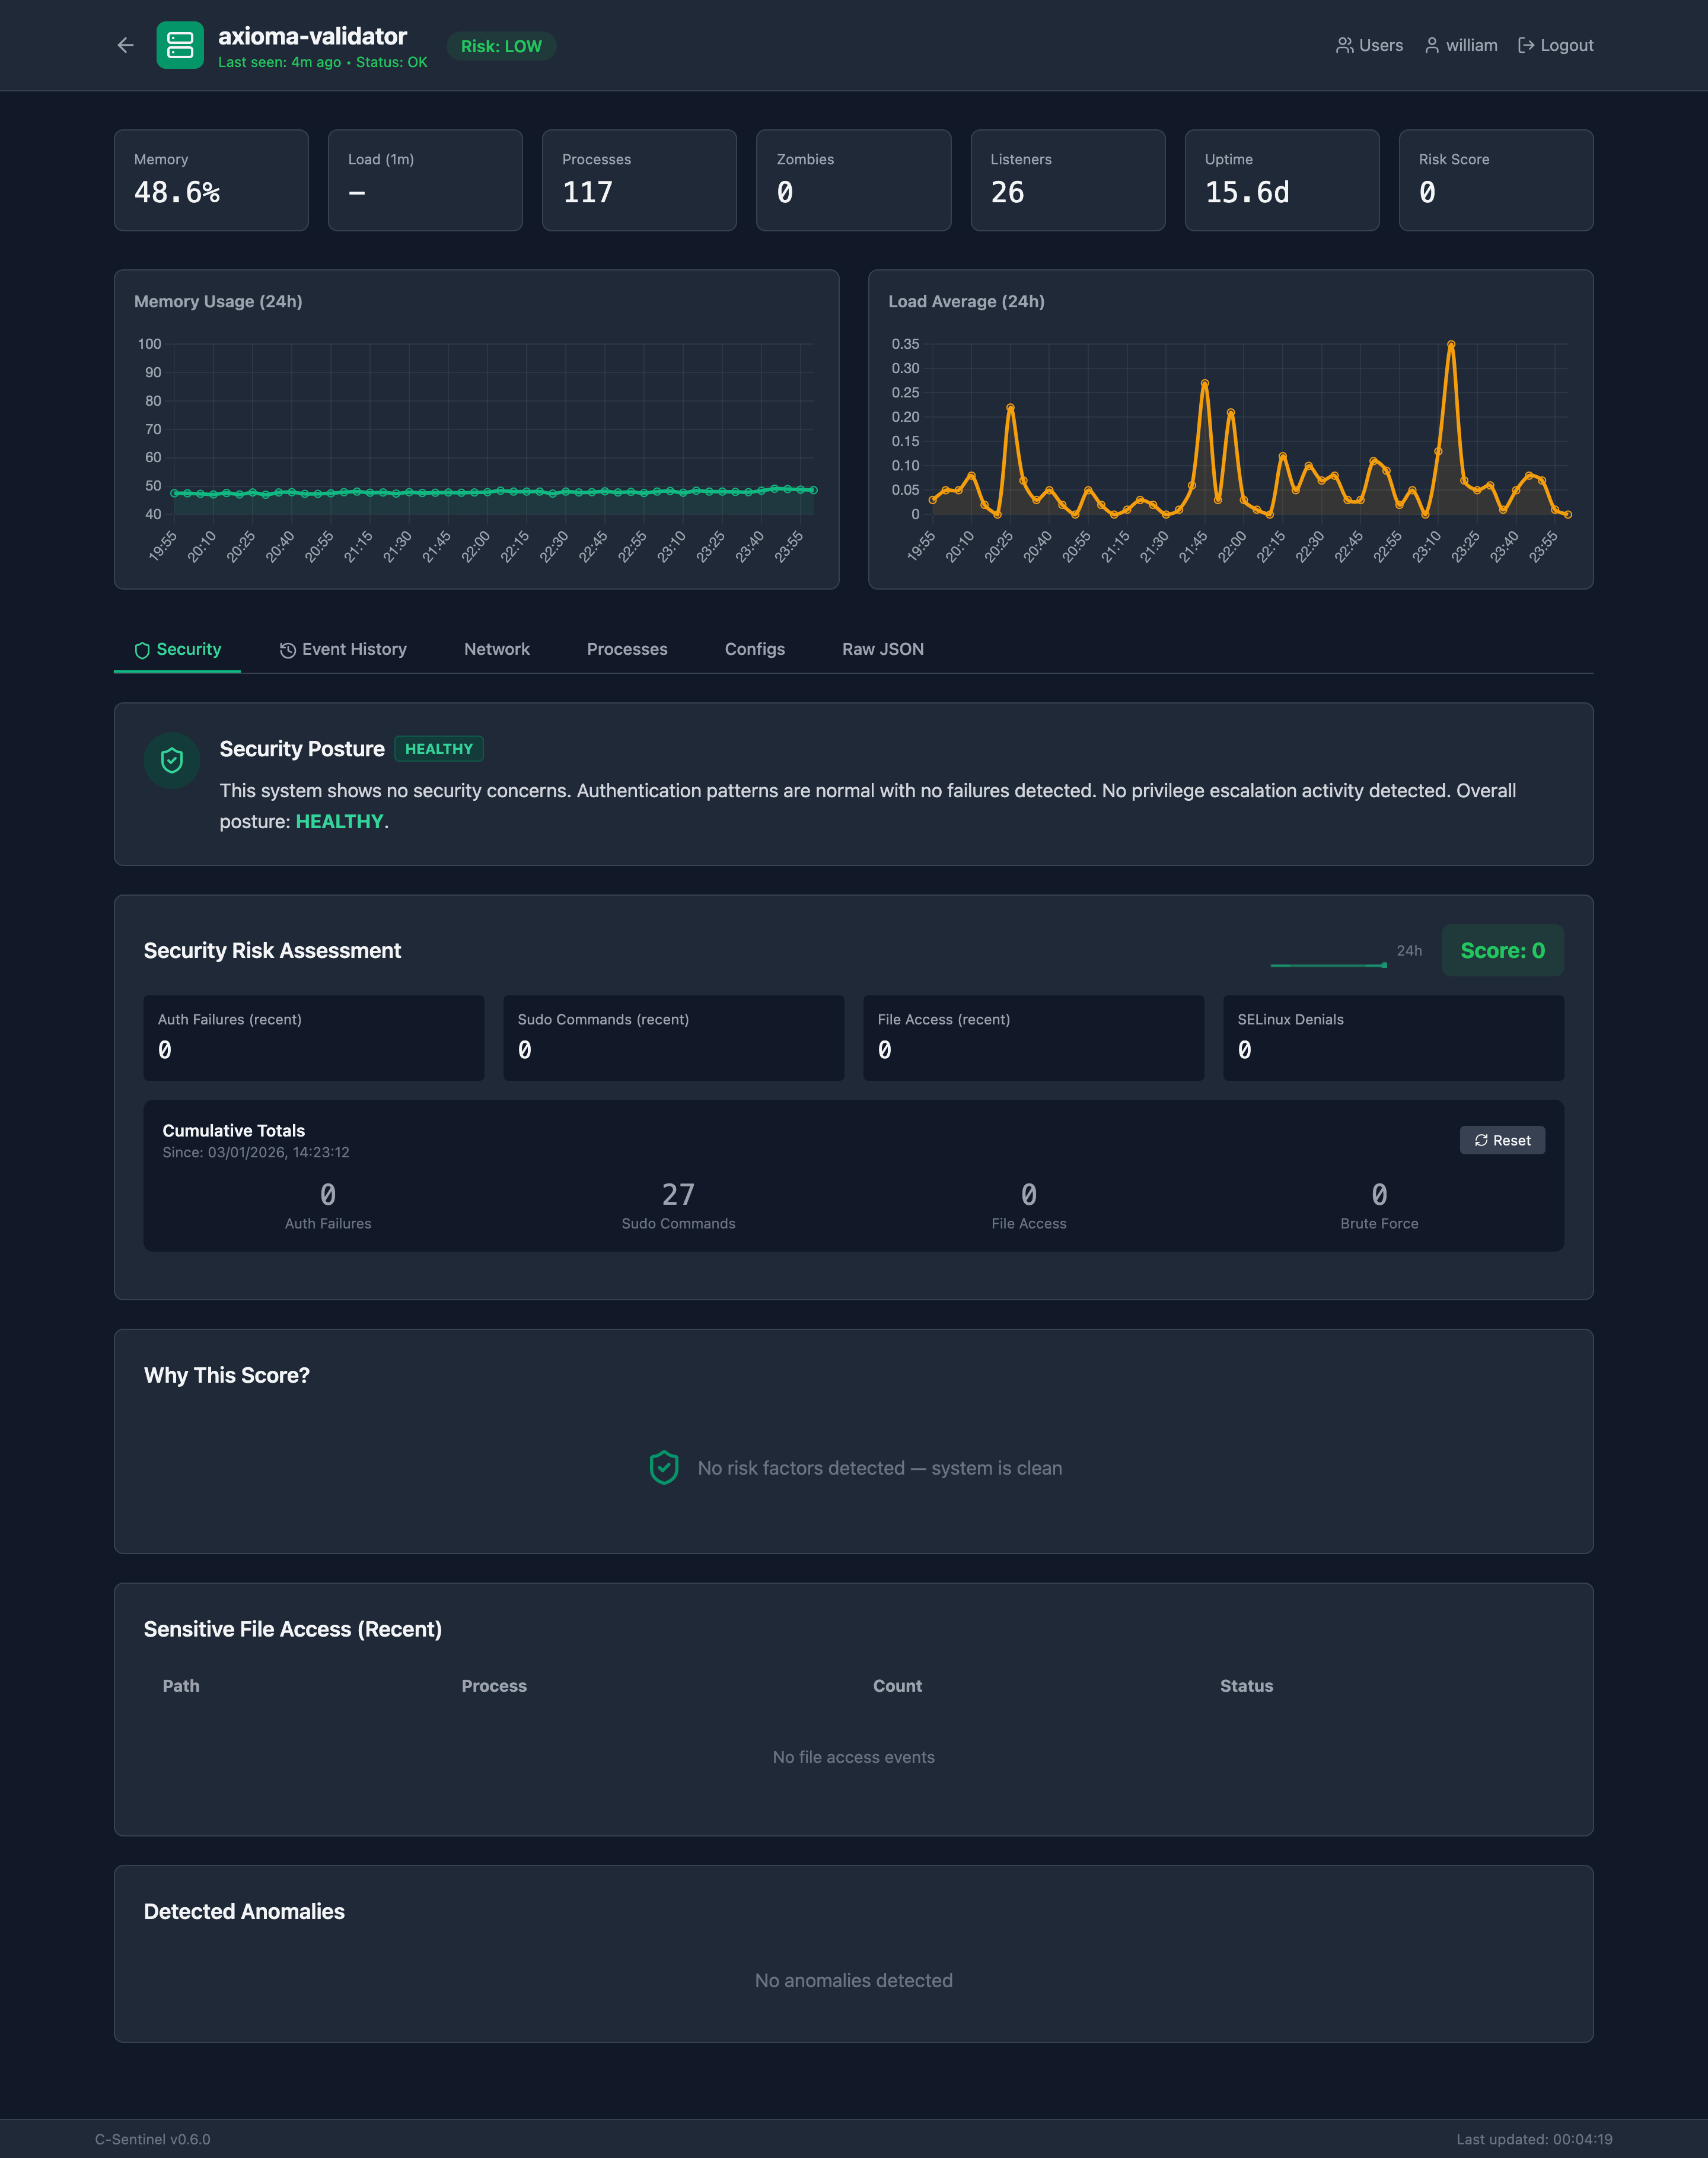
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.

SpookySSL CVE-2022-3602 SSLv3 Scanner for Windows, Linux, macOS

Laboratory toolkit for CVE-2026-98432 Linux TCP ireq_opt use-after-free: race trigger with heap-reuse oracle, leak parser, KASLR resolver, pcap…

Python proof-of-concept and C exploit generator for the Linux kernel TCP IPv4/MPTCP use-after-free (CVE-2026-98432), triggering a SYN retransmission…

PoC, non-destructive version scanner, KASAN crash verifier, and Suricata/Sigma detection rules for the Linux kernel TCP/IPv4 IP-options…

Go probe that reproduces the Linux IPv4 checksum-offload bug PwnEscape on a prepared TAP, injecting crafted virtio headers and verifying the…