
my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…

Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…

All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…

Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…

3D threat intelligence dashboard that visualizes malicious infrastructure from OSINT sources like AbuseIPDB and OpenPhish, with a live threat feed,…

Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.

Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…


Passive hybrid fingerprinting engine — identify hosts without sending a single packet

NetSpecter is a lightweight yet powerful asynchronous OSINT and reconnaissance engine built in Python.


Transparent proxy through Tor for Kali Linux OS

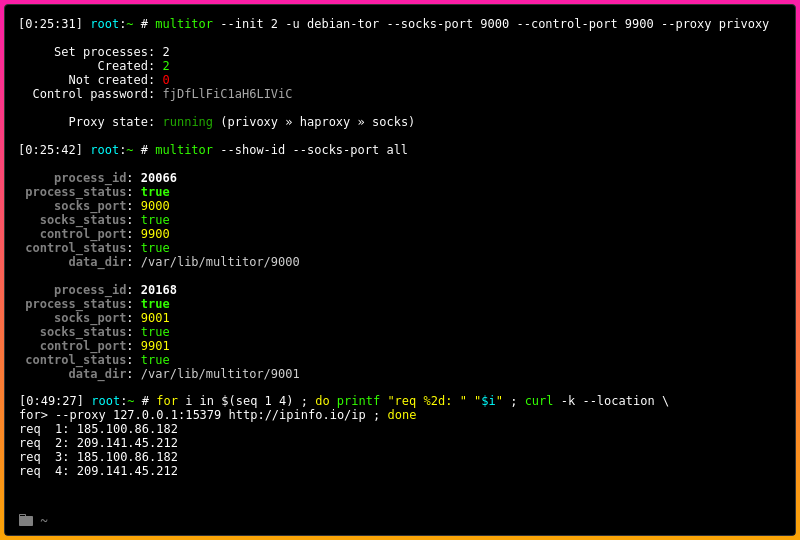
Create multiple TOR instances with a load-balancing.

Scripts to detect Fast-Flux and DGA using DNS query responses

Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…

Shodan-based scanner that discovers FortiGate SSL VPN devices and tests them for CVE-2024-21762 vulnerability, displaying organization and country…