

pacemaker
 lekensteyn/pacemaker
Heartbleed (CVE-2014-0160) client exploit
cryptographyexploitationnetwork-security+3
33010 years ago
lekensteyn/pacemakerHeartbleed (CVE-2014-0160) client exploit
 cerbrutus-bruteforcer/cerbrutus
Network brute force tool, written in Python. Faster than other existing solutions (including the main leader in the network brute force market).
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 strozfriedberg/ssh-weak-dh
Audits SSH servers for weak Diffie-Hellman key exchange groups by testing multiple client configurations, identifying Logjam-vulnerable endpoints…
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 magisterquis/sshhipot
High-interaction MitM SSH honeypot
 nccgroup/bkscan
BlueKeep scanner supporting NLA
 ociredefz/vsaudit
VOIP Security Audit Framework
 smythtech/sdnpwn
An SDN penetration testing toolkit
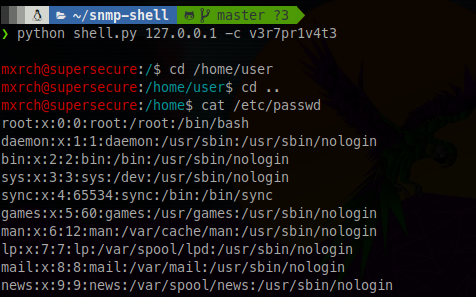 mxrch/snmp-shell
Shell Simulation over Net-SNMP with extend functionality
 nccgroup/datajackproxy
Datajack Proxy allows you to intercept TLS traffic in native x86 applications across platforms
 rofl0r/nat-tunnel
NAT Tunnel: to effortlessly serve from behind NAT
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 xen0bit/netprobe-cve-2026-98432
Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
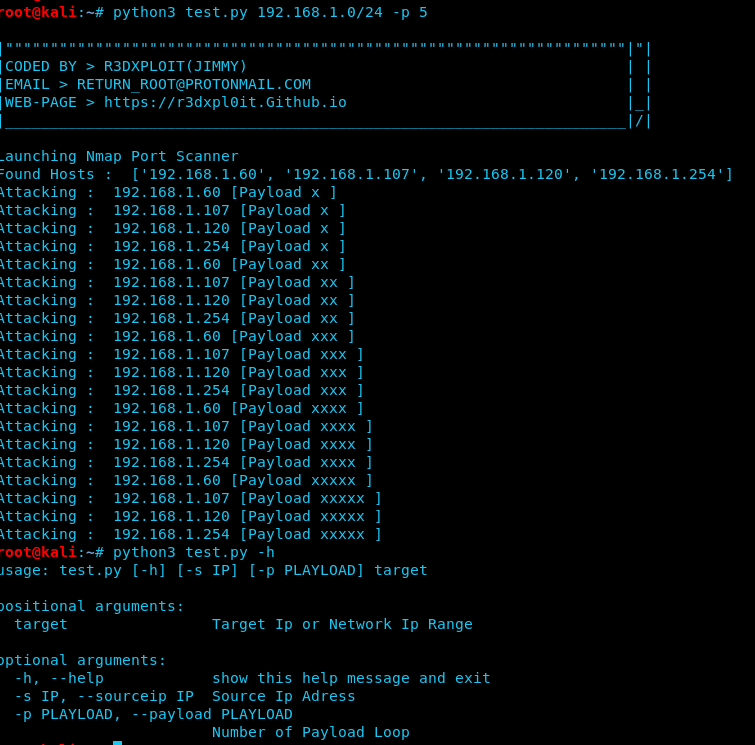 r3dxpl0it/cve-2018-4407
IOS/MAC Denial-Of-Service [POC/EXPLOIT FOR MASSIVE ATTACK TO IOS/MAC IN NETWORK]
 corelight/ecs-templates
Corelight or Zeek Elastic Common Schema Templates
 dag-erling/kexkill
SSH KEXINIT flood tool exploiting CVE-2016-8858 to trigger memory exhaustion in vulnerable OpenSSH servers. Proof-of-concept for denial-of-service…
 corelight/zeek-elf
A Zeek ELF File Analyzer