Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
vsaudit — VOIP Security Audit Framework | Kitploit
Tools/GitHubGitHub/ociredefz/vsaudit
Vulnerability ScannersExploitationNetwork SecurityPenetration Testing
GitHubociredefz/vsaudit

vsaudit

VOIP Security Audit Framework

View Repository
10936958 years agoReviewed by Kitploit
Share

vsaudit

This is an opensource tool to perform attacks to general voip services It allows to scans the whole network or single host to do the gathering phase, then it is able to search for most known vulnerabilities on the founds alive hosts and try to exploit them.

Install dependencies

To start using vsaudit you must install the 'bundler' package that will be used to install the requireds gem dependencies through the Gemfile.

Download directly from website:

http://bundler.io/

Or install with 'gem' (ruby package manager) with:

deftcode ~ $ gem install bundler

After that the installation has been completed, run (in the directory where is located vsaudit):

deftcode vsaudit $ bundle

Now you can start vsaudit with:

deftcode vsaudit $ ruby vsaudit.rb

NOTE: If you get an error with gem, you need to install the ruby-dev and libssl-dev packages (kali-linux: apt install ruby-dev libssl-dev).
Environment commands

  • Display the available options that can be set
  • List the environment variables
  • Get the value of environment variable
  • Set or change the environment variables

Audit commands

  • Check mistakes in the local configuration files
  • Scan a local o remote network
  • Enumerate the extensions
  • Bruteforce extensions
  • Get the live network traffic
  • Intercept the network traffic by custom bpf

Informations commands

  • Get informations about modules or address
  • Show the report list
  • Show the extensions list

Global commands

  • Display the help message
  • Quit from the framework

Screenshots

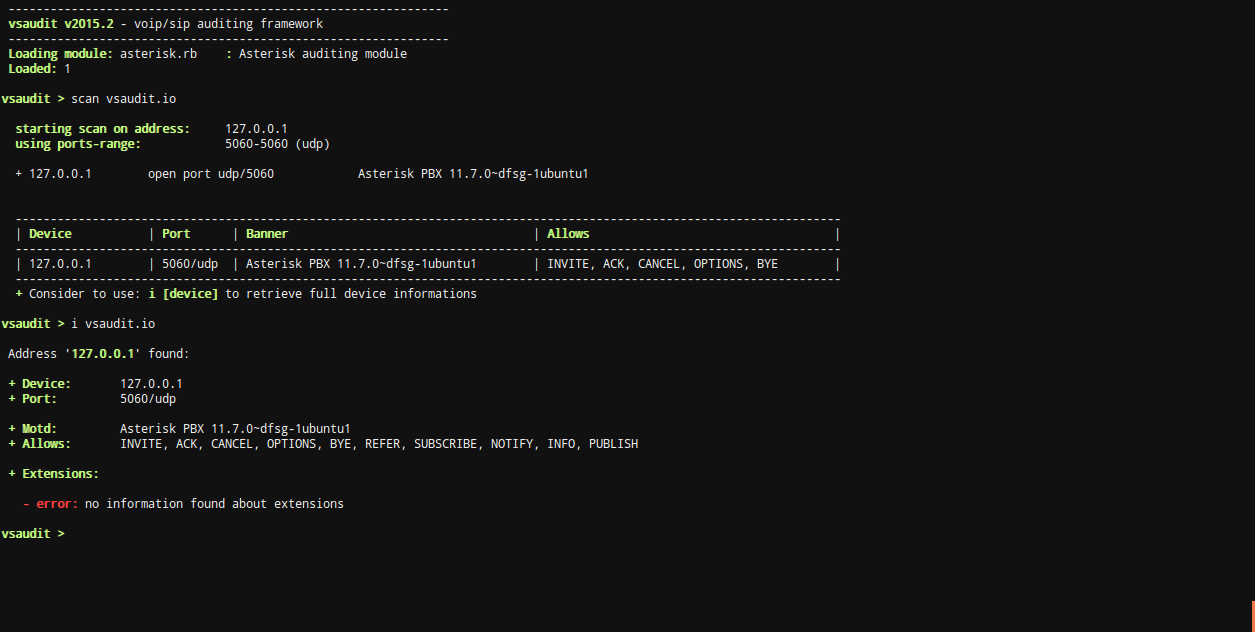
vsaudit - scanner

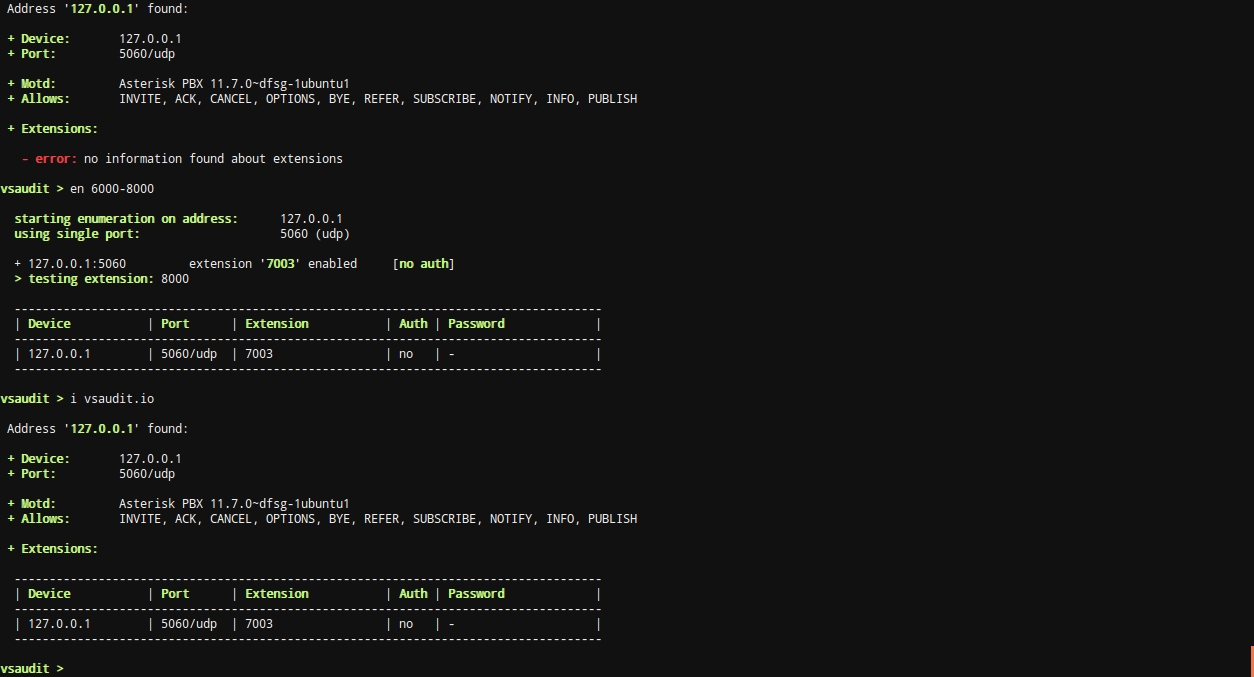
vsaudit - enumeration

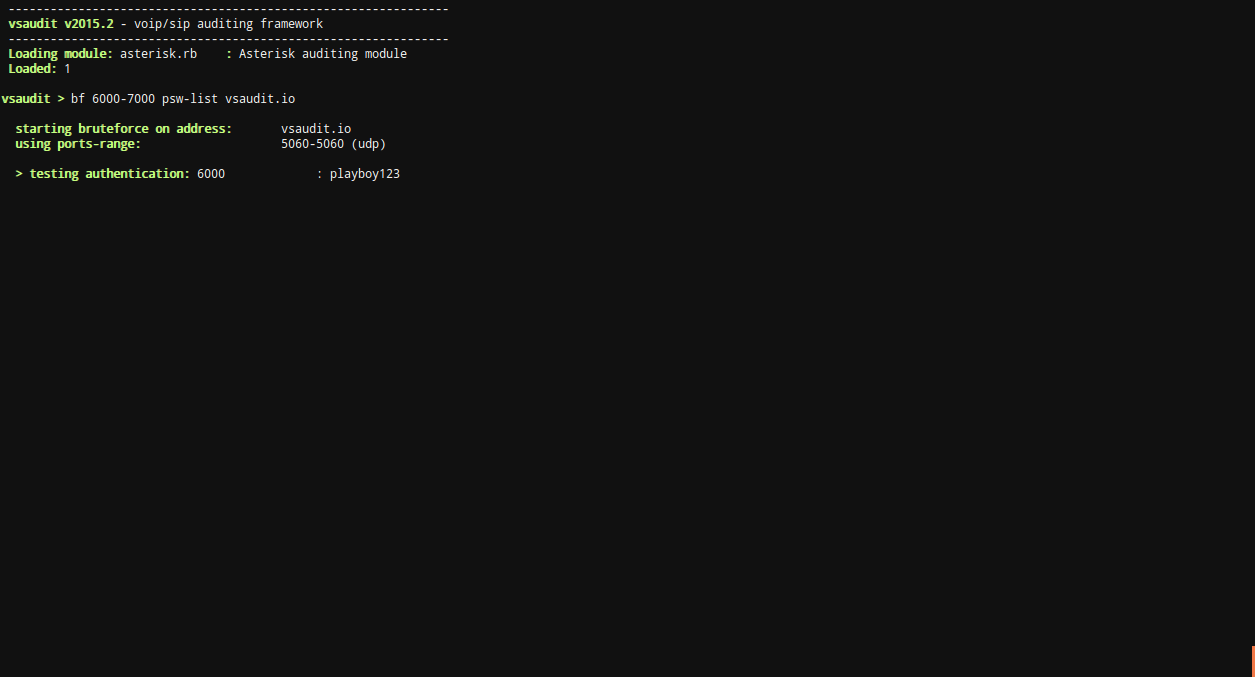
vsaudit - bruteforce

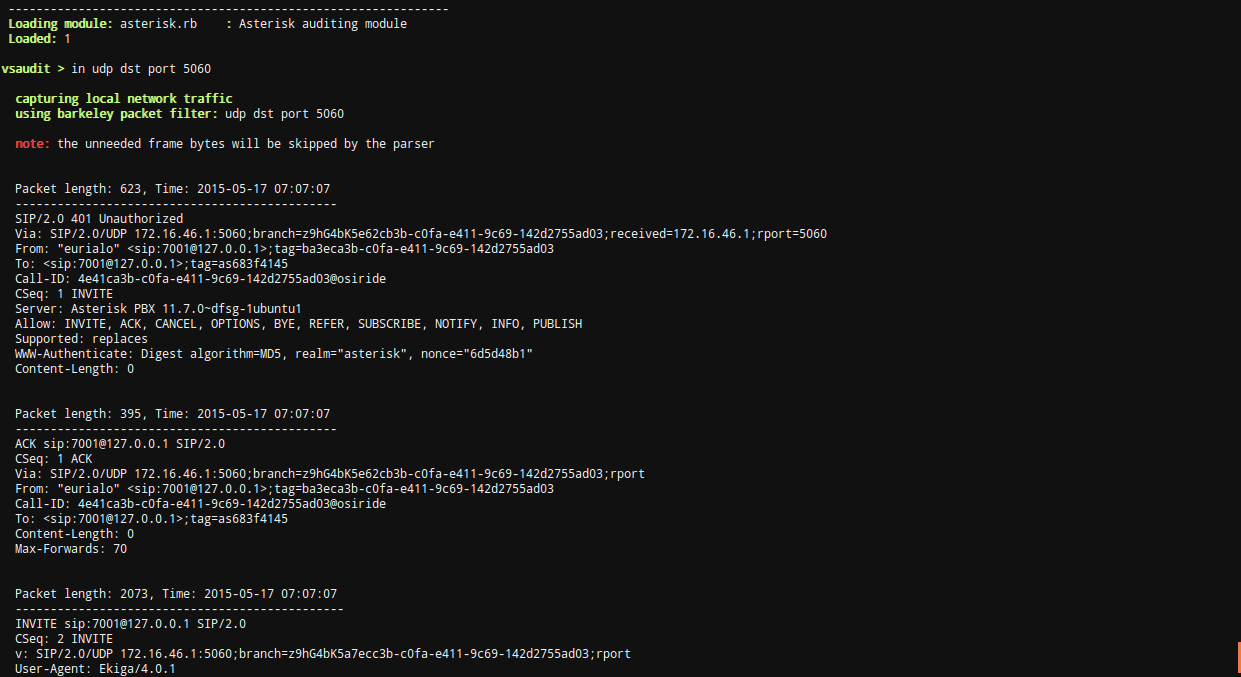
vsaudit - intercept

Reference

  • Manual: http://deftcode.ninja/post/vsaudit-voip-security-audit-framework
  • RFC-3261 (SIP - Session Initiation Protocol): https://www.ietf.org/rfc/rfc3261.txt
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →