gitlab-cve-2026-85706-ioc

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

Safely detect Citrix NetScaler SAML auth bypass CVE-2026-19490

SSRF via smtplib raw TCP sockets bypassing HTTP blocklist in AutoGPT SendEmailBlock

CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit

Multithreaded Modbus/TCP detection scanner written in C using libmodbus.

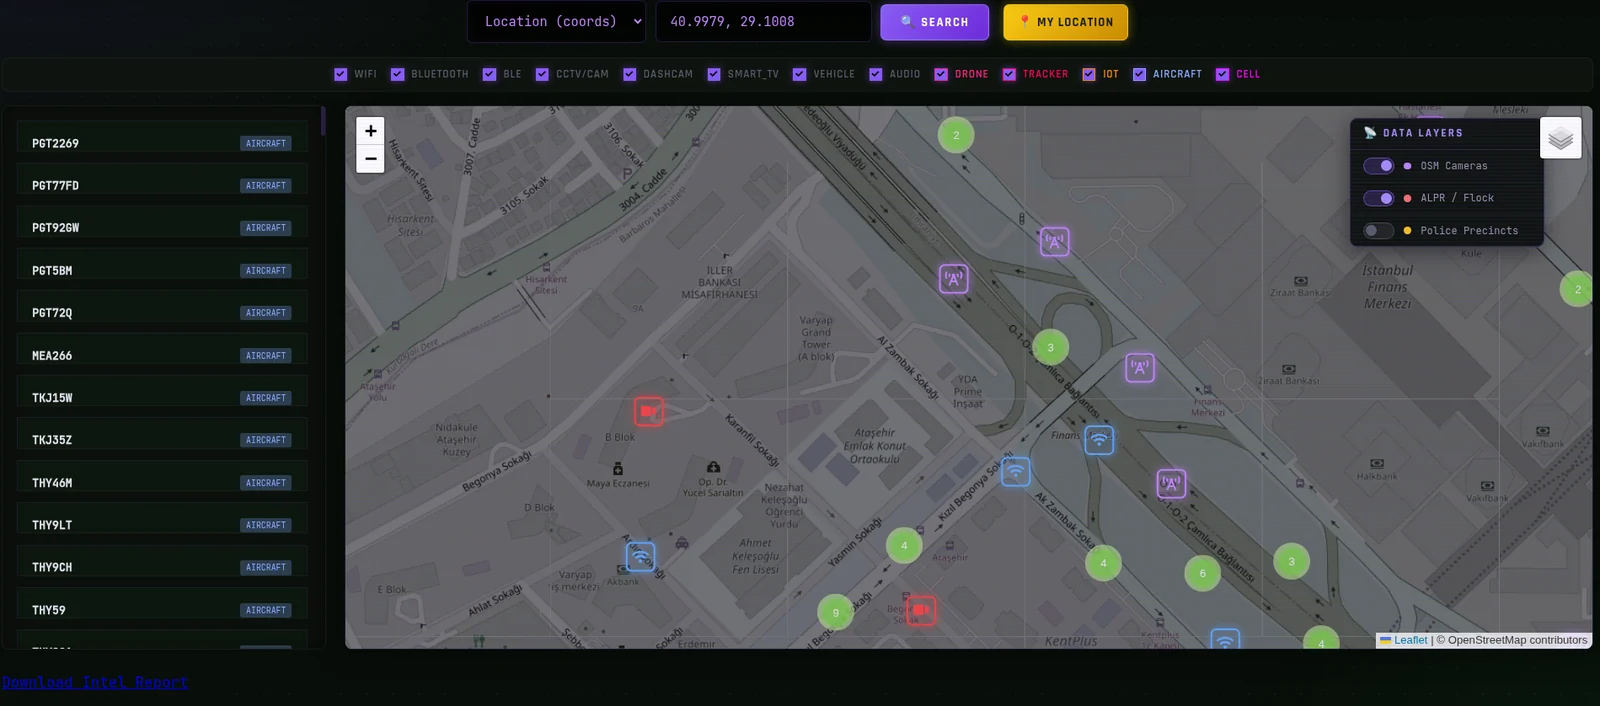
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…

Does This Look Like An Honeypot? (DTLLAH) Multi-protocol CLI that fingerprints whether a target IP behaves like a low-interaction honeypot — Shodan…

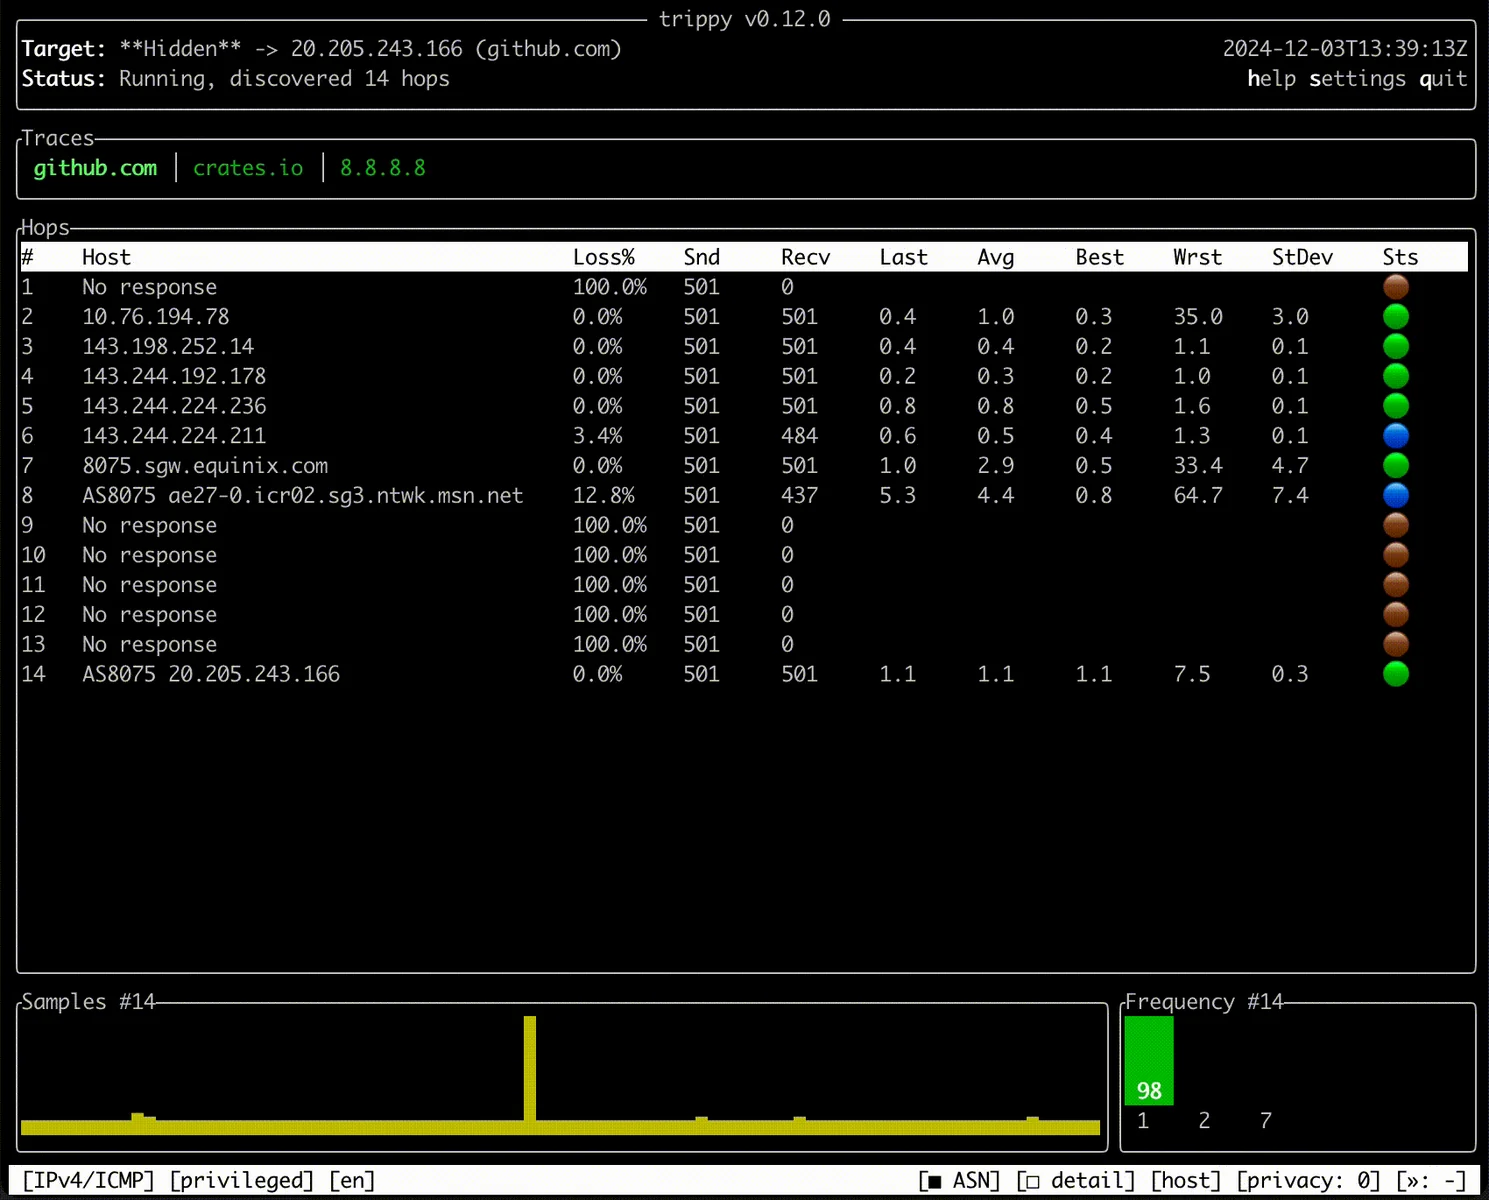
A network diagnostic tool combining traceroute and ping for analyzing network paths, latency, and packet loss with an interactive terminal UI.

Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥

Python client for dnsdumpster.com to retrieve DNS records, subdomains, and network maps for reconnaissance and security research.

Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…

A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.

Network asset discovery and scanning client that integrates nmap and masscan for large-scale asset identification, port scanning, and vulnerability…

Non-destructive exposure survey tool for assessing PAN-OS User-ID Authentication Portal surfaces related to CVE-2026-0300, performing safe HTTP(S)…

IP CIDRs (presumably as input, maybe command line or file) and checks ports 2083 and 2087 for openness

Scans internet-exposed cPanel/WHM instances for CVE-2026-41940 authentication bypass, probing HTTPS on port 2087 and matching response markers to…

AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…

Passive reconnaissance and fingerprinting tool for detecting FreeScout deployments and analyzing exposure related to CVE-2026-28289, aiding…