
cve-2026-19553-wrap-bio
 abraxas/cve-2026-19553-wrap-bio
Proof-of-concept lab reproducing CVE-2026-19553, where CPython ssl.SSLContext.wrap_bio() silently skips TLS hostname verification when…
cryptographyeducationexploitation+4
abraxas/cve-2026-19553-wrap-bioProof-of-concept lab reproducing CVE-2026-19553, where CPython ssl.SSLContext.wrap_bio() silently skips TLS hostname verification when…
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 gagaltotal/cve-2026-mikrotik-poc
CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 horkimhab/cve-2026-68121
Proof-of-concept for CVE-2026-68121 (PPPoEject), providing a Python exploit implementation for authorized security research and lab testing.
 mrgoofydev/zx-ddos
Python-based DDoS stress testing tool for educational and authorized network security evaluation, supporting configurable workers and request counts.
 raniaemran/cve-2024-36401-security-simulator
Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…
 l1lf1ng3r/heartbleed-vulnerability-exploitation
hands on investigation of the heartbleed vulnerability (CVE-2014-0160).
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 muhammad-usama-sardar/intra-handshake-fail
Early Attestation Considered Very Harmful (CVE-2026-92701, CVE-2026-92702, CVE-2026-33697, and more to come)
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
 mngunibanda1-prog/jozini-network-scanner
Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.
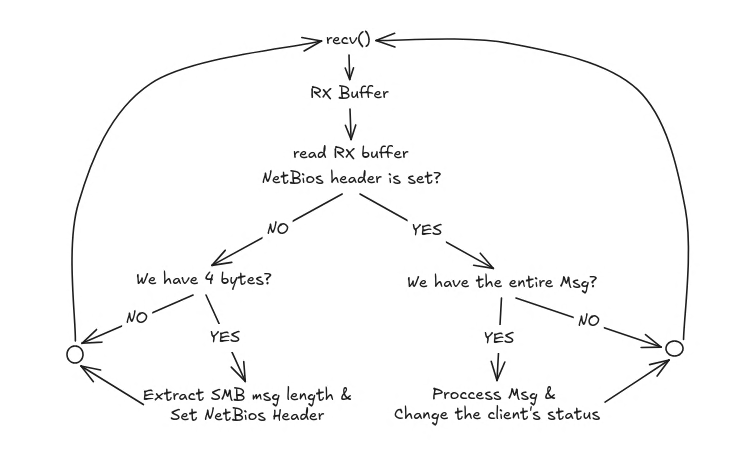 lcky00/impostor
SMB1 server for NTLMv2 hash interception, written in C.
 zhoucc-cpu/cve-2023-23397-detection-lab
Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.
 tiborscholtz/cve-2026-24061
Educational Docker lab demonstrating Telnet NEW-ENVIRON username injection (CVE-2026-24061) with a Python client and vulnerable server for isolated…
 randeepajayasekara/cve-2026-20127
Walkthrough of the CVSS 10.0 authentication bypass in Cisco Catalyst SD-WAN from first malformed peering request to root on the management plane.
 jlinebau/cve-2025-55315-scanner-monitor
Quick and Simple Scripts to Scan for Vulnerable Servers and Packet Level Monitors
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.