prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

A powerful open-source tool for managing networks and troubleshooting network problems!

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…

Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.

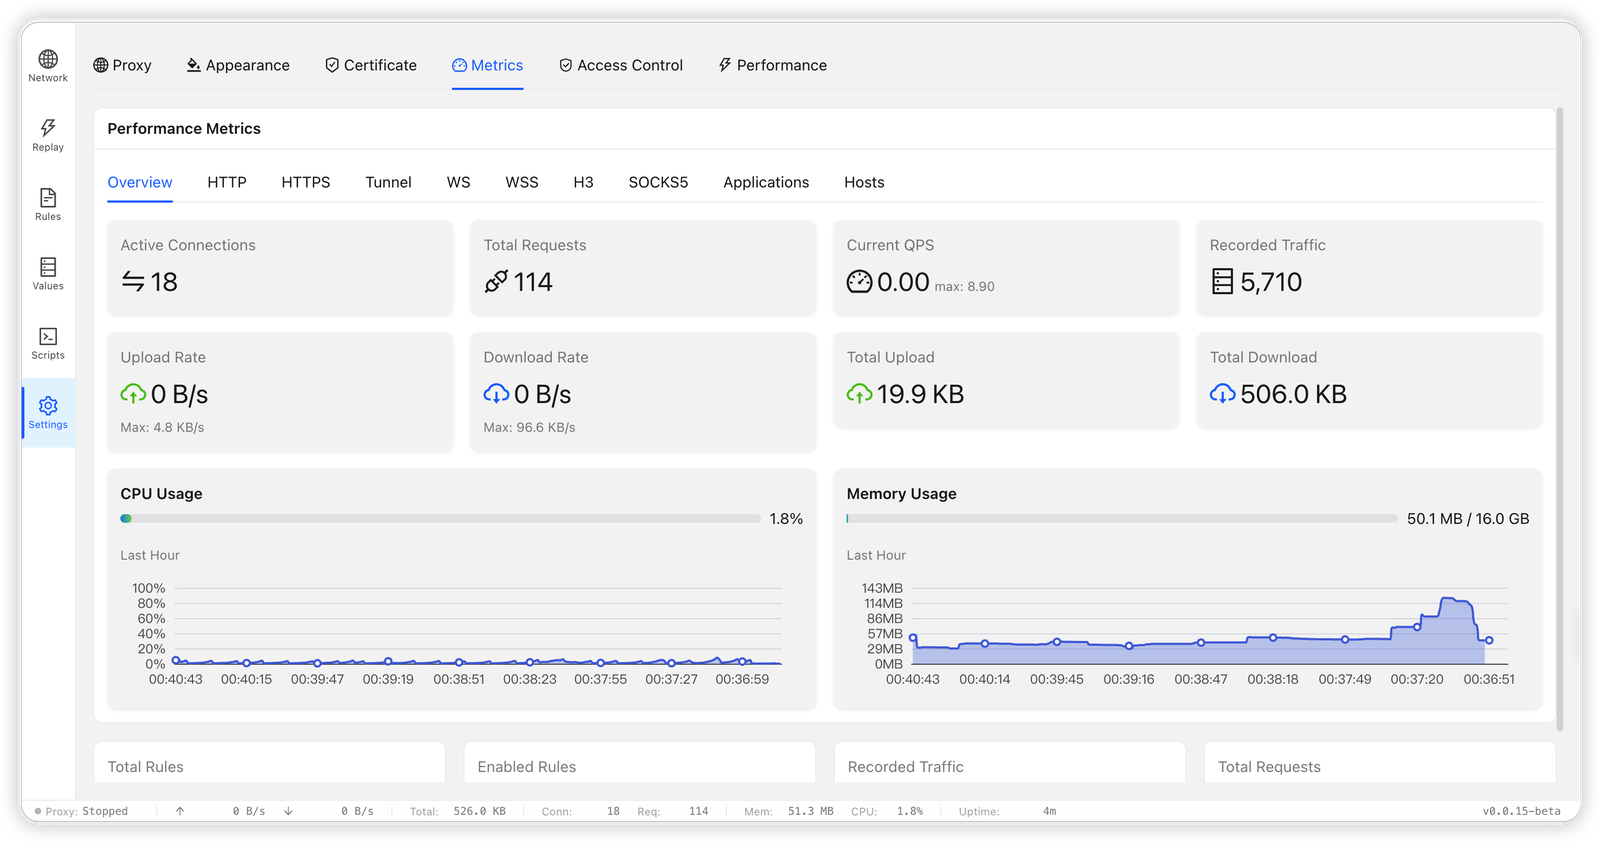
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…

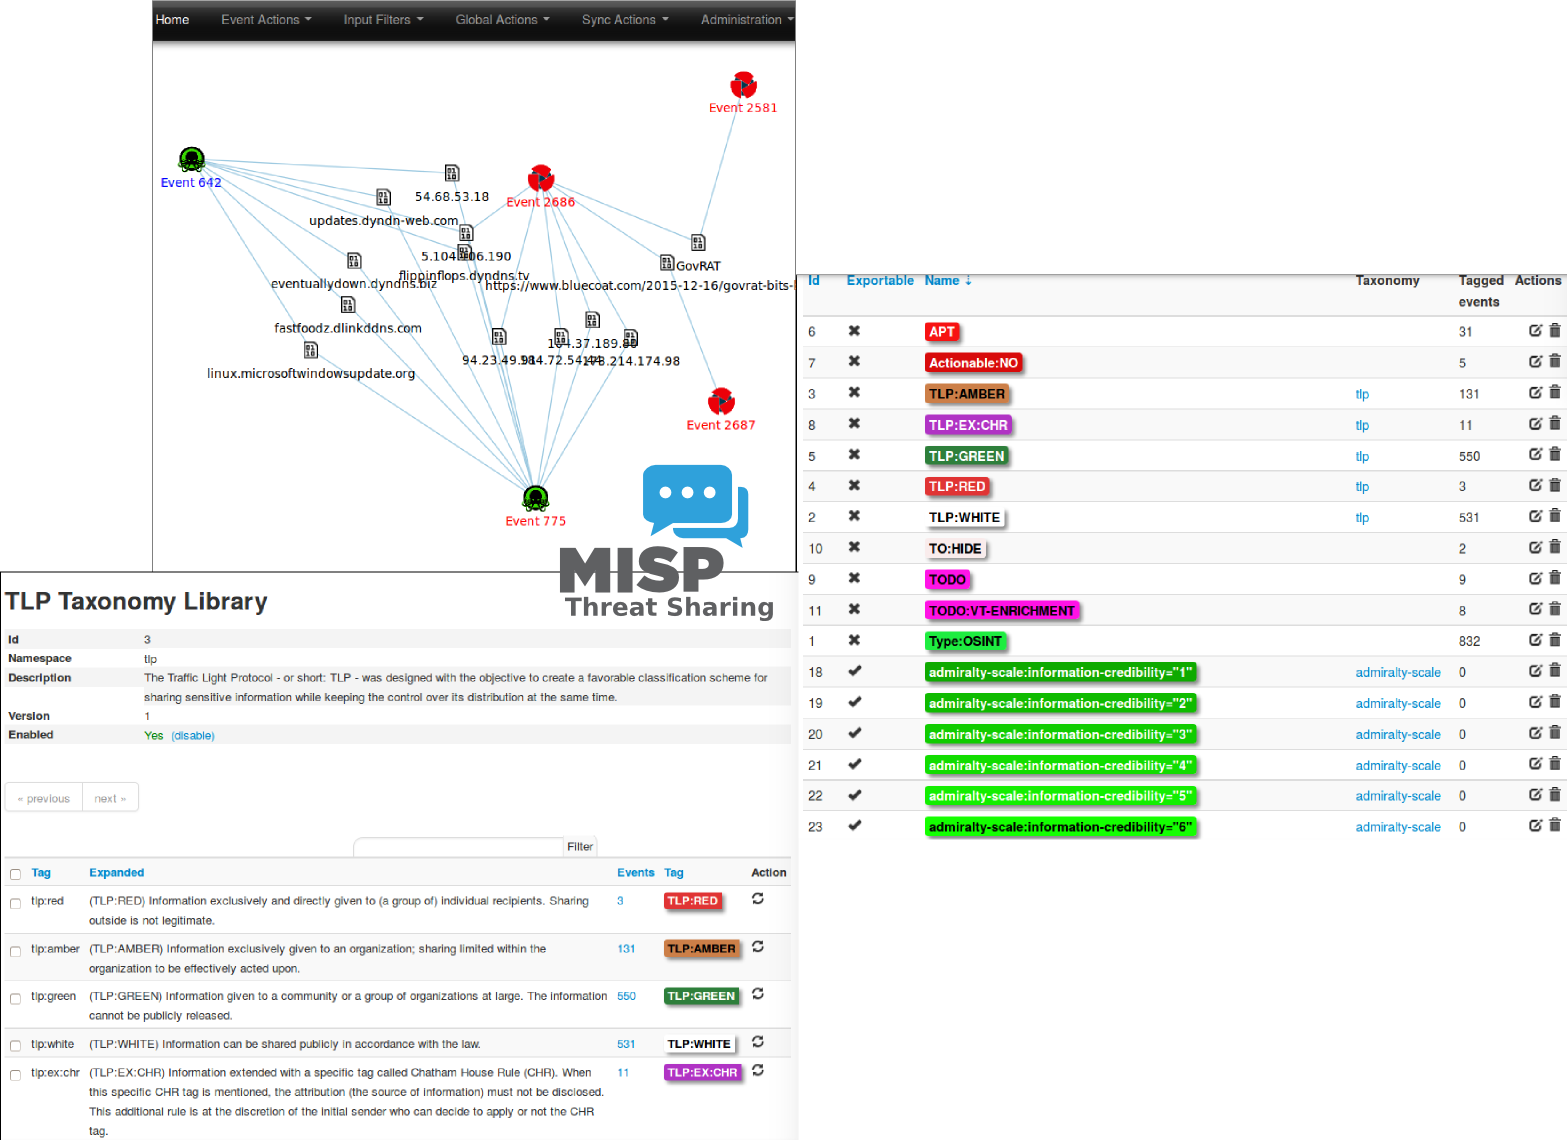
MISP (core software) - Open Source Threat Intelligence and Sharing Platform

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…

A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32

Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

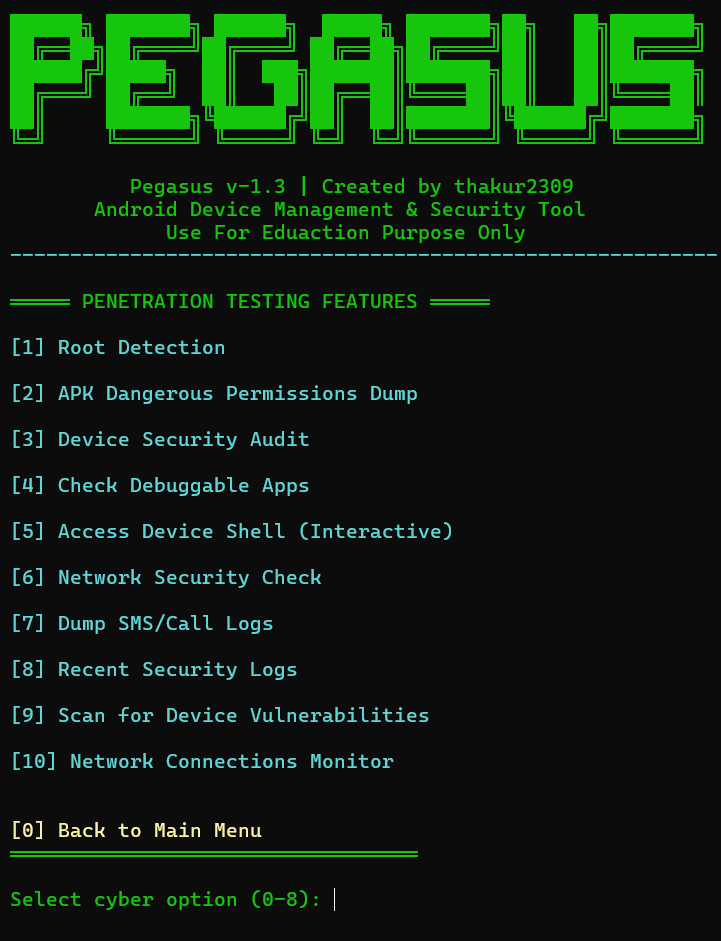
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

The open-source wireless research platform for ESP32.

Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…

Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…