
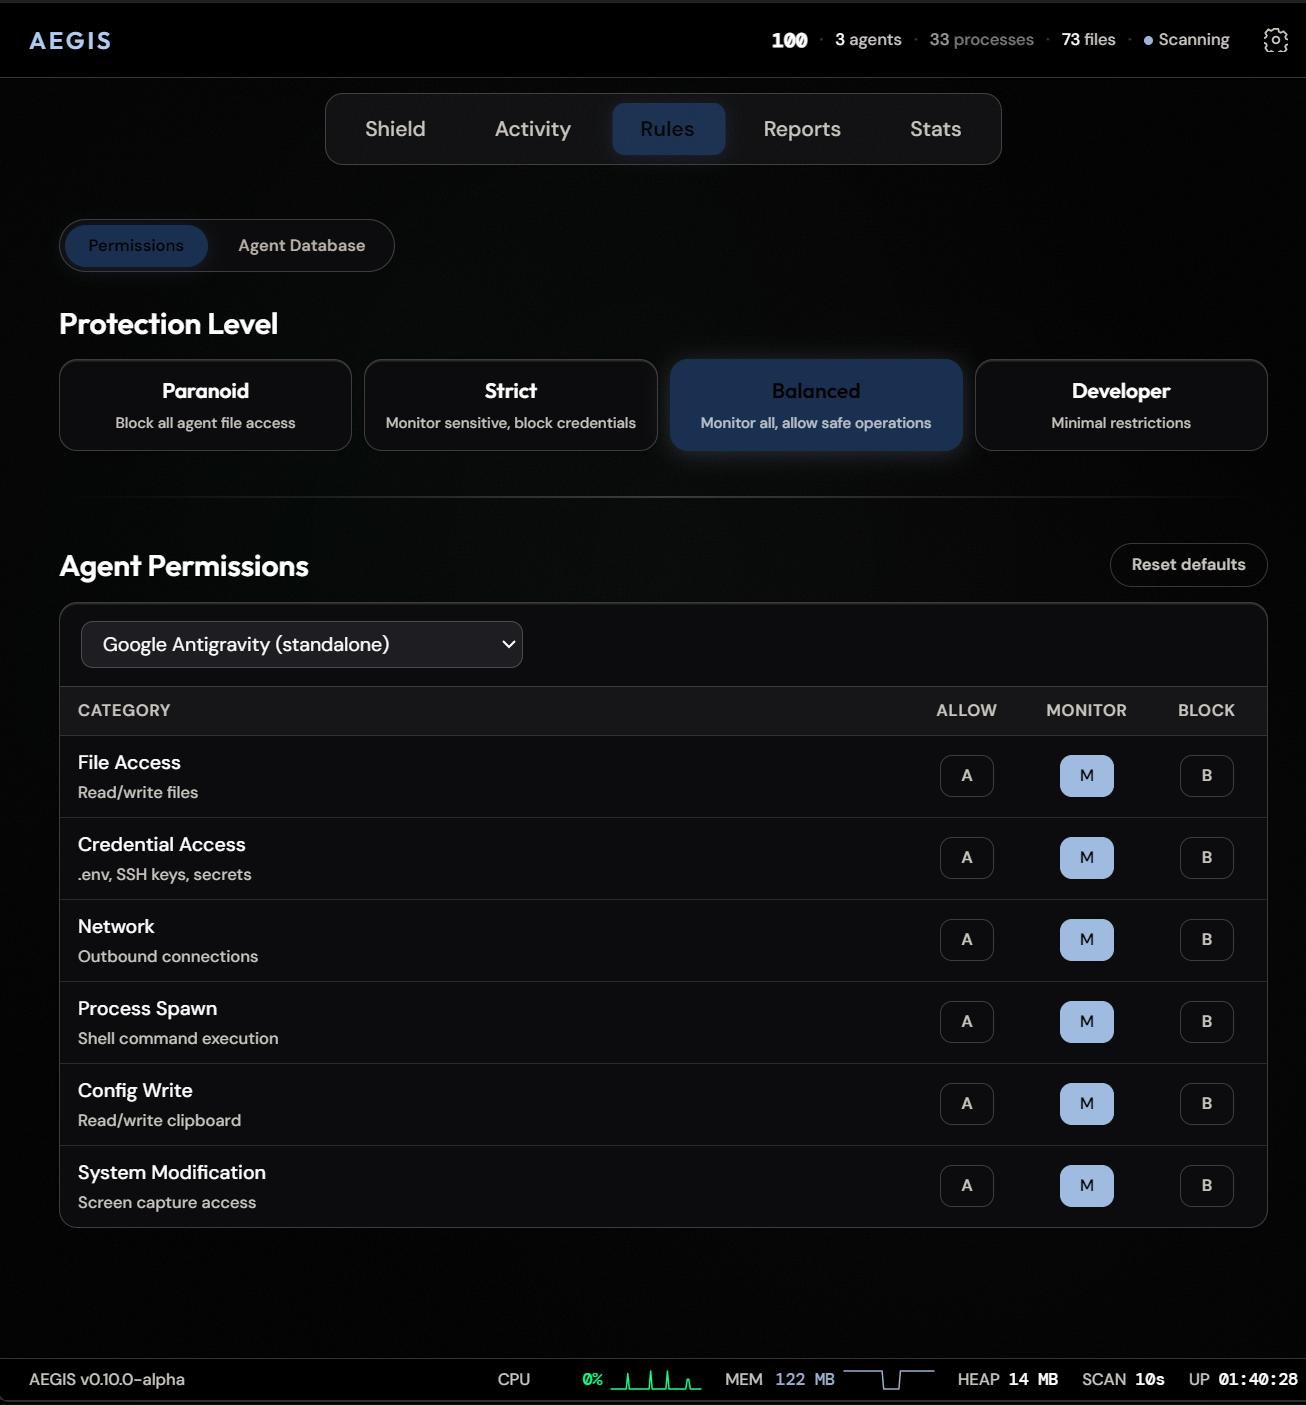
Aegis
 antropos17/aegis
Desktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…
ai-securityanomaly-detectiondefensive-tools+4
154
antropos17/aegisDesktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…
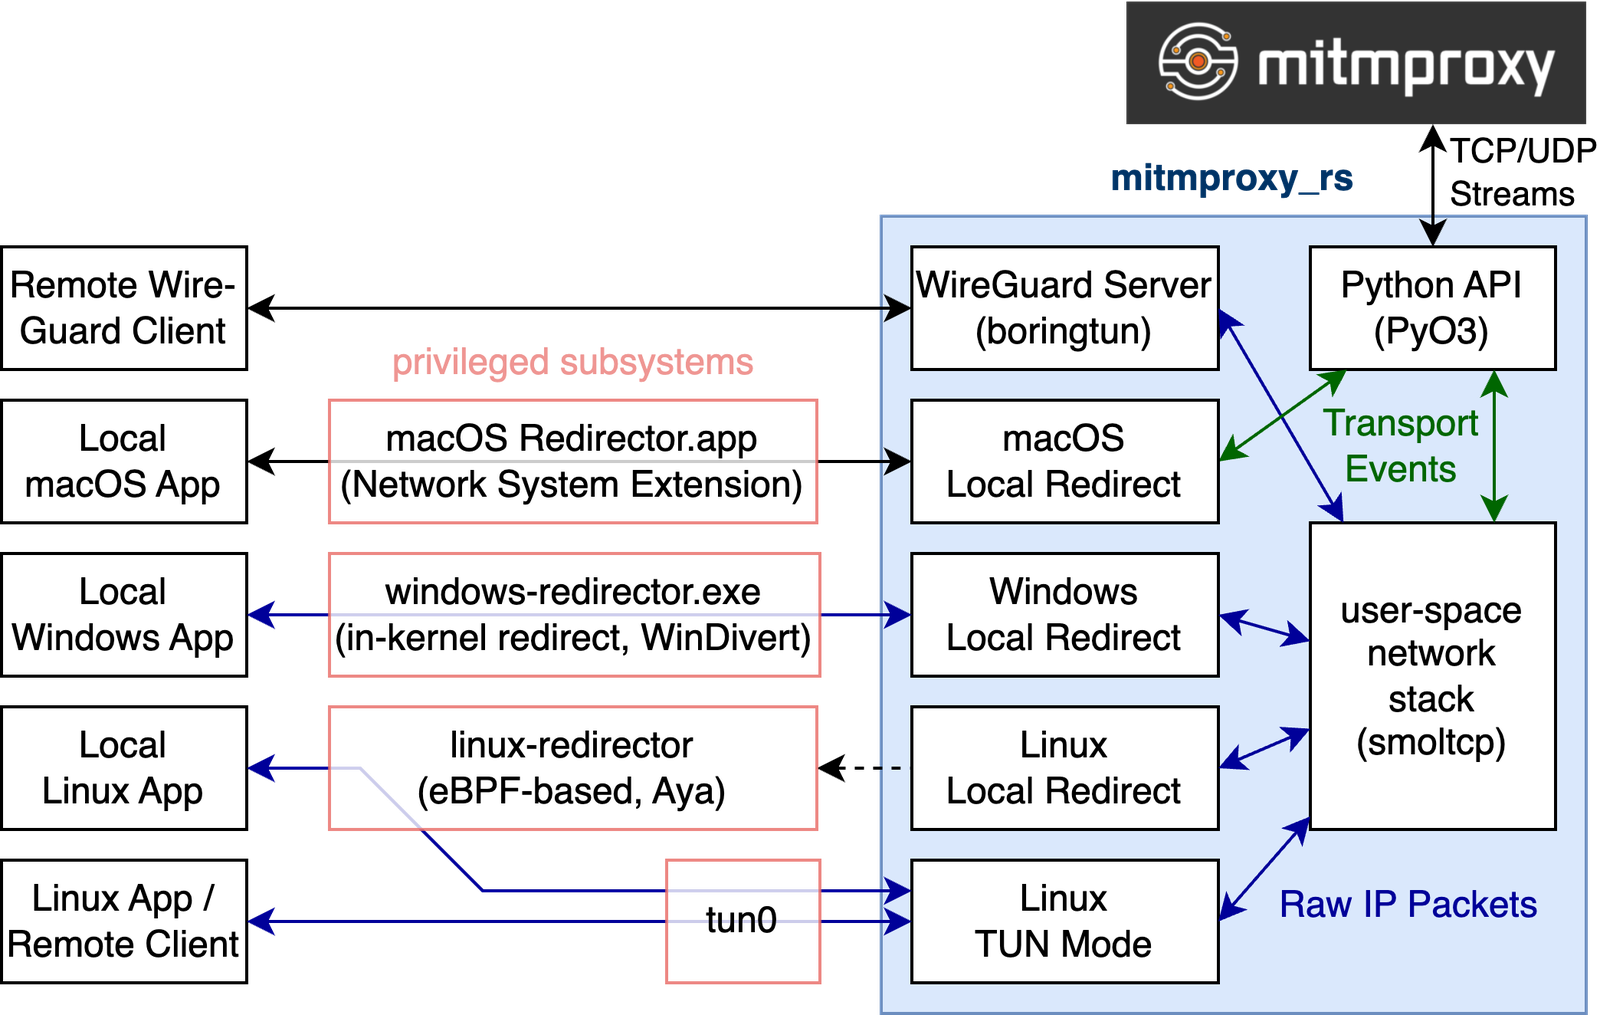 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 kevincrrl/evillimiter-ng
EvilLimiter Next Generation: monitor, analyze and limit the bandwidth
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
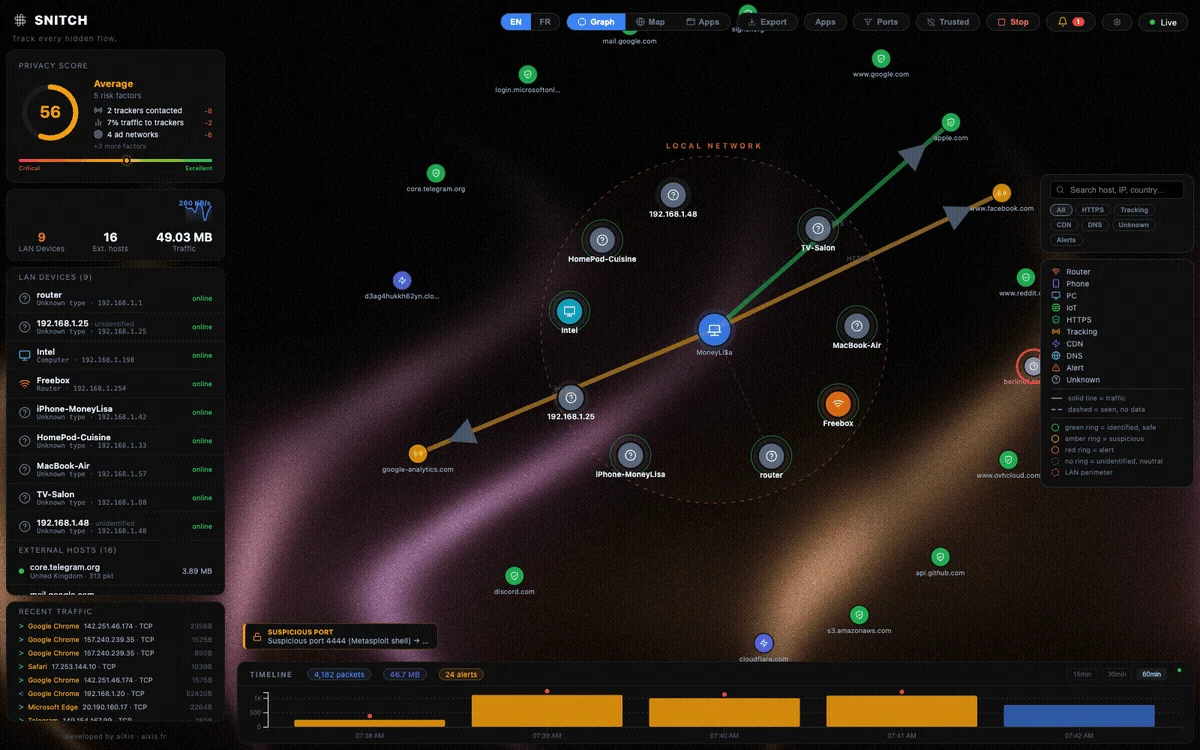 aixisstudio/snitch
Real-time network traffic visualizer — see every connection your computer makes. Privacy-first, 100% local. / Visualiseur de trafic réseau en temps…
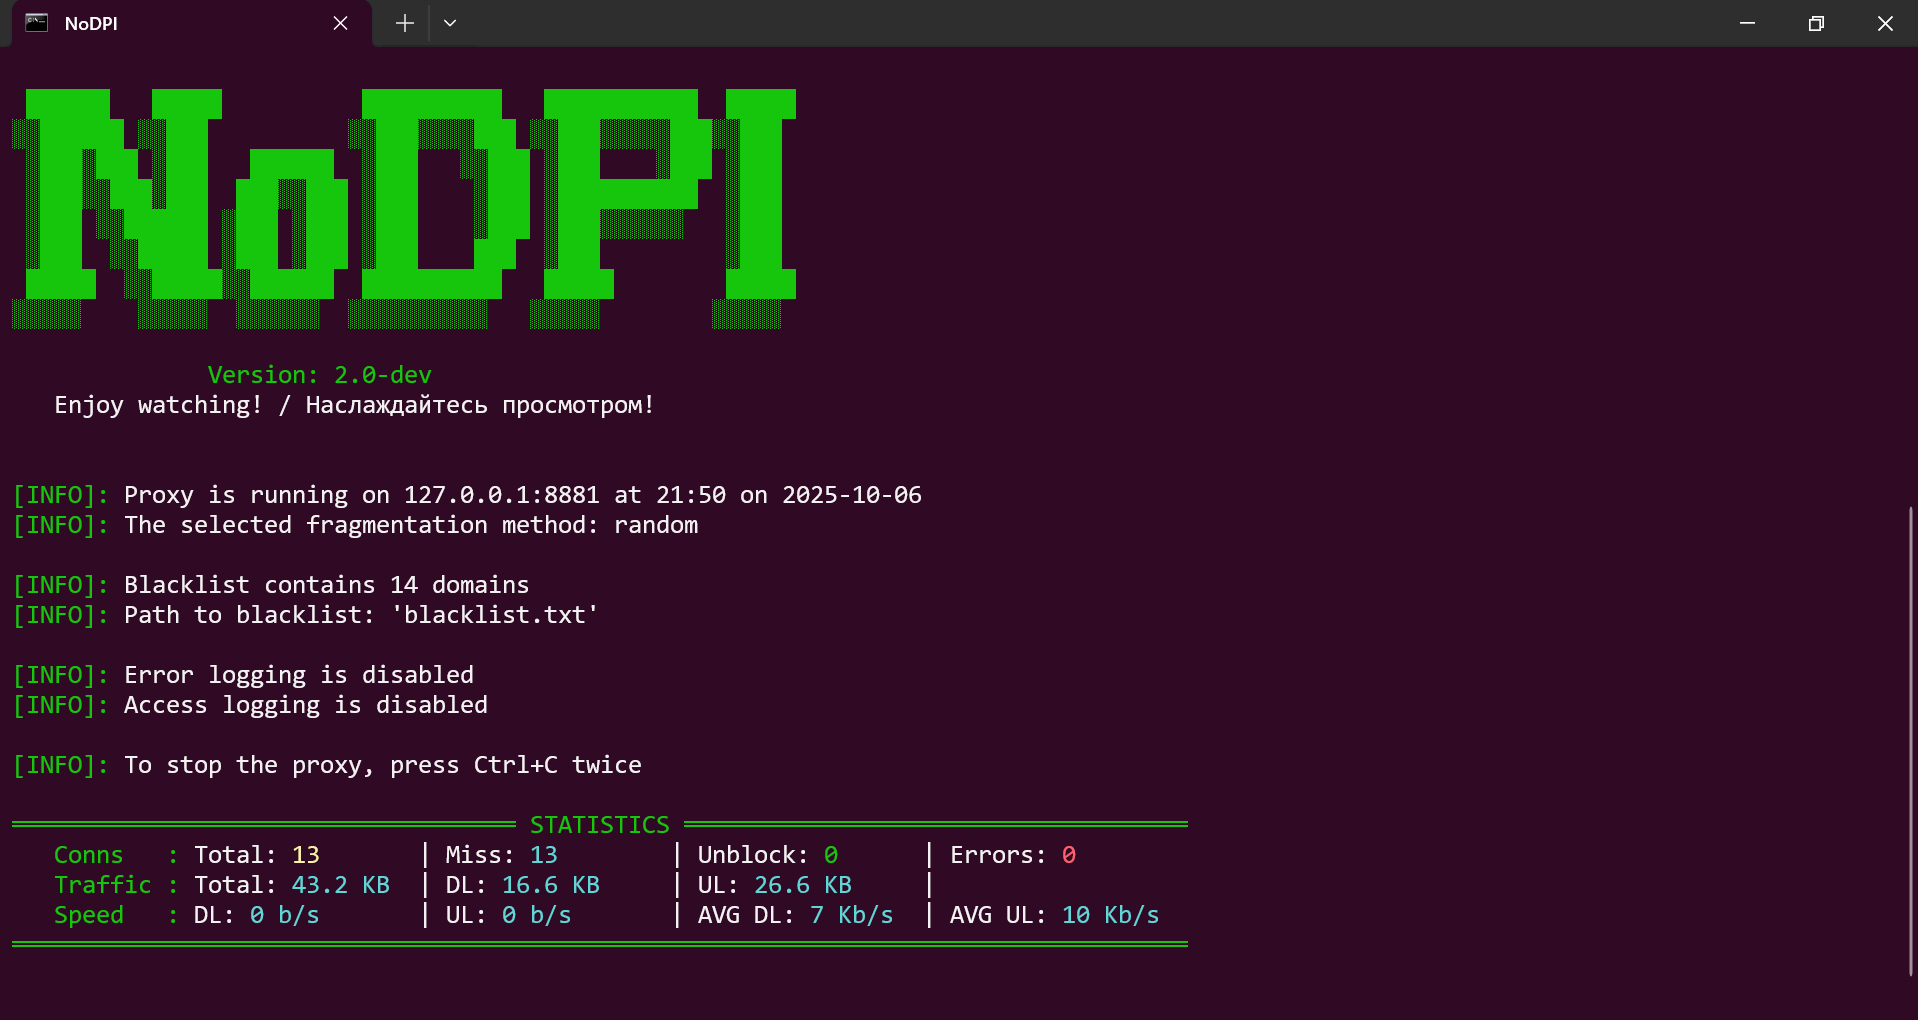 gvcoder09/nodpi
Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…
 ekzhang/bore
Simple TCP tunnel in Rust that exposes local ports to a remote server, bypassing NAT firewalls. Lightweight, self-hostable, and easy to install.
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
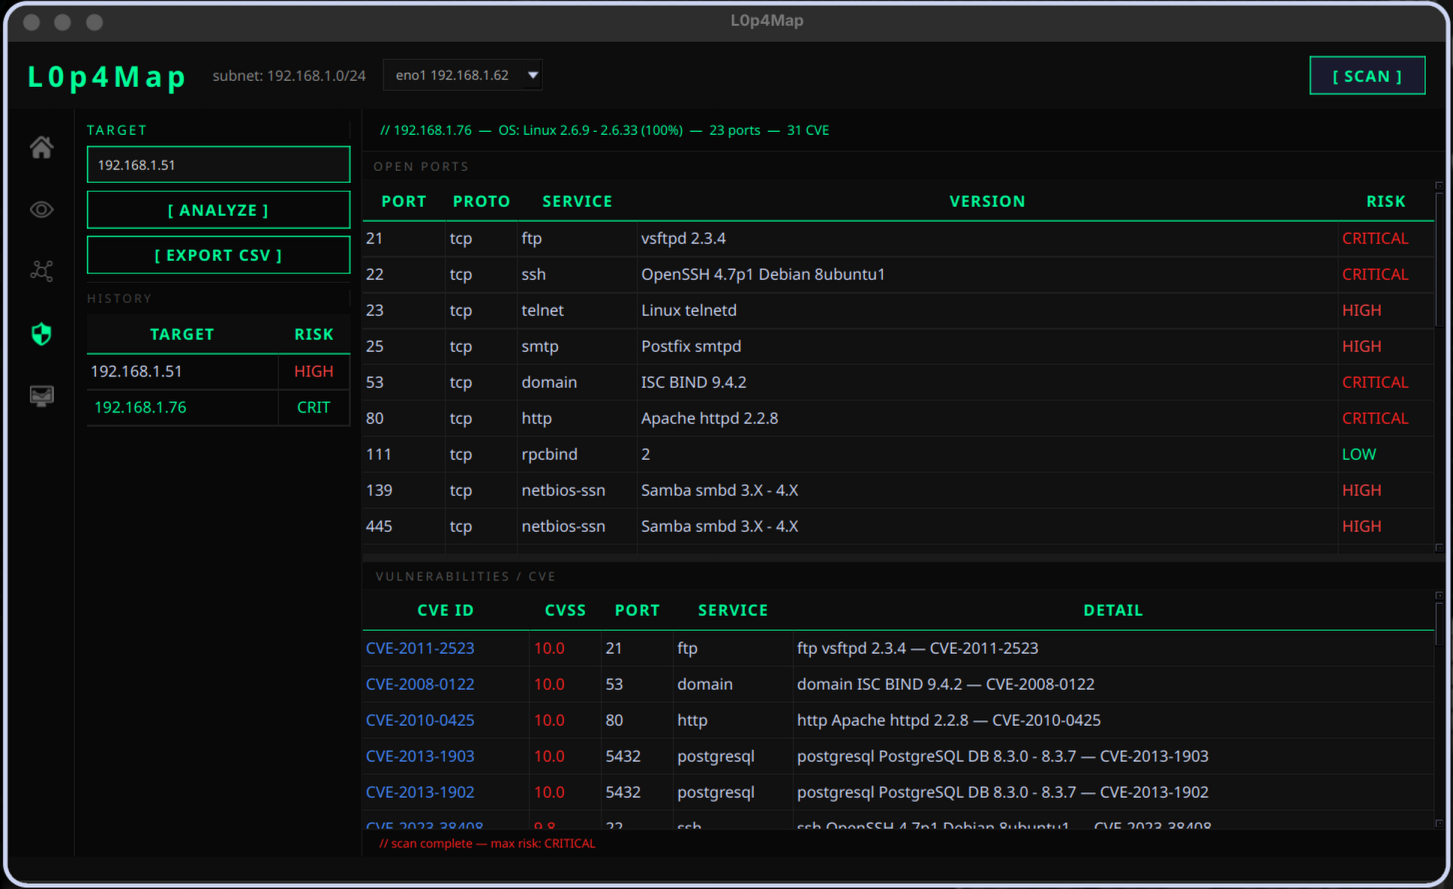 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 ashishraste/arp-dns-attacks
ARP spoofing, HTTP redirection, DNS spoofing and DNS forging using pcap library
 zayan-mohamed/orb
Orb is a secure, terminal-first utility that allows you to share a local folder across the internet using end-to-end encryption. No accounts, no…
 bitbrute/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 bitbrute/evillimiter-windows
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access (for Windows only)
 tothi/servicedetector
Detect whether a service is installed (blindly) and/or running (if exposing named pipes) on a remote machine without using local admin privileges.
 shirosaidev/sharesniffer
Network share sniffer and auto-mounter for crawling remote file systems
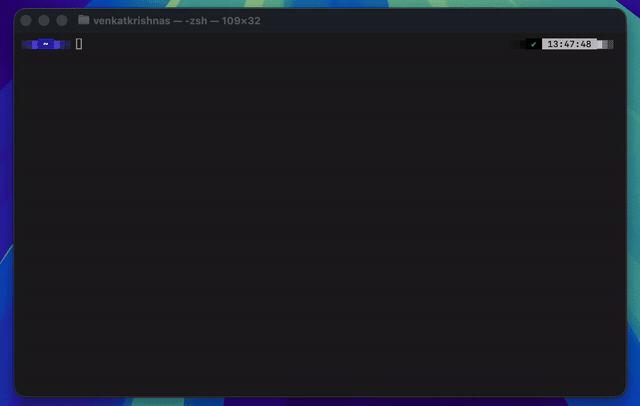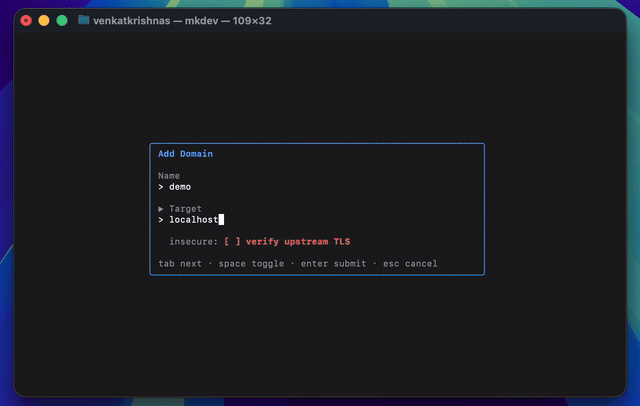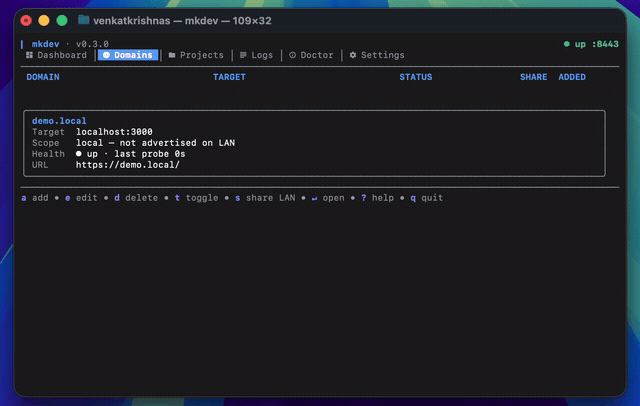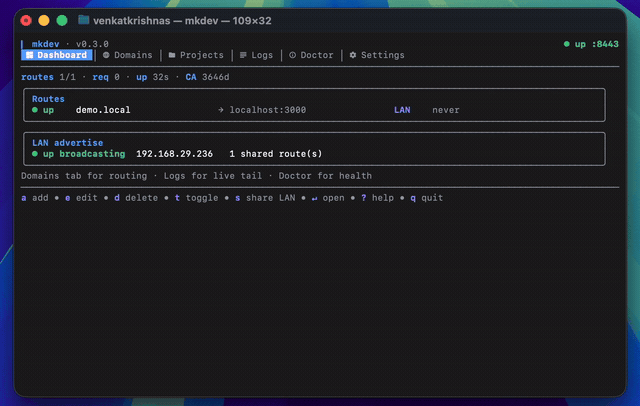 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
 jimi2x/dirtycups
UDP-based scanner for CVE-2024-47176 that validates CUPS vulnerability by creating a local socket listener and triggering target responses.