
Excalibur
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
educationexploitationexploit-frameworks+9
dviros/excaliburExcalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 algosecure/iotmap
Research project on heterogeneous IoT protocols modelling
 rinaliyeva/metasploitable2-vsftpd-exploitation
Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.
 masjohncook/netsec-project
Script of Network Security Project - Attack on CVE-2021-22555
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 seifeldienahmad/penetration-testing-on-metasploitable2
Hands-on pentest project using Kali Linux vs Metasploitable2. Includes full workflow: Nmap scanning, enumeration, Metasploit exploitation (Samba…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 neweracracker/loic
Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…
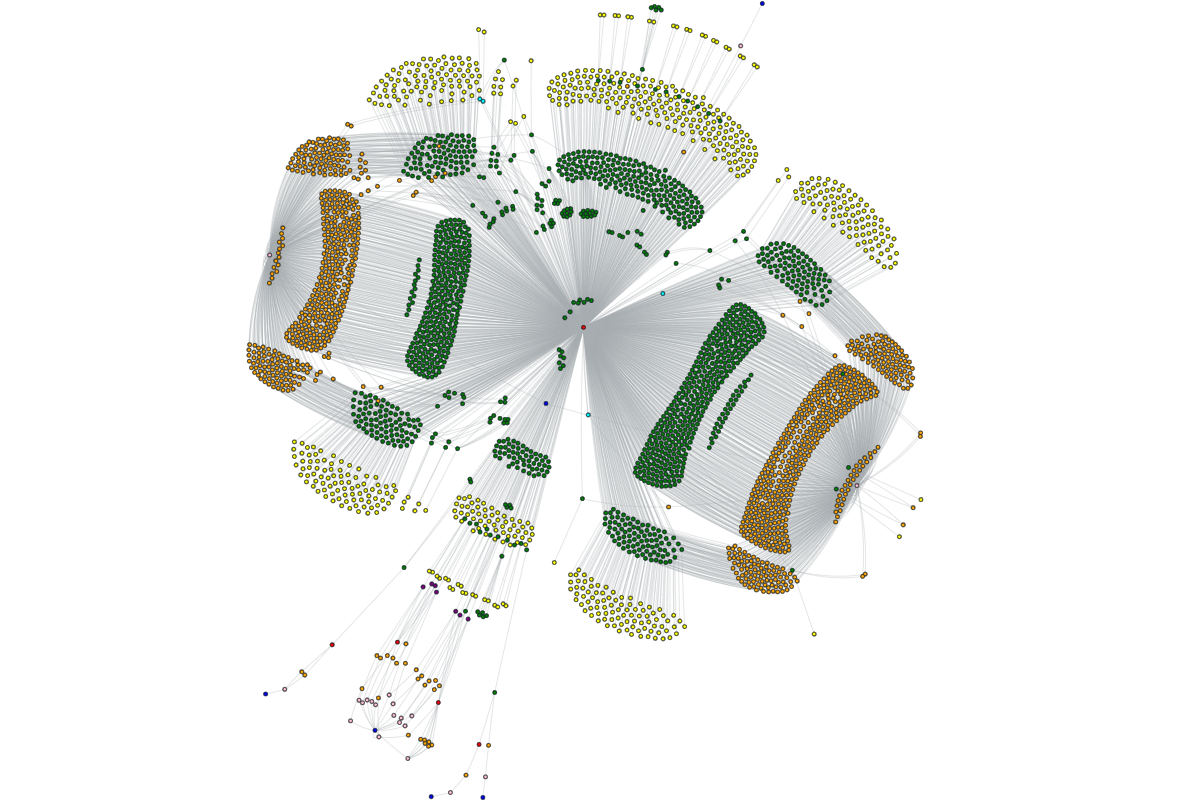 owasp-amass/amass
In-depth attack surface mapping and asset discovery
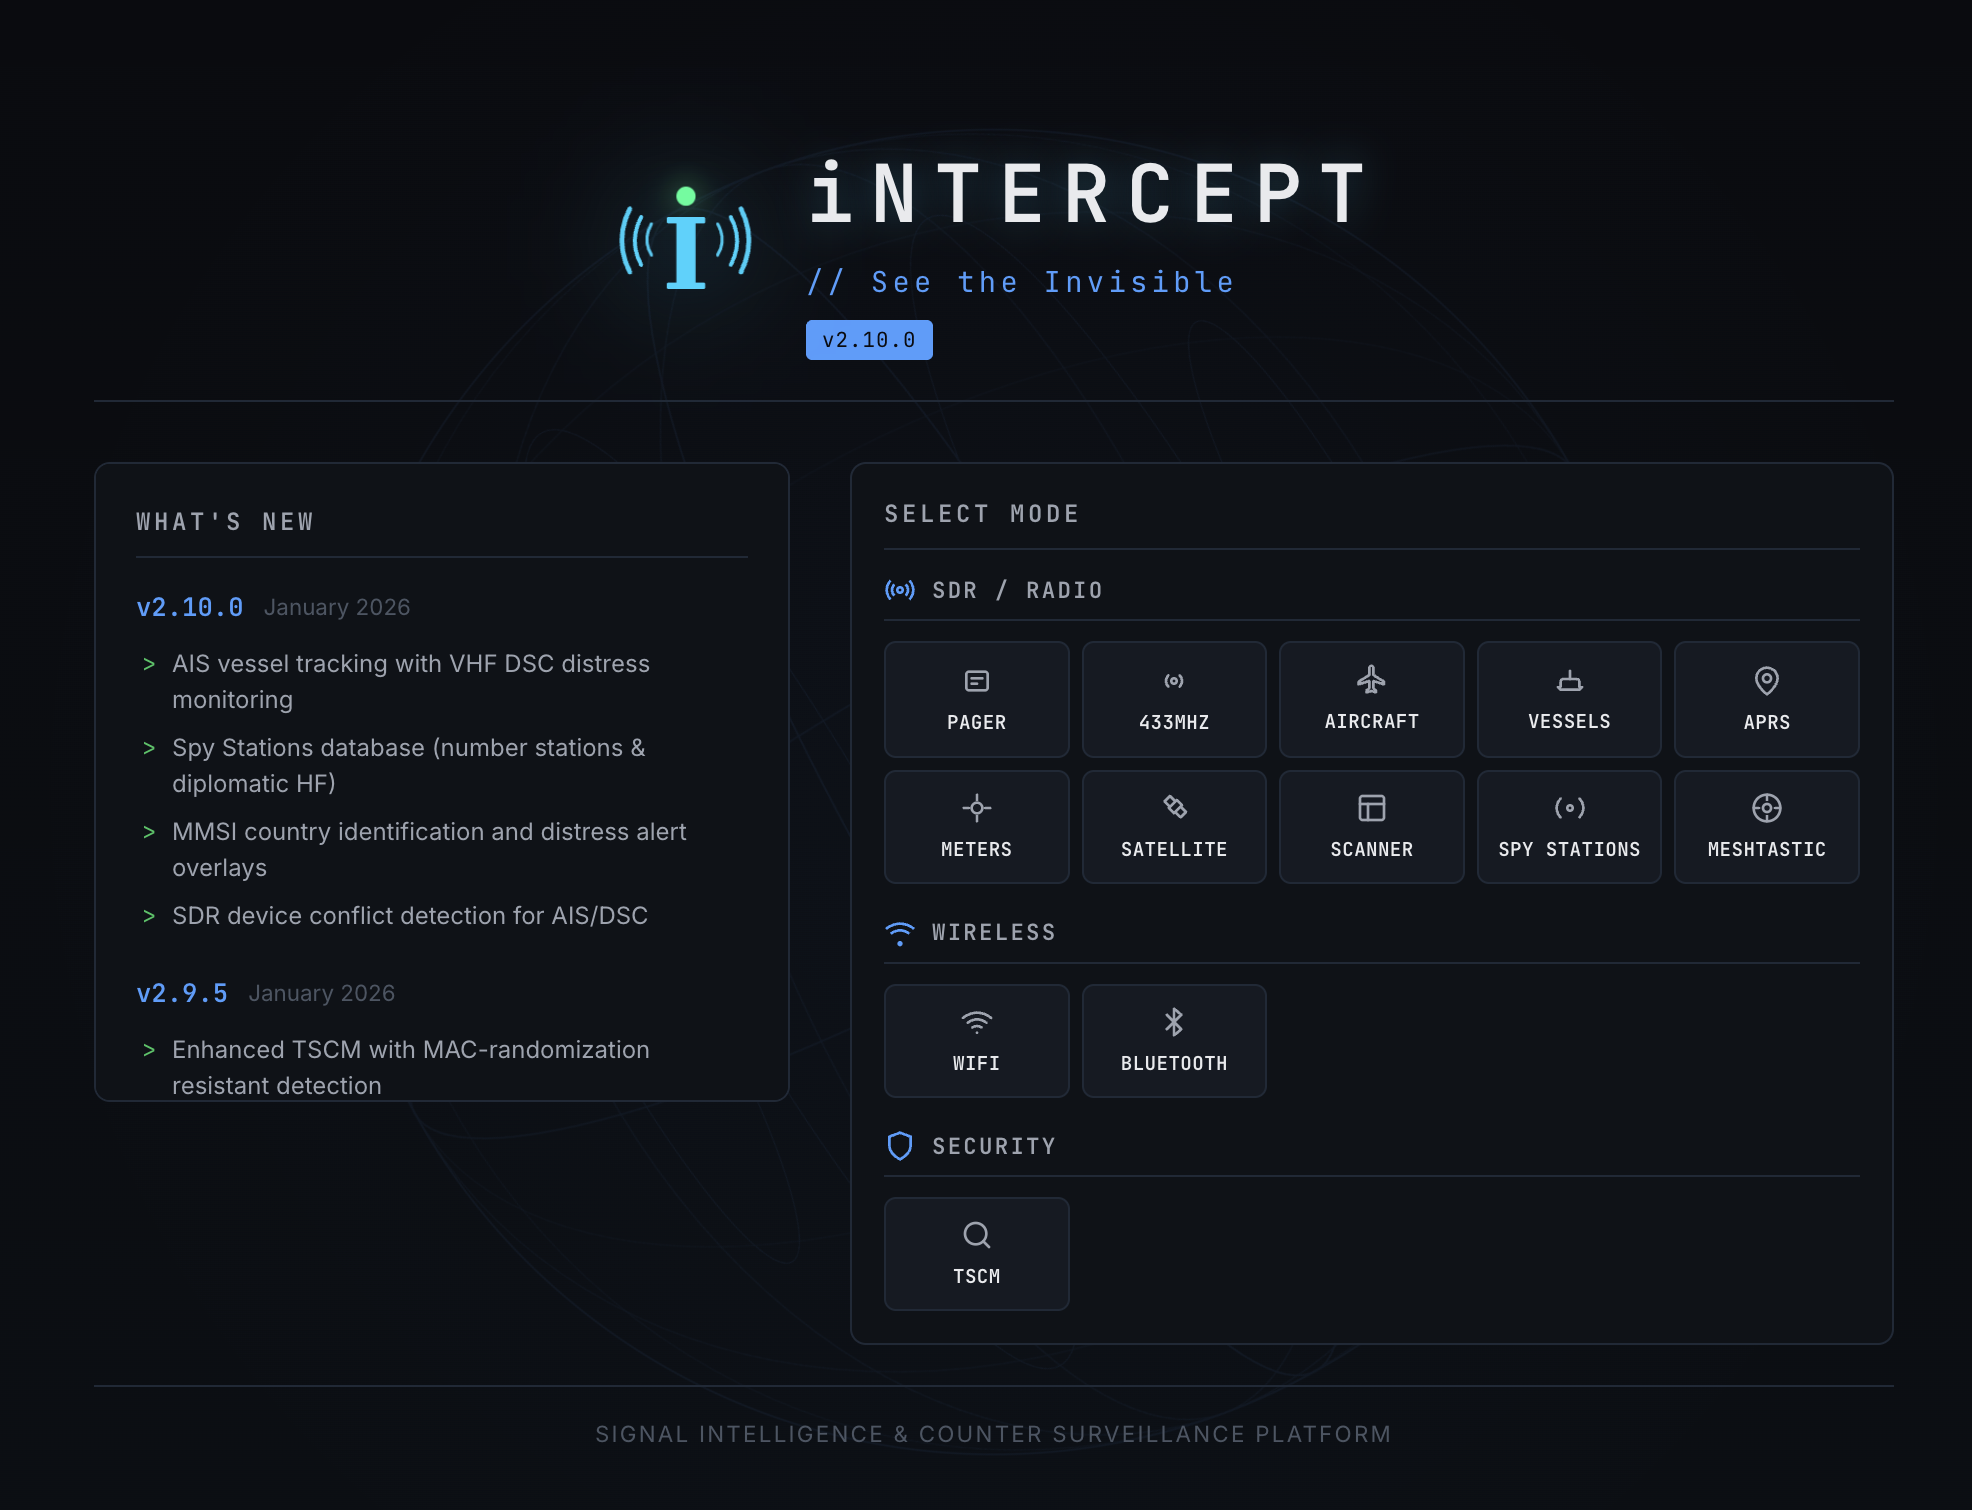 smittix/intercept
iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
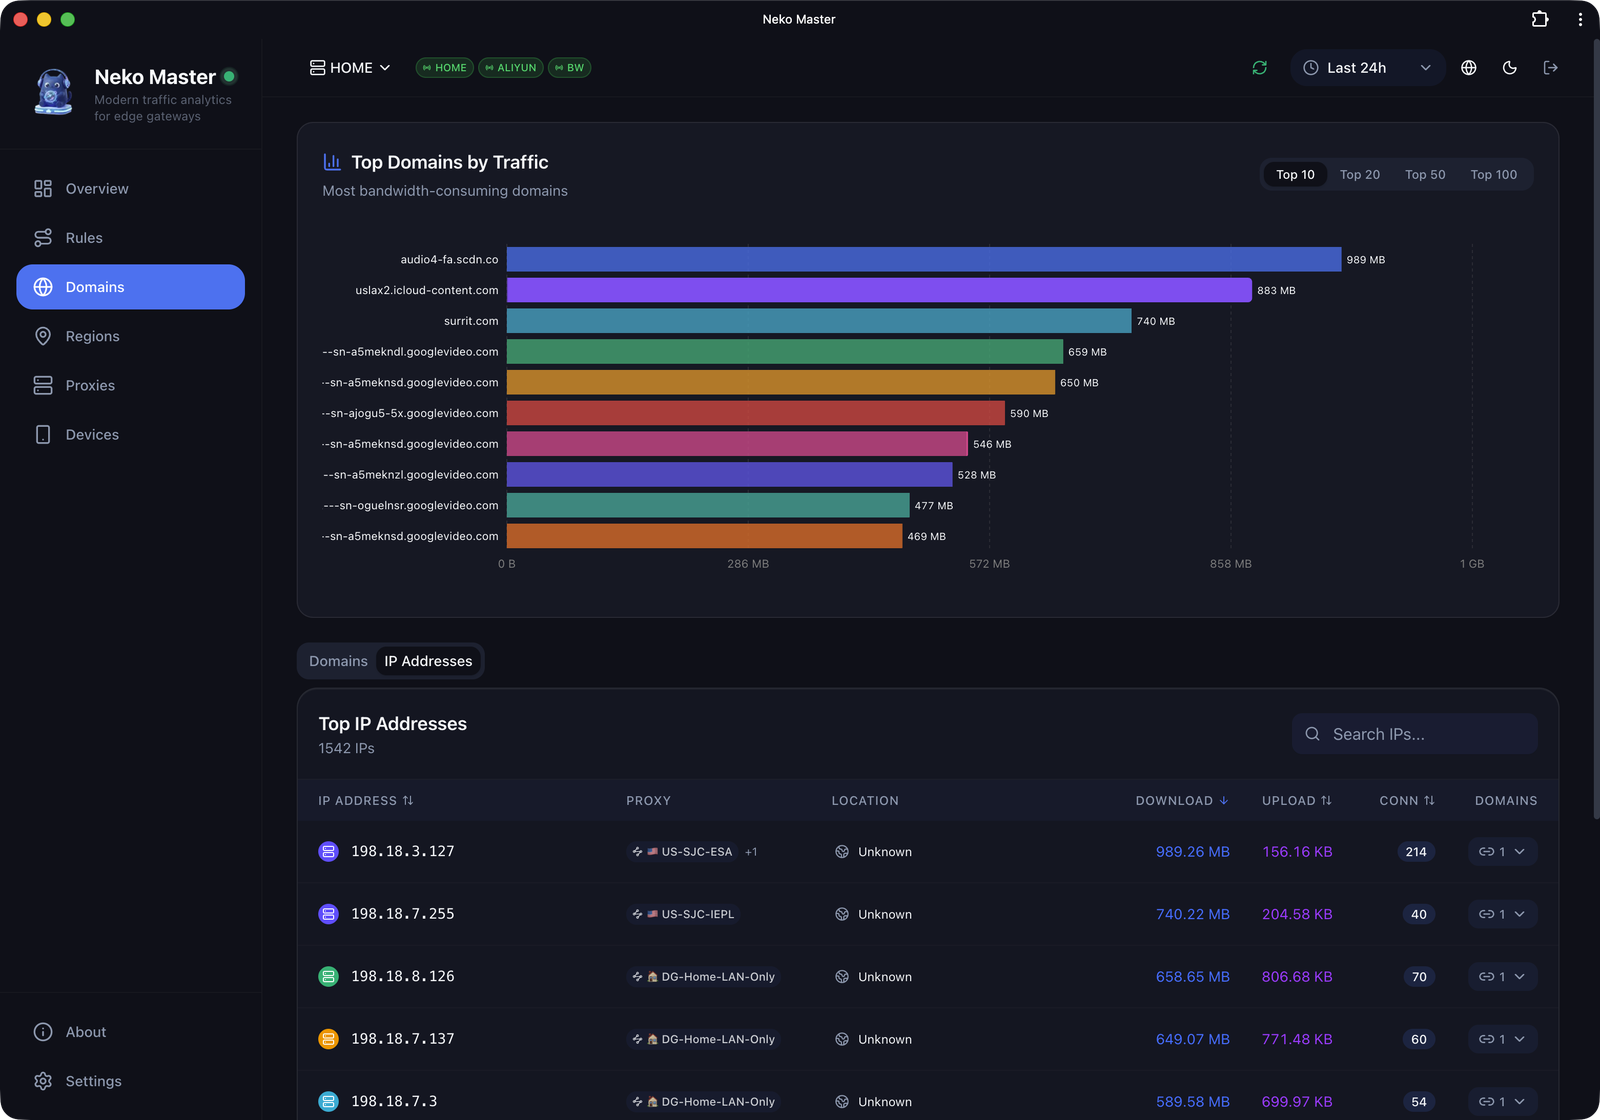 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
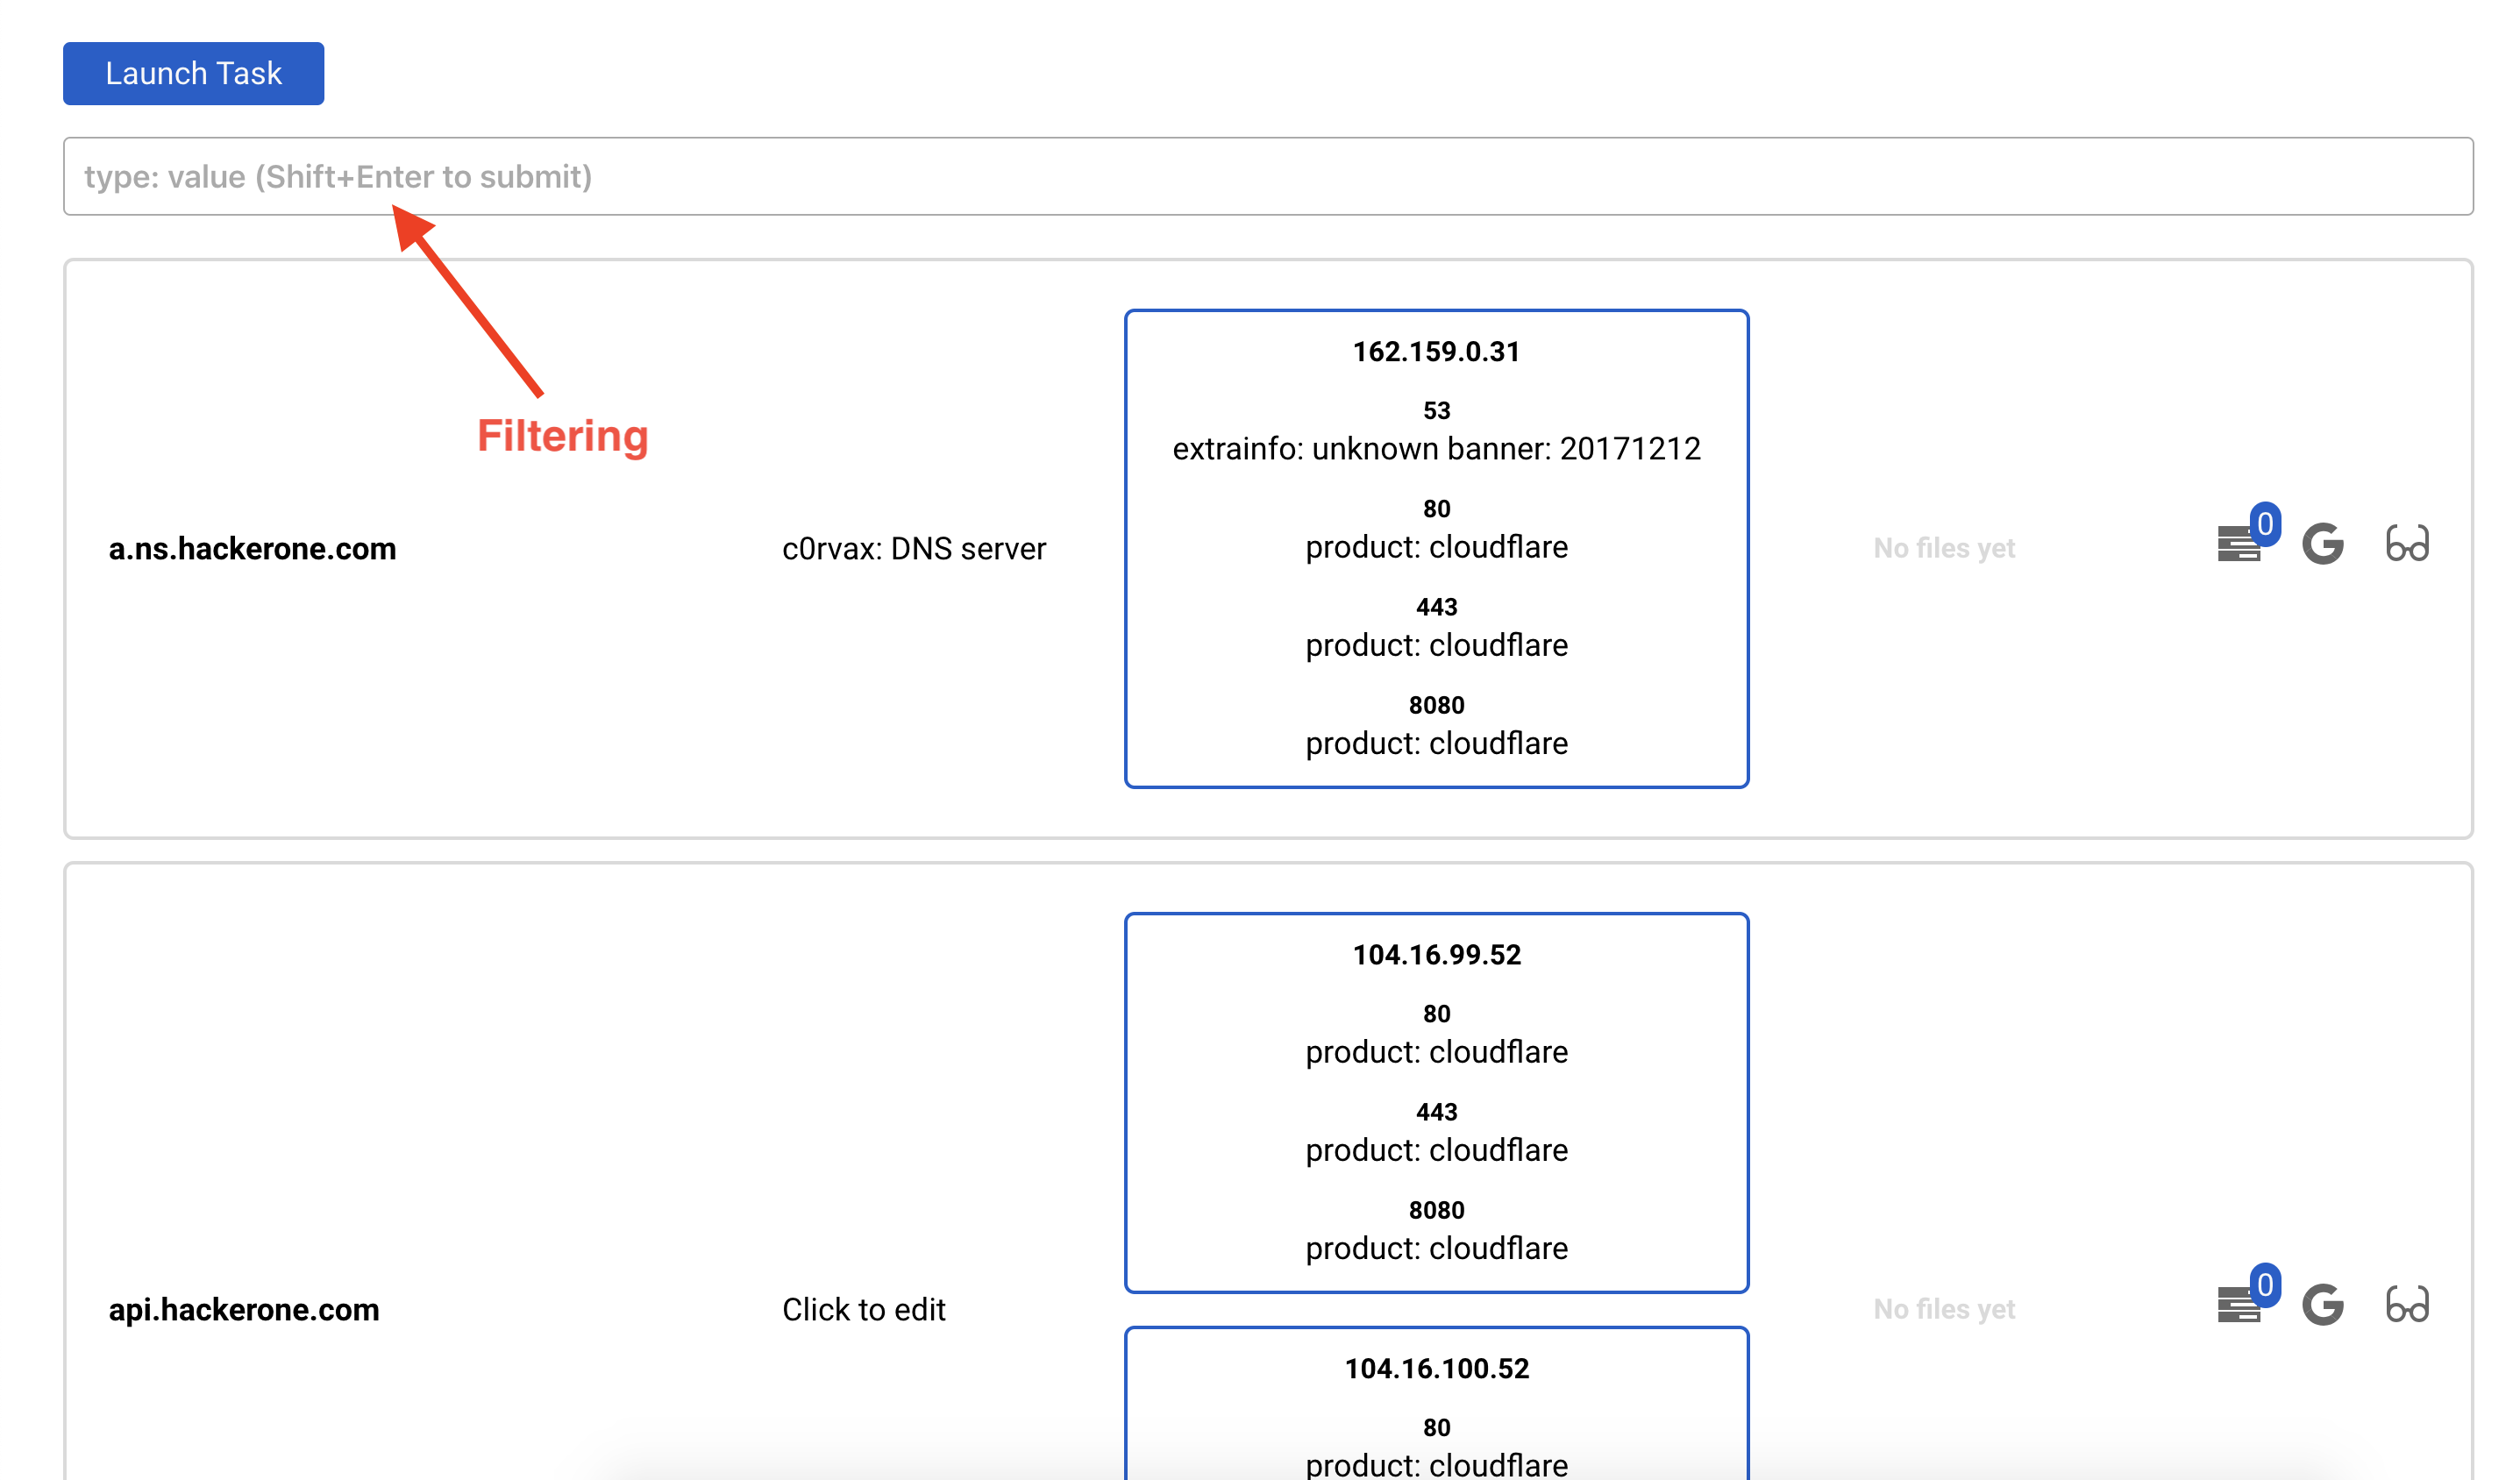 c0rv4x/project-black
Pentest/BugBounty progress control with scanning modules
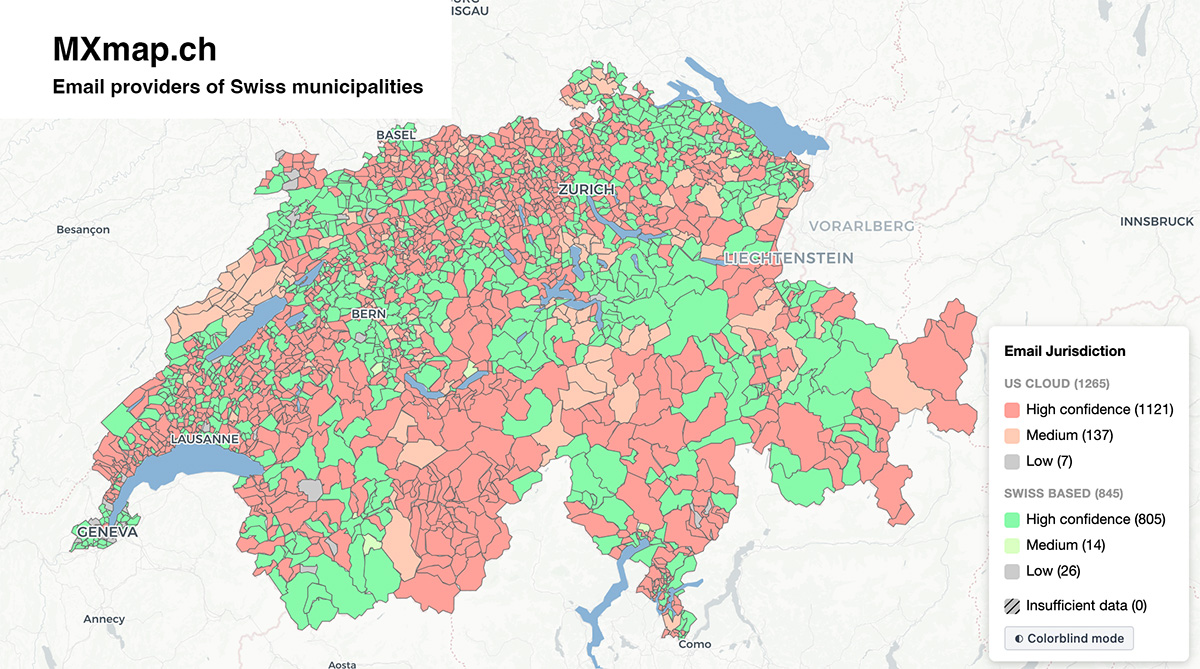 davidhuser/mxmap
Automated pipeline that resolves Swiss municipality domains, scrapes websites for email addresses, and classifies email providers via MX, SPF, DKIM,…
 macmod/flashingestor
TUI-based Active Directory data collector that ingests LDAP objects, performs remote RPC/SMB/HTTP collection, and generates BloodHound CE-compatible…
 0xor0ne/qscan
Quick network scanner library. https://crates.io/crates/qscan
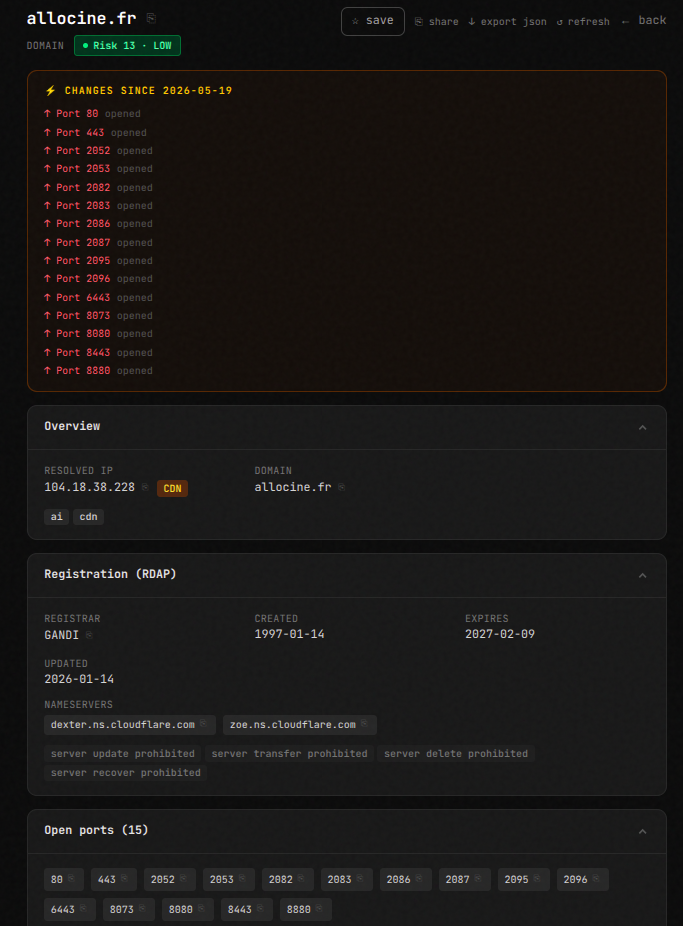 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.