
RXScan
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
defensive-toolsdns-analysisdns-subdomain-enumeration+8
1
darkrx1/rxscanRust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
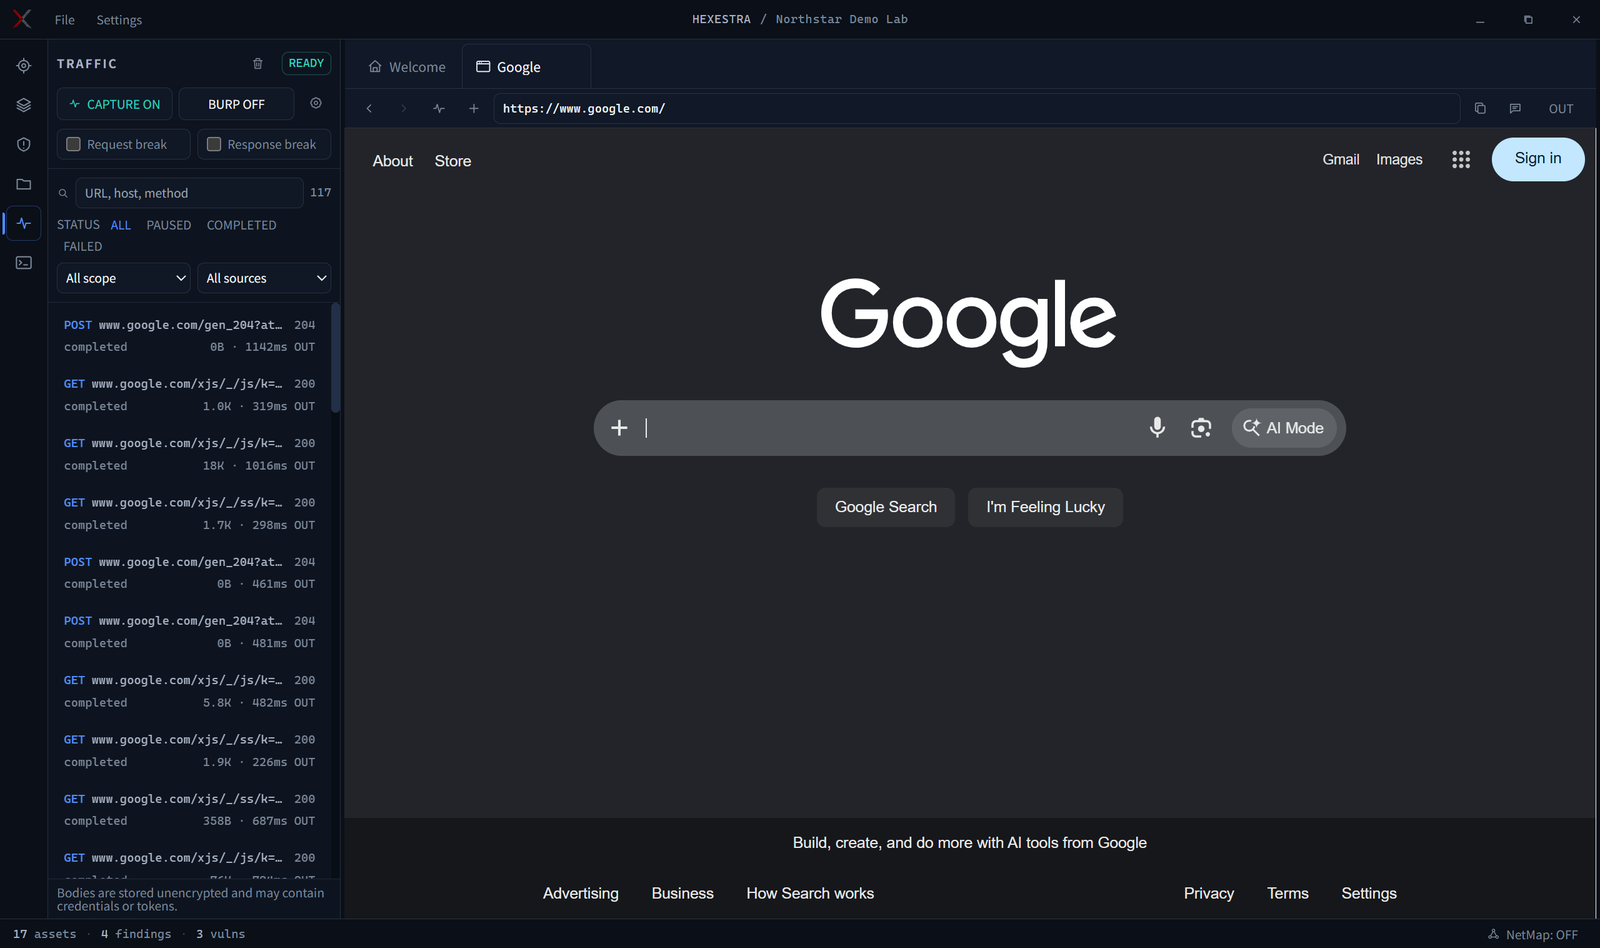 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
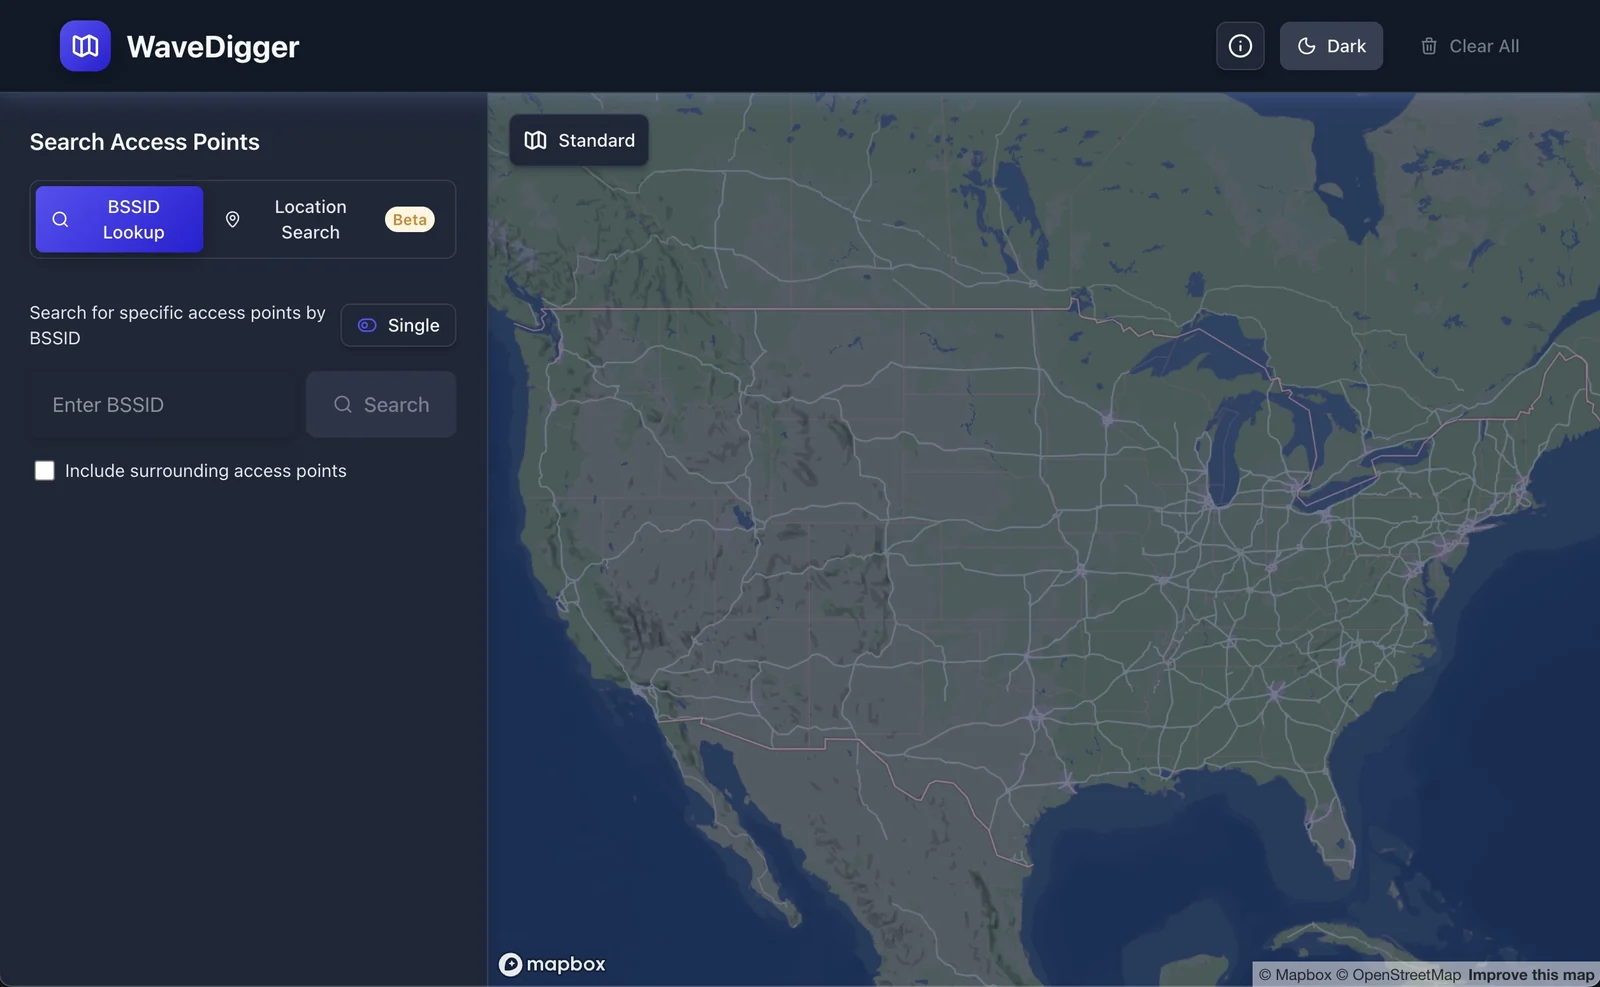 christianrowlands/wavedigger
BSSID Search in Apple's public WPS service
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
 jhaddix/awsscrape
A tool to scrape the AWS ranges looking for a keyword in SSL certificate data.
 bojanisc/quicmap
quicmap is a simple yet quic (!) QUIC protocol scanner
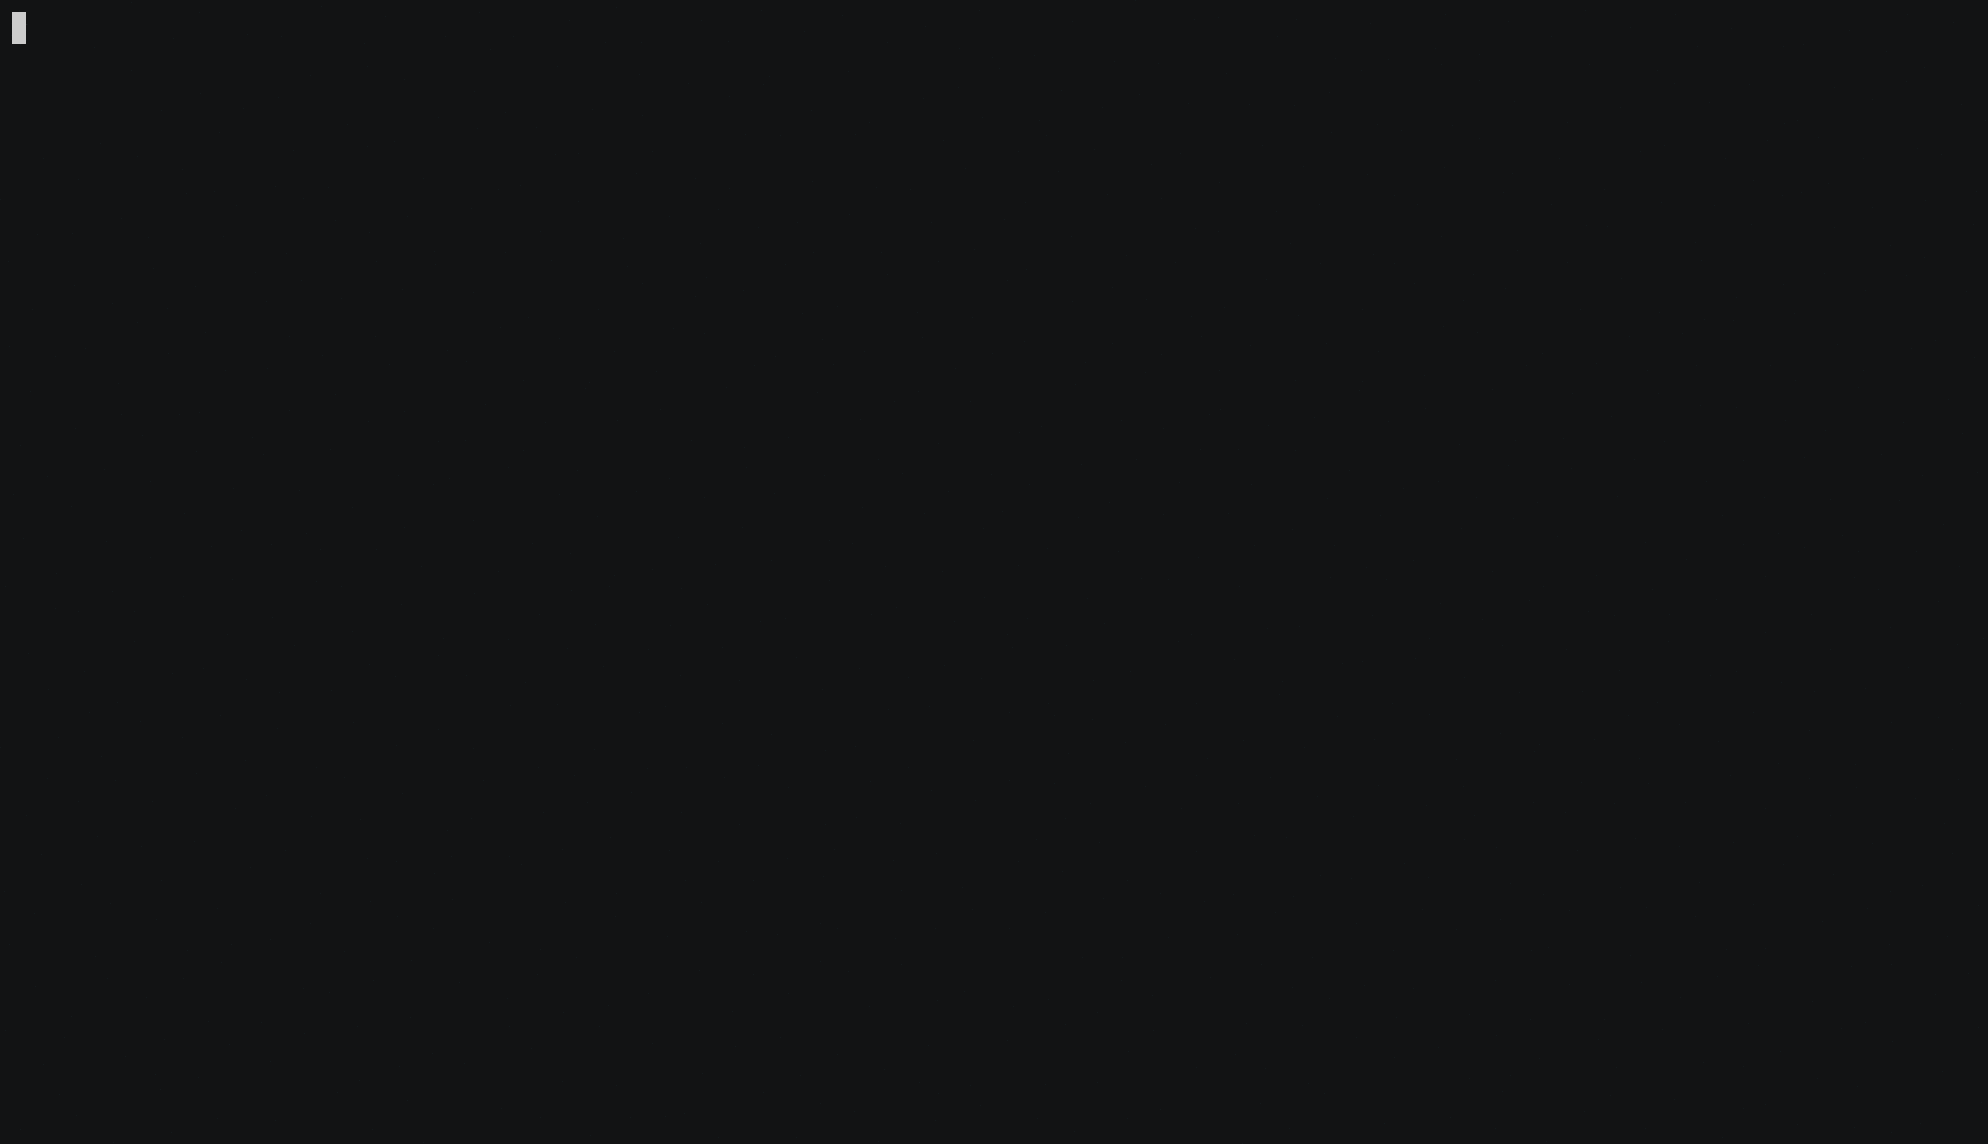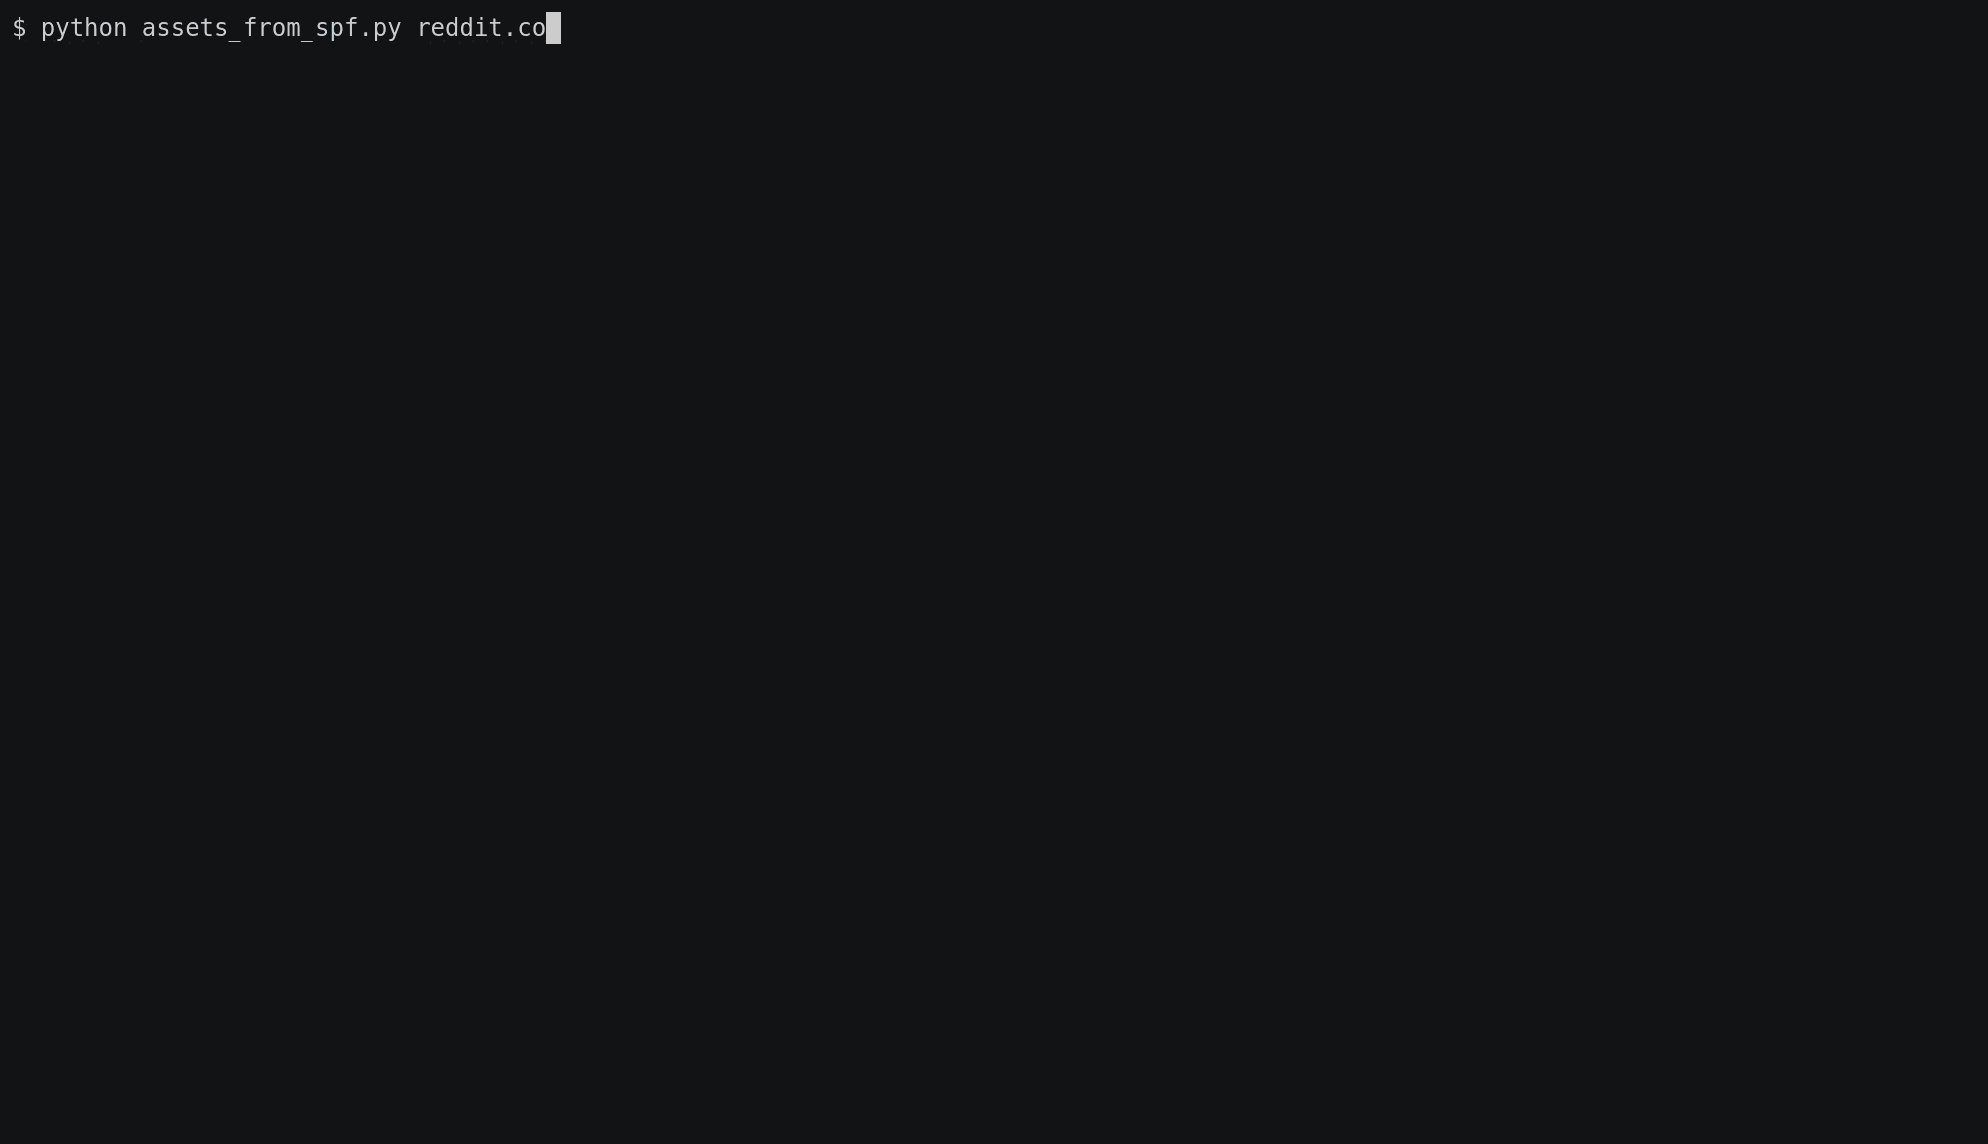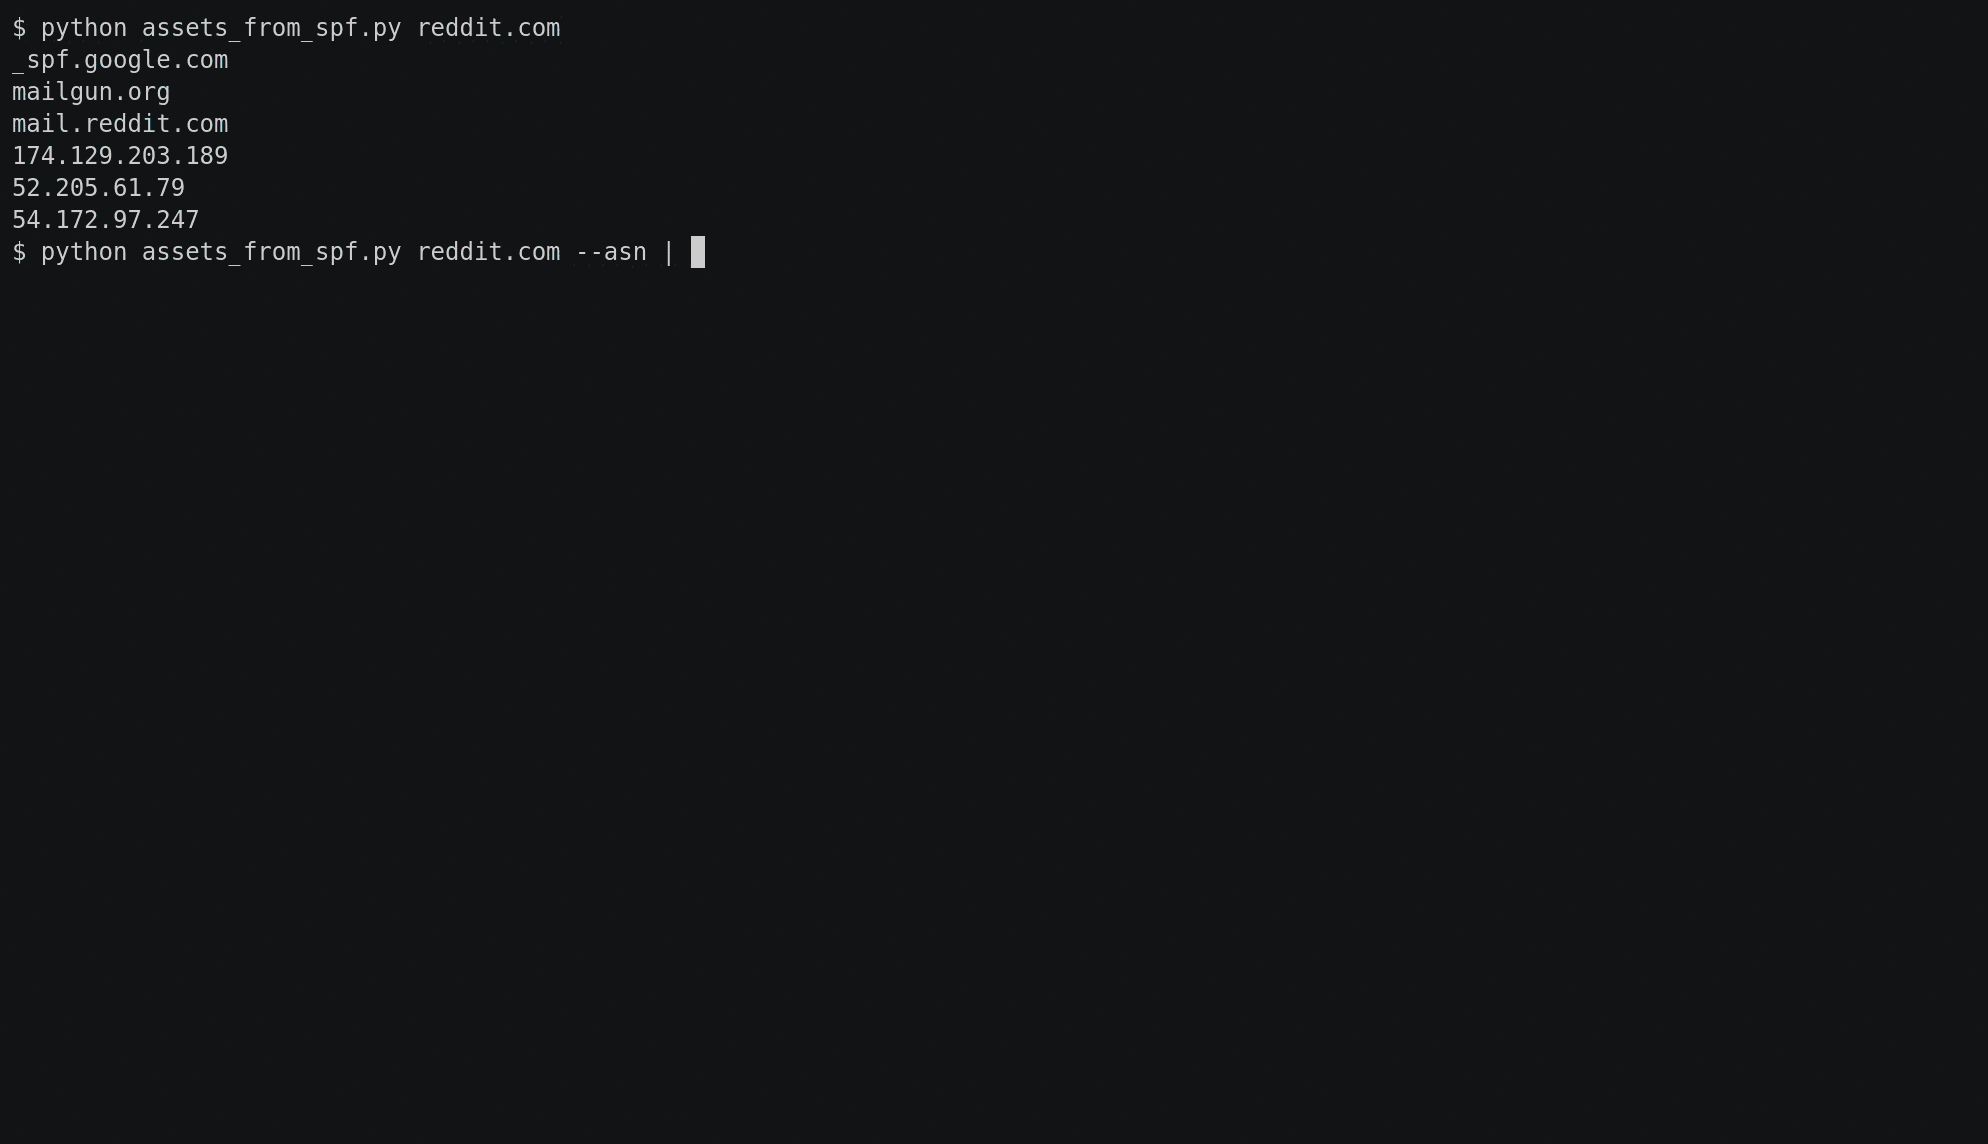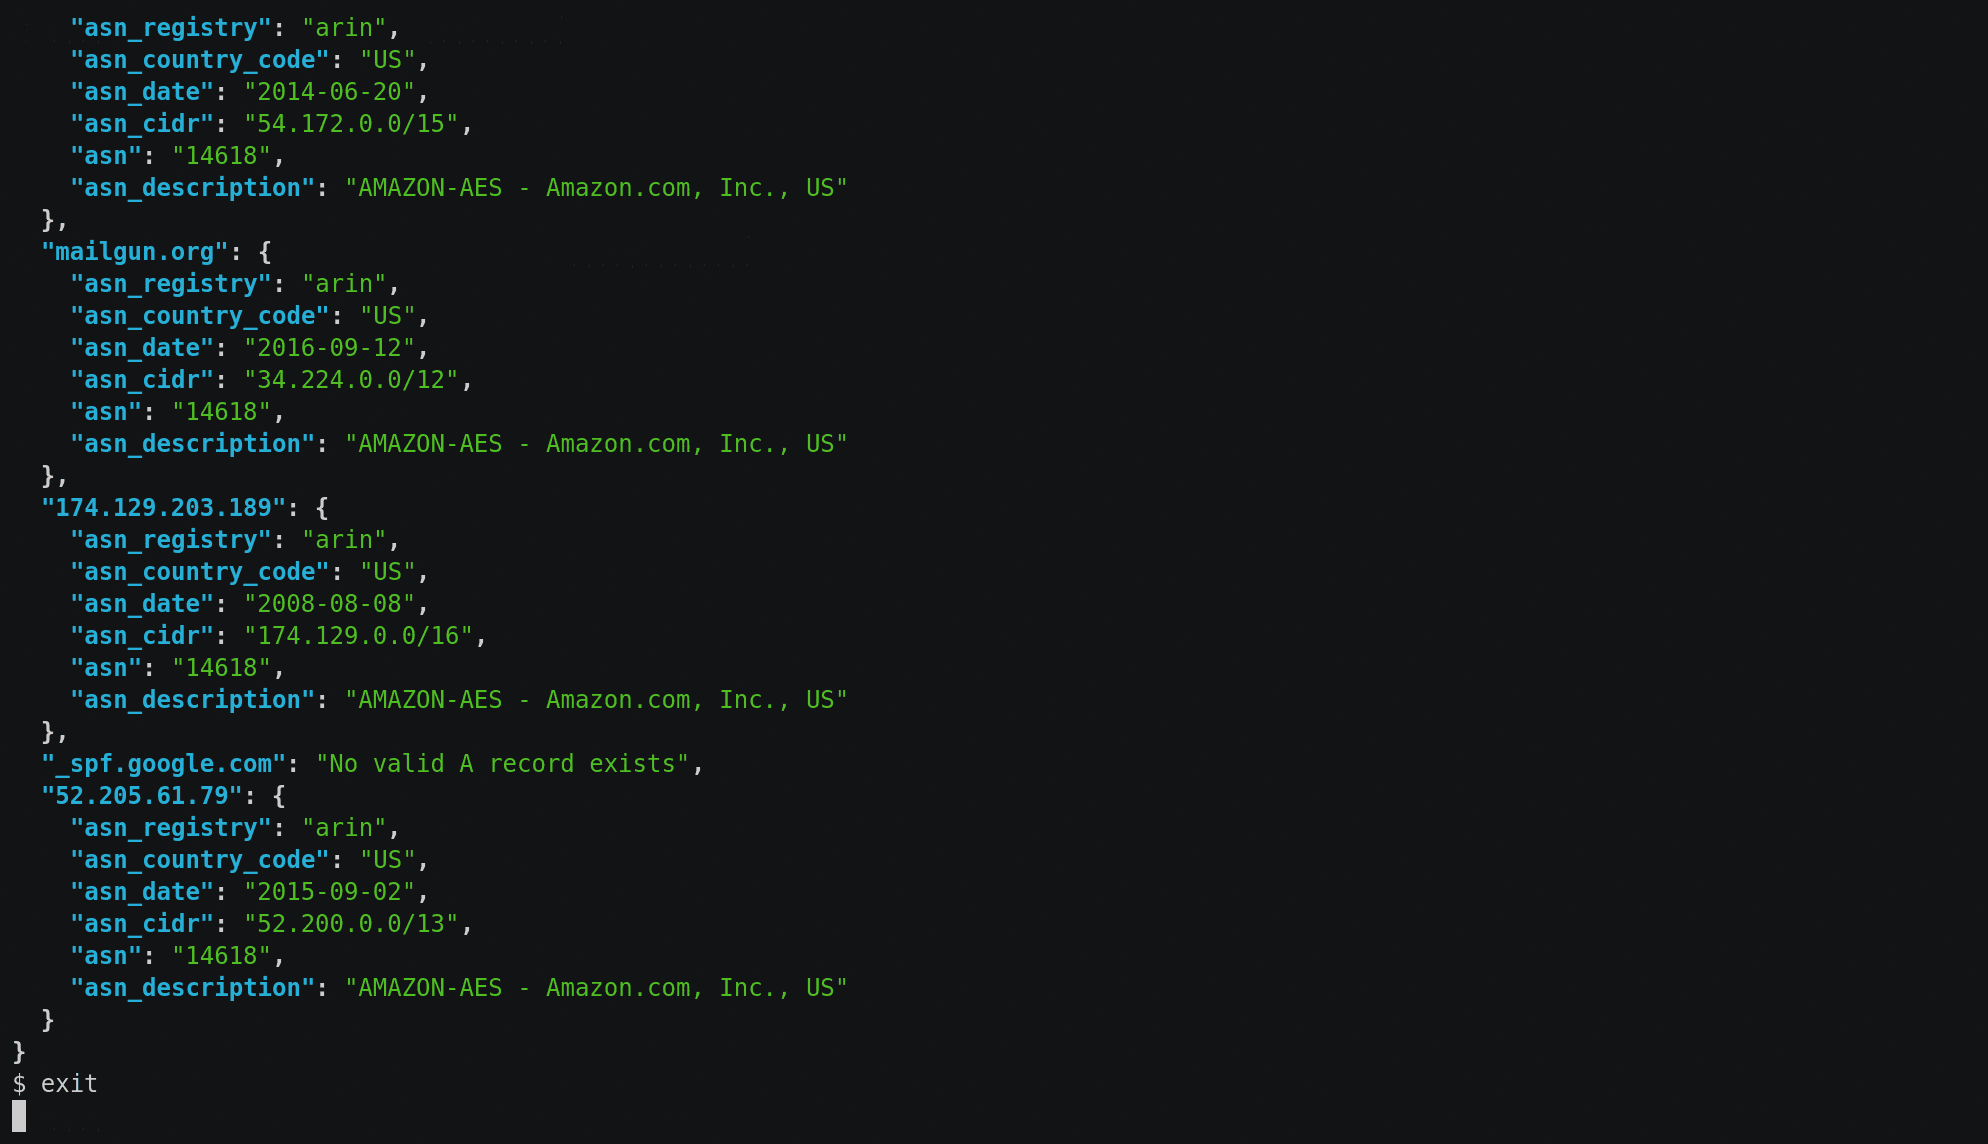 0xbharath/assets-from-spf
A Python script to parse net blocks & domain names from SPF record
 nccgroup/cloud_ip_ranges
Identify IP addresses owned by public cloud providers
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 nccgroup/fat-finger
NMAP script to enumerate users via finger
 nccgroup/nlist
An nmap script to produce target lists for use with various tools.
 nccgroup/ps2
A port scanner written purely in PowerShell.