
passer
 activecm/passer
Passive service locator, a python sniffer that identifies servers, clients, names and much more
defensive-toolsdns-analysisfingerprint-spoofing+6
2688 months ago
activecm/passerPassive service locator, a python sniffer that identifies servers, clients, names and much more
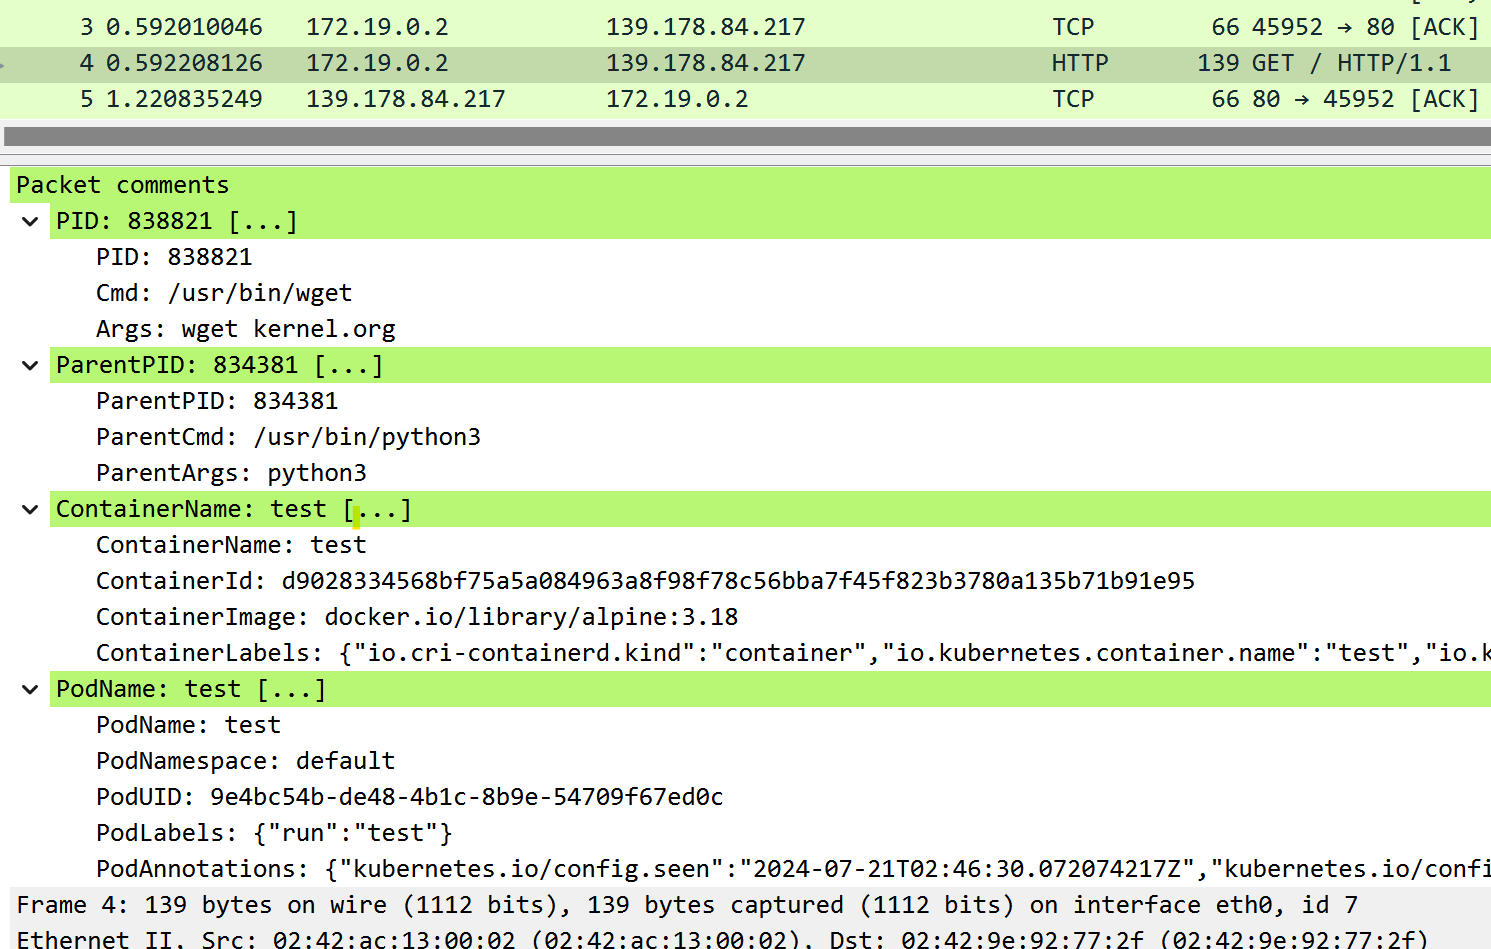 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
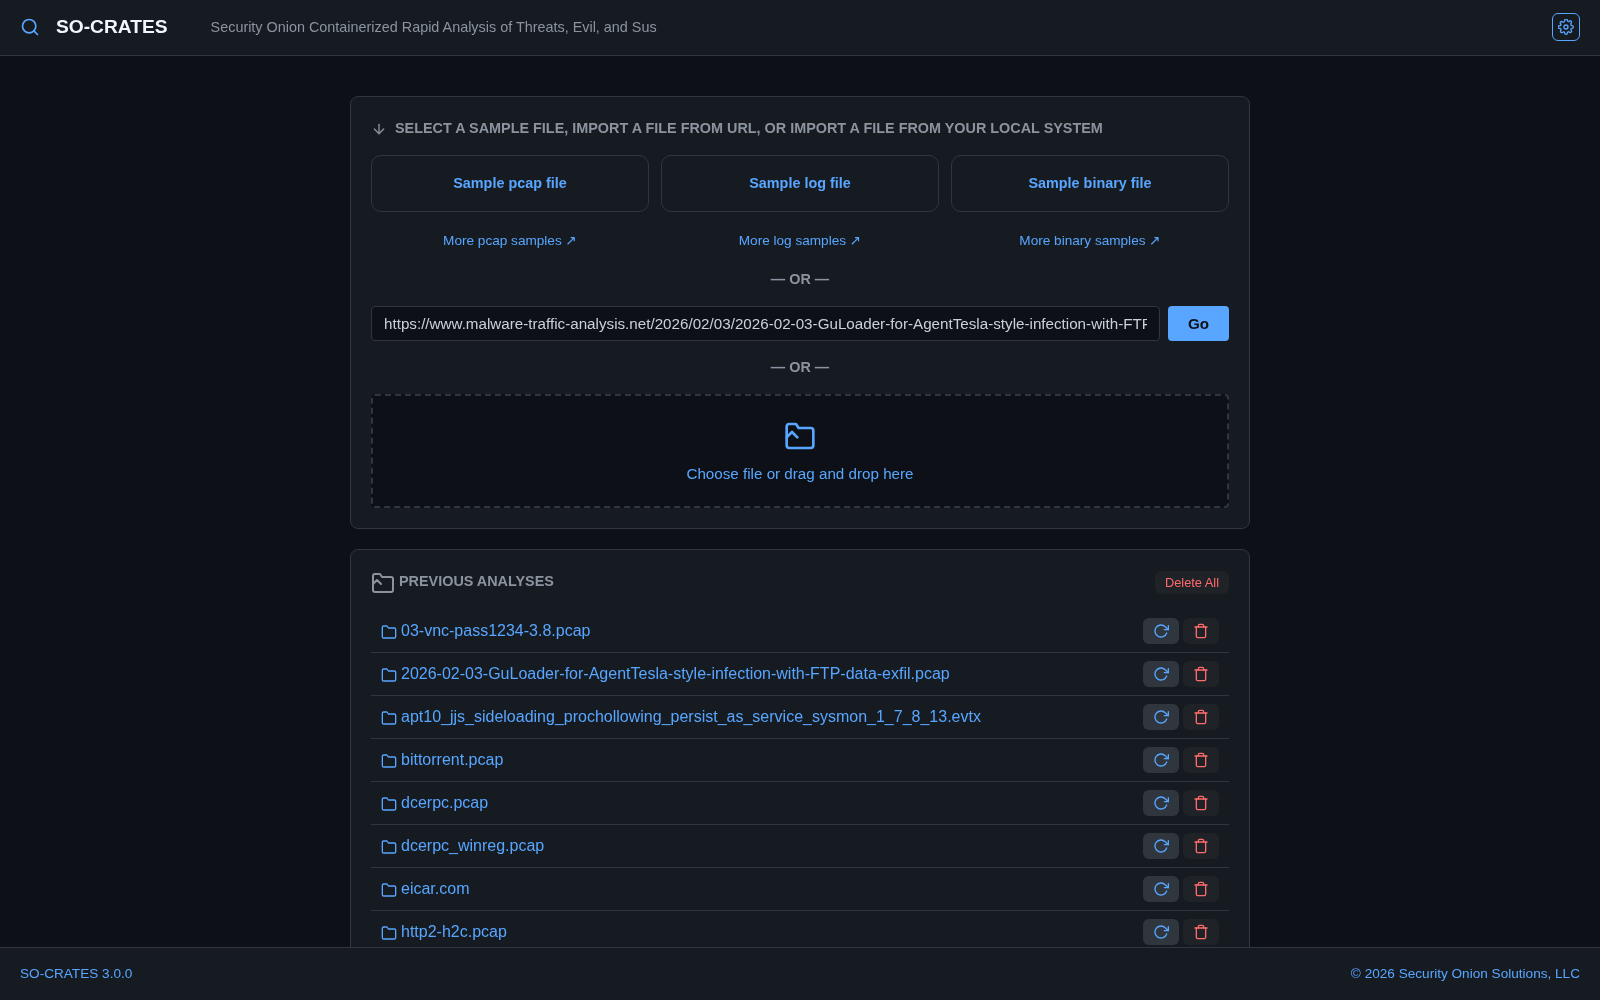 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
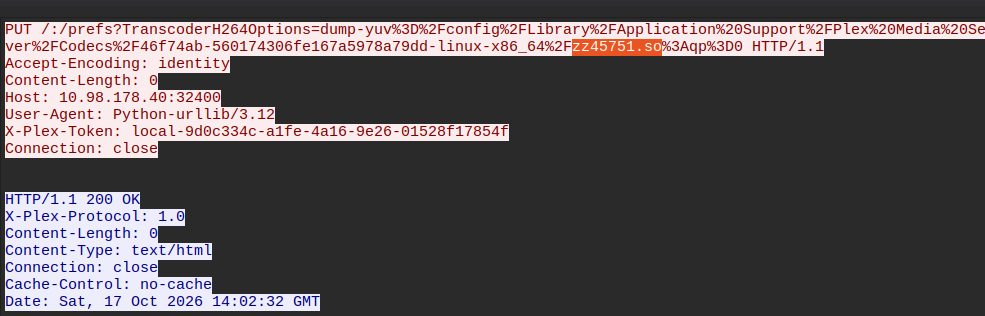 boredhackerblog/plex2shell_pcap
Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
 opposum0112/decretum
Contract LinkML compiler for a security researchers
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)