NexaCorp-DFIR-INC-2026-001

DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…

DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…

Distributed & real time digital forensics at the speed of the cloud

Dshell is a network forensic analysis framework.

This is the development tree. Production downloads are at:

TCP/IP packet demultiplexer. Download from:


Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally

Android Connections Forensics

Shell Companies Inside Apple's Privacy Relay

A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.

CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE

Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic

Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…

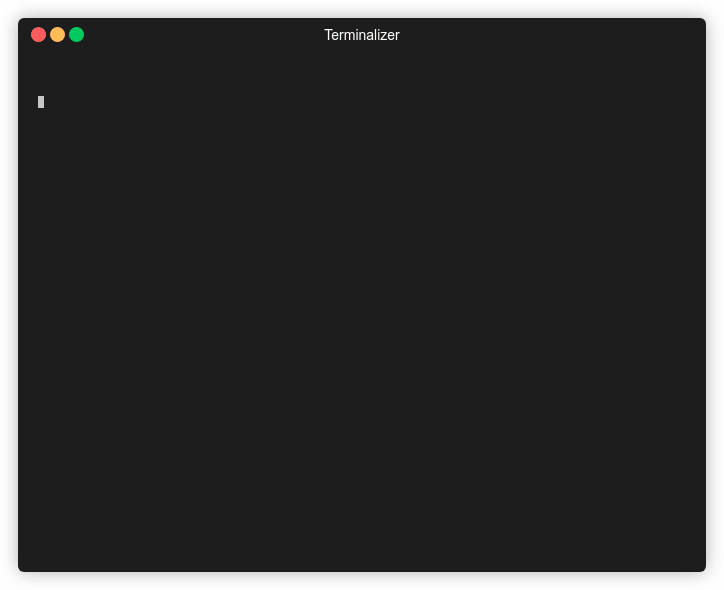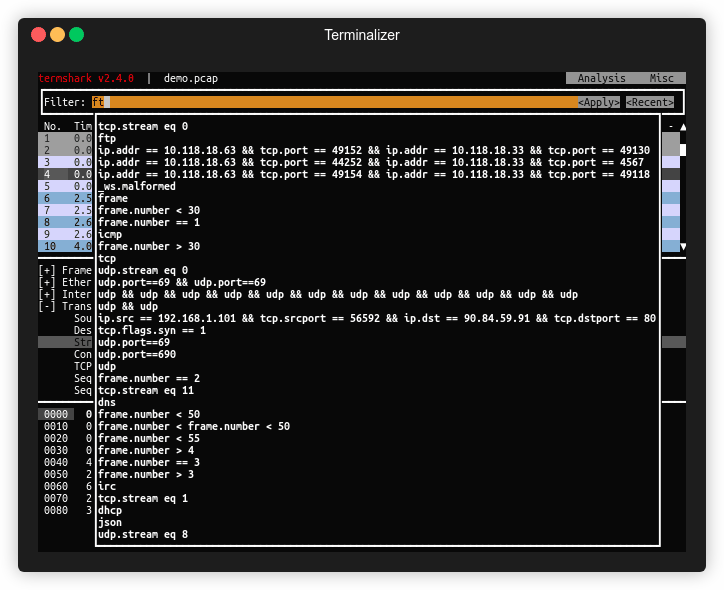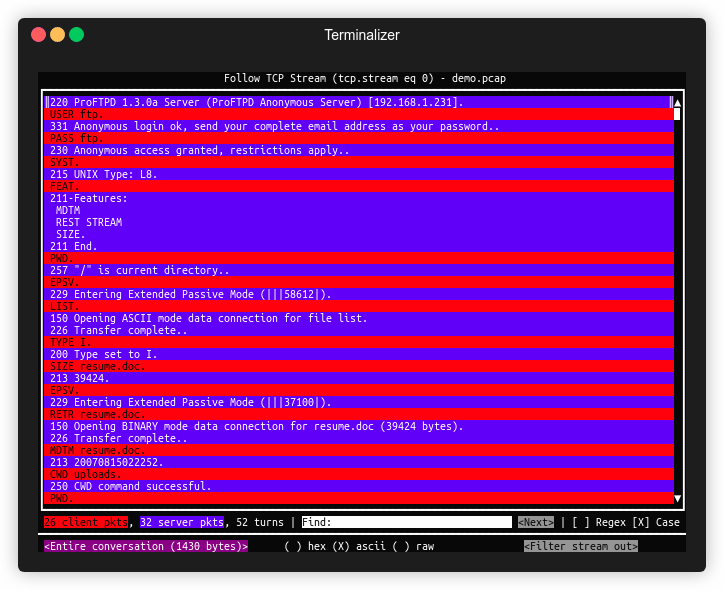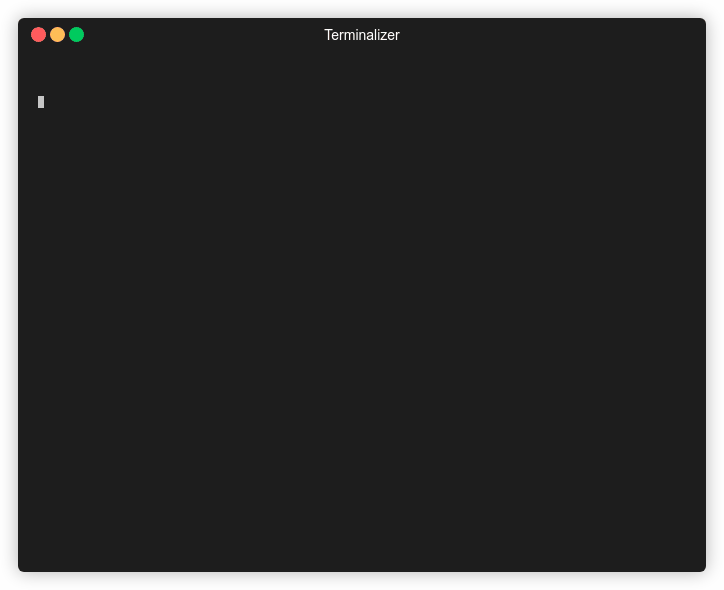
A terminal UI for tshark, inspired by Wireshark

Provides packet processing capabilities for Go

A Swiss army knife for your daily Linux network plumbing.

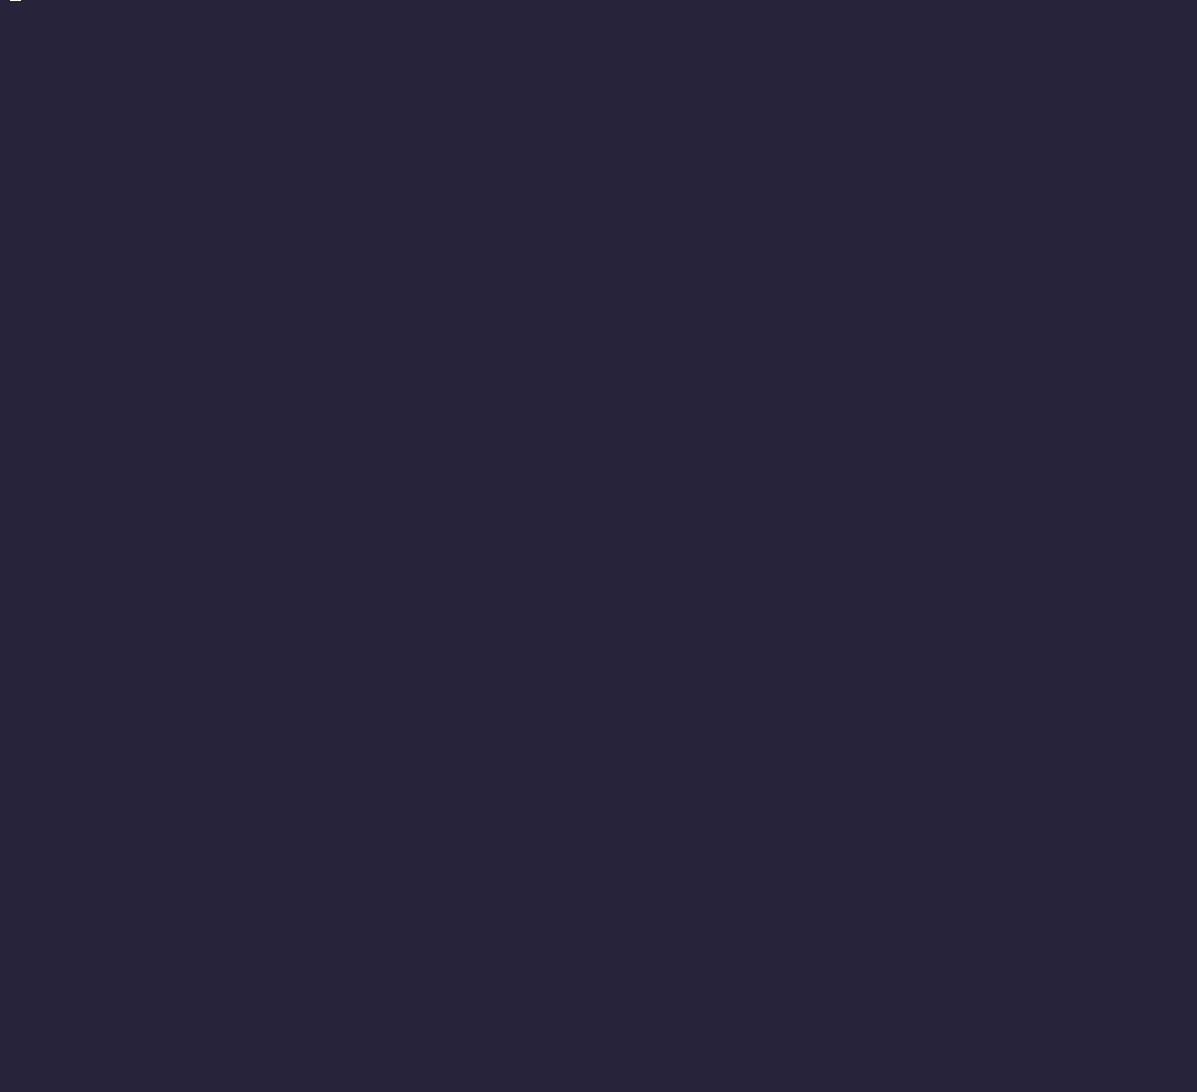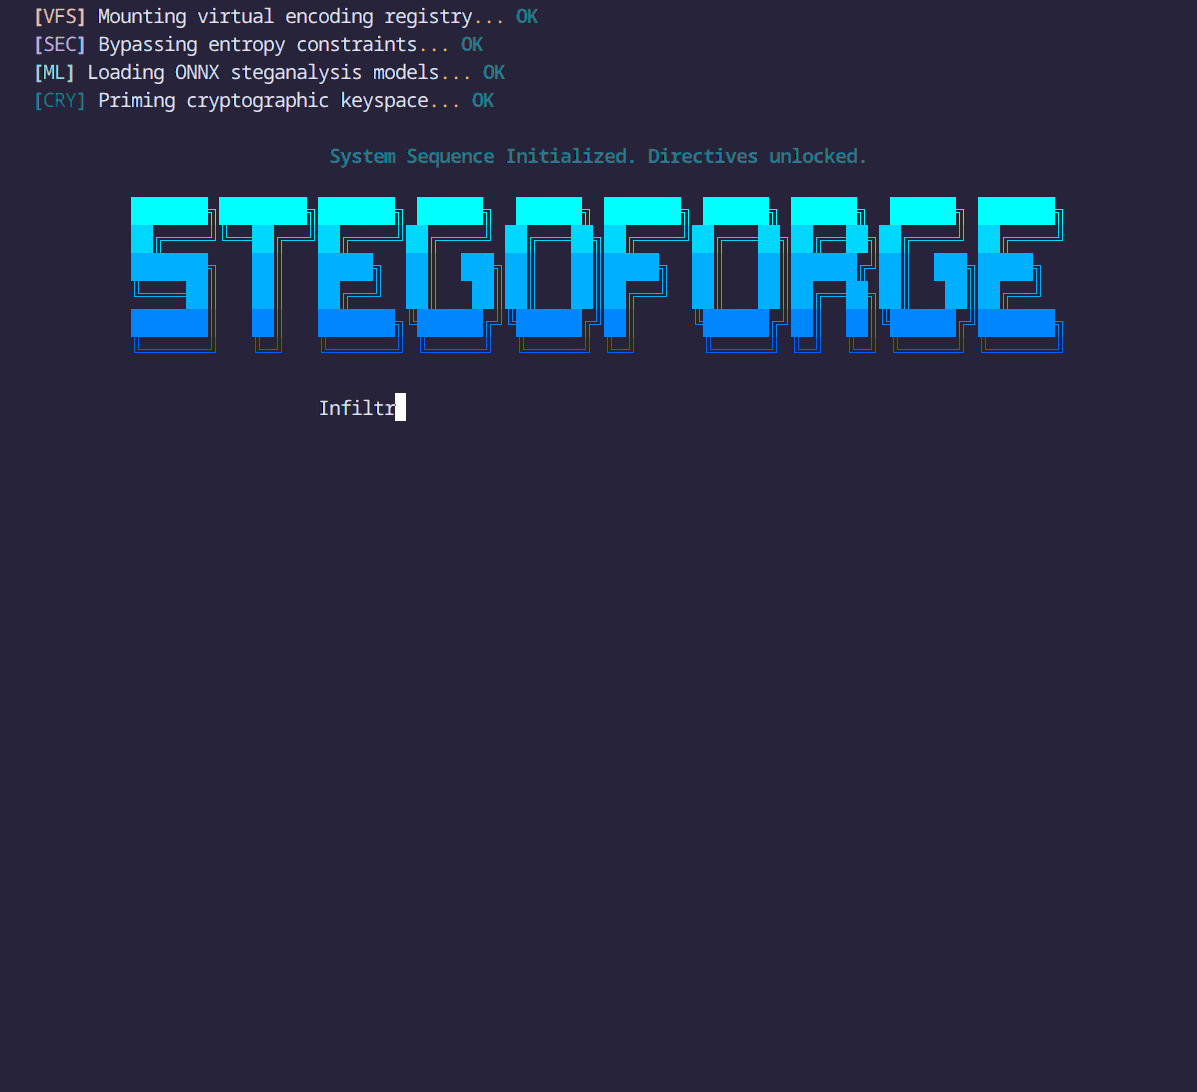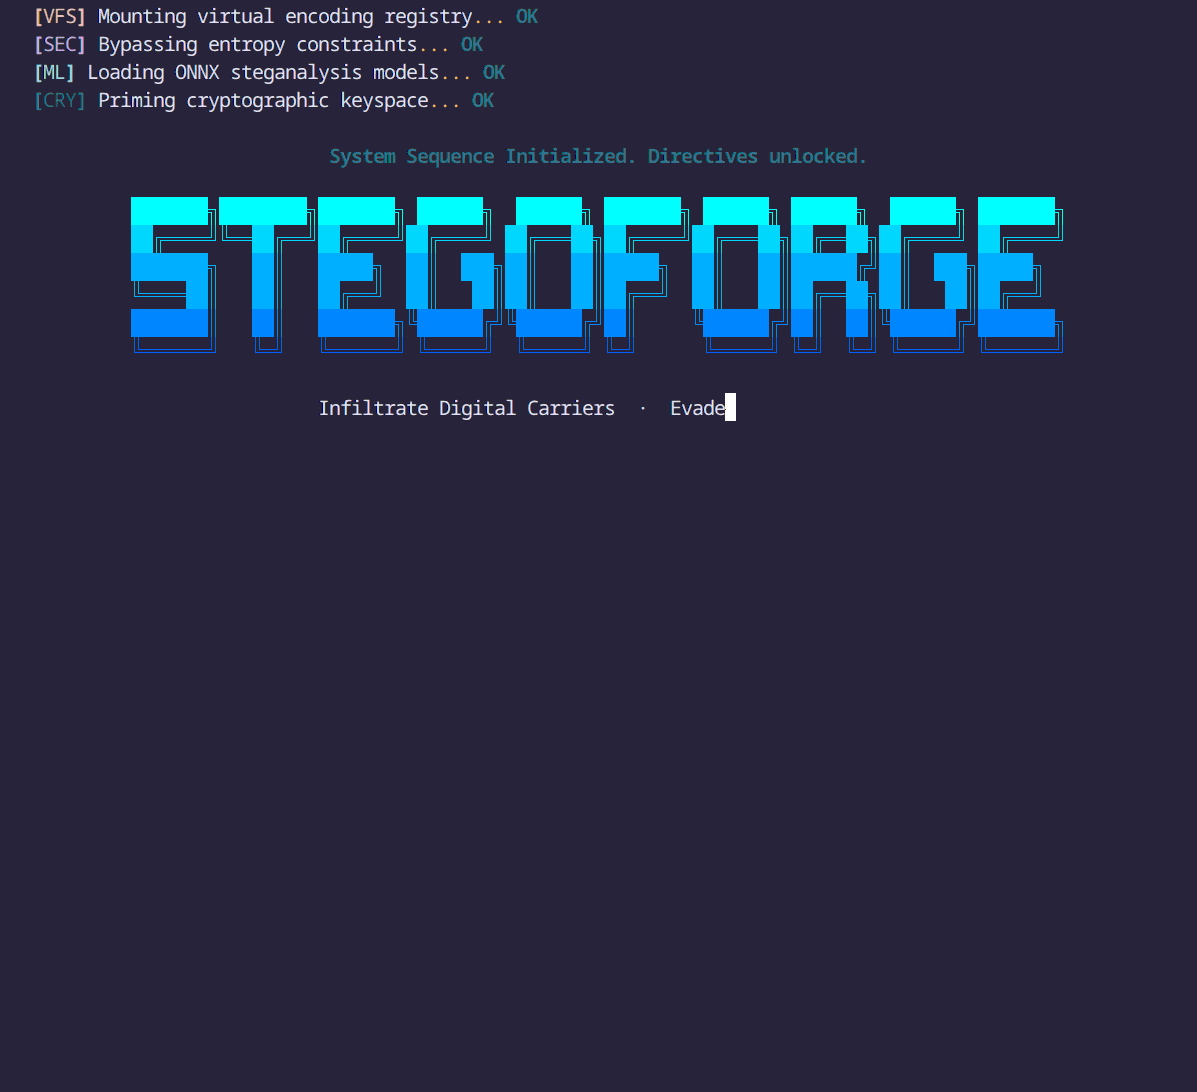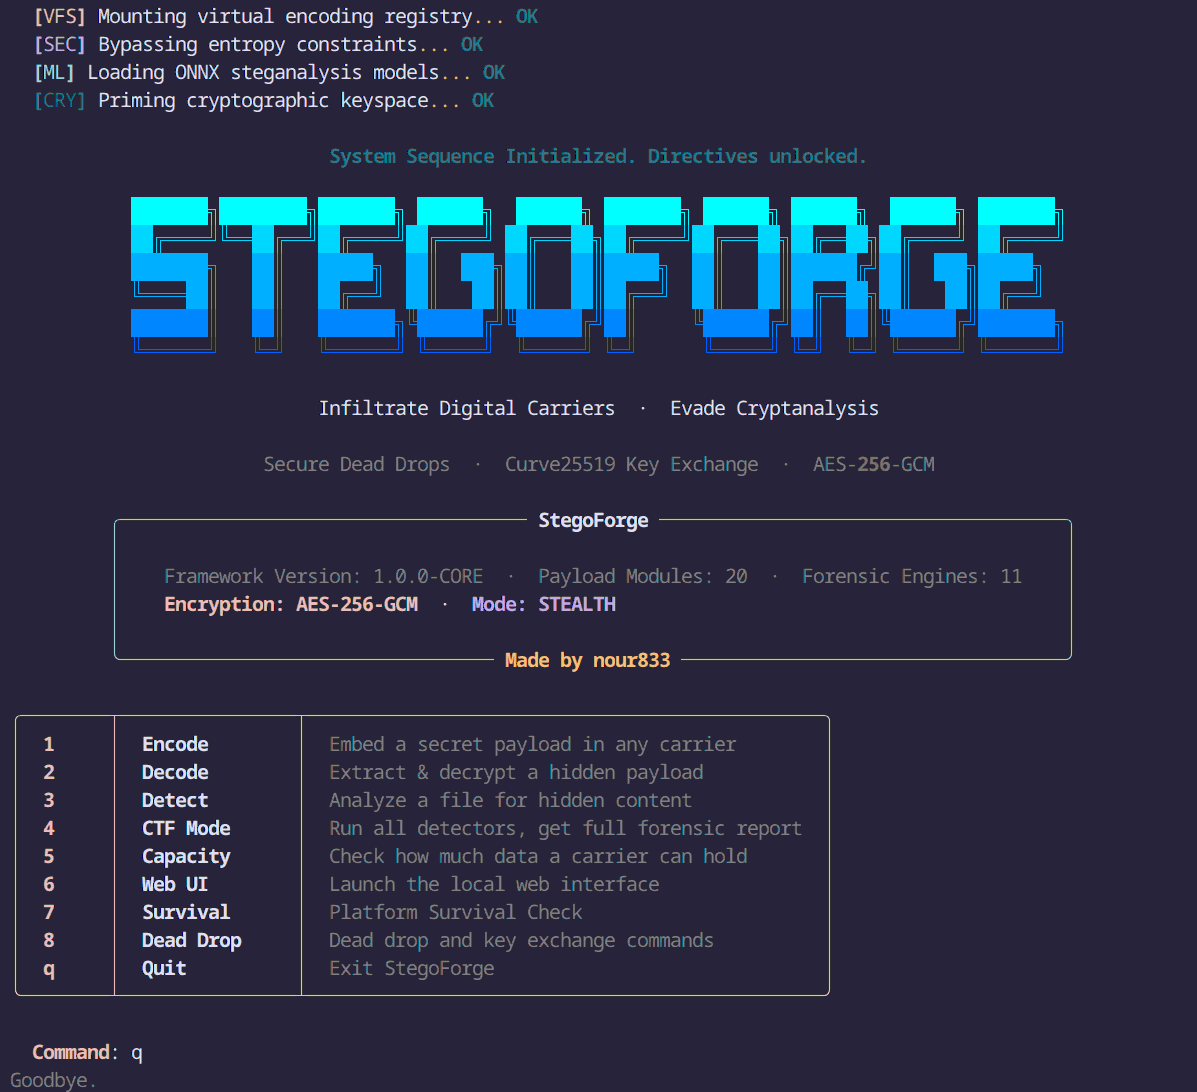
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…