
RITA-J
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
anomaly-detectiondns-analysislog-analysis+3
216
cyb3r-monk/rita-jImplementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.

 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark

 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
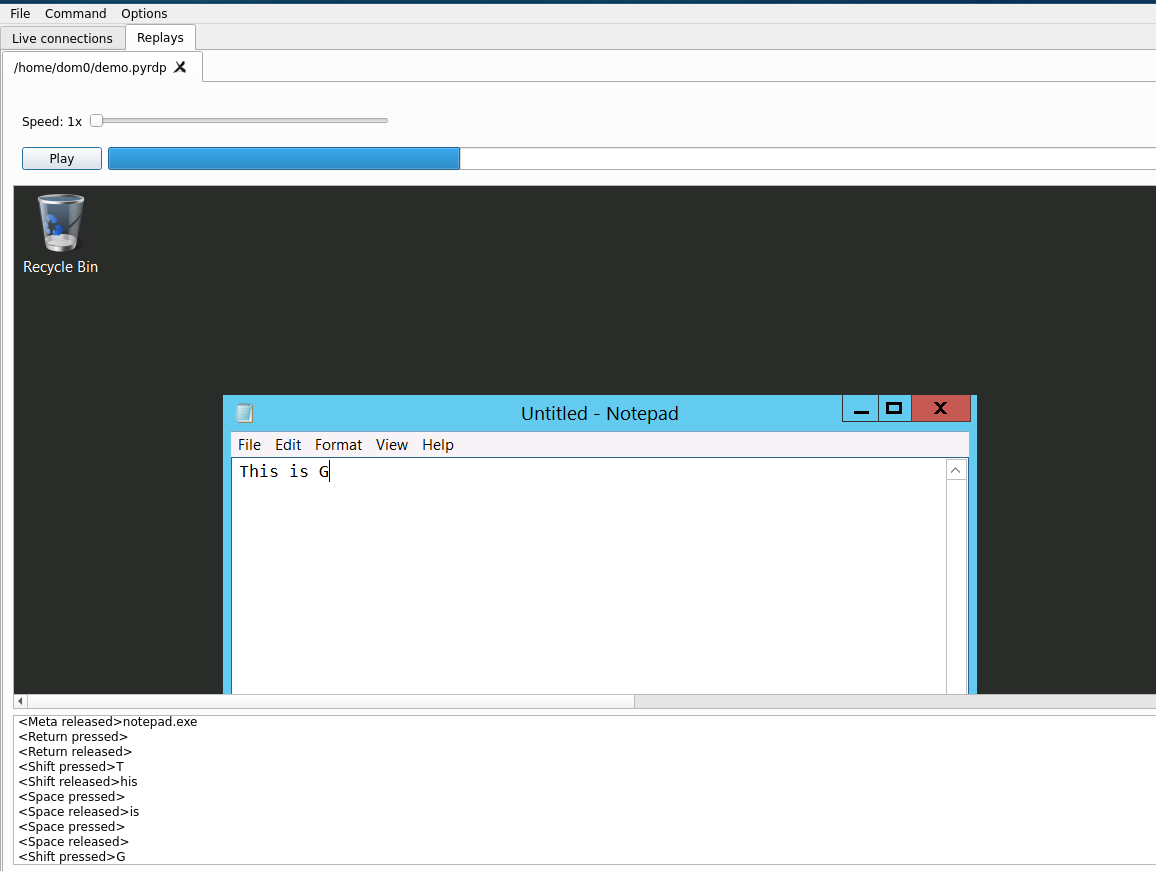 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
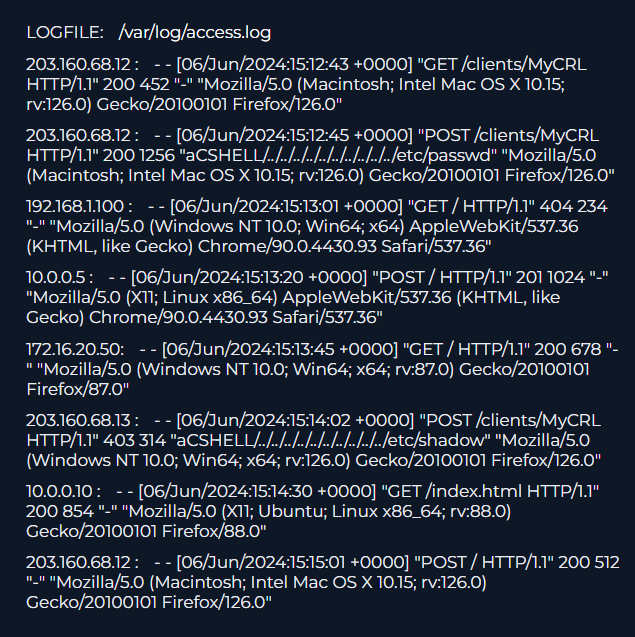 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
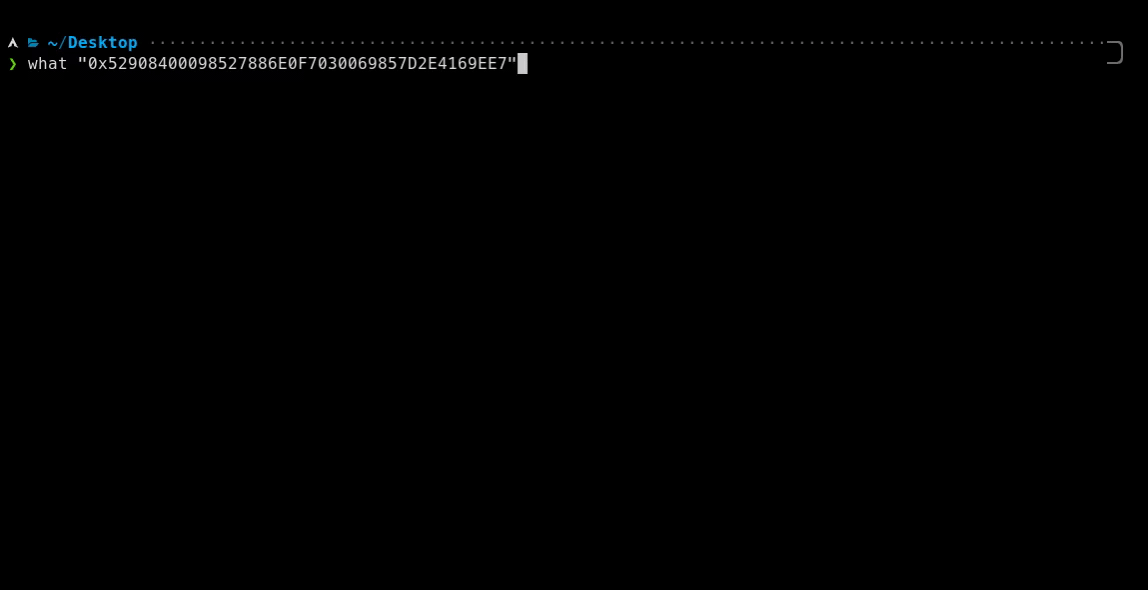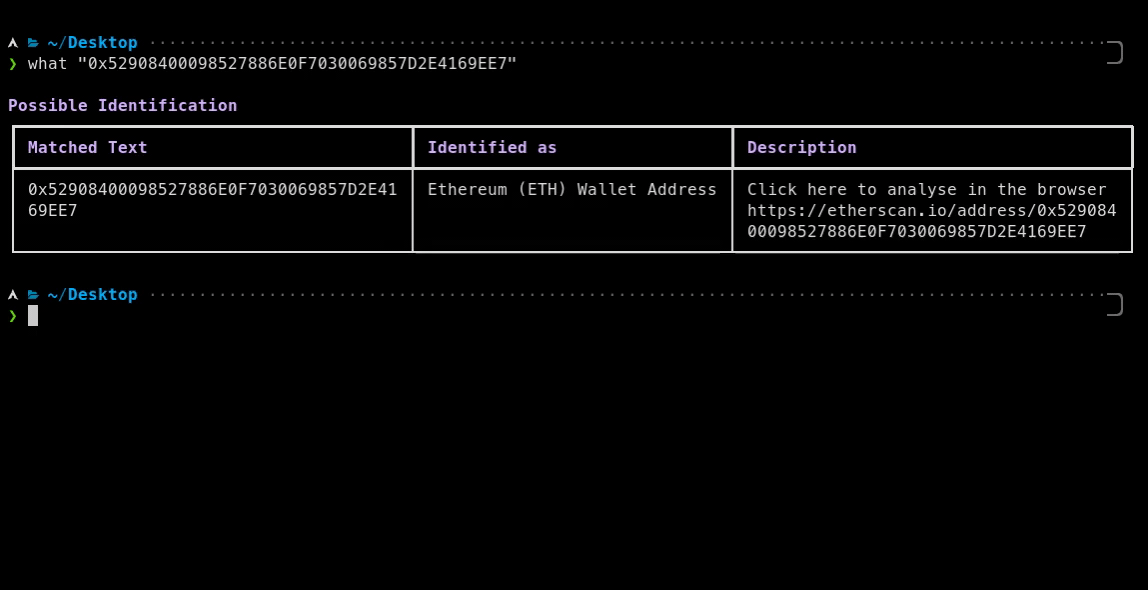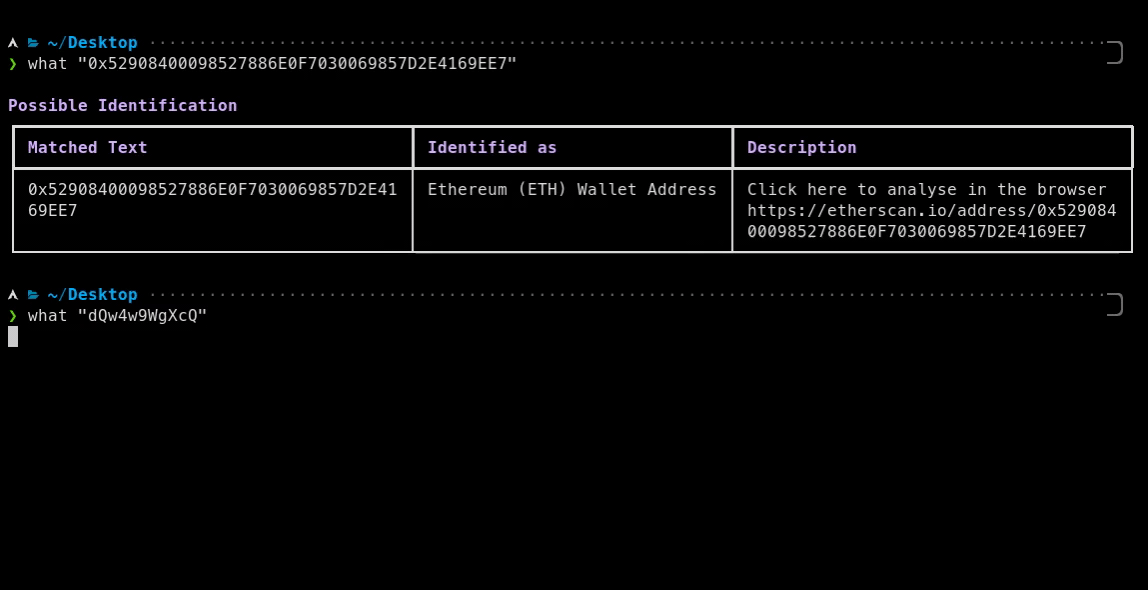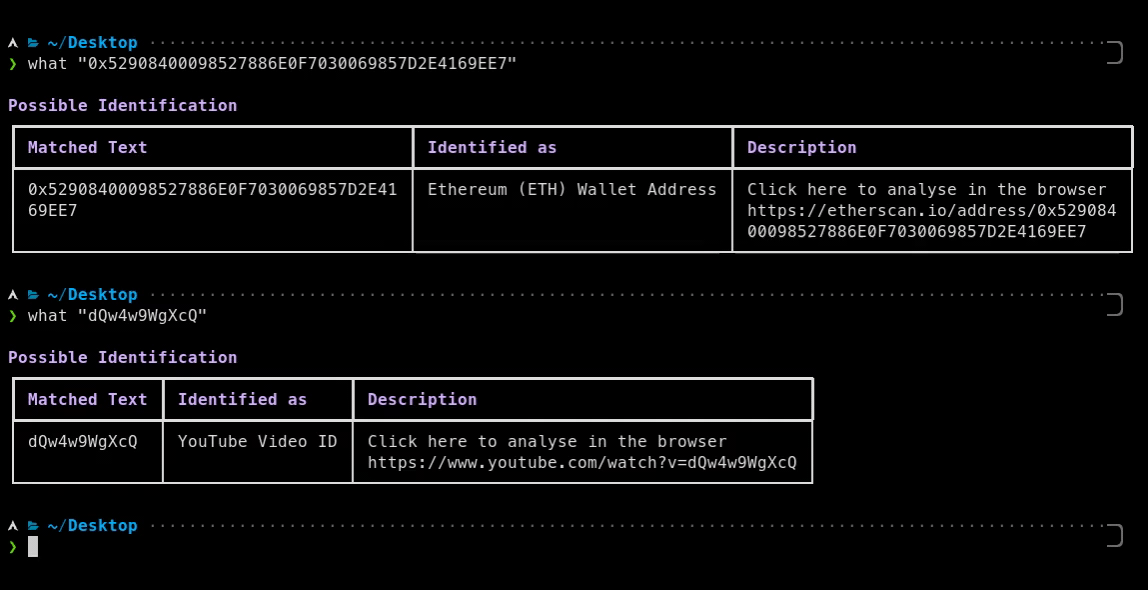 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
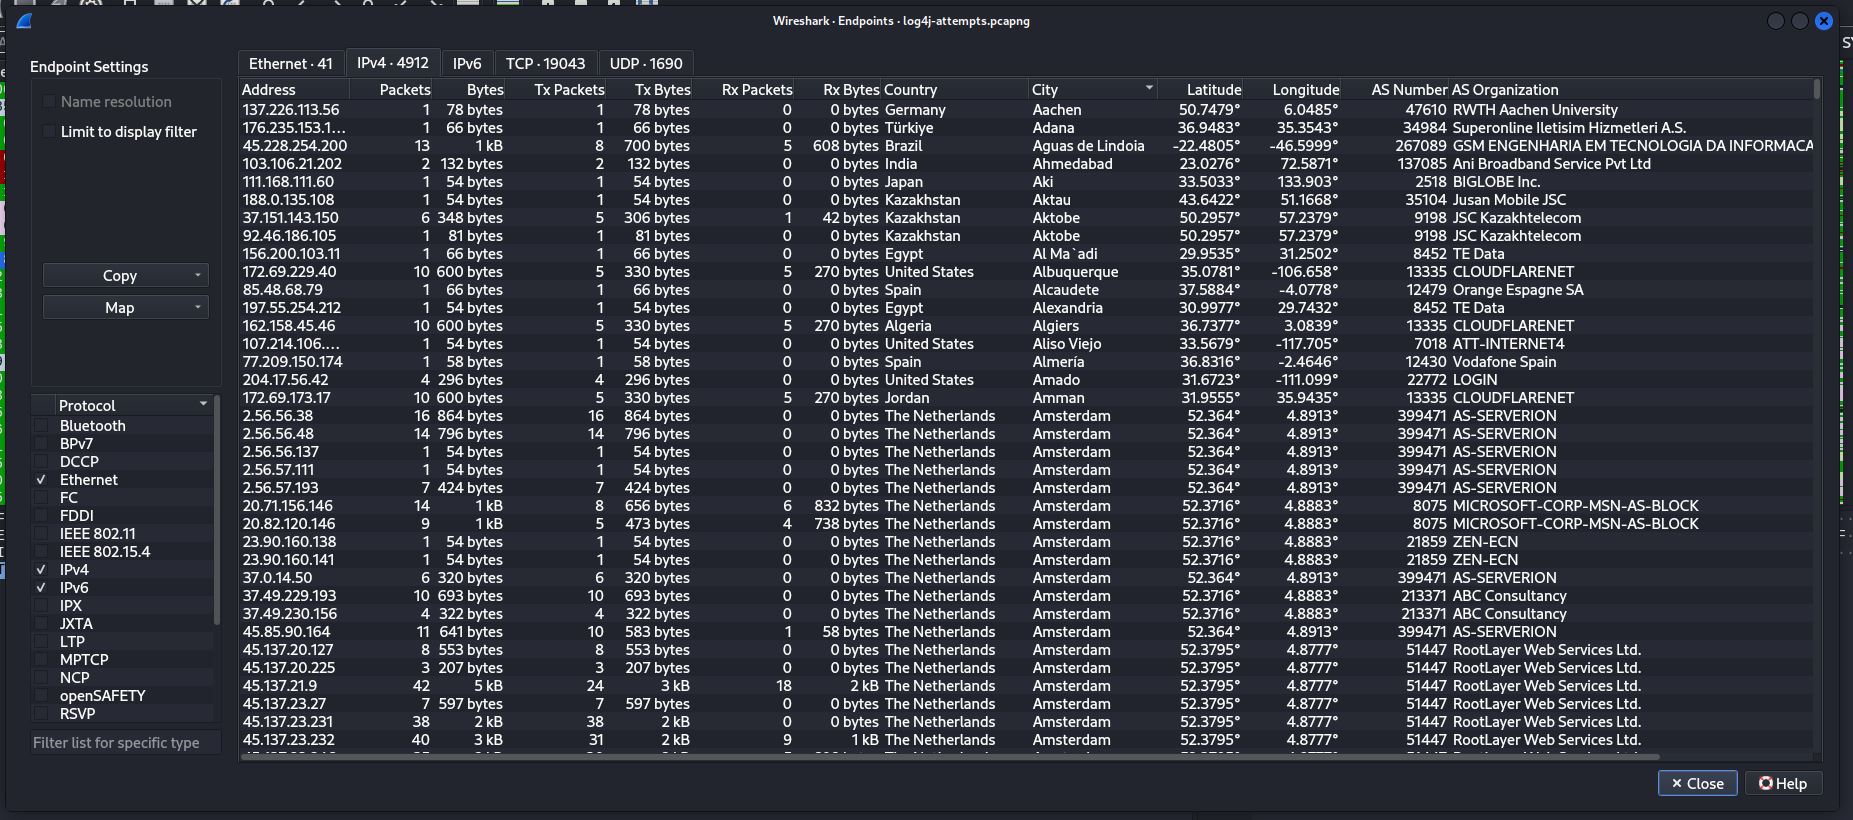 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis