
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
145 results
PcapPlusPlus preview

PcapPlusPlus

GitHubseladb/pcapplusplus

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
crawlerdns-analysisforensics+5
3.1k
7 days ago
passer preview

passer

GitHubactivecm/passer

Passive service locator, a python sniffer that identifies servers, clients, names and much more

defensive-toolsdns-analysisfingerprint-spoofing+6
2688 months ago
scapy preview

scapy

GitHubsecdev/scapy

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

bluetooth-securitycryptographydata-exfiltration+23
12.5k1 day ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
2.7k11 days ago
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

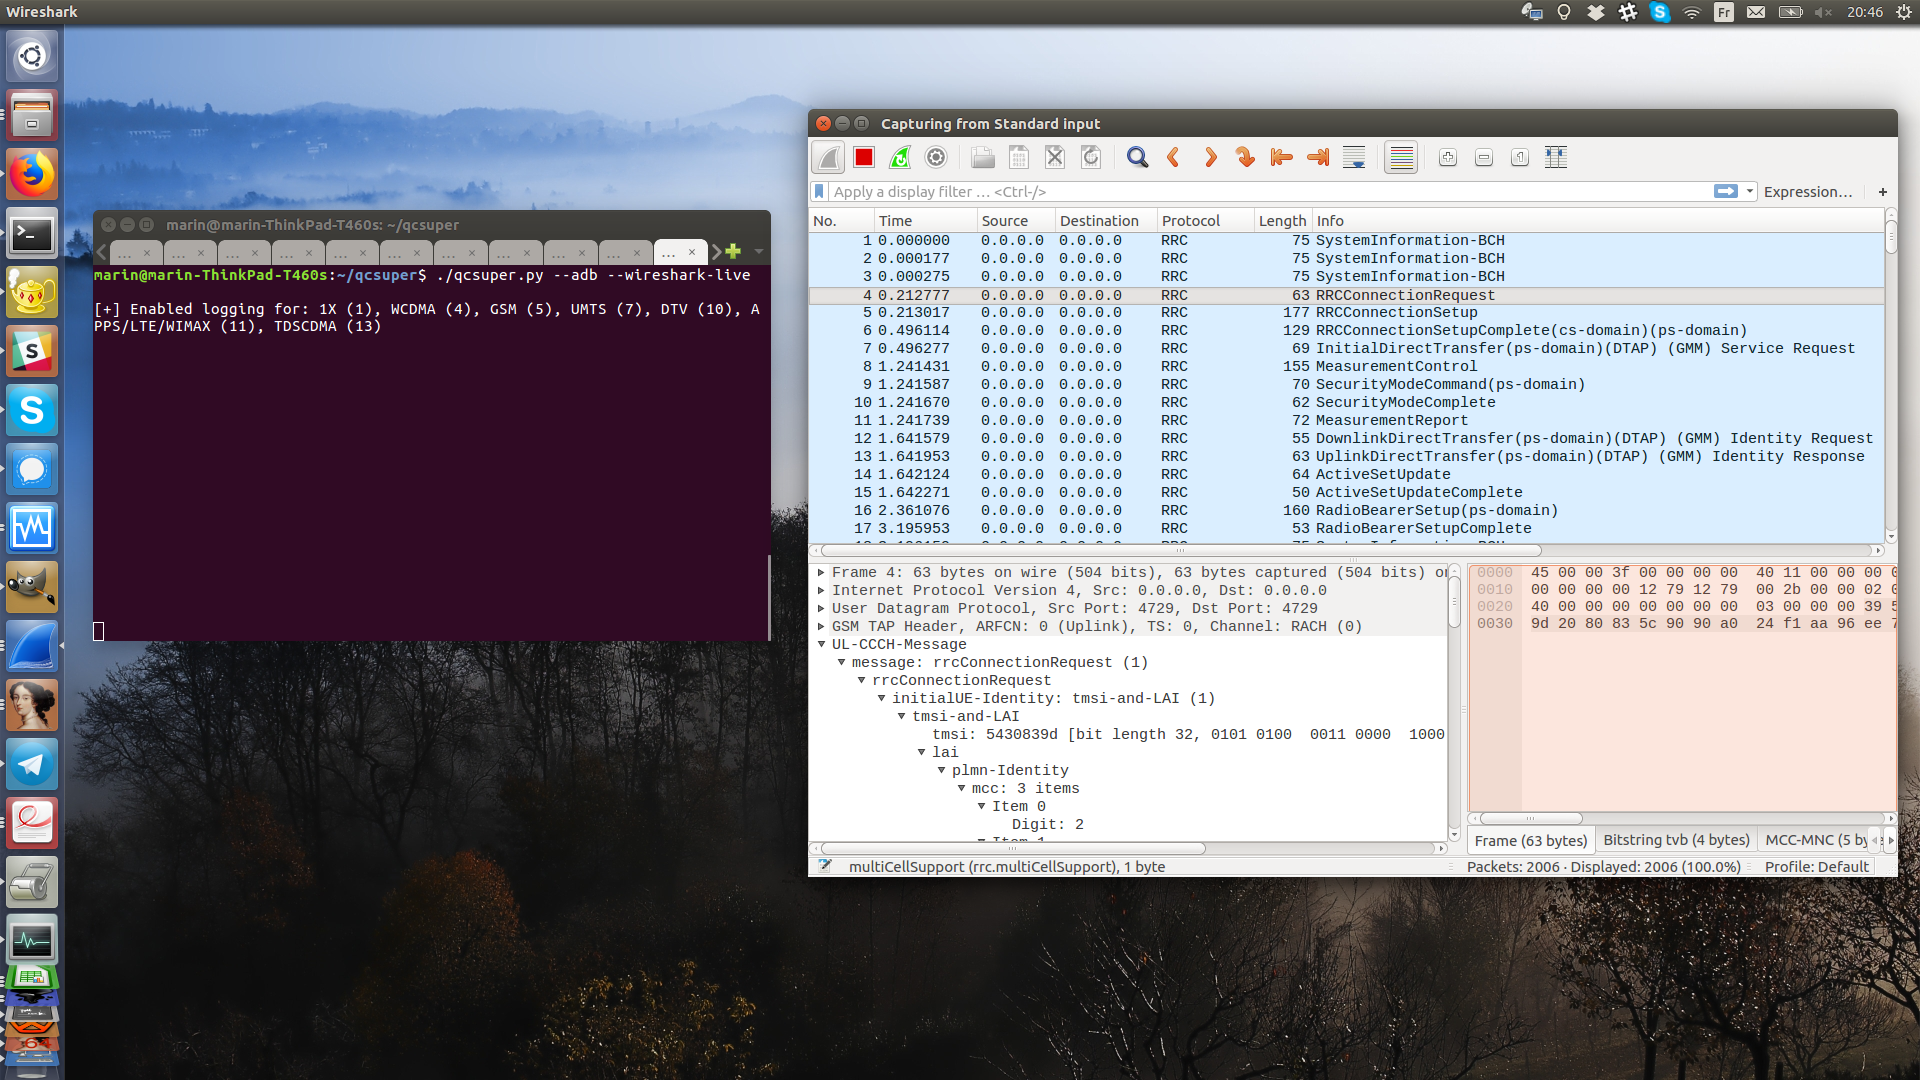
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.6k15 days ago
ptcpdump preview

ptcpdump

GitHubmozillazg/ptcpdump

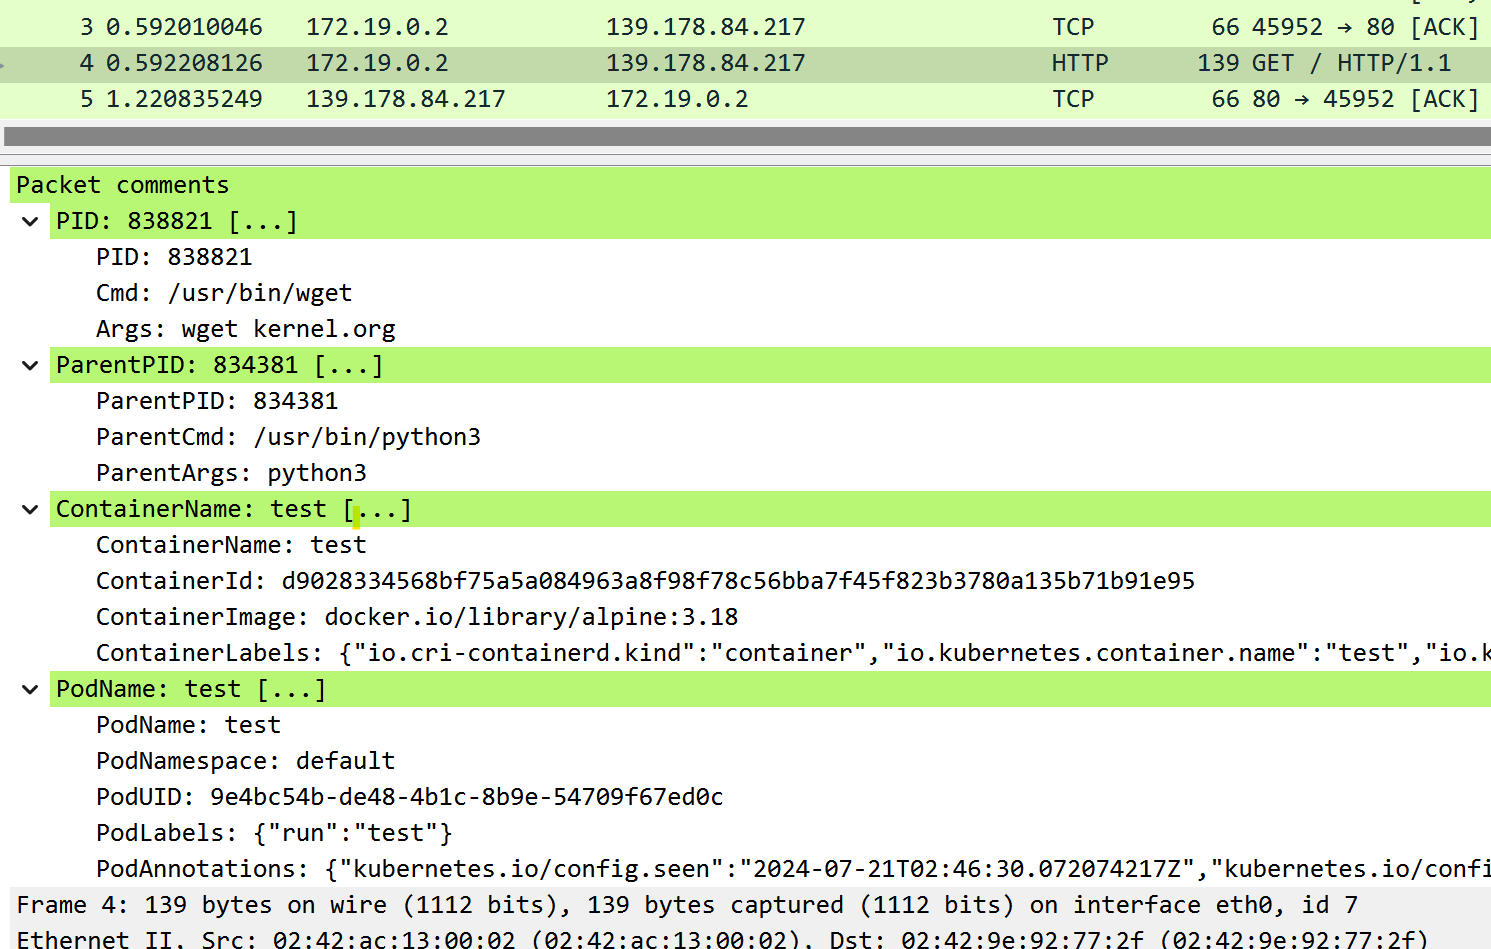
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k2 days ago
fatt preview

fatt

GitHub0x4d31/fatt

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
network-forensicspacket-sniffing-analysisthreat-intelligence
6844 years ago
CyberScan preview

CyberScan

GitHubmedbenali/cyberscan

Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
information-gatheringnetwork-forensicsnetwork-mapping+3
4646 months ago
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files

data-recoverydigital-forensicsforensics+2
2296 years ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

command-and-controldigital-forensicseducation+8
101 year ago
SecLog preview

SecLog

GitHubseclog-open/seclog

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

anomaly-detectiondynamic-analysis-sandboxingeducation+6
212 days ago
Qu1cksc0pe preview

Qu1cksc0pe

GitHubcyb3rmx/qu1cksc0pe

All-in-One malware analysis tool.

android-securitydynamic-analysis-sandboxingforensics+4
2.0k1 month ago
ja4 preview

ja4

GitHubfoxio-llc/ja4

JA4+ is a suite of network fingerprinting standards
dns-analysisencryption-decryption-toolsfingerprint-spoofing+9
2.0k28 days ago
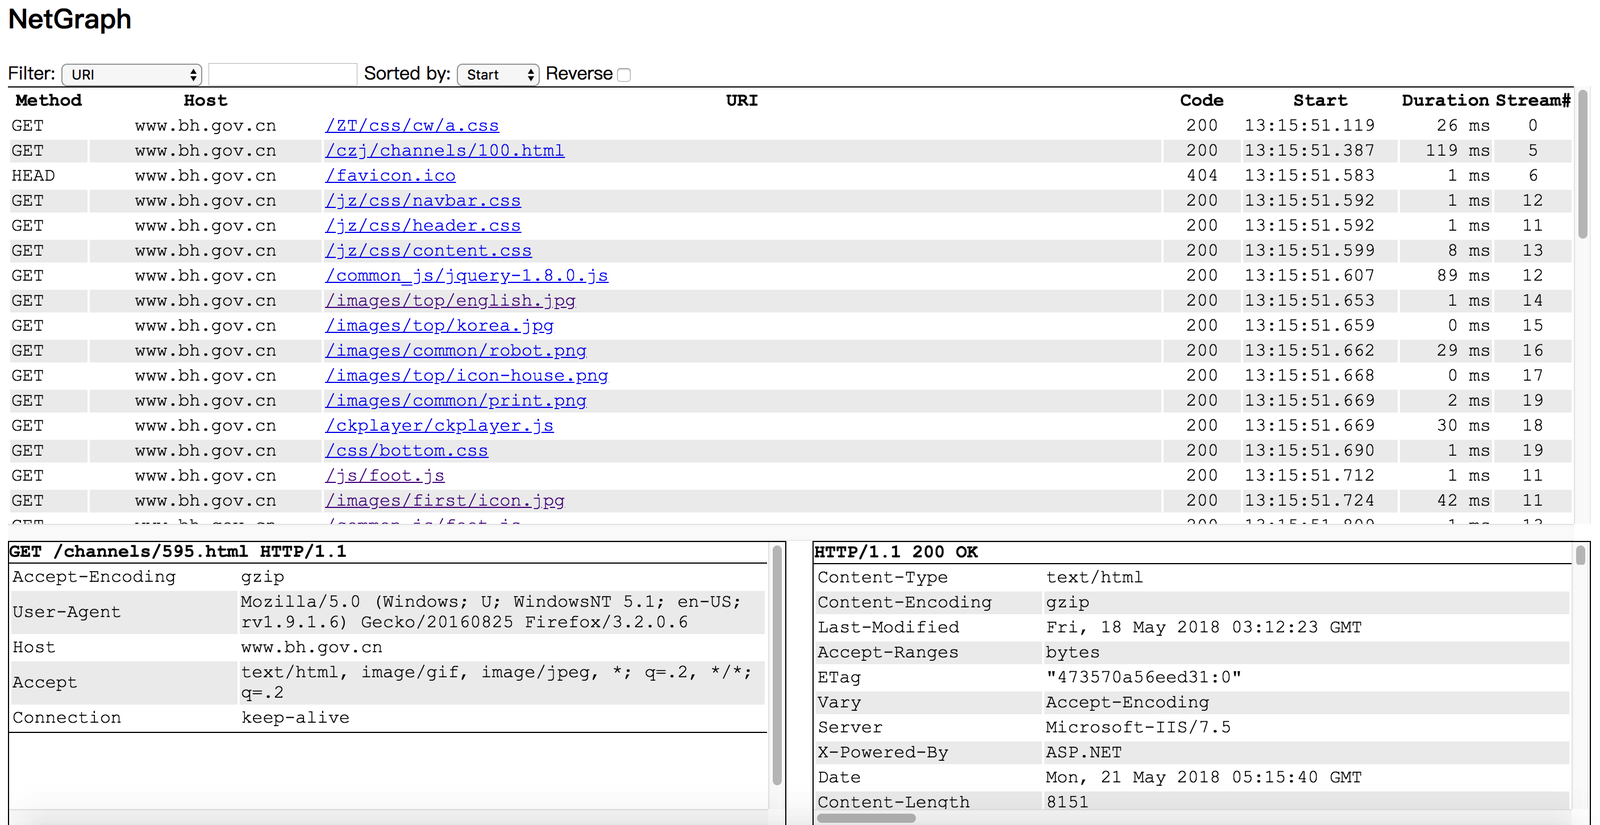
netgraph preview

netgraph

GitHubga0/netgraph

A cross platform http sniffer with a web UI

information-gatheringnetwork-forensicspacket-sniffing-analysis+2
9563 years ago
DFIR-Companion preview

DFIR-Companion

GitHubhasamba/dfir-companion

DFIR forensics companion server + capture extension

ai-securitydefensive-toolsdigital-forensics+9
361 day ago
NexaCorp-DFIR-INC-2026-001 preview

NexaCorp-DFIR-INC-2026-001

GitHubjhatchi/nexacorp-dfir-inc-2026-001

DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…

digital-forensicseducationincident-response+6
4 months ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.2k9h 5m ago
tcpdump preview

tcpdump

GitHubthe-tcpdump-group/tcpdump

the TCPdump network dissector

dns-analysisforensicslog-analysis+5
3.2k13 days ago
Previous123…9Next