

SecLog
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
anomaly-detectiondynamic-analysis-sandboxingeducation+6
seclog-open/seclogCollects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
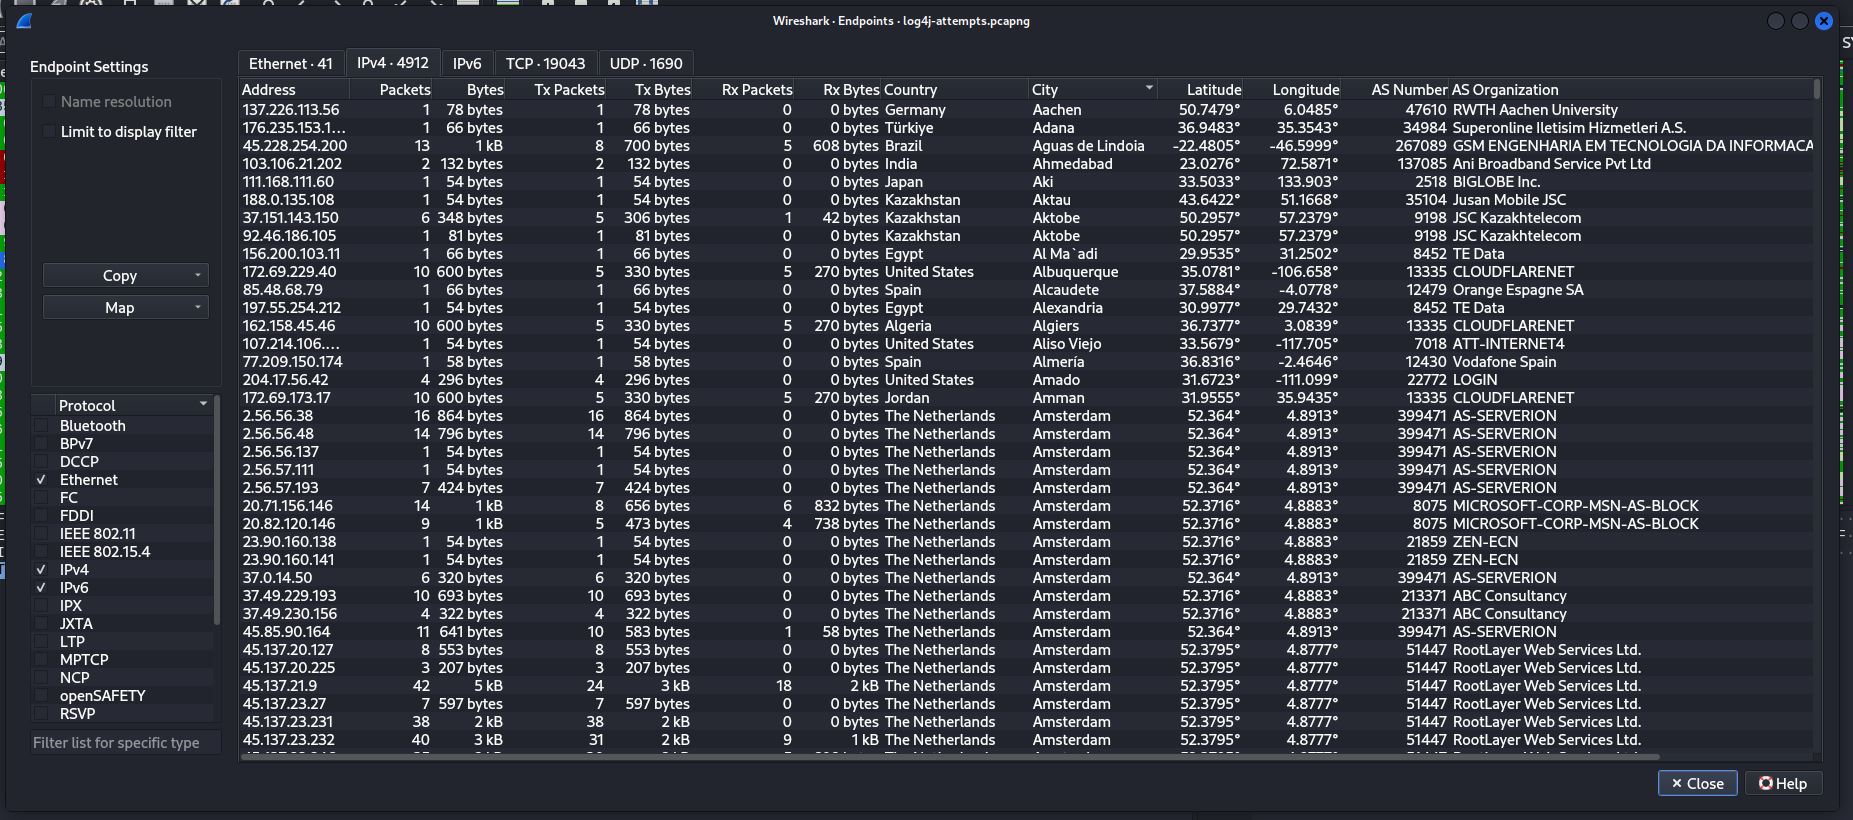 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
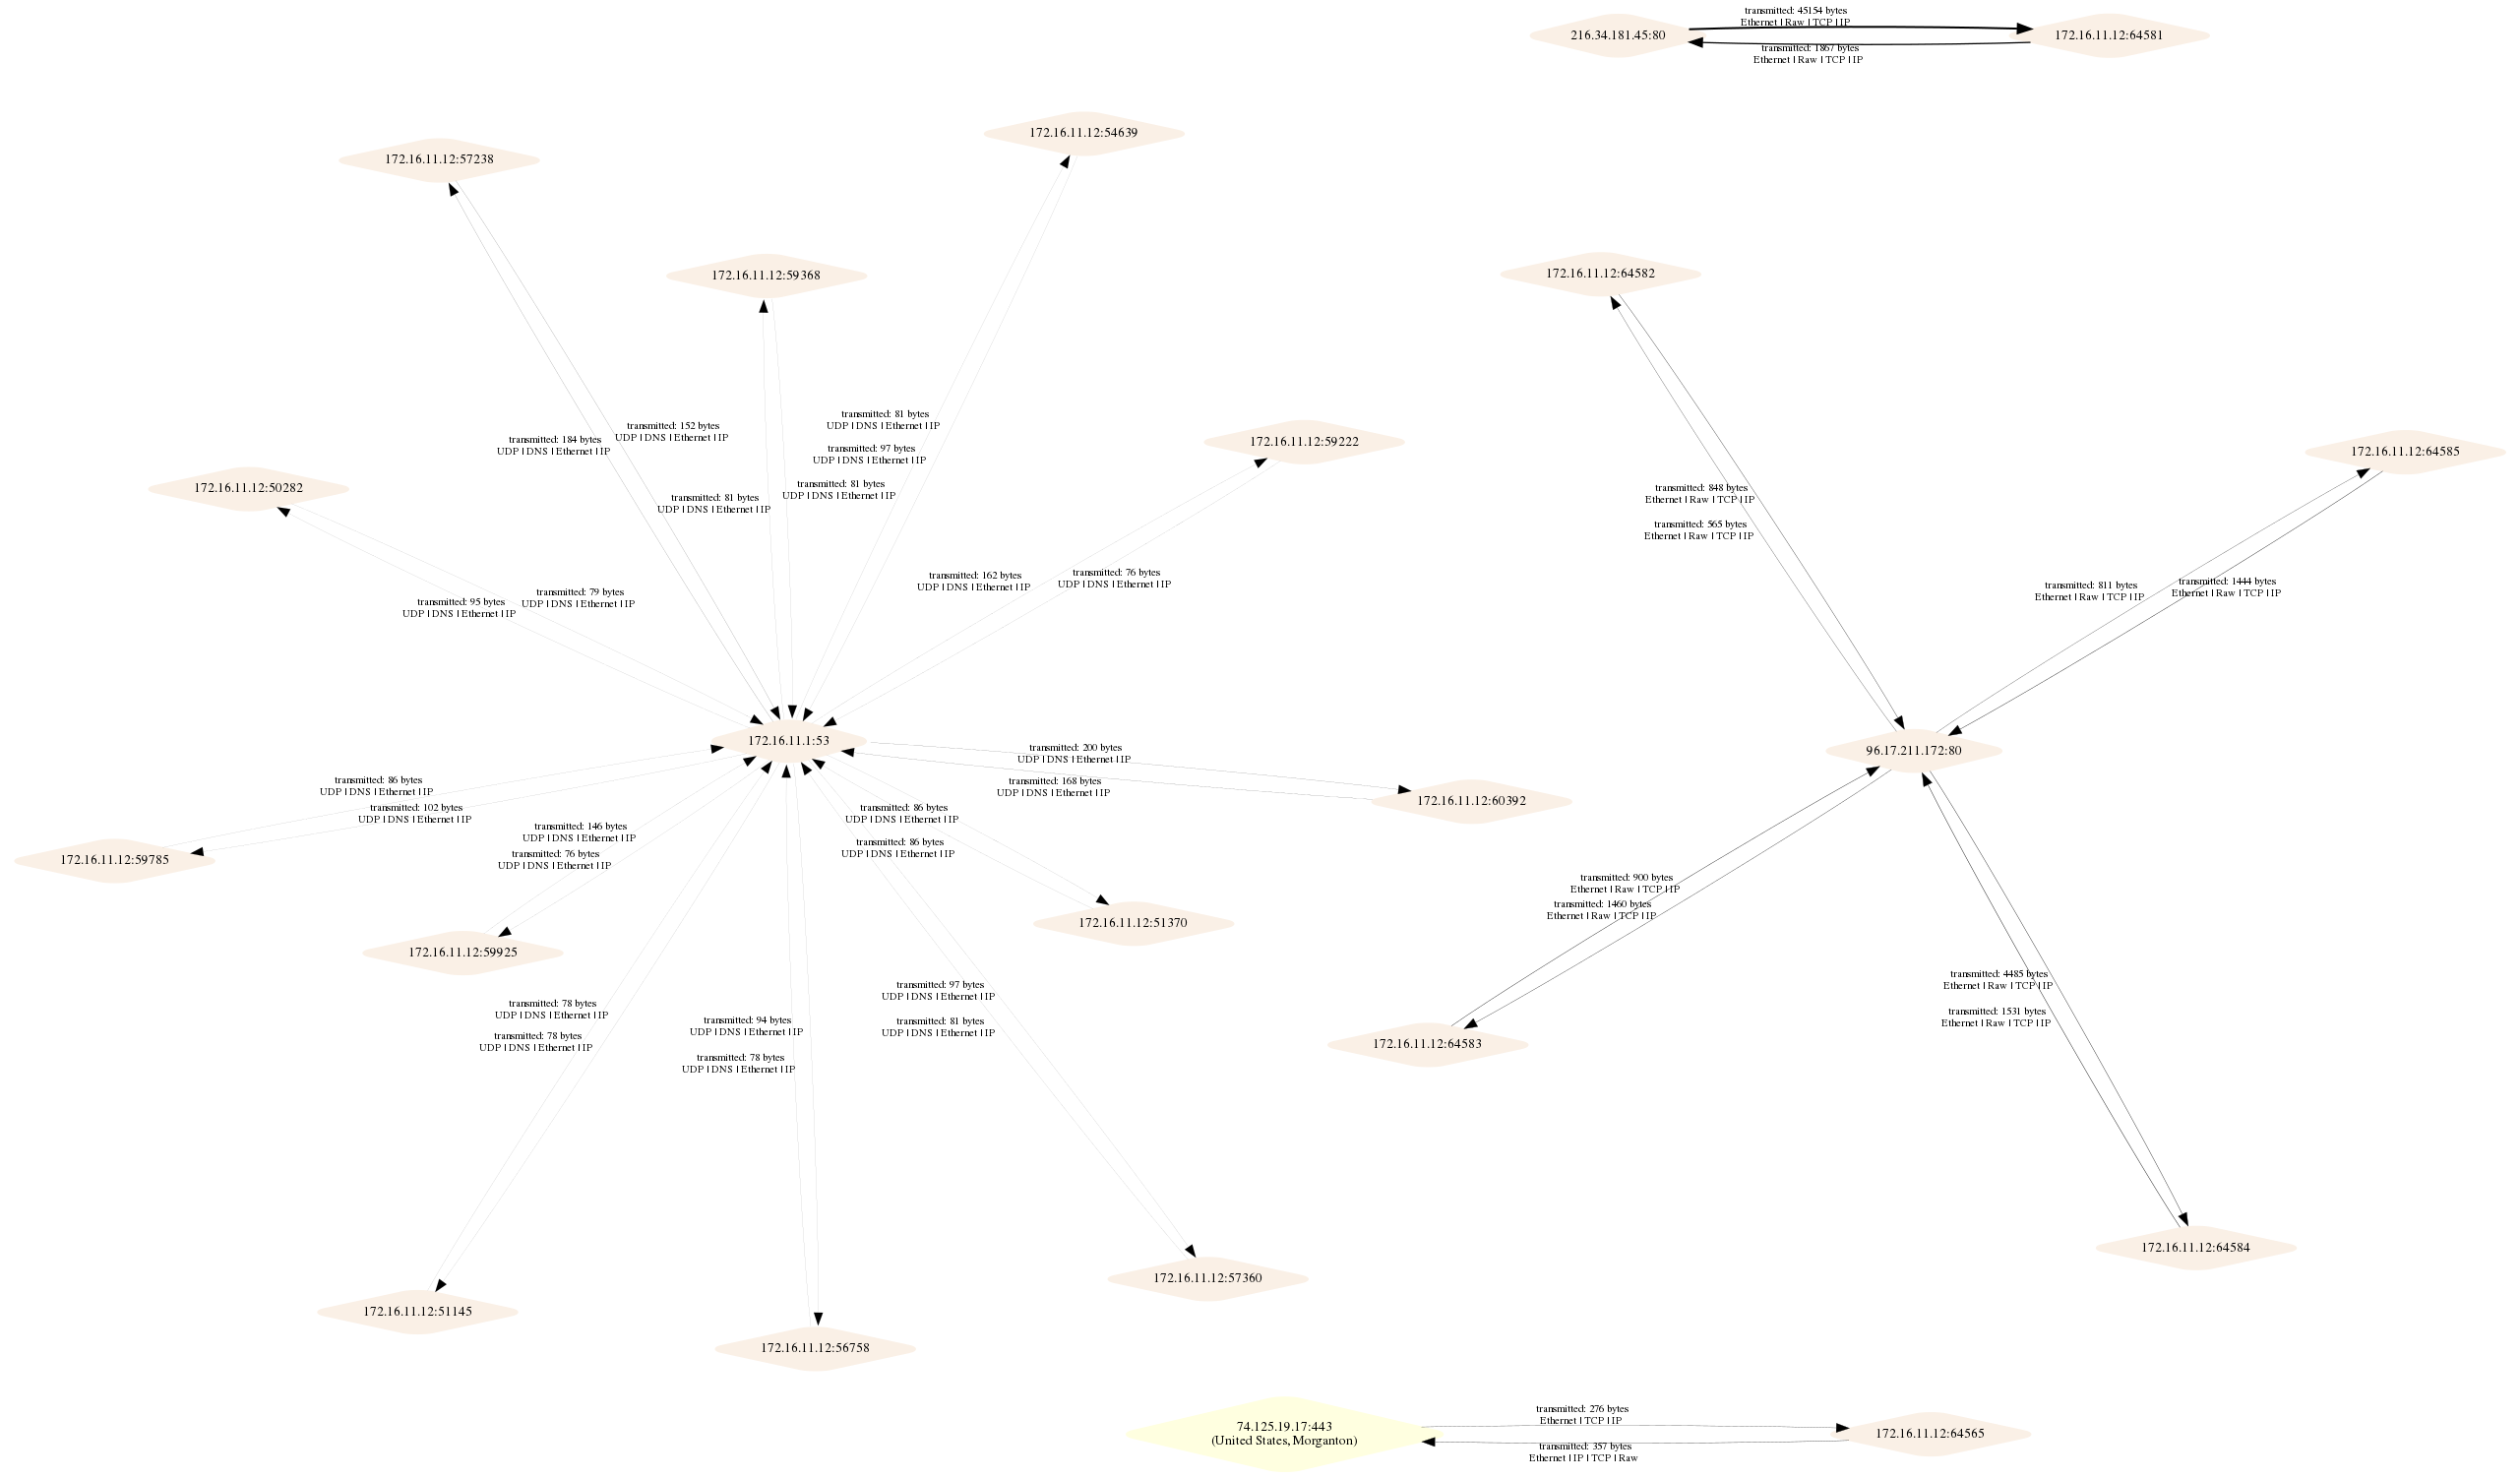 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
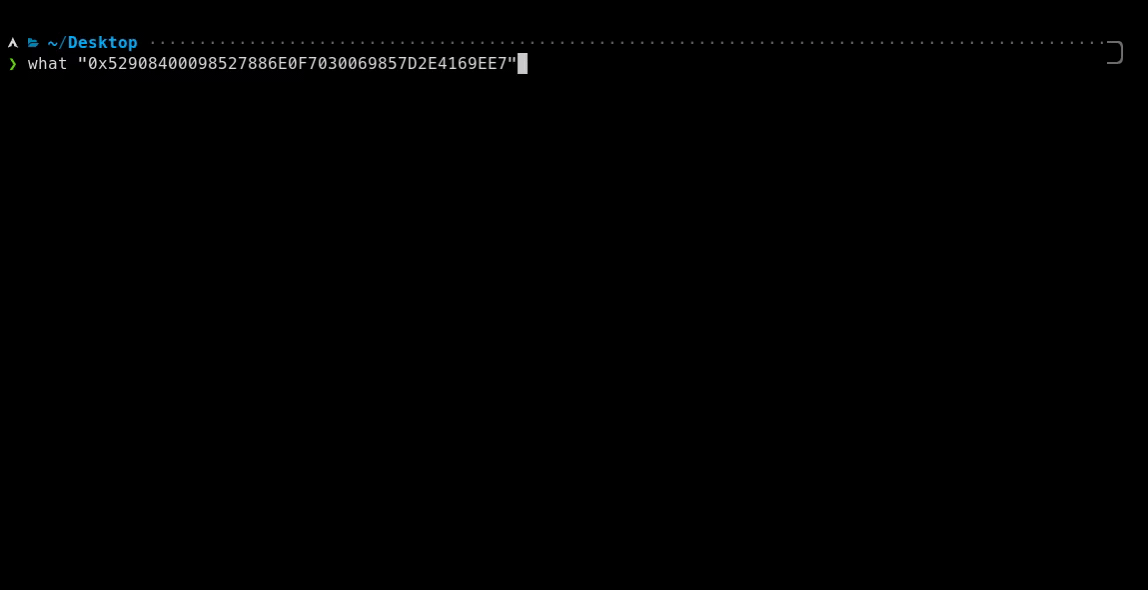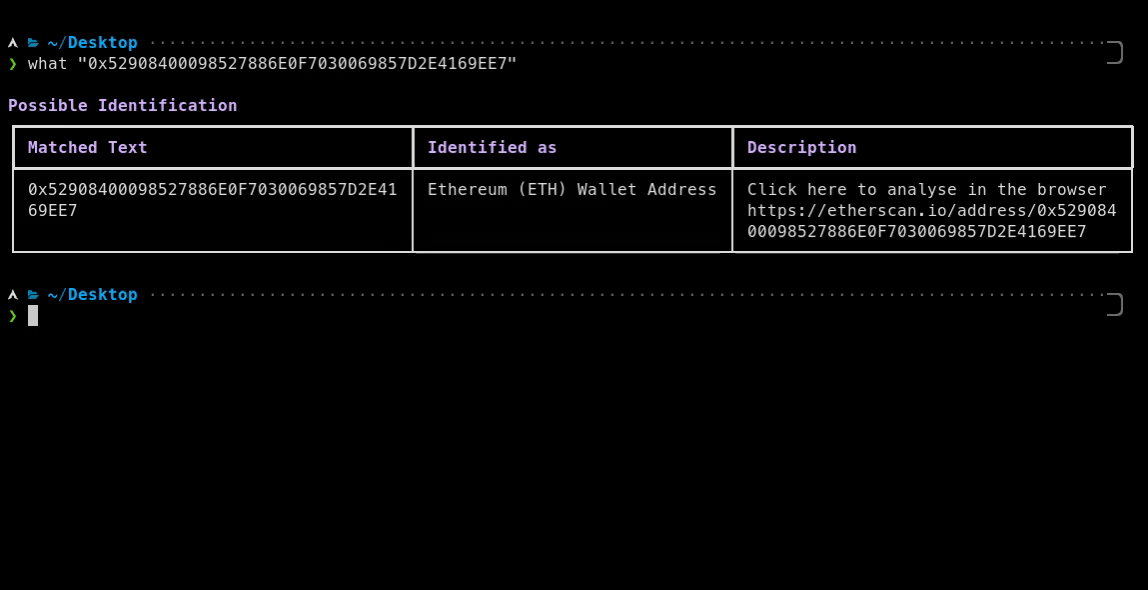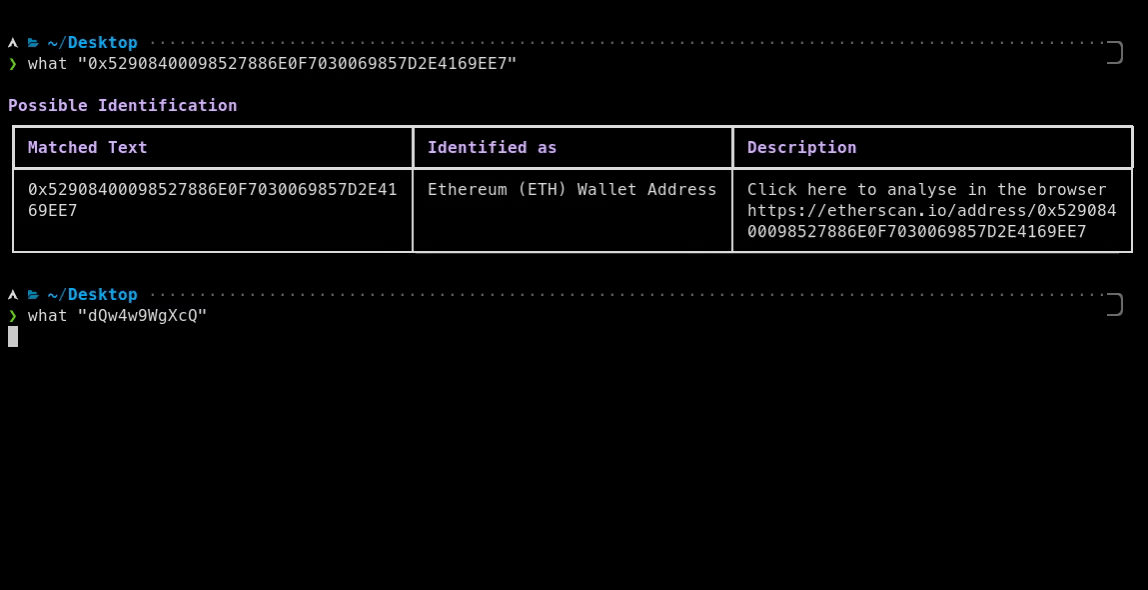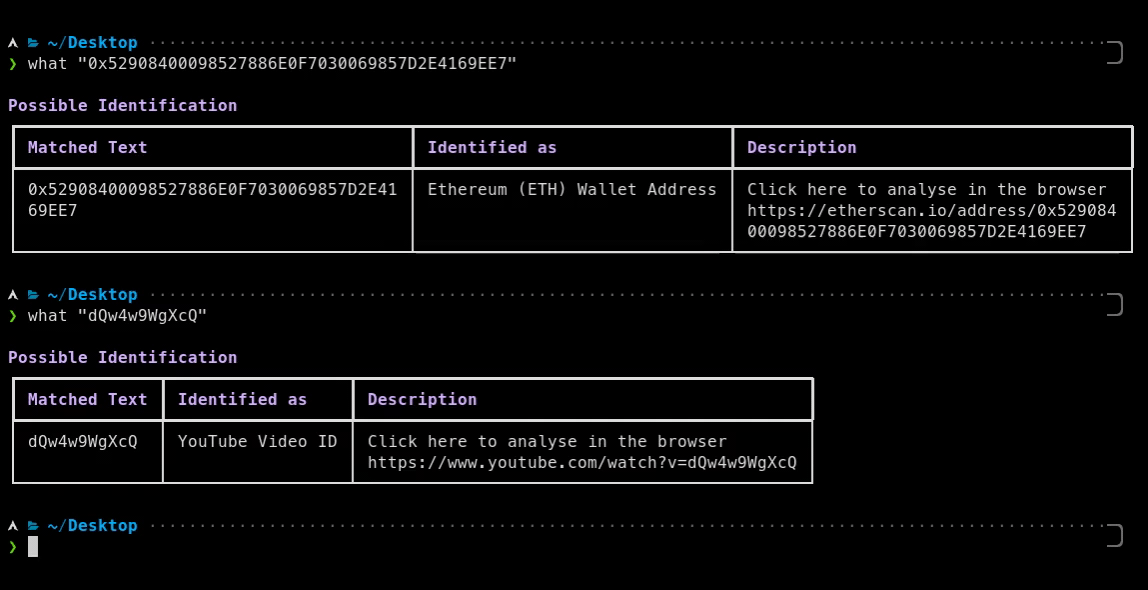 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 cyberhatcoil/acf
Android Connections Forensics
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…