

Archived
PacketStreamer
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
cloud-securitycontainer-securityforensics+6
1.9k
deepfence/packetstreamer⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
 bee-san/pywhat
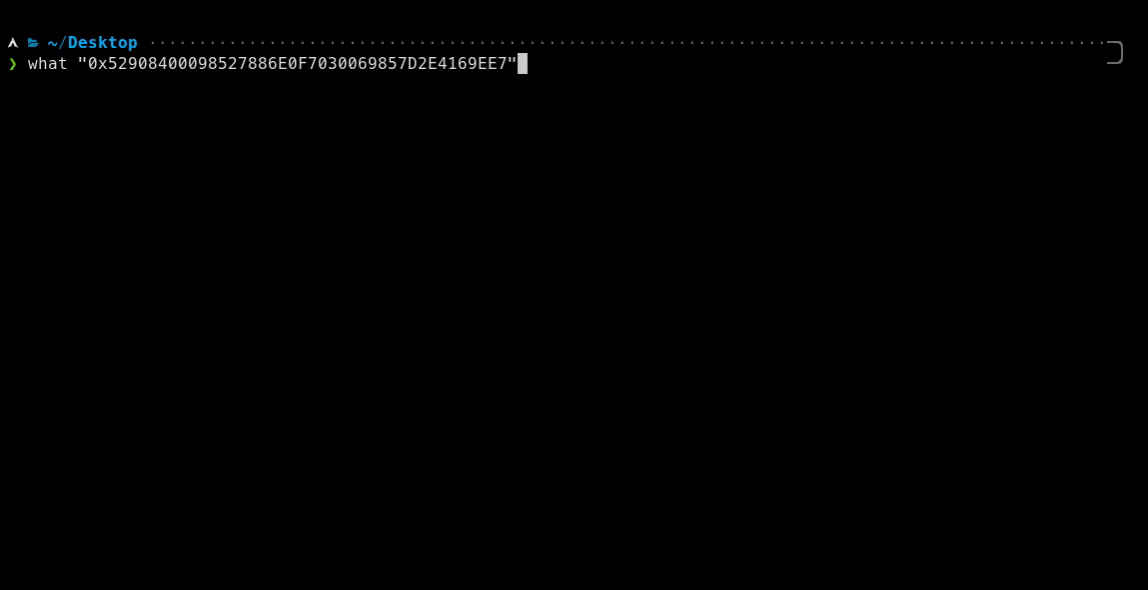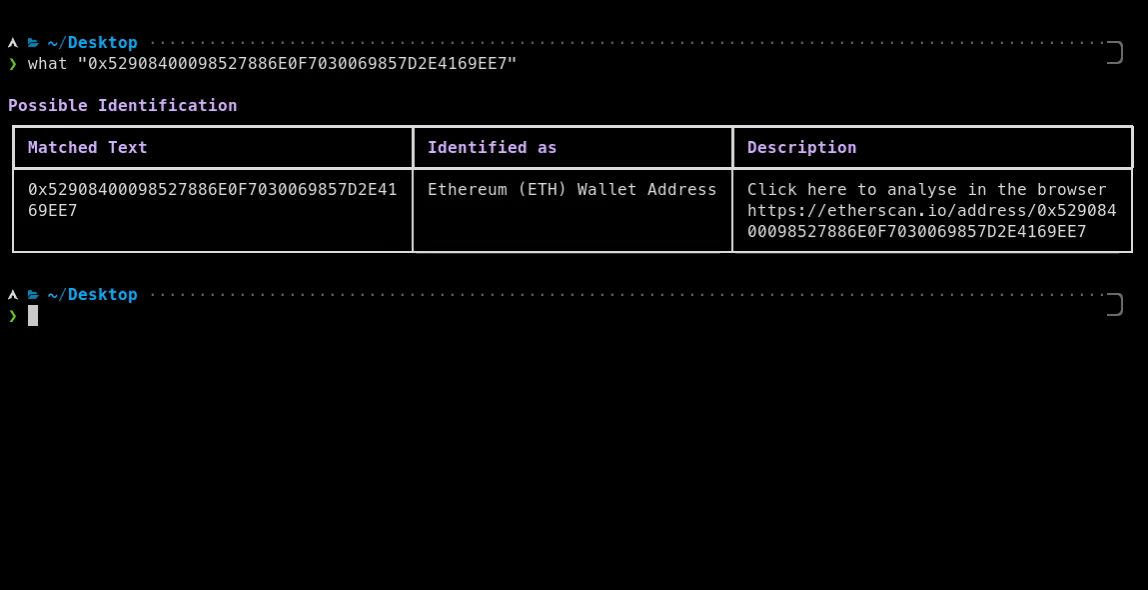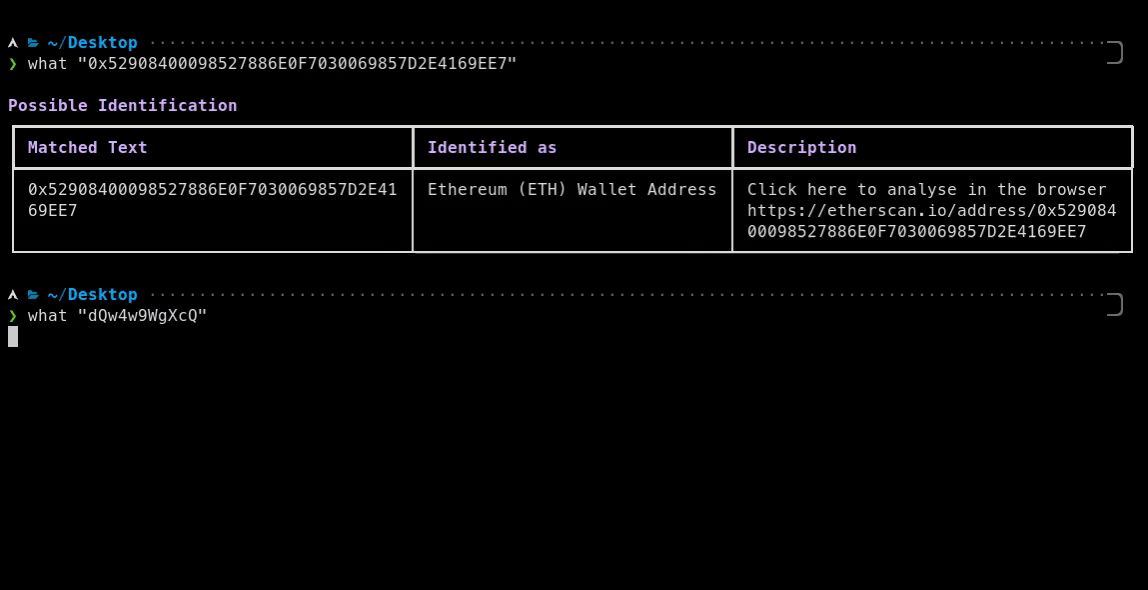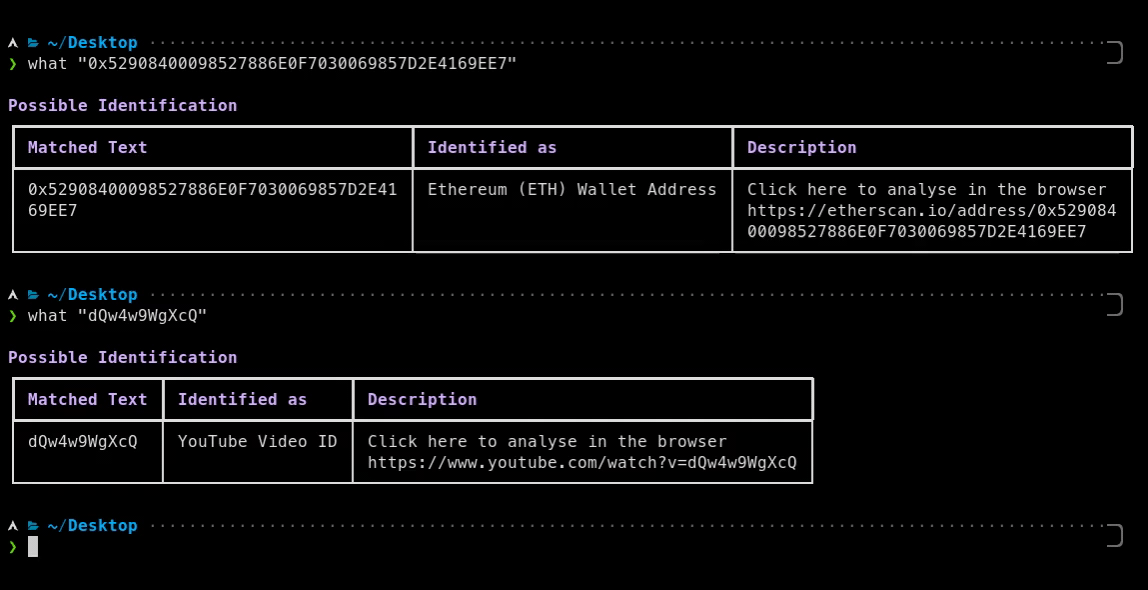
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
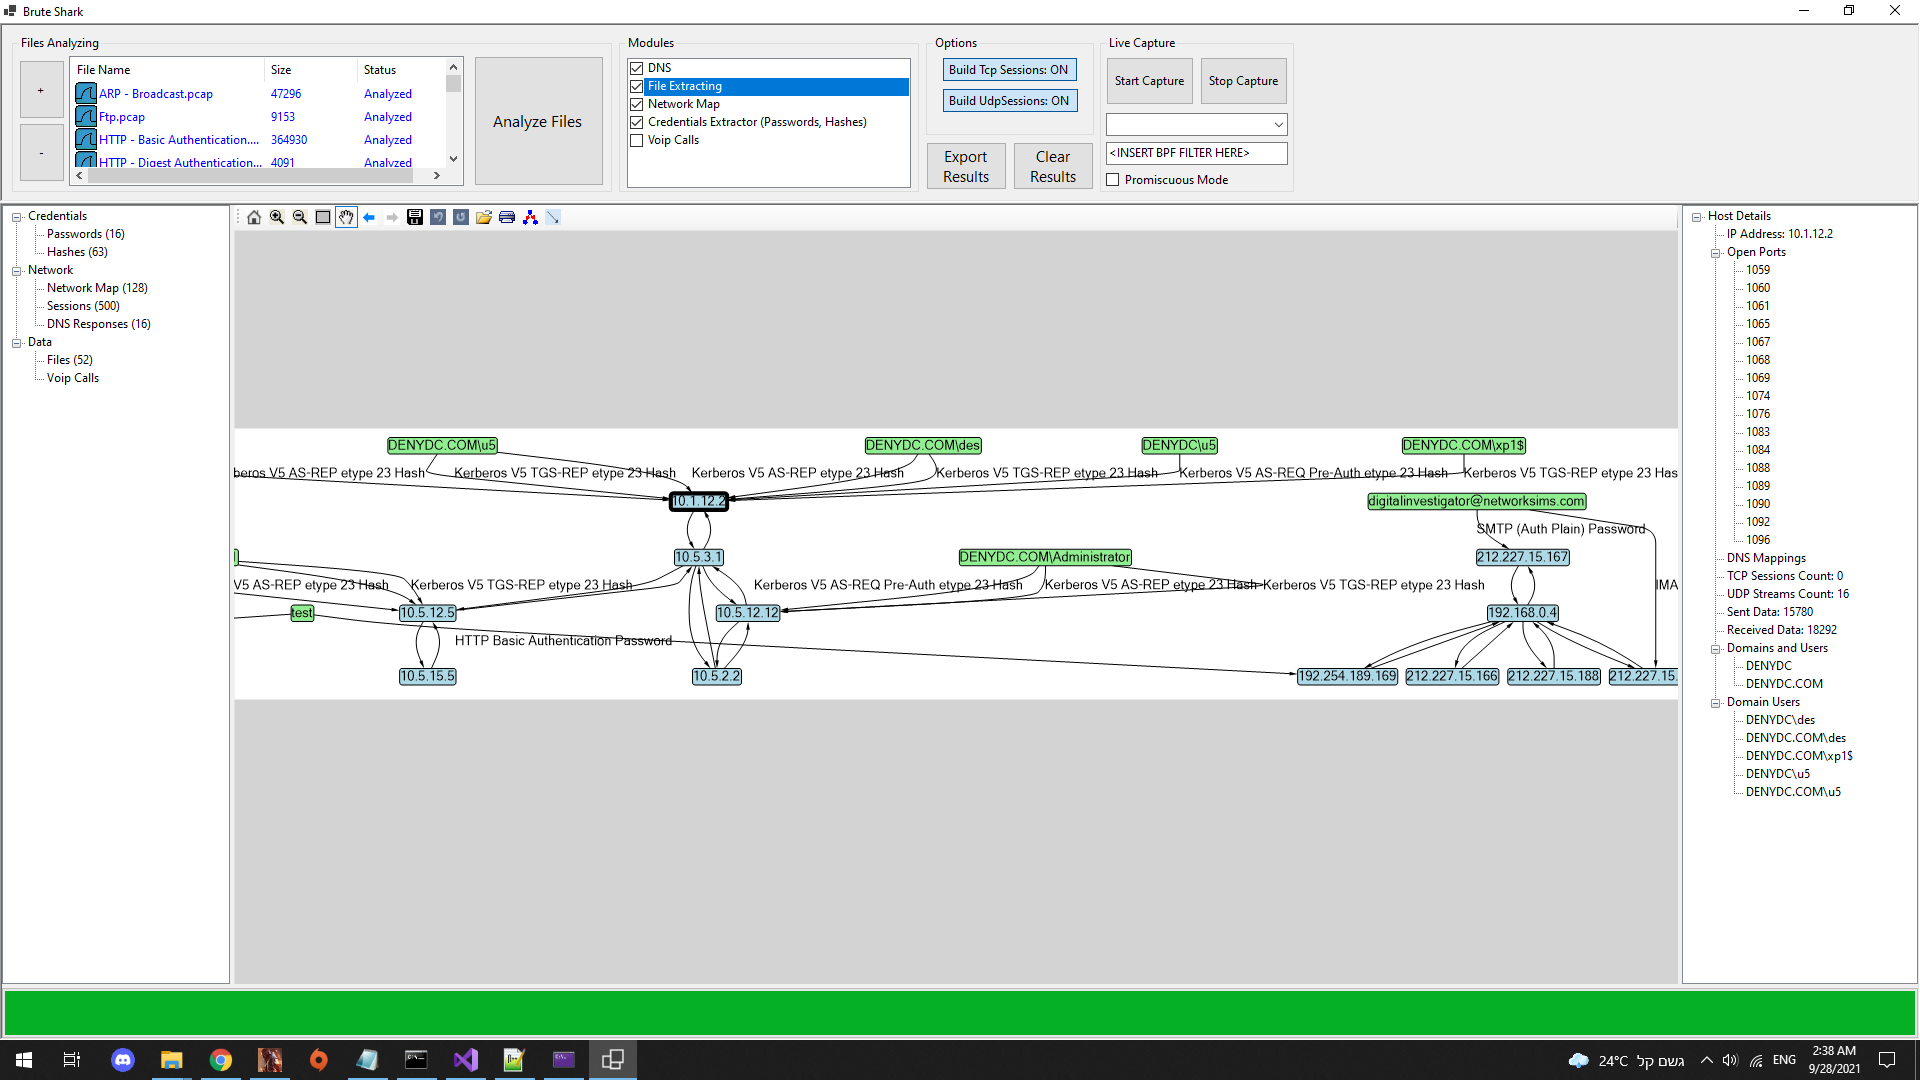
 synacktiv/pcapan
A pcap capture analysis helper
 jgoyd/fourteen_endpoints
Shell Companies Inside Apple's Privacy Relay
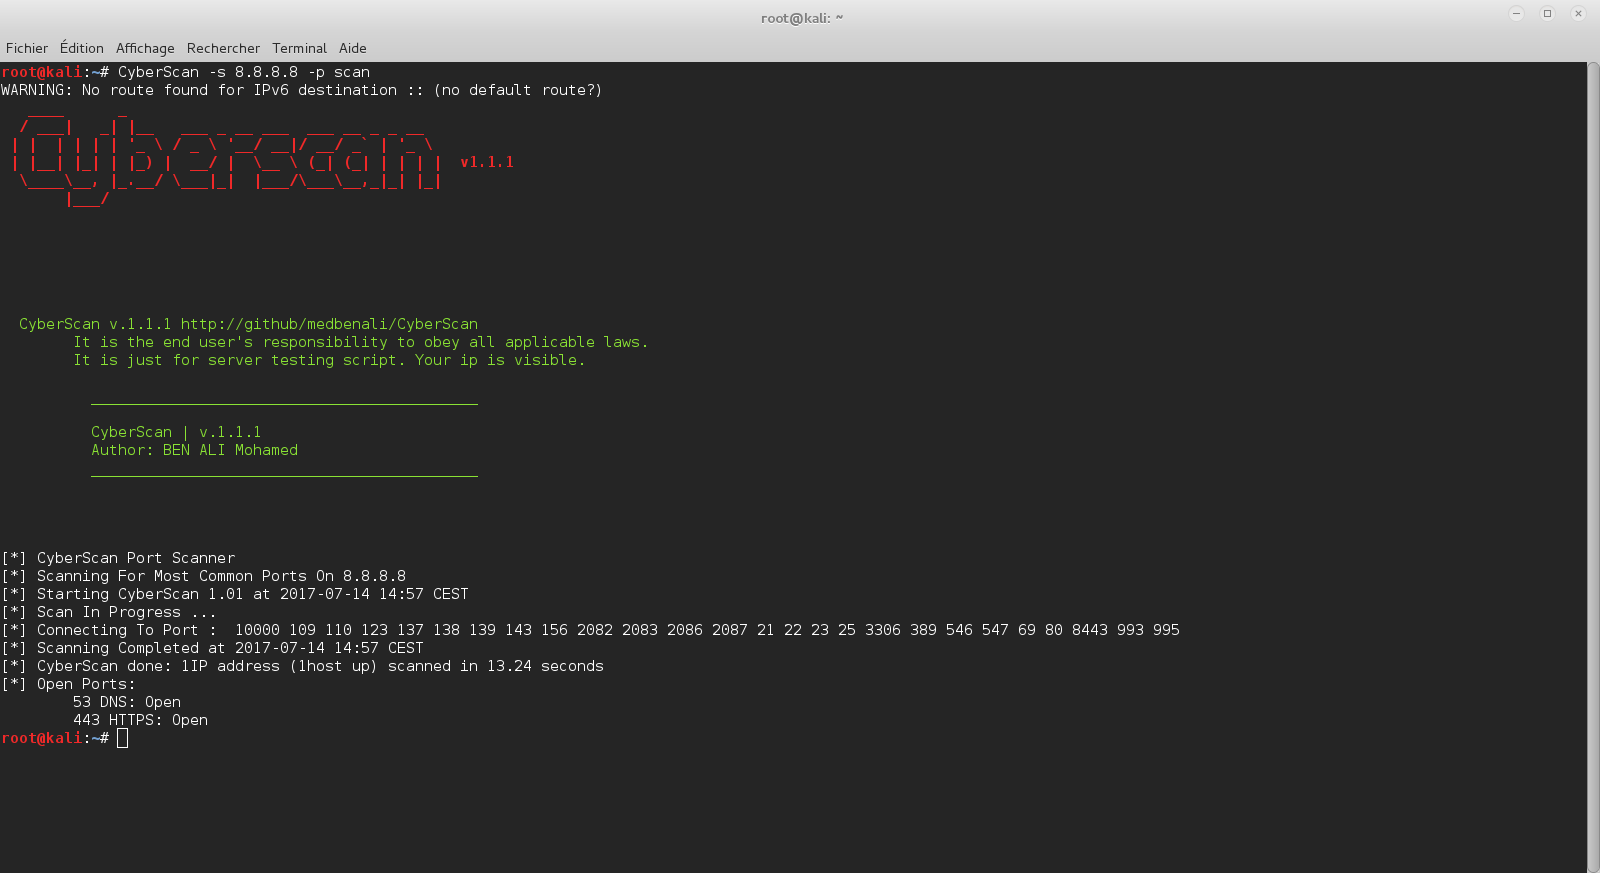 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
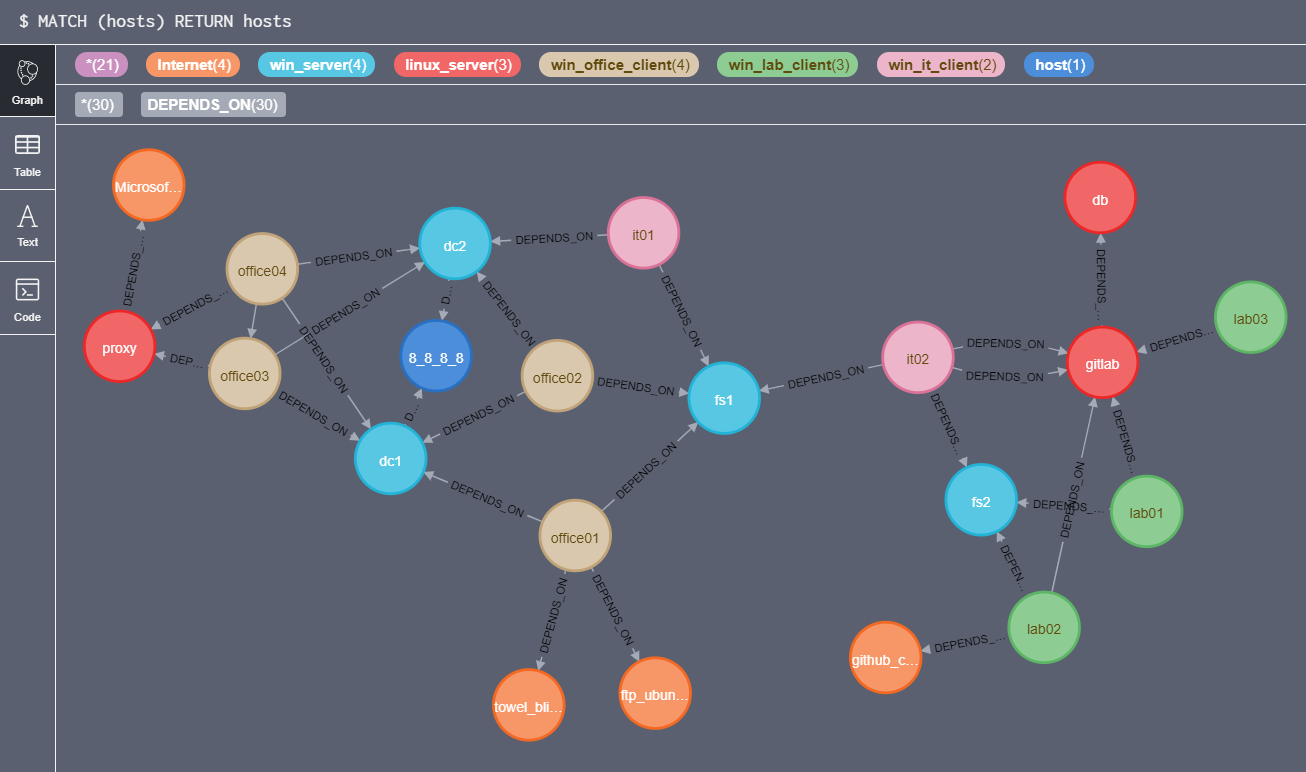 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 telefonica/hiddennetworks-python
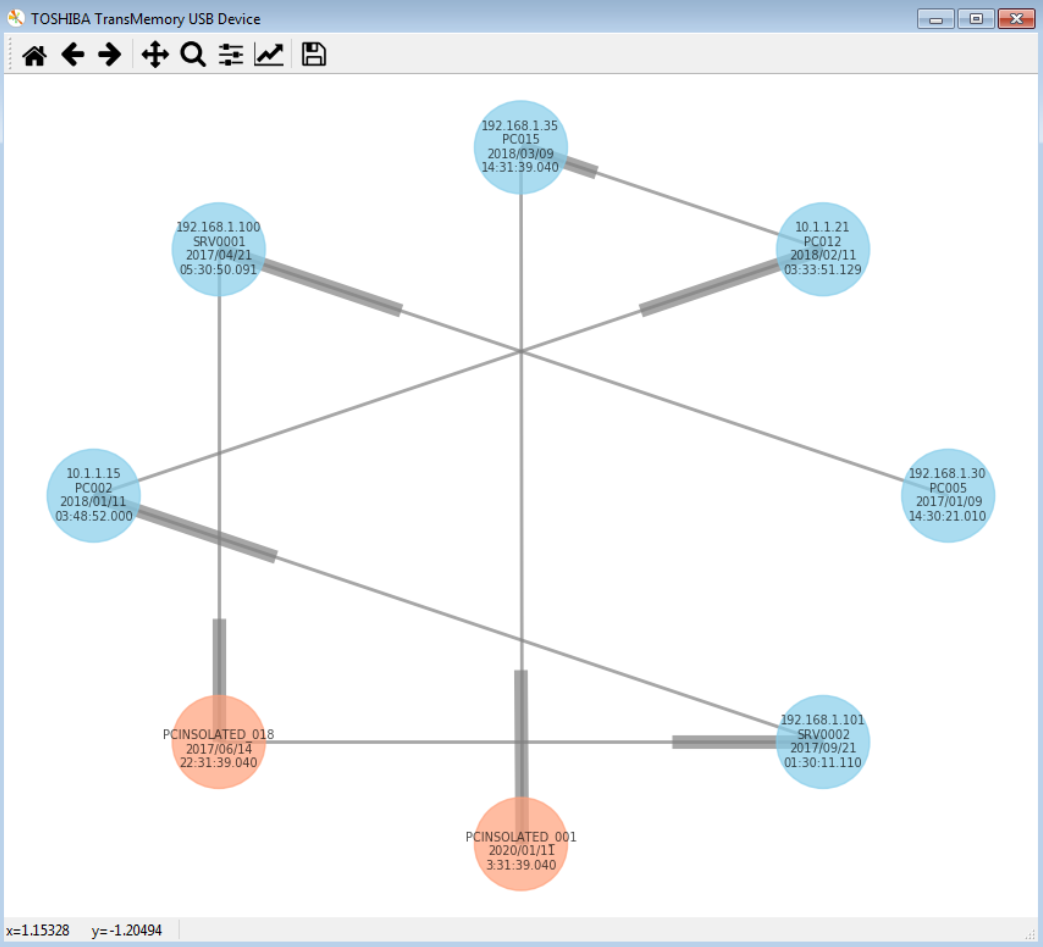
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 1ultimat3/pcapviz
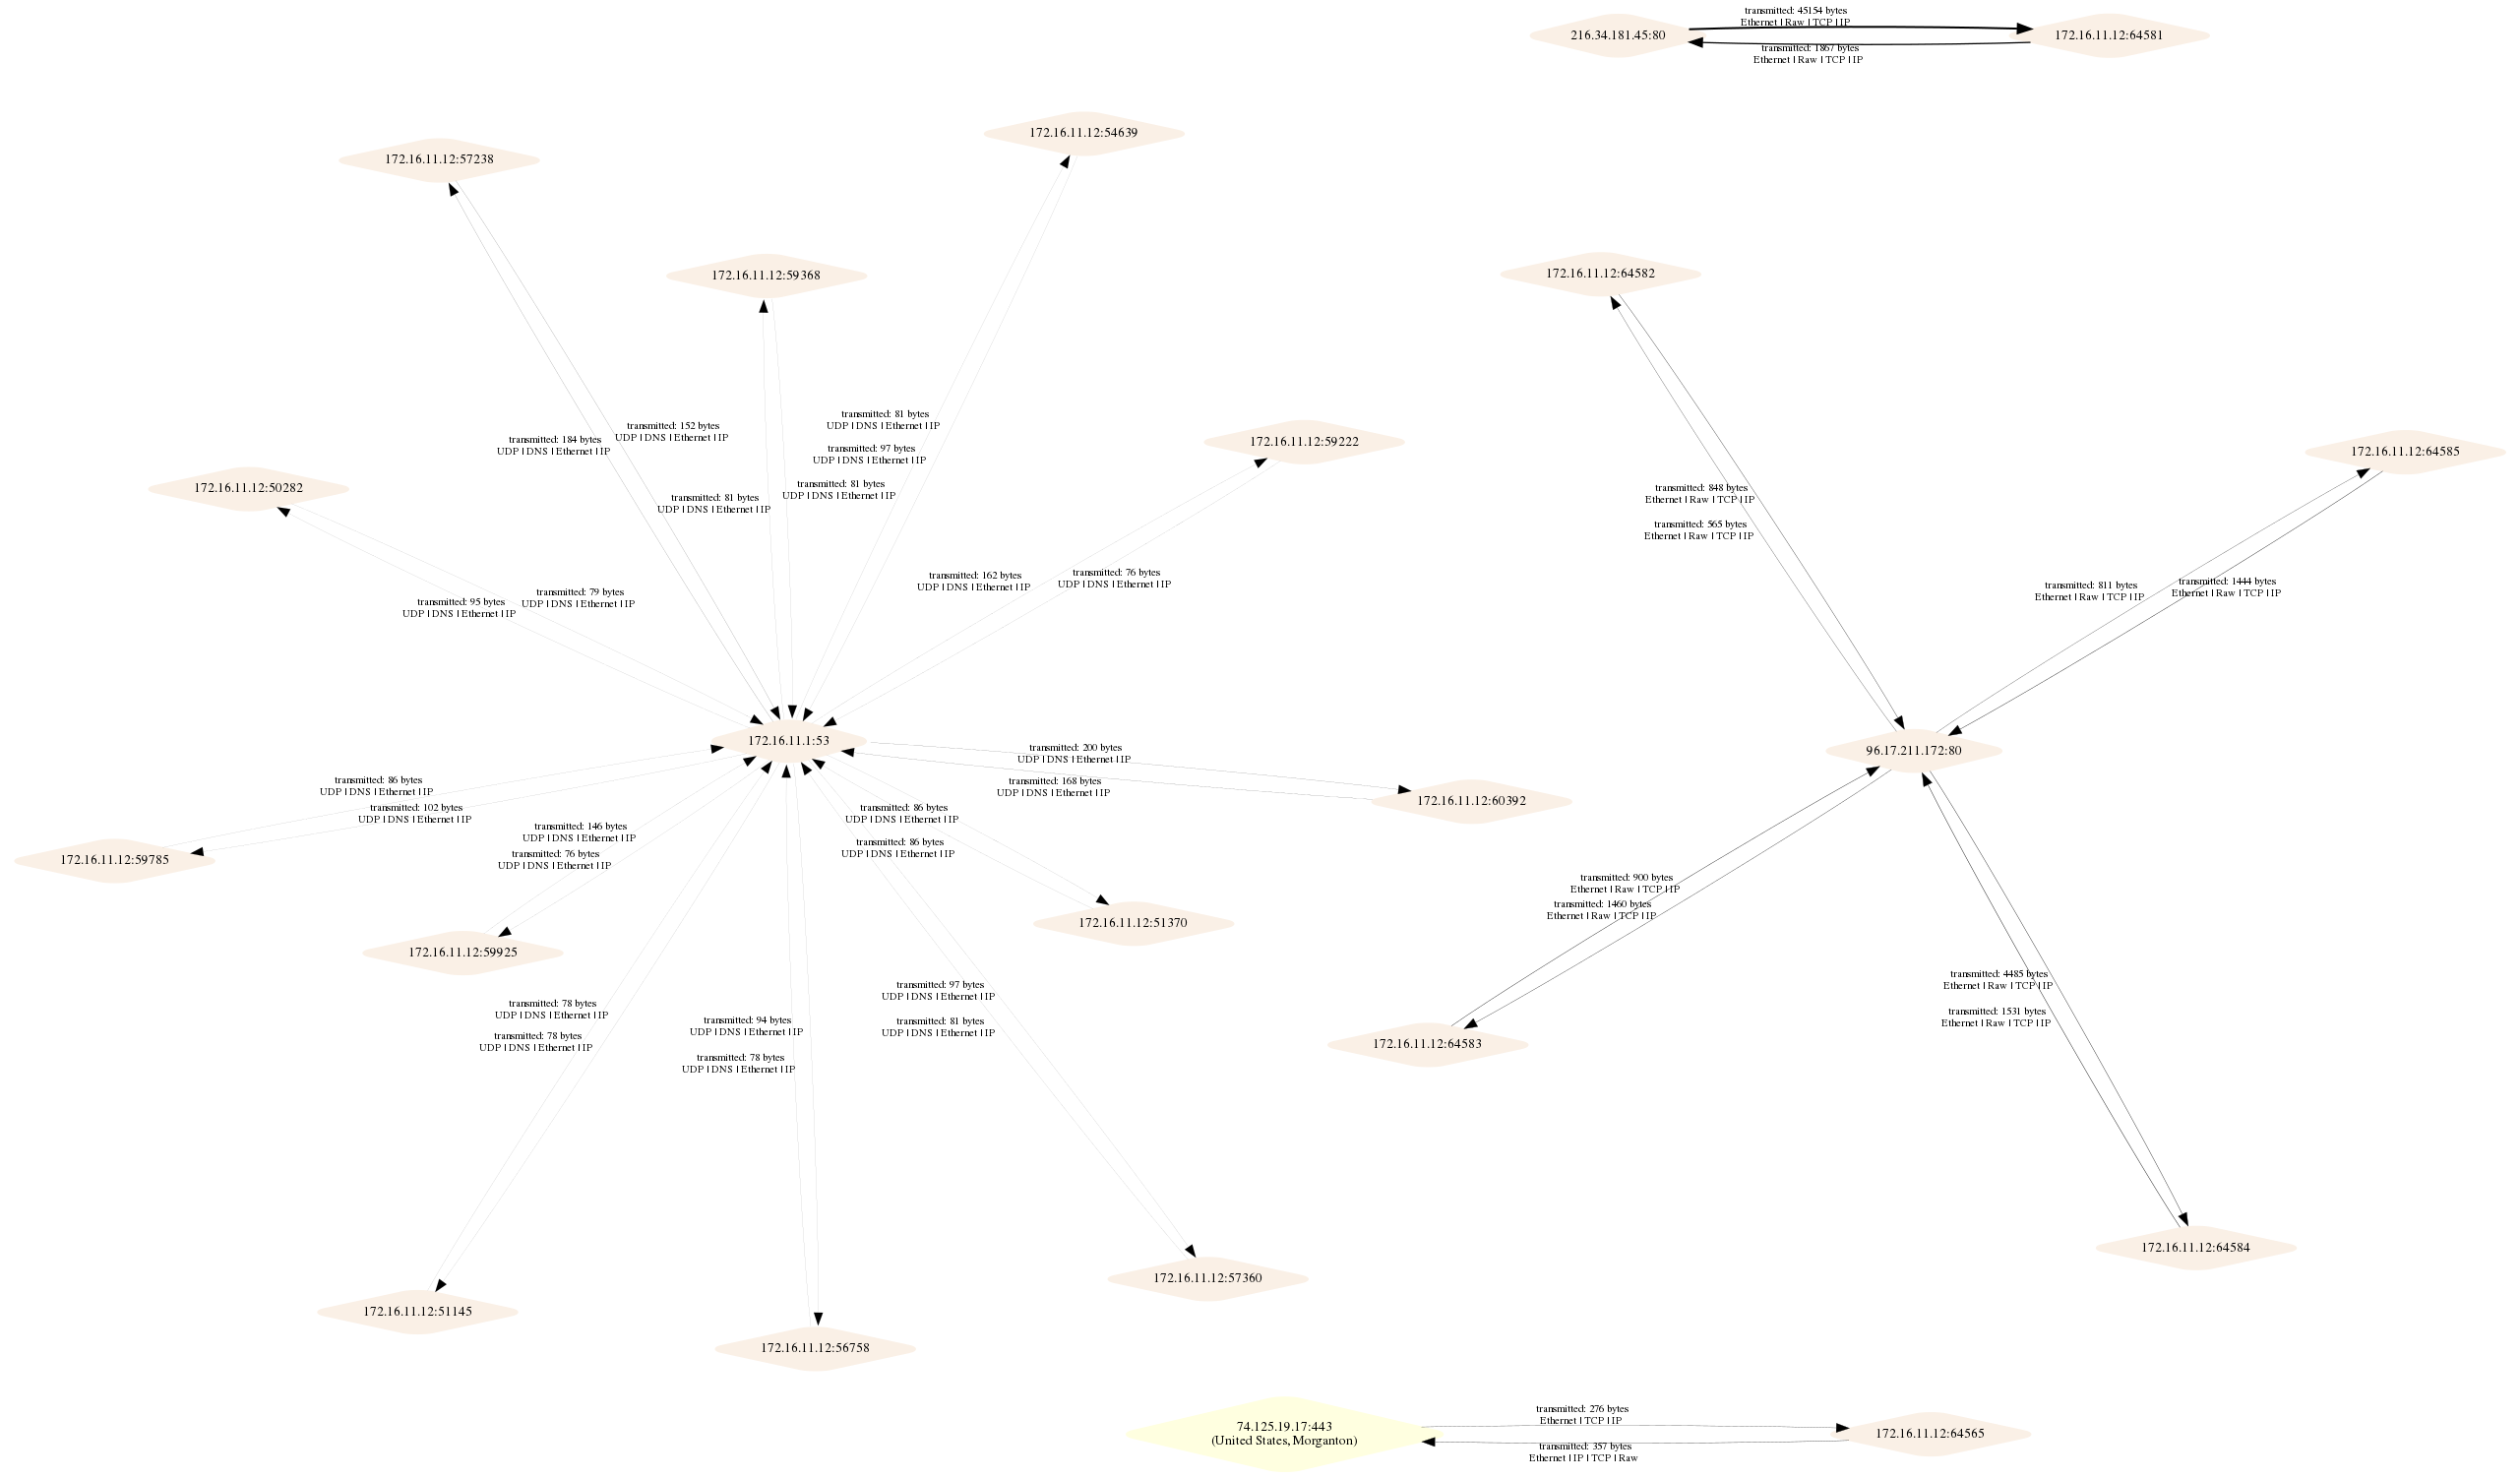
Visualize network topologies and collect graph statistics based on pcap files