

arkime
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
defensive-toolsdigital-forensicsforensics+7
arkime/arkimeArkime is an open source, large scale, full packet capturing, indexing, and database system.
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
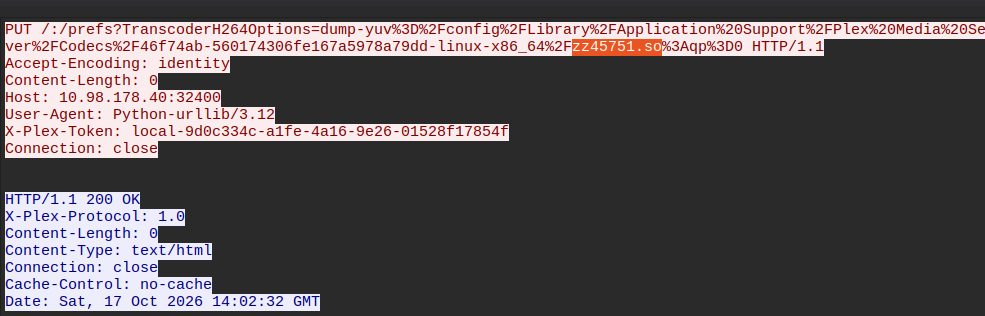 boredhackerblog/plex2shell_pcap
Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 cristianzsh/forensictools
Collection of forensic tools
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 awakecoding/wireshark-rdp
Wireshark RDP resources