

passer
 activecm/passer
Passive service locator, a python sniffer that identifies servers, clients, names and much more
defensive-toolsdns-analysisfingerprint-spoofing+6
2668 months ago
activecm/passerPassive service locator, a python sniffer that identifies servers, clients, names and much more
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
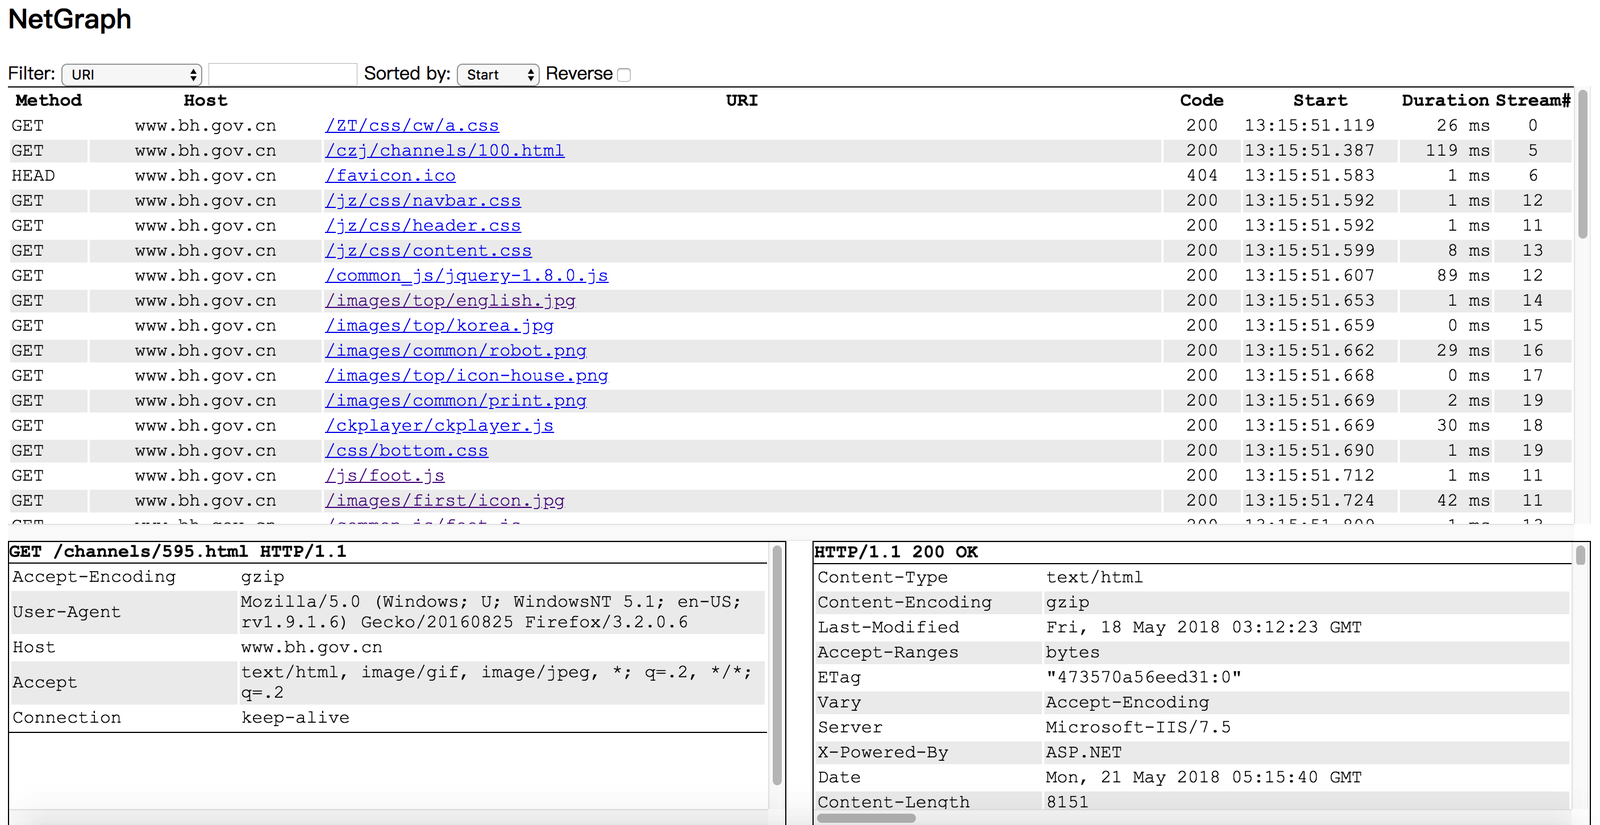 ga0/netgraph
A cross platform http sniffer with a web UI
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
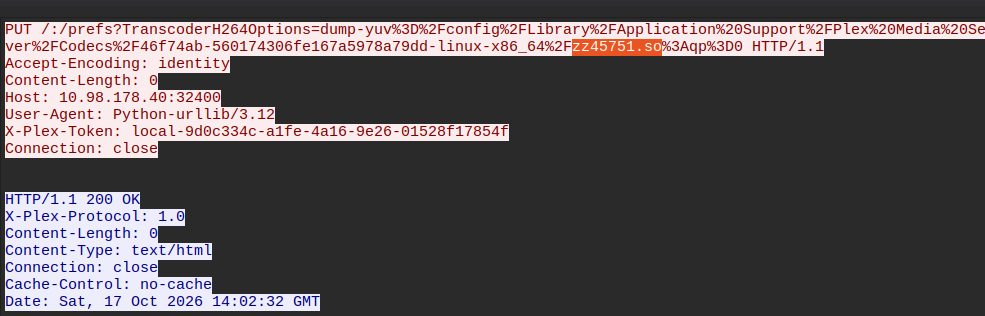 boredhackerblog/plex2shell_pcap
Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 google/gopacket
Provides packet processing capabilities for Go
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
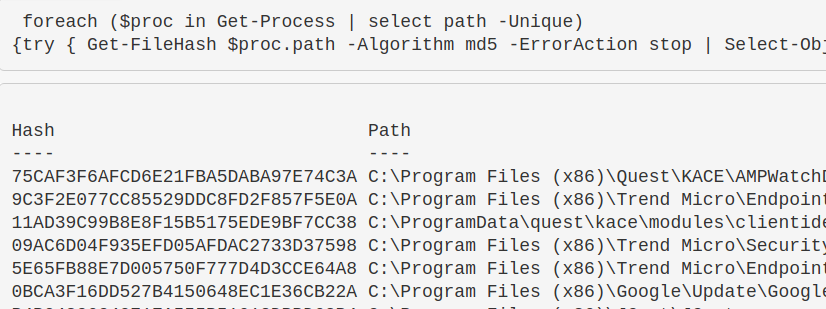 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 awakecoding/wireshark-rdp
Wireshark RDP resources
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…