
SOC335-CVE-2024-49138-Exploitation-Detected
 mohamedbrek/soc335-cve-2024-49138-exploitation-detected
LetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.
digital-forensicseducationincident-response+6
mohamedbrek/soc335-cve-2024-49138-exploitation-detectedLetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
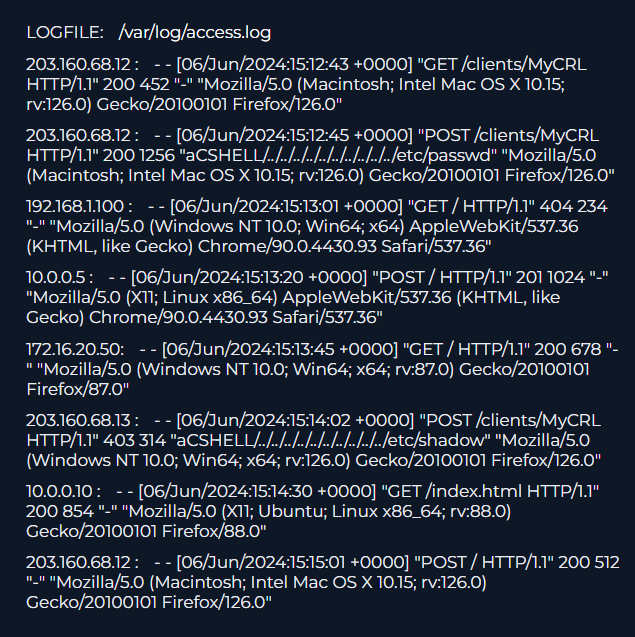 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 corelight/zeek-spicy-wireguard
A Zeek Wireguard protocol analyzer based on Spicy.
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 gilberto47831/network-filesystem-forensics
Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…