Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

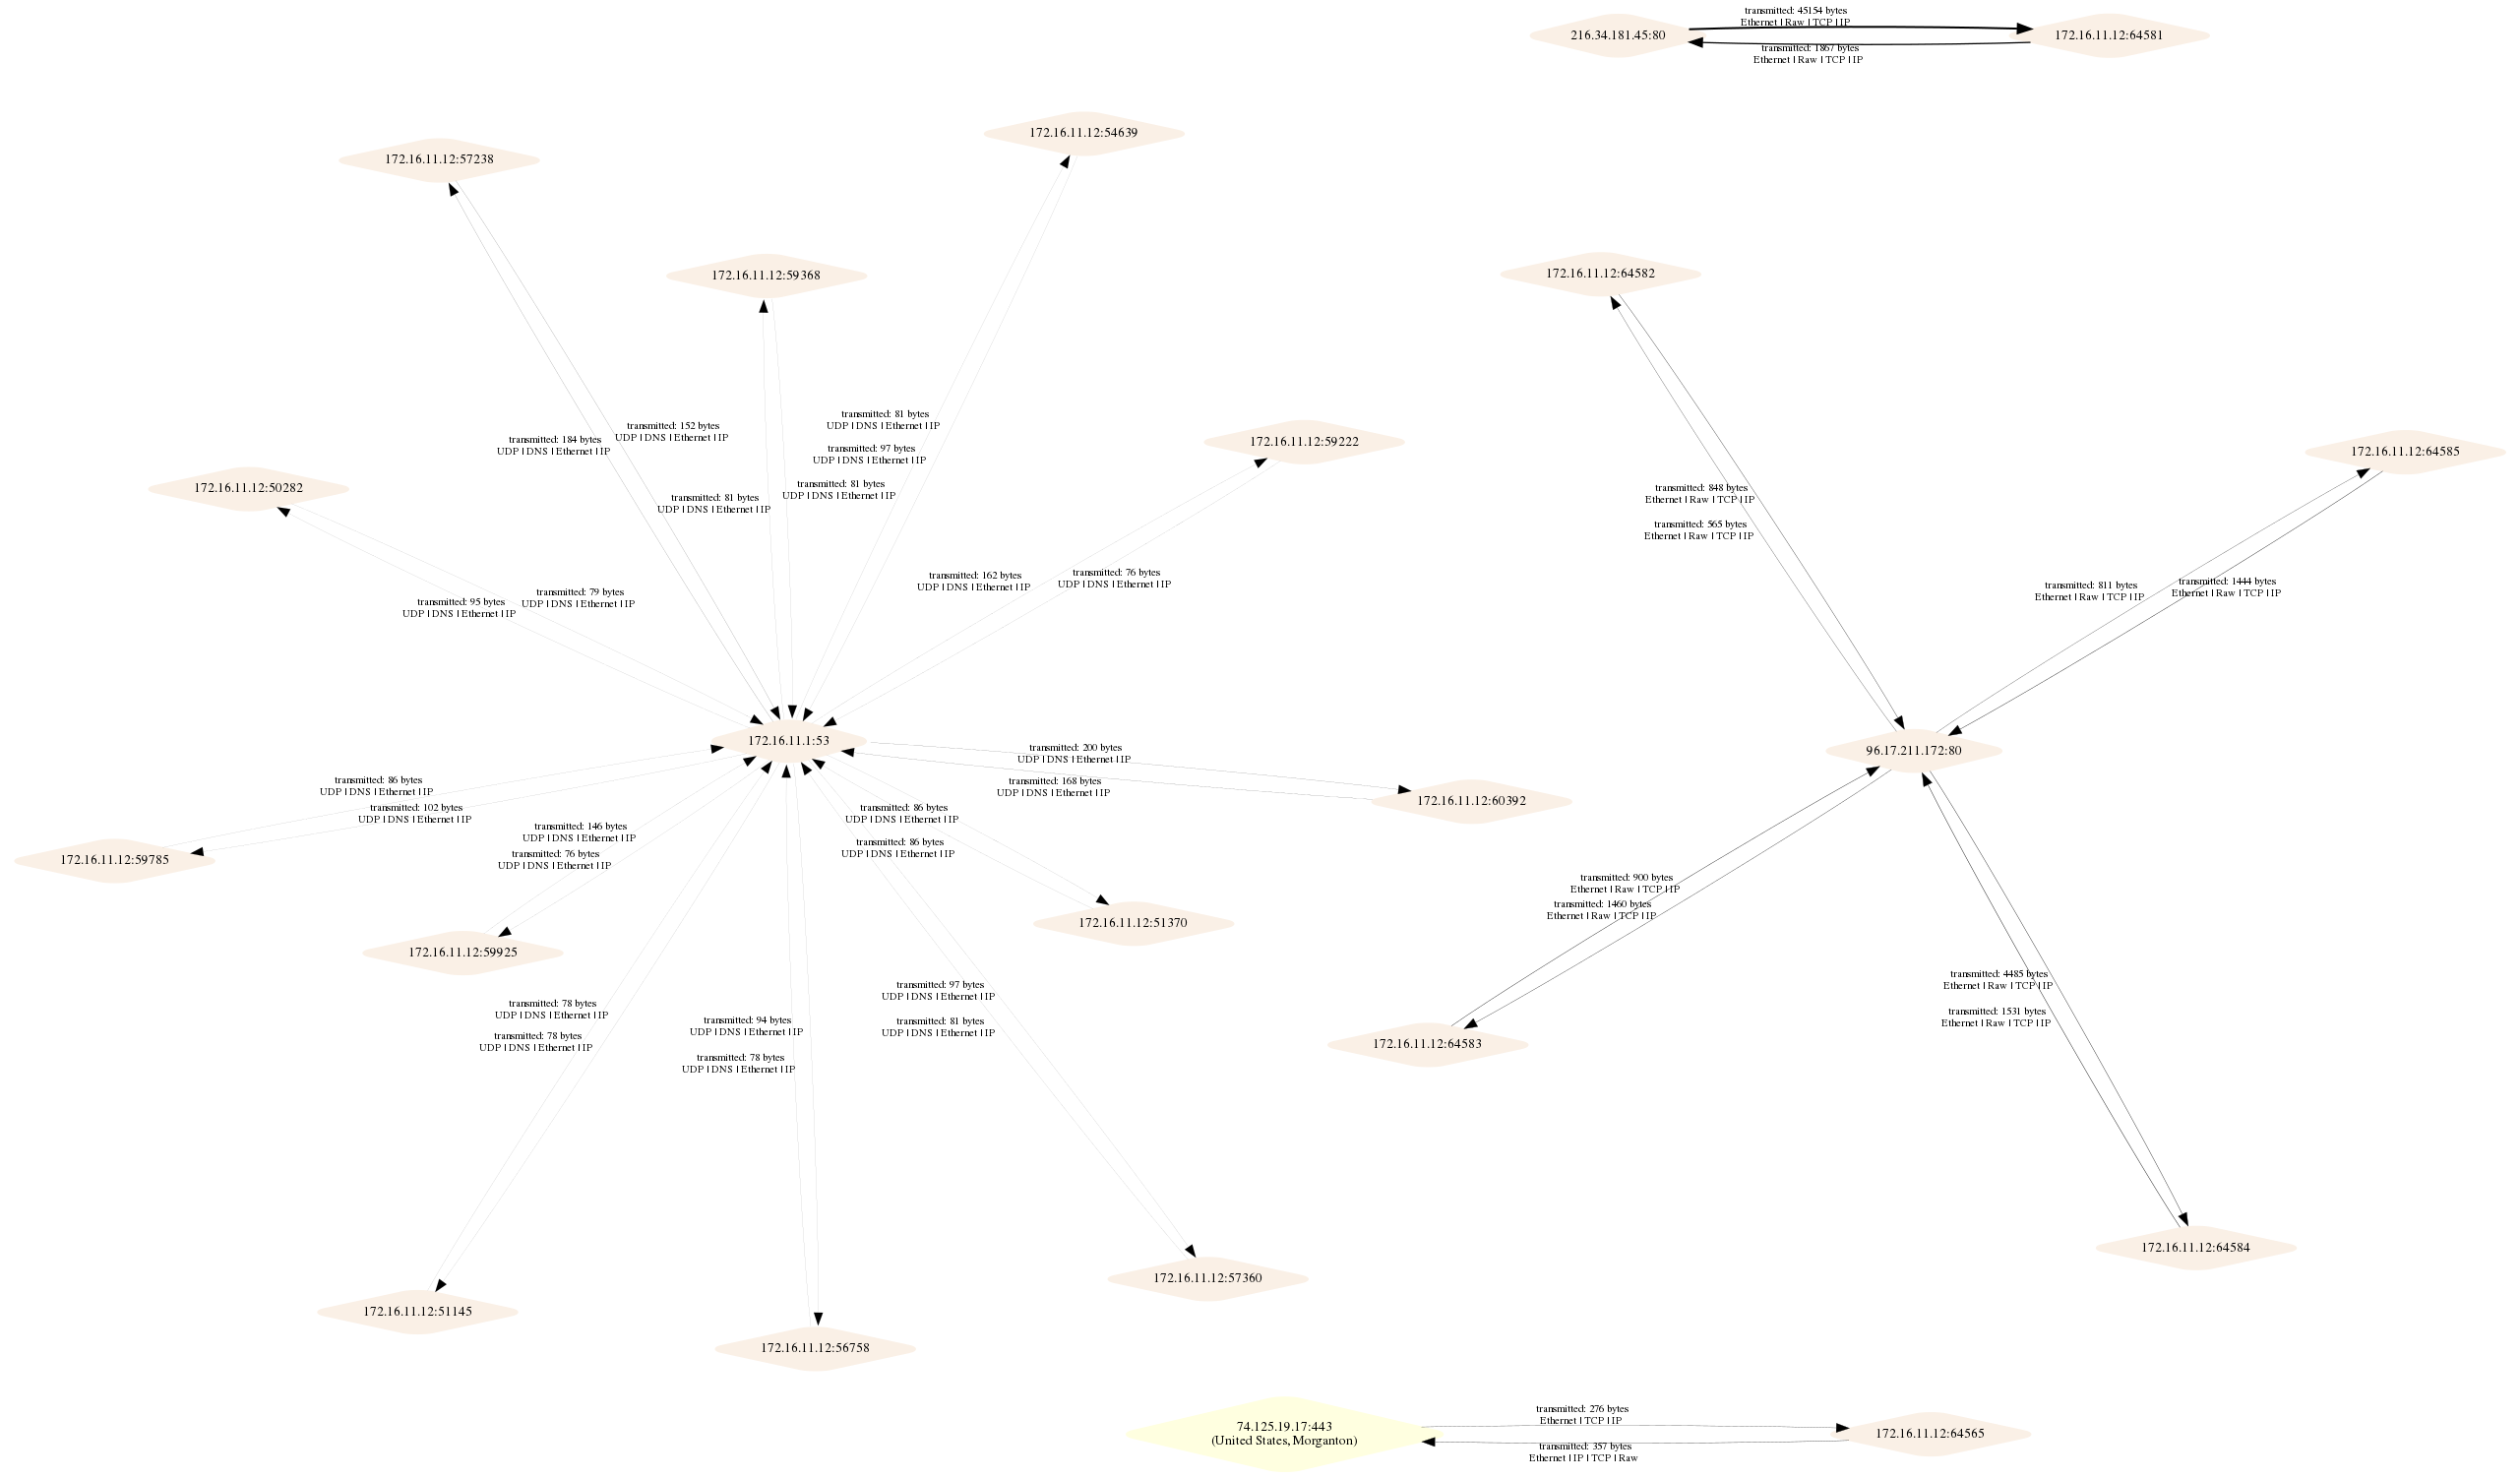
Visualize network topologies and collect graph statistics based on pcap files

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

Selective protocol extractor from PCAPs or interfaces

The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark

All-in-One malware analysis tool.

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

A Zeek STUN protocol analyzer based on Spicy.

A Zeek IPSec protocol analyzer based on Spicy.

Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)

Powershell module for VMWare vSphere forensics

OpenFPC, Open Source Full Packet Capture

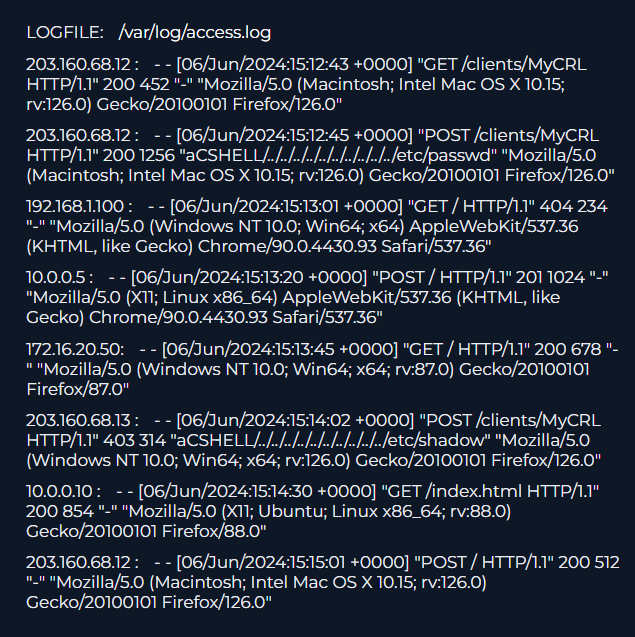
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

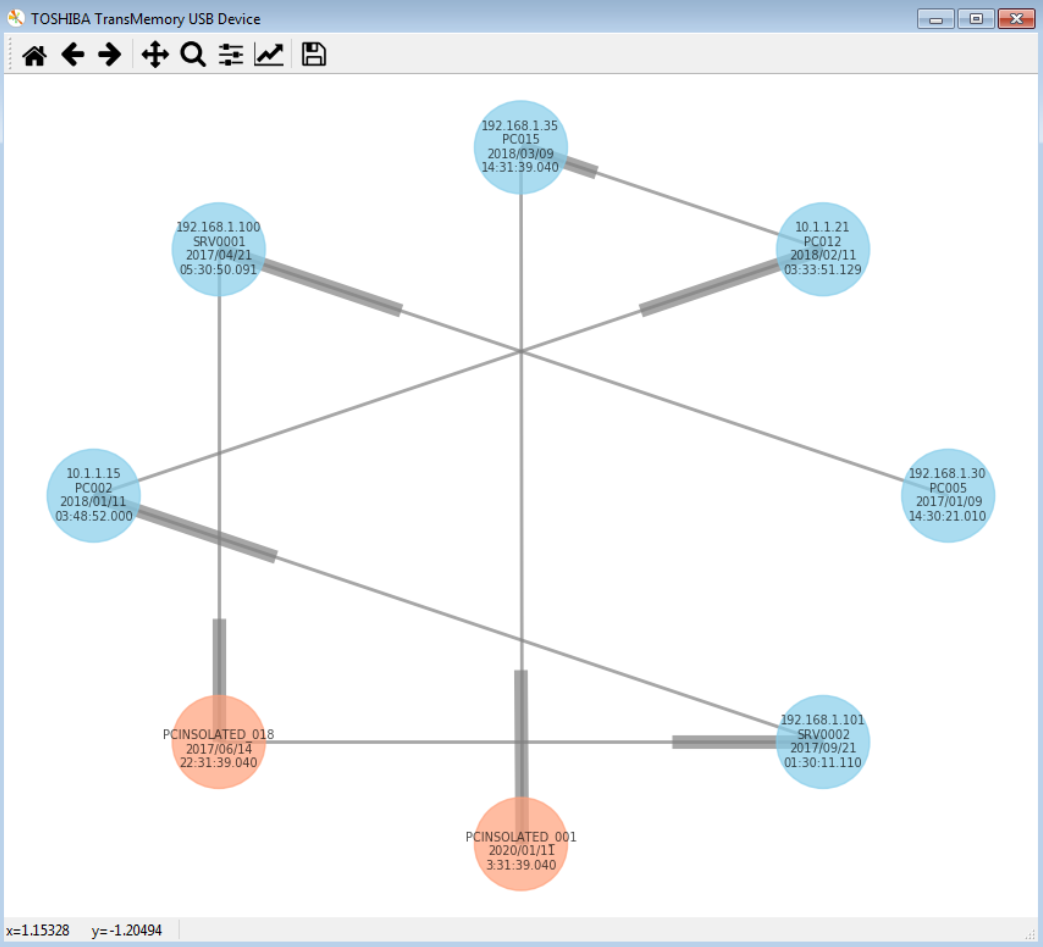
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…

Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…

A Zeek OSPF packet analyzer based on Spicy.