

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

anomaly-detectionanti-botdefensive-tools+14
7.8k19h 56m ago
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k1 day ago
Android-Projector-C2-Malware preview

Android-Projector-C2-Malware

GitHubkavan00/android-projector-c2-malware

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
android-securitycommand-and-controldigital-forensics+9
181 month ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
5.1k1 month ago
BruteShark preview

BruteShark

GitHubodedshimon/bruteshark

Network Analysis Tool

dns-analysisforensicshash-analysis+4
3.4k5 years ago
joy preview

joy

GitHubcisco/joy

A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
anomaly-detectiondigital-forensicsdns-analysis+7
1.4k6 years ago
fatt preview

fatt

GitHub0x4d31/fatt

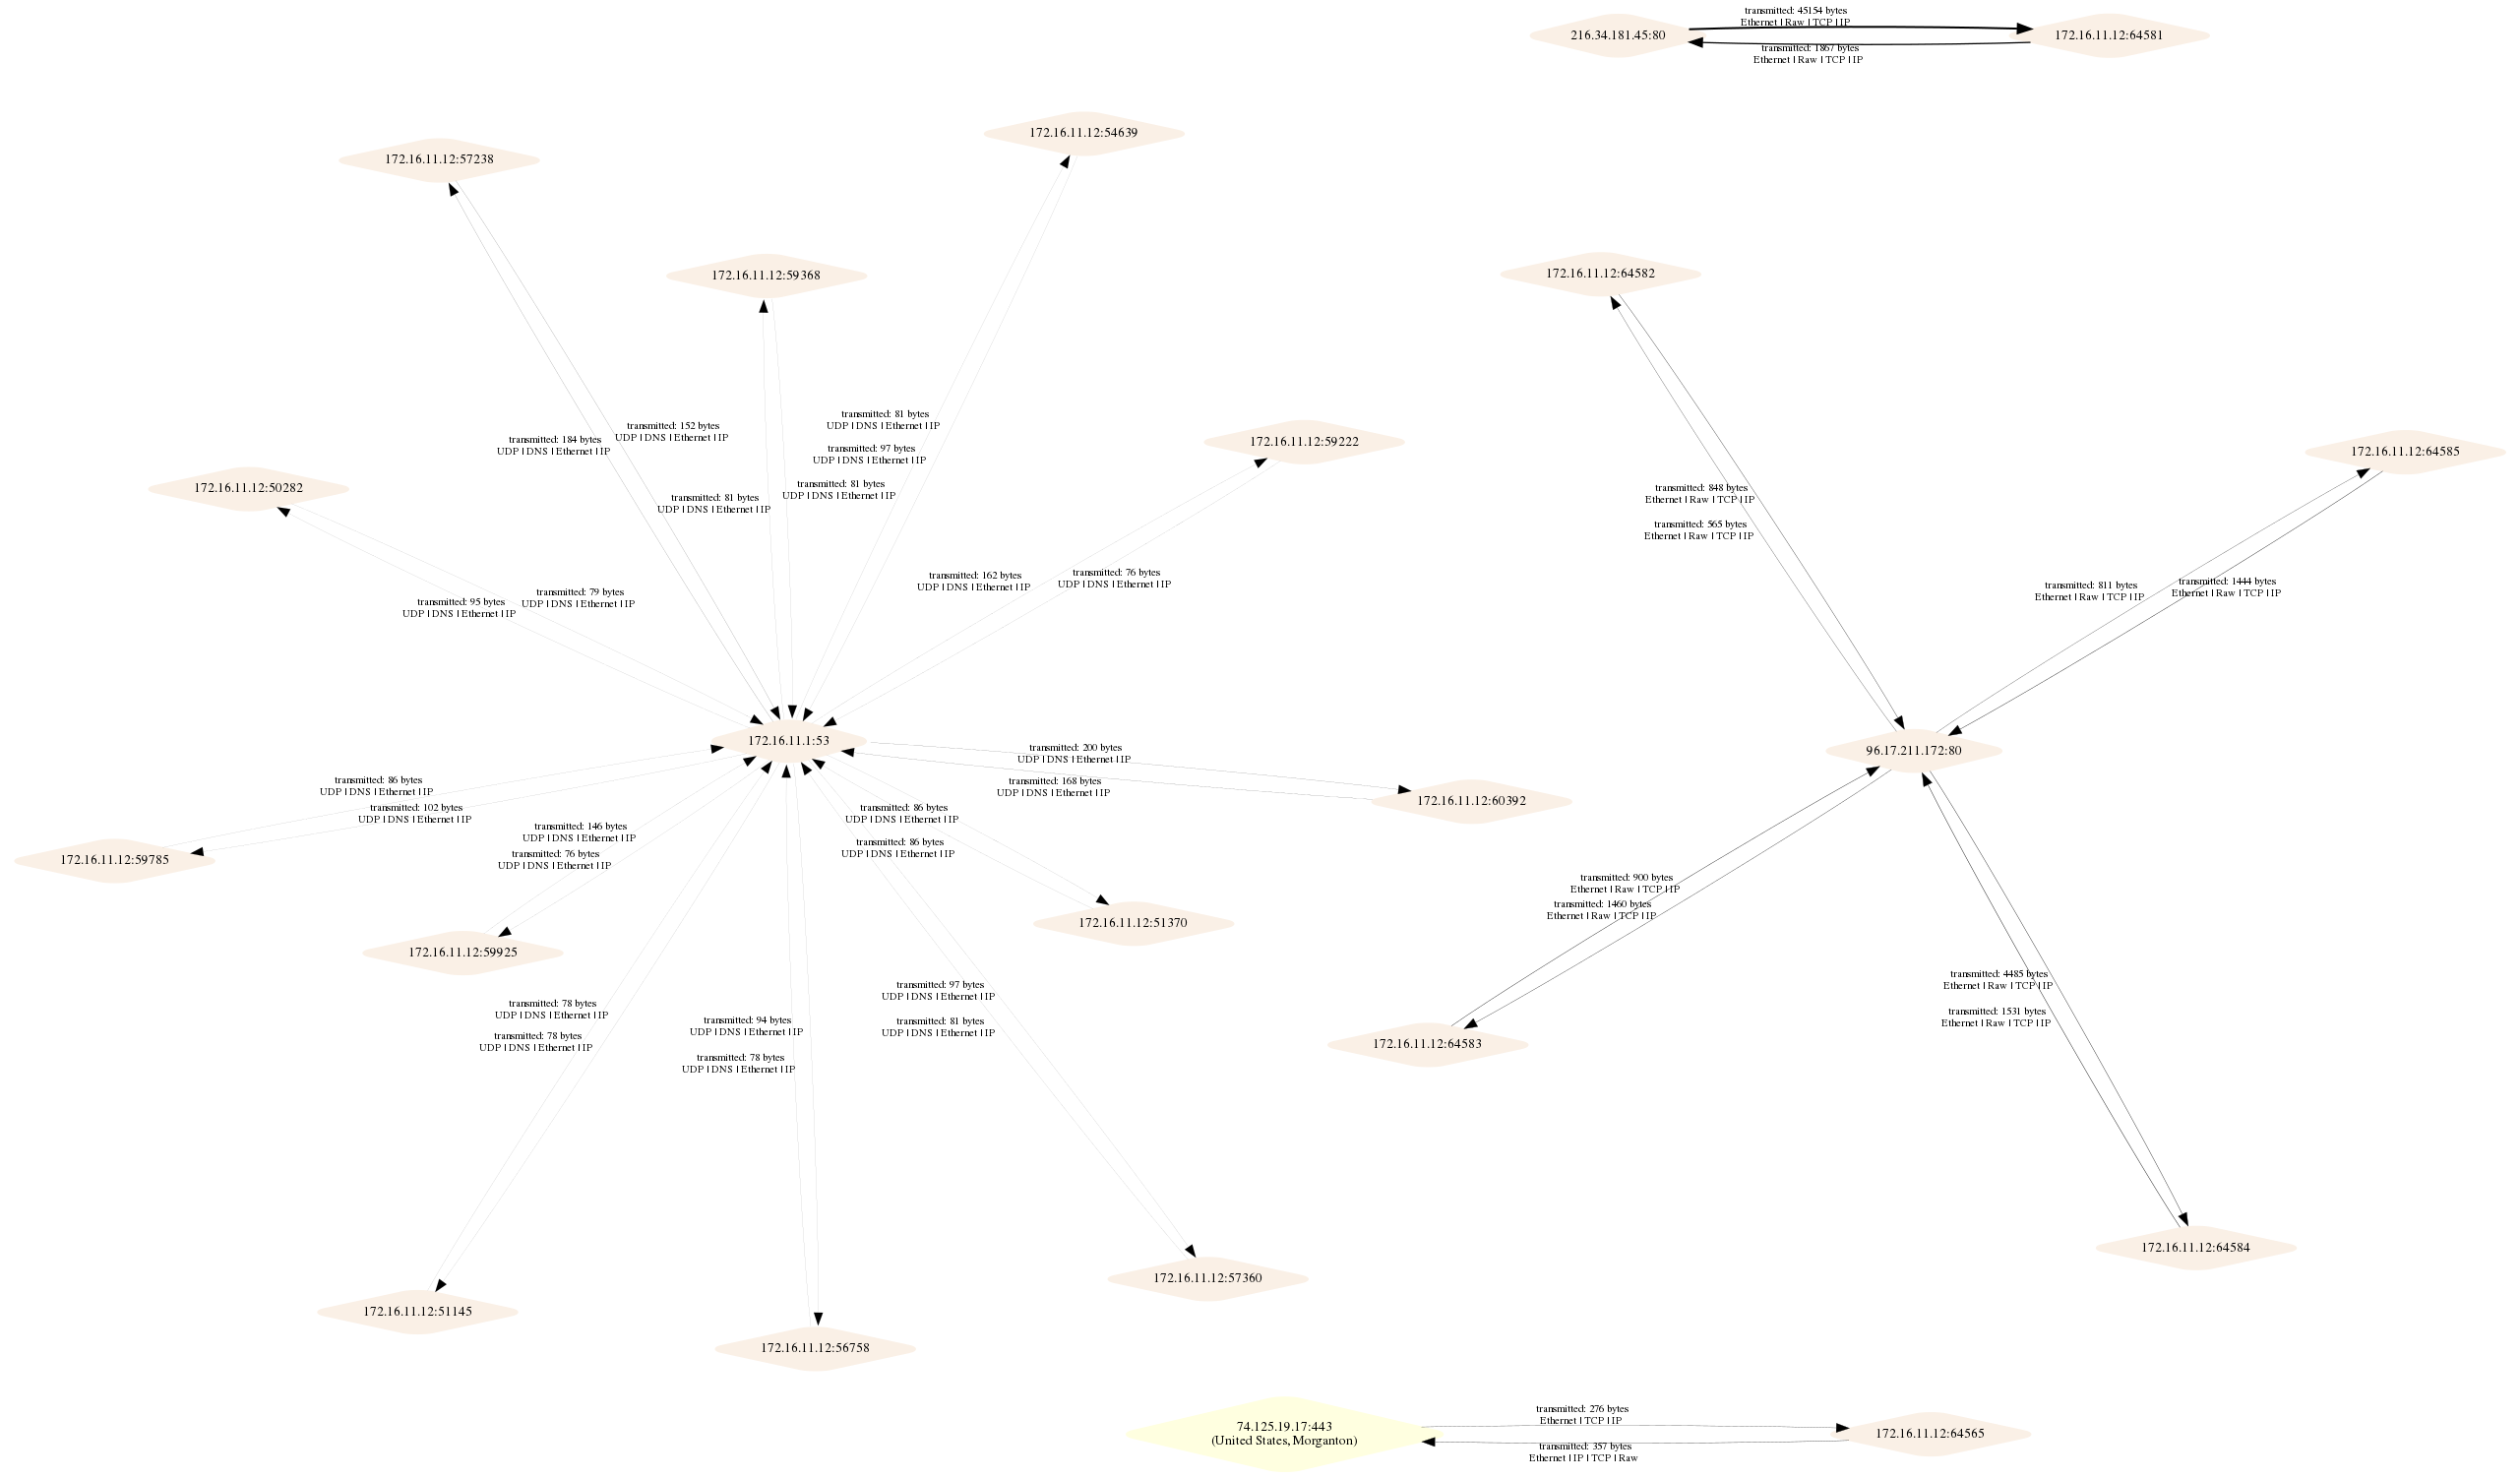
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
network-forensicspacket-sniffing-analysisthreat-intelligence
6844 years ago
PcapViz preview

PcapViz

GitHub1ultimat3/pcapviz

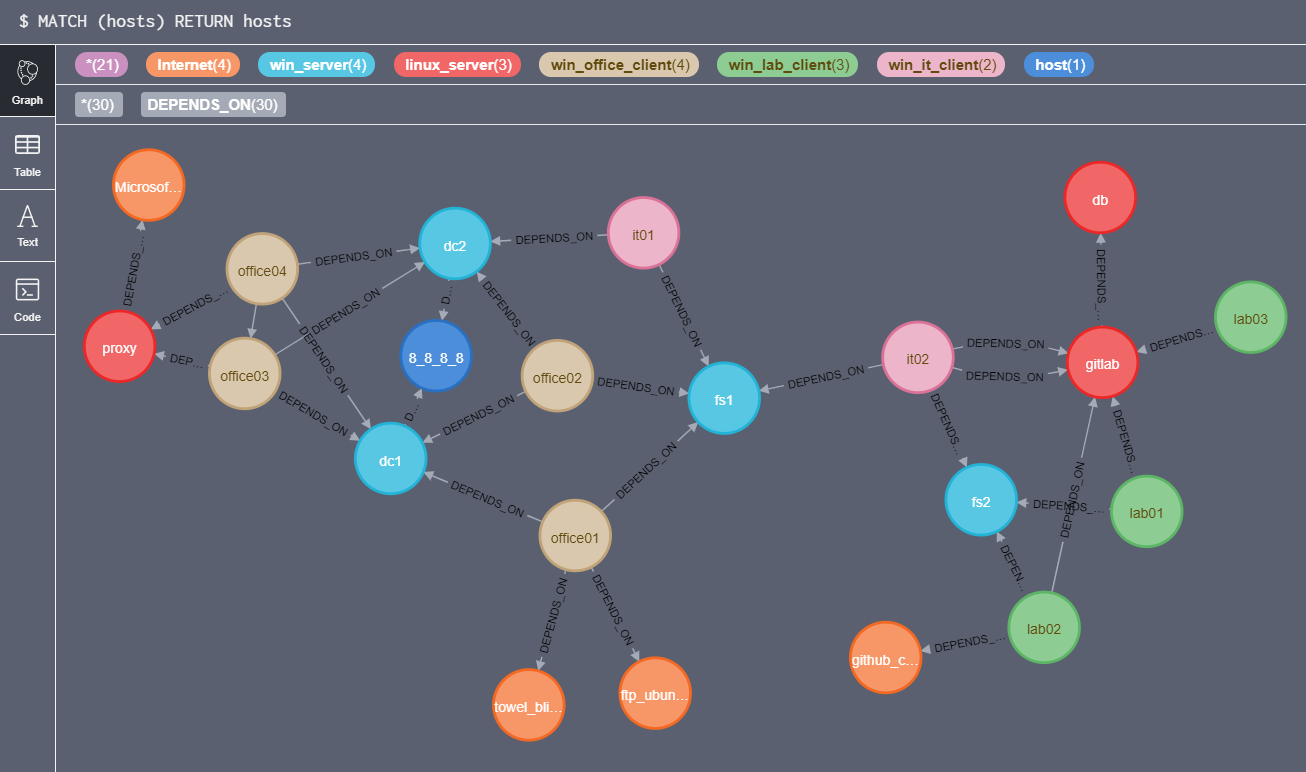
Visualize network topologies and collect graph statistics based on pcap files
information-gatheringnetwork-forensicsnetwork-mapping+1
3593 years ago
netstat2neo4j preview

netstat2neo4j

GitHubtrinitor/netstat2neo4j

create cypher create statements for neo4j out of netstat files from multiple machines

information-gatheringlog-analysisnetwork-forensics
415 years ago
Qu1cksc0pe preview

Qu1cksc0pe

GitHubcyb3rmx/qu1cksc0pe

All-in-One malware analysis tool.

android-securitydynamic-analysis-sandboxingforensics+4
2.0k1 month ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

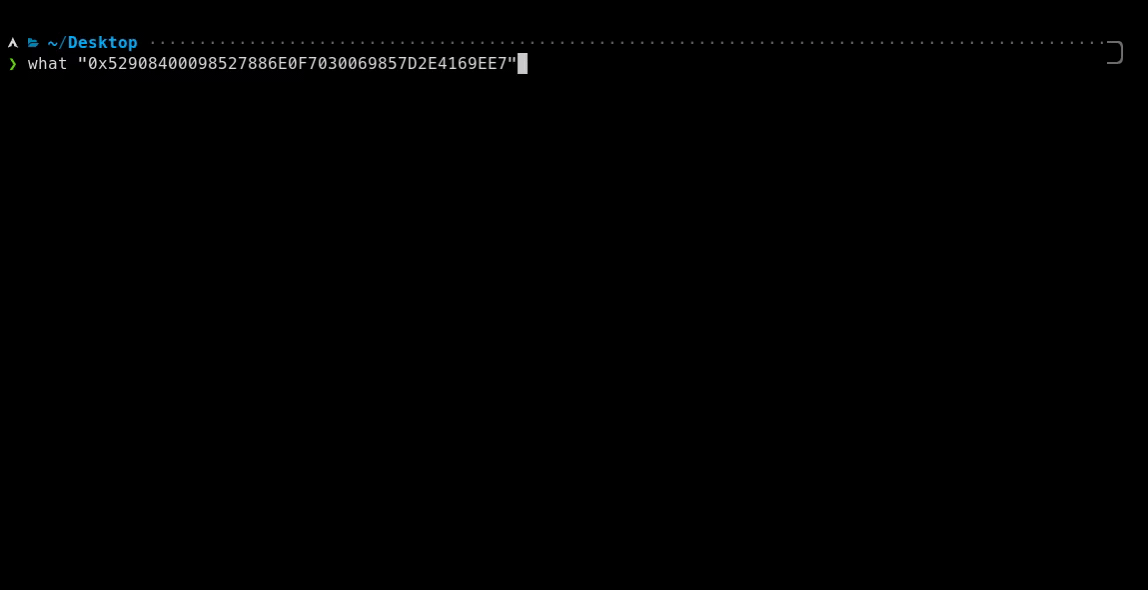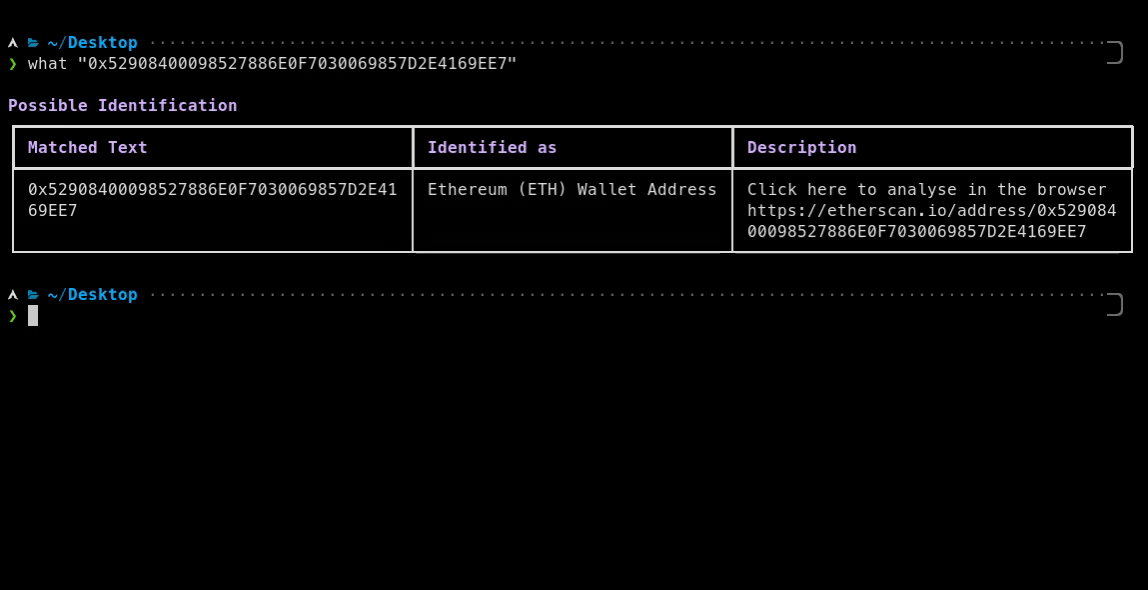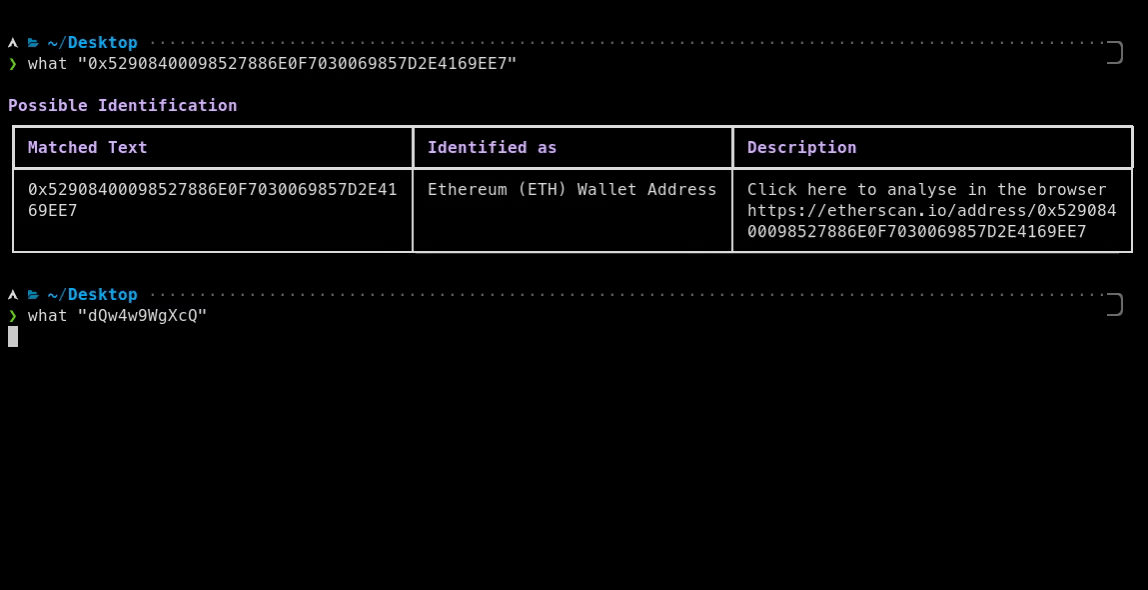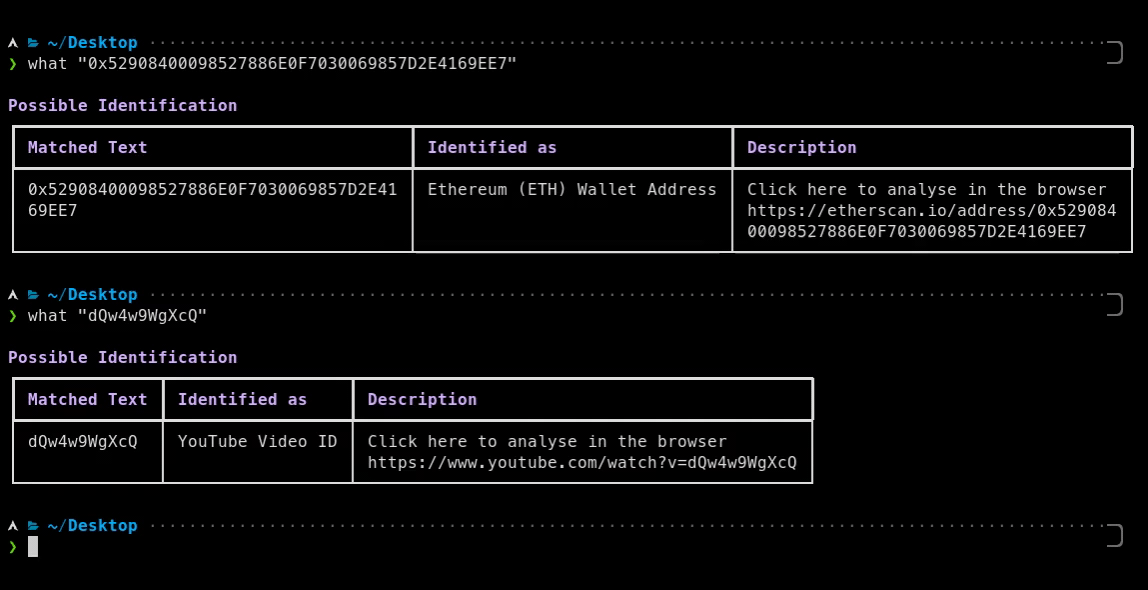
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
digital-forensicsforensicsnetwork-forensics+2
68 years ago
pyWhat preview

pyWhat

GitHubbee-san/pywhat

🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…

data-exfiltrationeducationforensics+7
7.3k1 month ago
honeypot-data preview

honeypot-data

GitHub0x4d31/honeypot-data

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…

incident-responseinformation-gatheringioc-management+4
447 days ago
dissect preview

dissect

GitHubfox-it/dissect

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
data-recoverydigital-forensicsdisk-forensics+5
1.1k1 day ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
122 months ago
Skadi preview

Skadi

GitHuborlikoski/skadi

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
curated-resourcesdigital-forensicsdisk-forensics+9
5174 years ago
StegoForge preview

StegoForge

GitHubnour833/stegoforge

The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
cryptographyctfdata-exfiltration+8
57511 days ago
Baskerville preview

Baskerville

GitHubnccgroup/baskerville

Selective protocol extractor from PCAPs or interfaces

incident-responsenetwork-forensicsnetwork-security+1
512 years ago
Previous12Next