

Loki
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k
neo23x0/lokiIOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
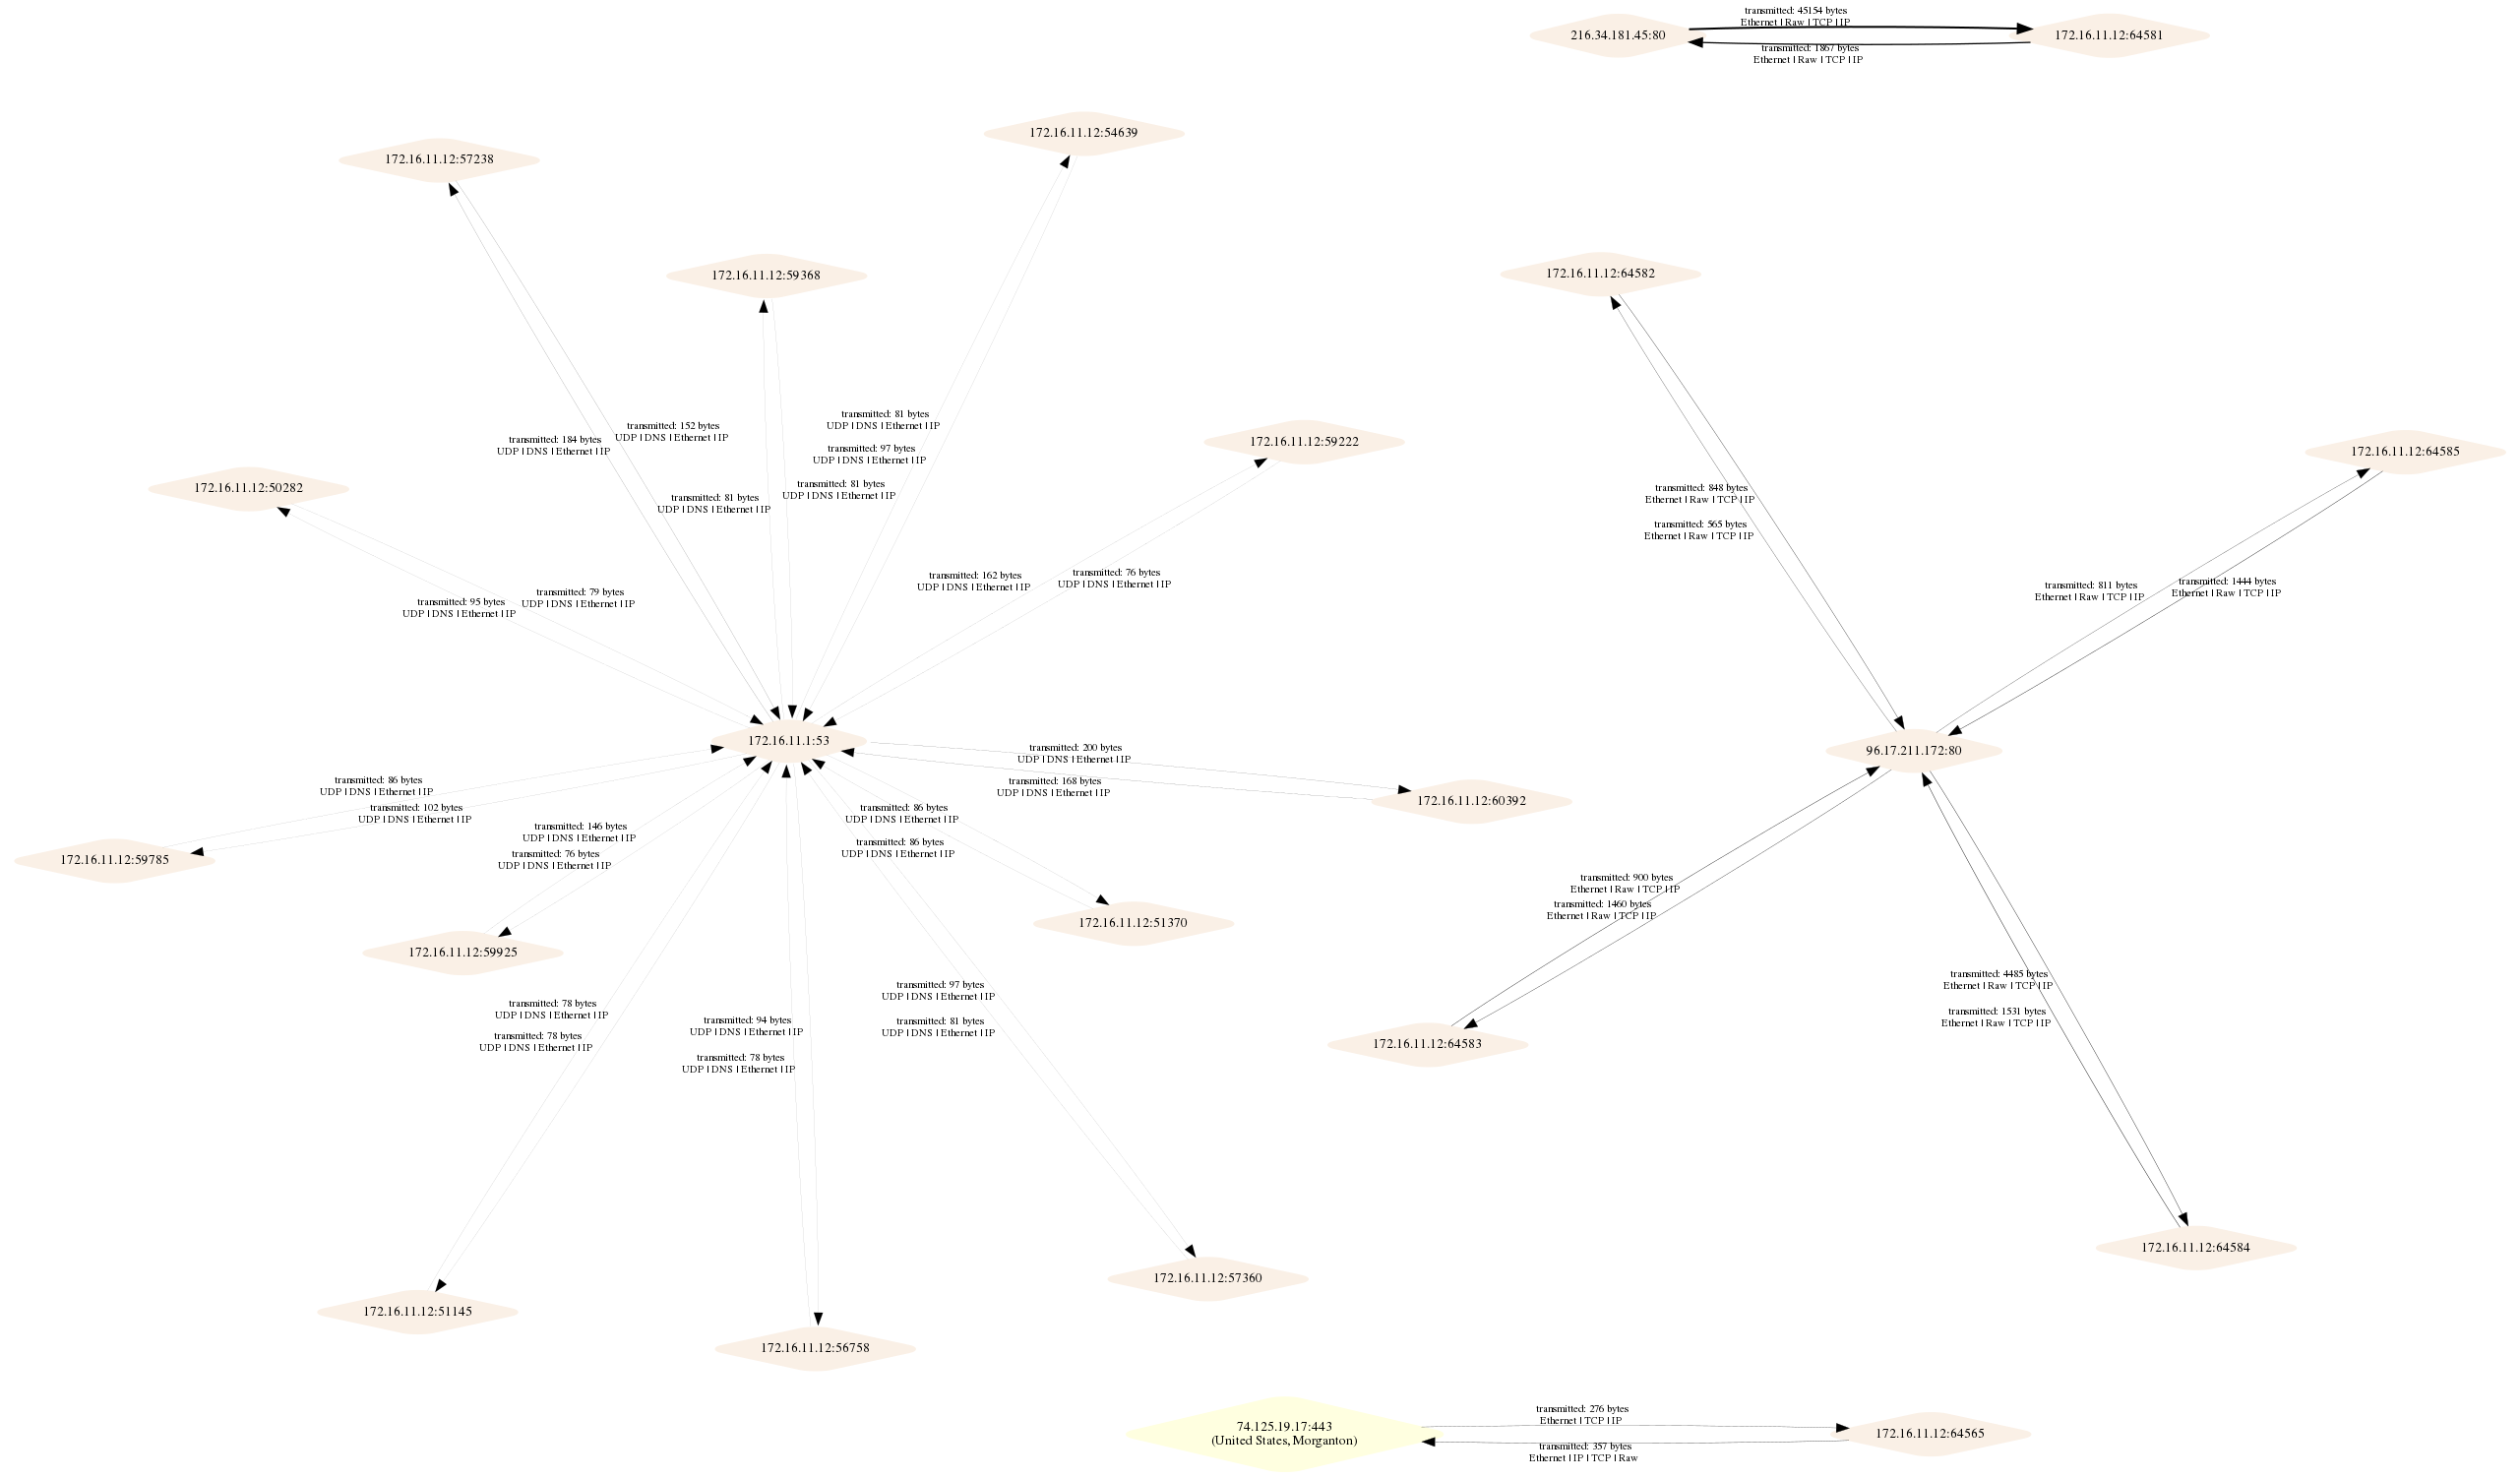 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
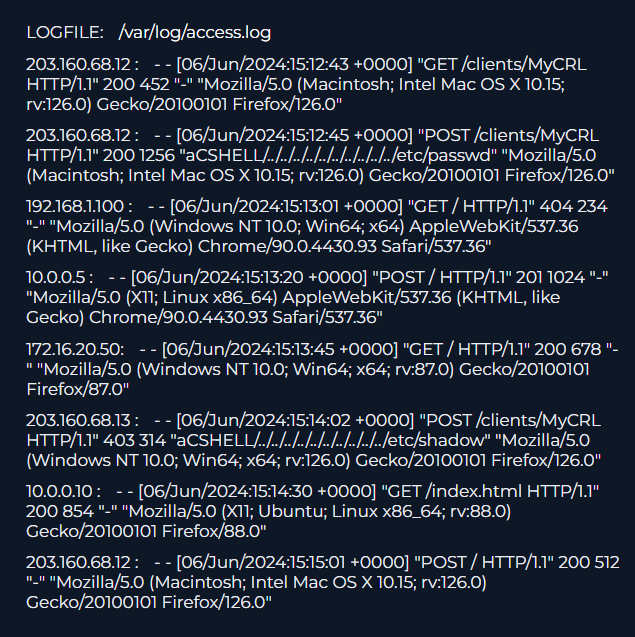 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 gilberto47831/network-filesystem-forensics
Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture