
CVE-2024-40815
 w0wbox/cve-2024-40815
POC for CVE-2024-40815 (Construction is in its final stage ==IOS 17.0)
exploitationios-securitymobile-security+2
1311 months ago
w0wbox/cve-2024-40815POC for CVE-2024-40815 (Construction is in its final stage ==IOS 17.0)
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 absholi7ly/poc-for-cve-2024-7014-exploit
Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 wqry085/poc-deployer-system
Quick tool for utilizing CVE-2024-31317 on Android
 agg23/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317
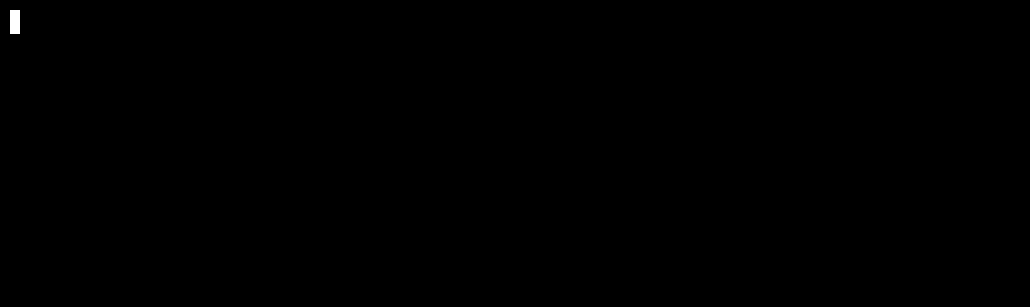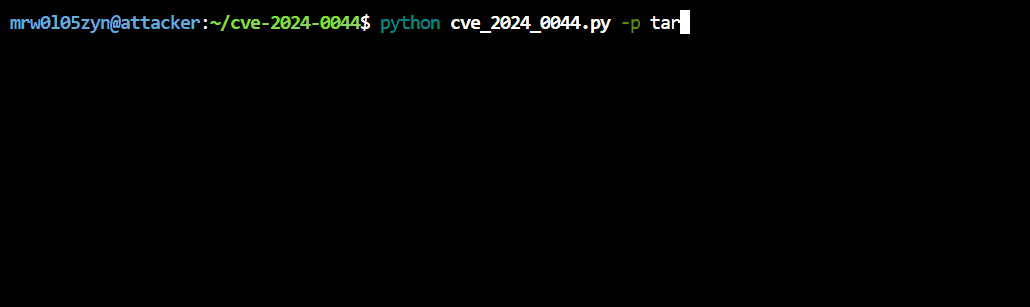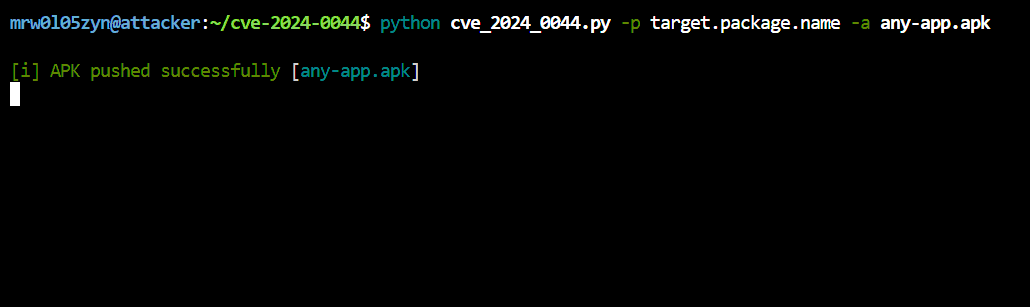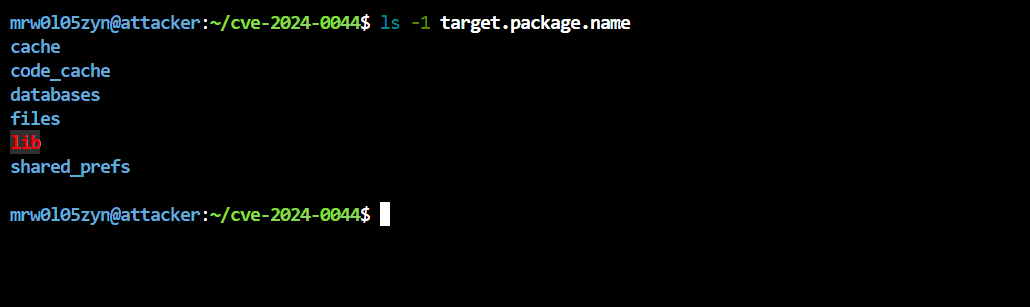
 re13orn/cve-2024-0044-exp
利用 CVE-2024-0044 Android 权限提升下载任意目标App沙箱文件。
 hackerronin/cve-2024-0044
a vulnerability affecting Android version 12 & 13
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 007criptografia/c-cve-2024-0044
CVE-2024-0044: uma vulnerabilidade de alta gravidade do tipo "executar como qualquer aplicativo" que afeta as versões 12 e 13 do Android
 rifting/zygotroller
Remove Android profile owners/family link with CVE-2024-31317
 thebl4ckph4nt0m/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13. This repo demonstrates how to exploit…