
pois0nSword
 genericcoding/pois0nsword
A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
binary-exploitationexploitationexploit-frameworks+5
69
genericcoding/pois0nswordA demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
 geosn0w/cve-2025-24203-ios-exploit-with-error-logging
Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero
 awakened1712/cve-2019-11932
Simple POC for exploiting WhatsApp double-free bug in DDGifSlurp in decoding.c in libpl_droidsonroids_gif
 amorcool/ios26.6-cve-2026-65343
CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)
 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 dorkerdevil/cve-2019-11932
double-free bug in WhatsApp exploit poc
 persistent-security/smshell
PoC for a SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers
 b1n4r1b01/desc_race
iOS 15.1 kernel exploit POC for CVE-2021-30955
 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 projectorbug/cve-2020-11932
Double-Free BUG in WhatsApp exploit poc.
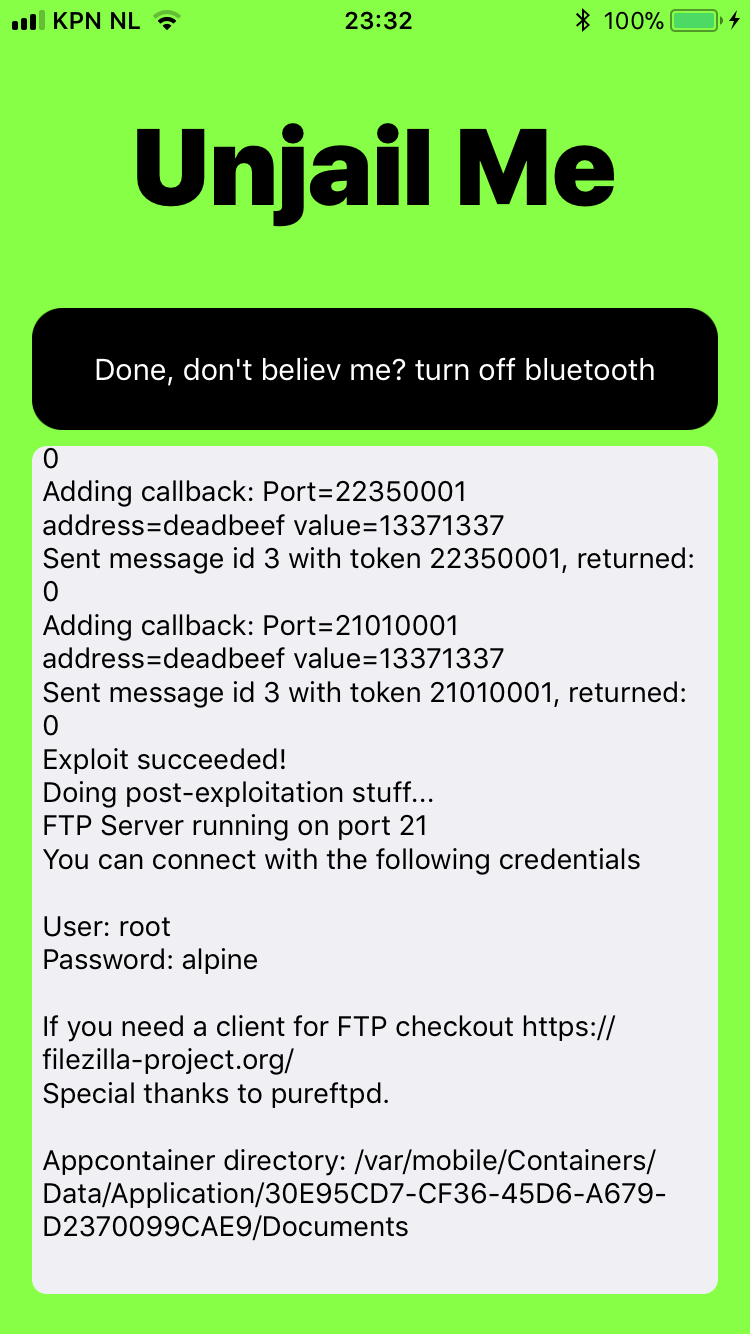 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 straight-tamago/nocamerasound
CVE-2022-46689
 fatgrass/osirisjailbreak12
iOS 12.0 -> 12.1.2 Incomplete Osiris Jailbreak with CVE-2019-6225 by GeoSn0w (FCE365)
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 keepwannabe/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
 zzzxxxxxxxxxx/ghostlock-got-w29
CVE-2026-43499 (GhostLock) research on HUAWEI MatePad Pro 11 GOT-W29
 jasonjerry/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
 josephshenton/triple_fetch-kernel-creds
Attempt to steal kernelcredentials from launchd + task_t pointer (Based on: CVE-2017-7047)