
CVE-2025-43300
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
binary-exploitationeducationembedded-systems-security+7
116
hunters-sec/cve-2025-43300This is POC for IOS 0click CVE-2025-43300
 elevenpaths/dirtytooth-raspberrypi
Exploit the hack for IOS 11.1.2 and earlier to collect leaked information.
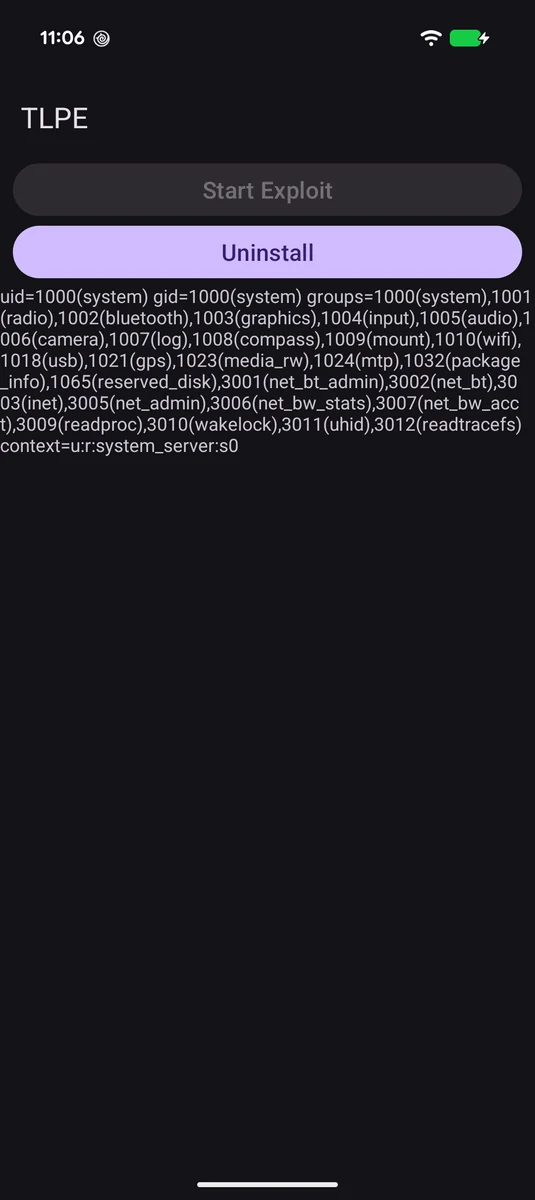 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
 aau-network-security/hostage
Low Interaction Mobile Honeypot
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 cakestwix/android-cve-2026-43499
Android version CVE-2026-43499 tester
 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
 ifpdz/cve-2025-24104
Technical writeup of CVE-2025-24104: an iOS sandbox escape via symlink validation bypass in backup restoration, enabling arbitrary file reads outside…
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.

 neternels/android_kernel_xiaomi_sunny
CAFest nethunter kernel based on LA.UM.9.1.r1-11900-SMXXX0.0 with latest upstream-f2fs-stable-linux-4.14.y merged, bb and perf focused. | Force push…
 yijiacloud/ghostlock-cve-2026-43499-4.19-k40
CVE-2026-43499 (GhostLock) rtmutex remove_waiter() UAF local-root PoC adapted for Qualcomm Android 4.19 kernels (Redmi K40 / Snapdragon 870 class),…
 alwentiu/covidsafe-cve-2020-12856
A bluetooth-related vulnerability in some contact tracing apps
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 dangtunguyen/towelroot
Gain root privilege by exploiting CVE-2014-3153 vulnerability