

framework_base_AOSP10_r33_CVE-2020-0137
 nanopathi/framework_base_aosp10_r33_cve-2020-0137
android-securitybinary-exploitationexploitation+2
nanopathi/framework_base_aosp10_r33_cve-2020-0137 nanopathi/framework_base_aosp10_r33_cve-2021-0954
 thampakon/cve-2023-35674
ช่องโหว่ CVE-2023-35674 *สถานะ: ยังไม่เสร็จ*
 natleoj/cve-2019-11933
Heap corruption in WhatsApp's media picker
 febinrev/cve-2019-6447-esfile-explorer-exploit
ES File Explorer v4.1.9.7.4 Open port vulnerability exploit. CVE-2019-6447
 nanopathi/packages_apps_managedprovisioning_cve-2021-39692
 726232111/packages_apps_settings_aosp_10_r33_cve-2022-20360
Provides AOSP Android Settings source for Android 10 r33, tagged with CVE-2022-20360 for vulnerability reproduction and patch analysis.
 shaikusaf/frameworks_base_aosp10_r33_cve-2021-20138
Analyzes and patches Android framework vulnerability CVE-2021-20138 in AOSP 10, providing security fixes for mobile platforms.
 sandarufdo/es-file-explorer-open-port-vulnerability---cve-2019-6447
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 huaguiqi/asus_i005-cve-2026-43499
Android local privilege escalation exploit for CVE-2026-43499 that patches kernel creds and launches embedded KernelSU in late-load mode via…
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
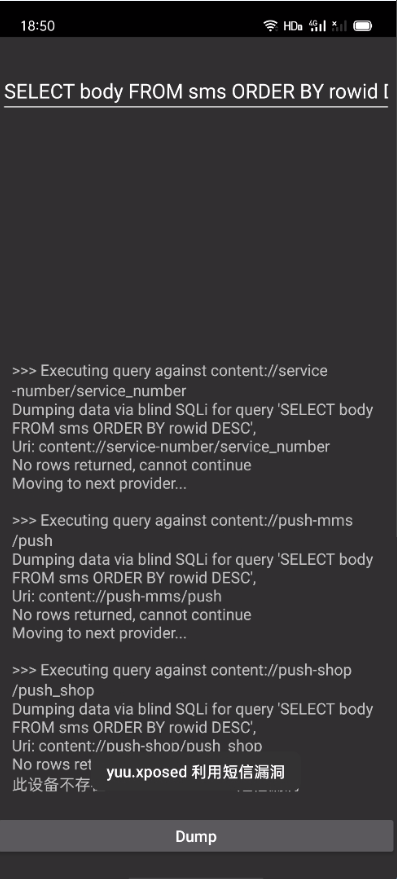 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
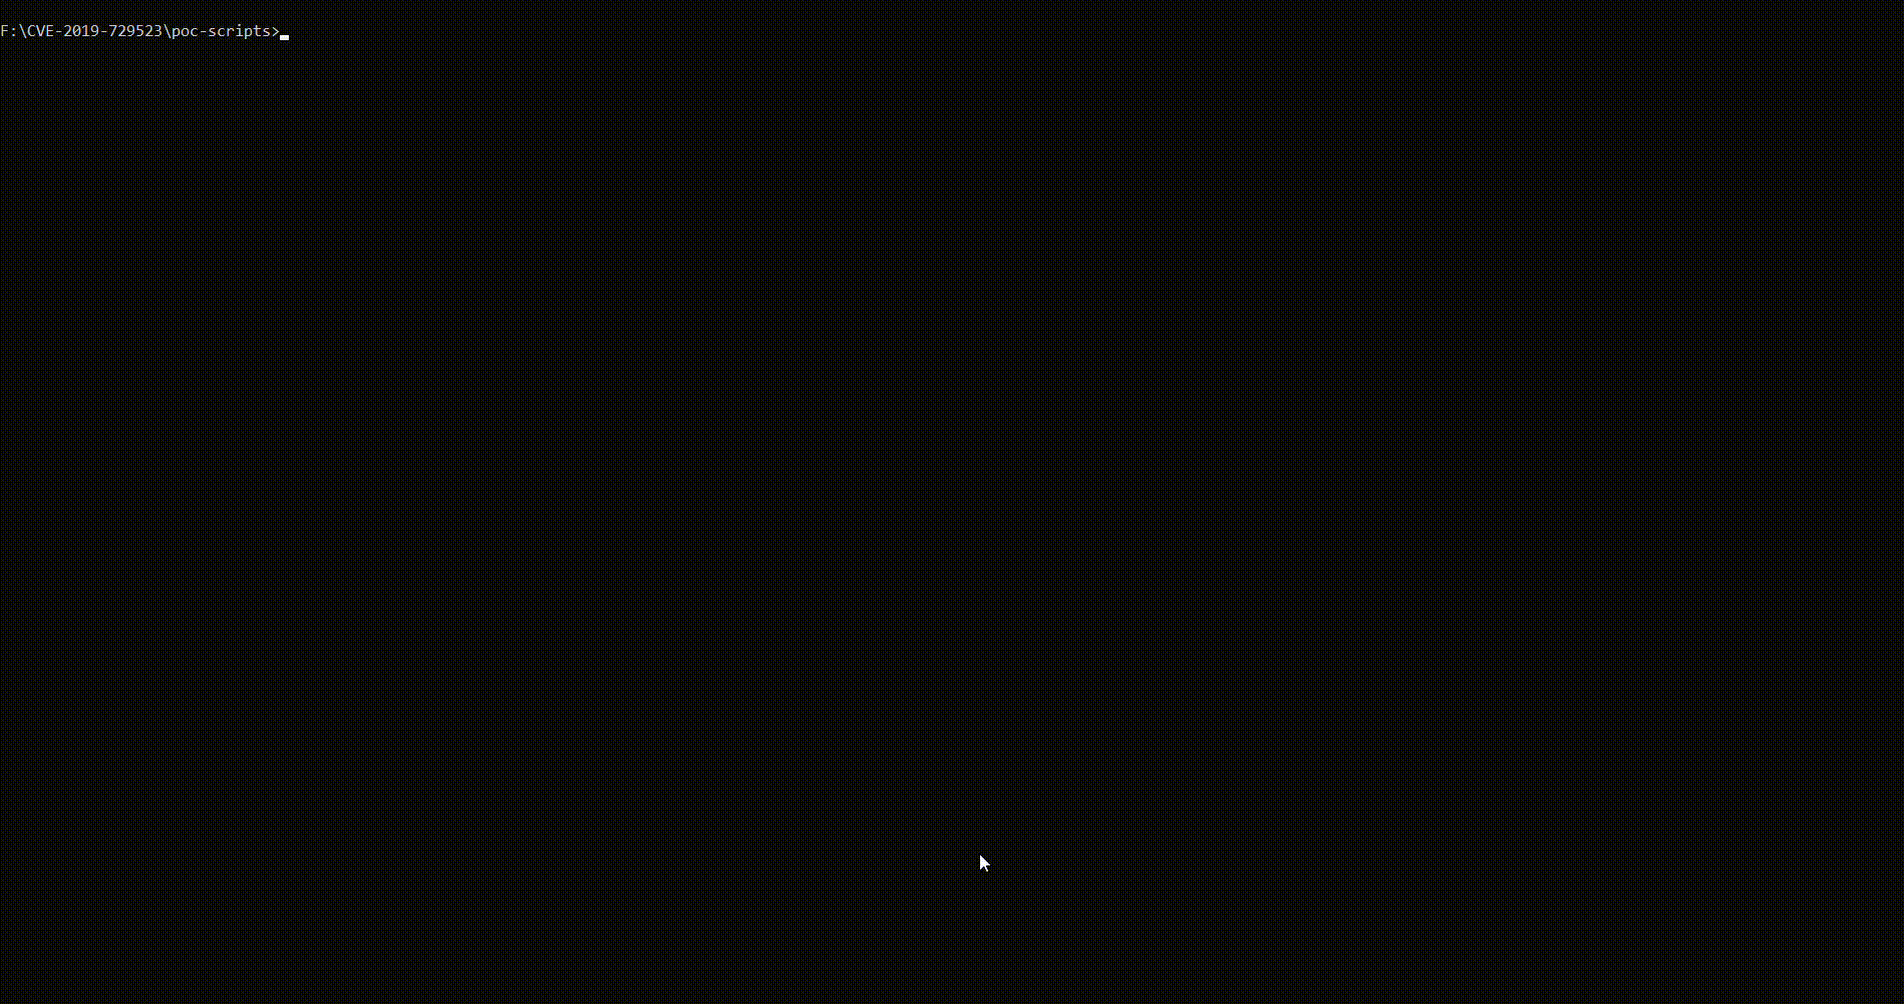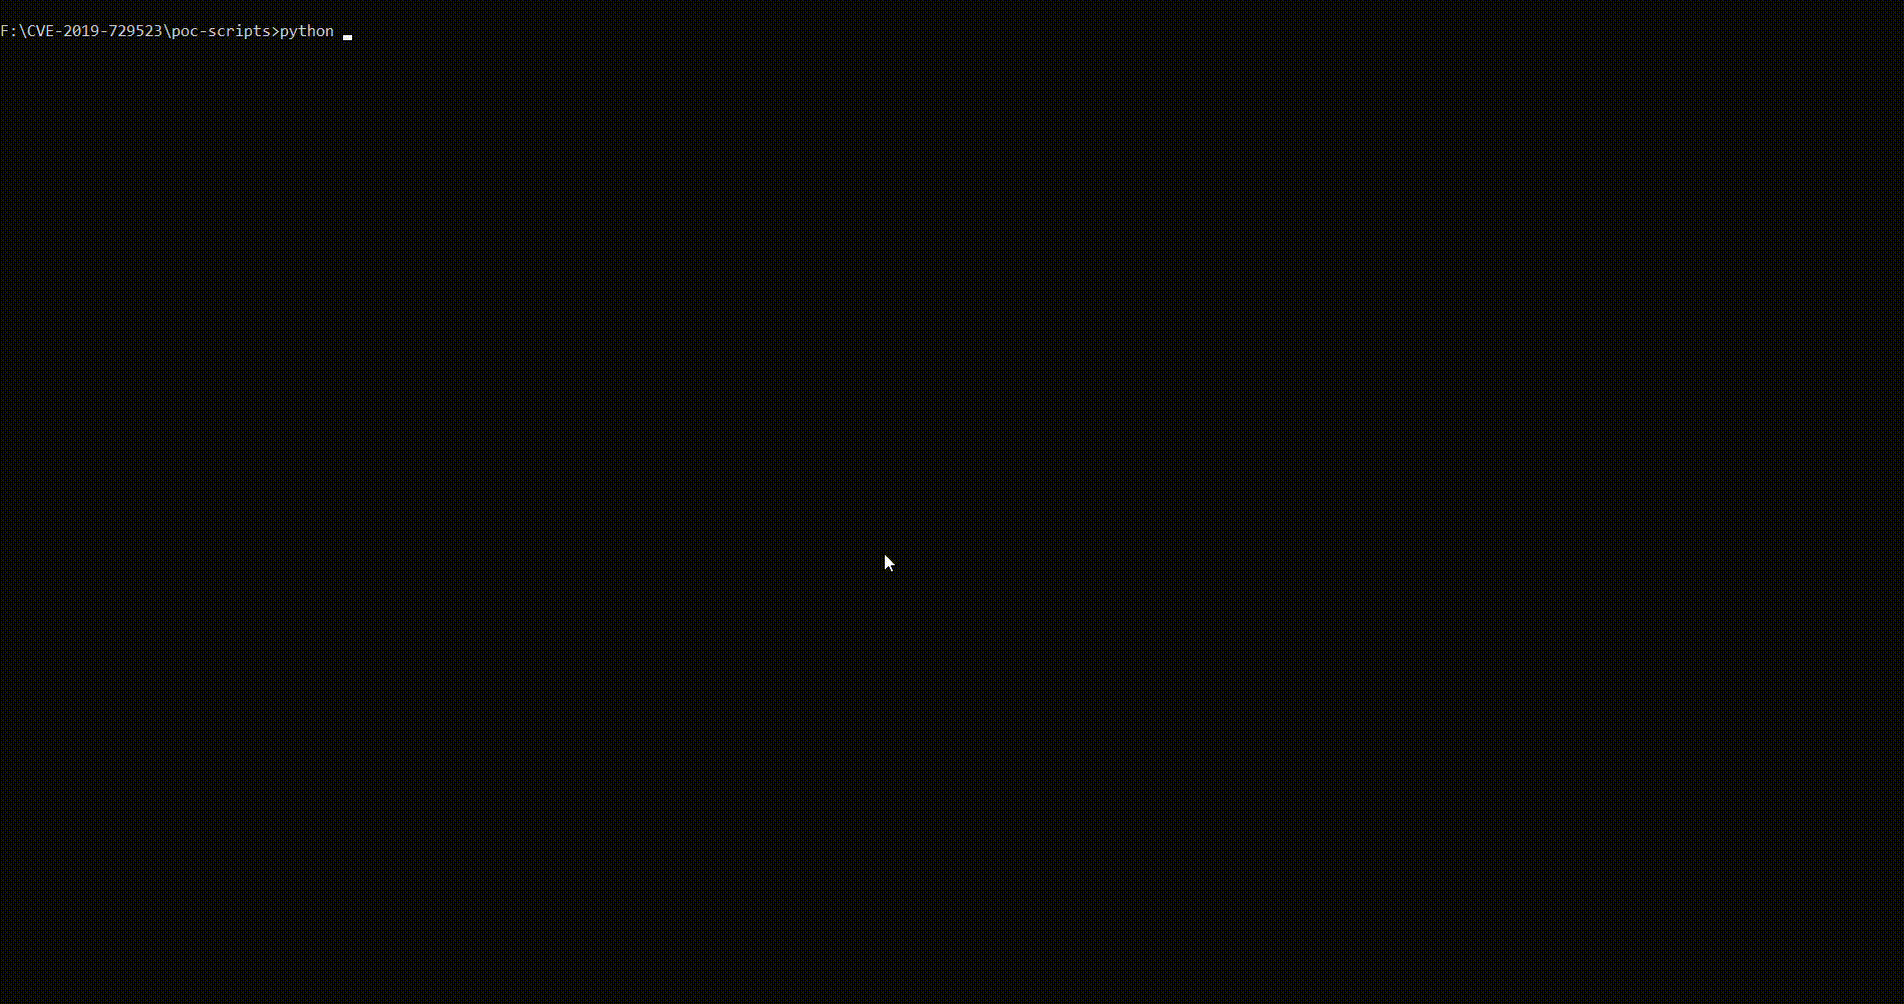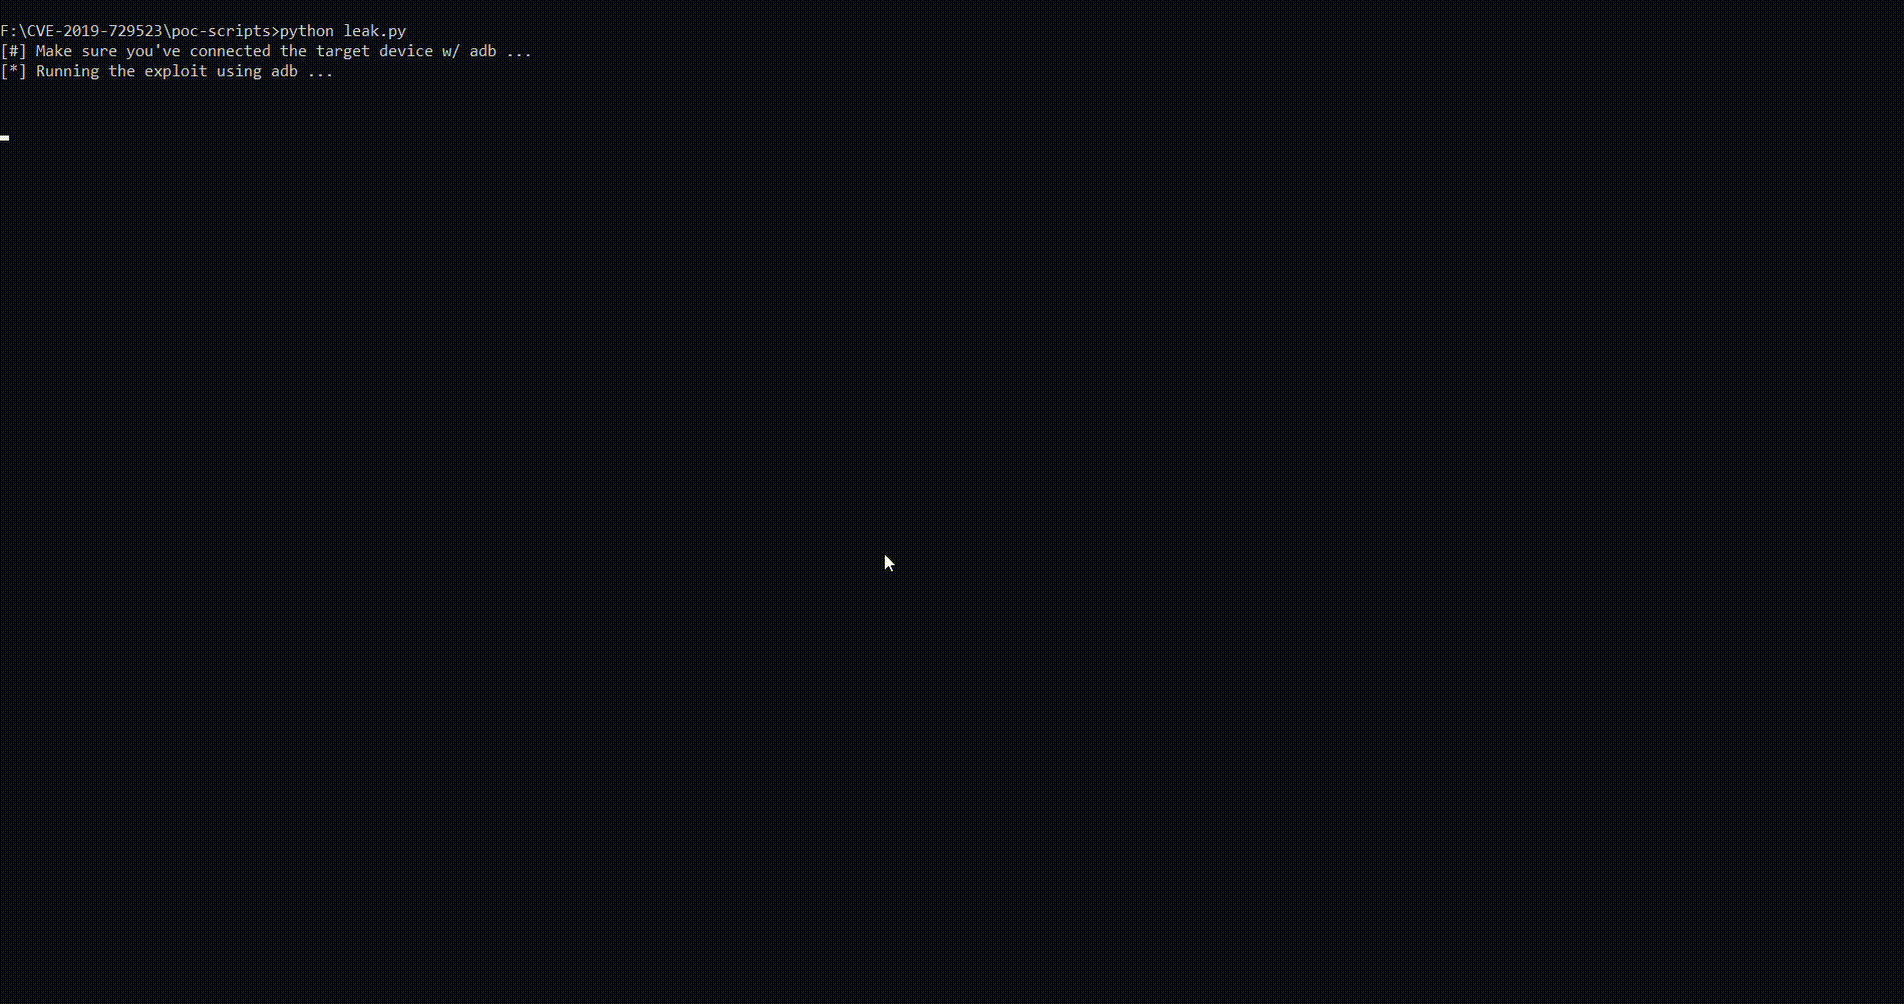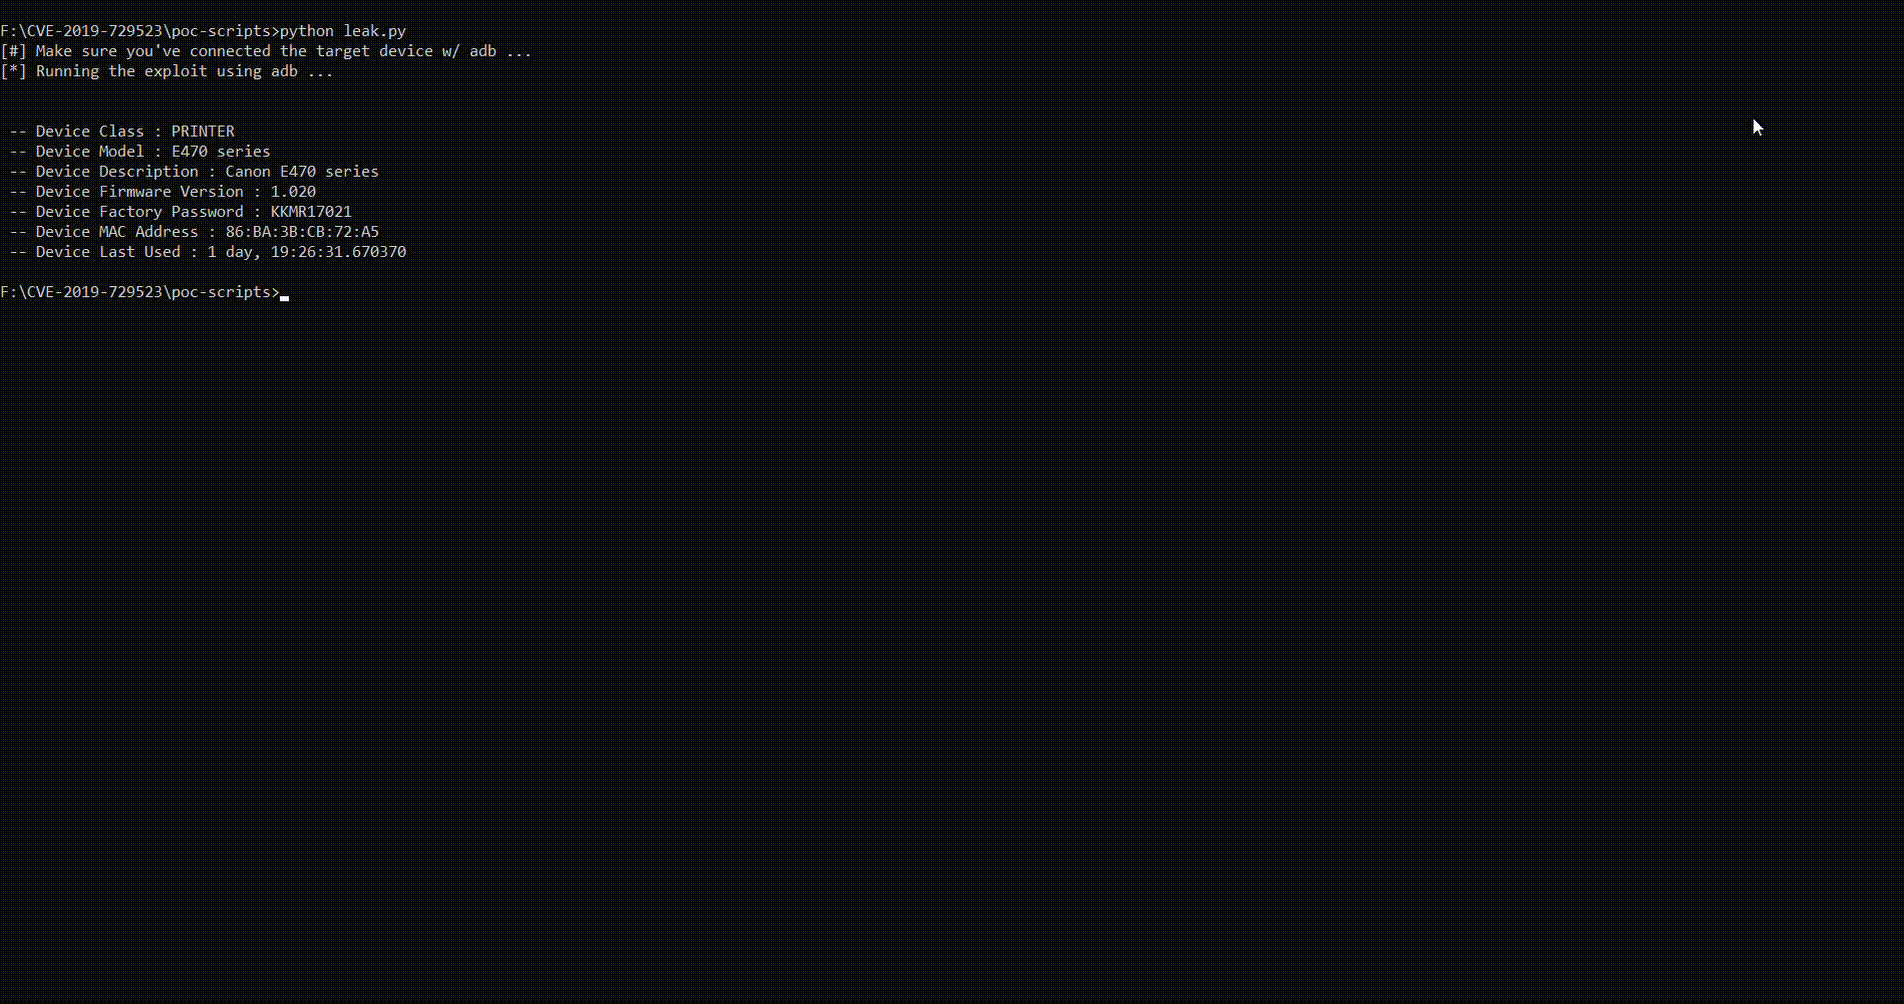 0x48piraj/cve-2019-14339
POC for CVE-2019-14339 Canon PRINT 2.5.5
 linuxoid-cn/mi8e5-unlocker-by-cve-2026-43499
基于 CVE-2026-43499 的 8E5 机型自动化解锁辅助工具,仅限授权安全研究与自有设备使用。