ekoparty
 actuator/ekoparty
Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers
android-securityeducationexploitation+5
actuator/ekopartyEkoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers
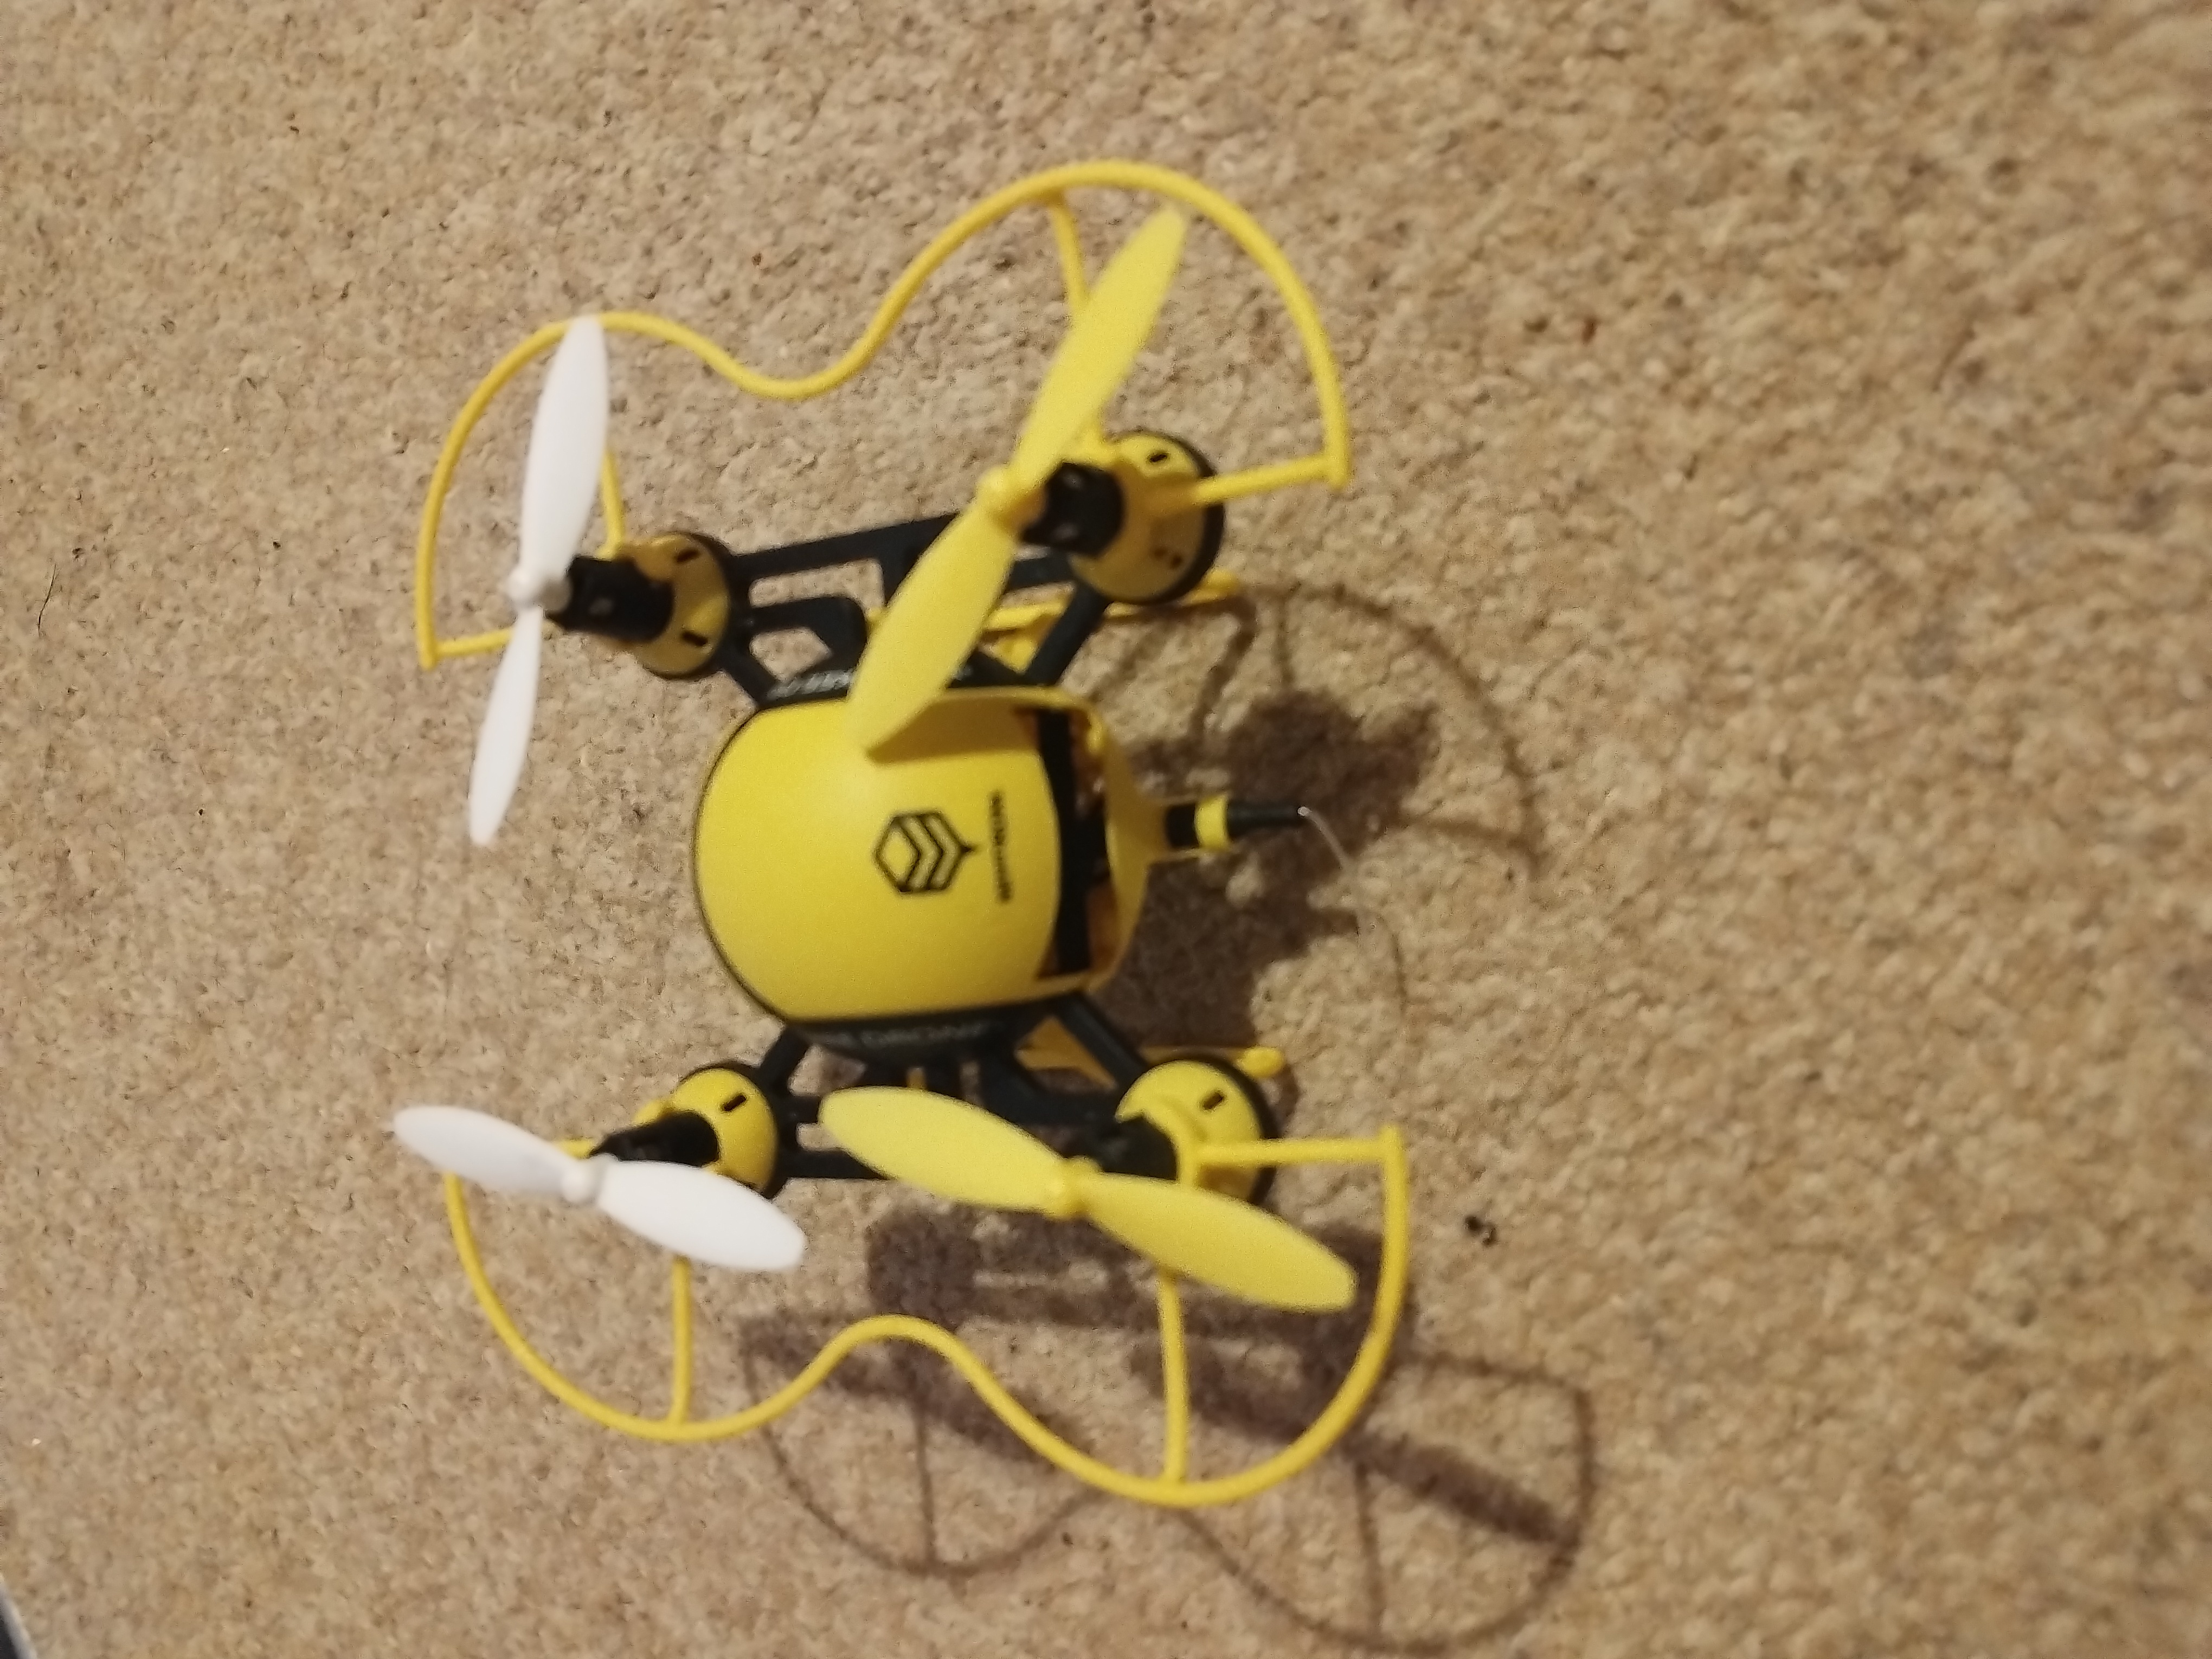 mretallack/dronecamera
Drone HASAKEE FPV video app for Android
 aymankhalfatni/cve-2017-0785
CVE-2017-0785: BlueBorne PoC
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 kavidk/cve-2019-6447-in-mobile-application
Research report detailing CVE-2019-6447 exploitation in real-world mobile applications, including practical examples and a demonstration video.
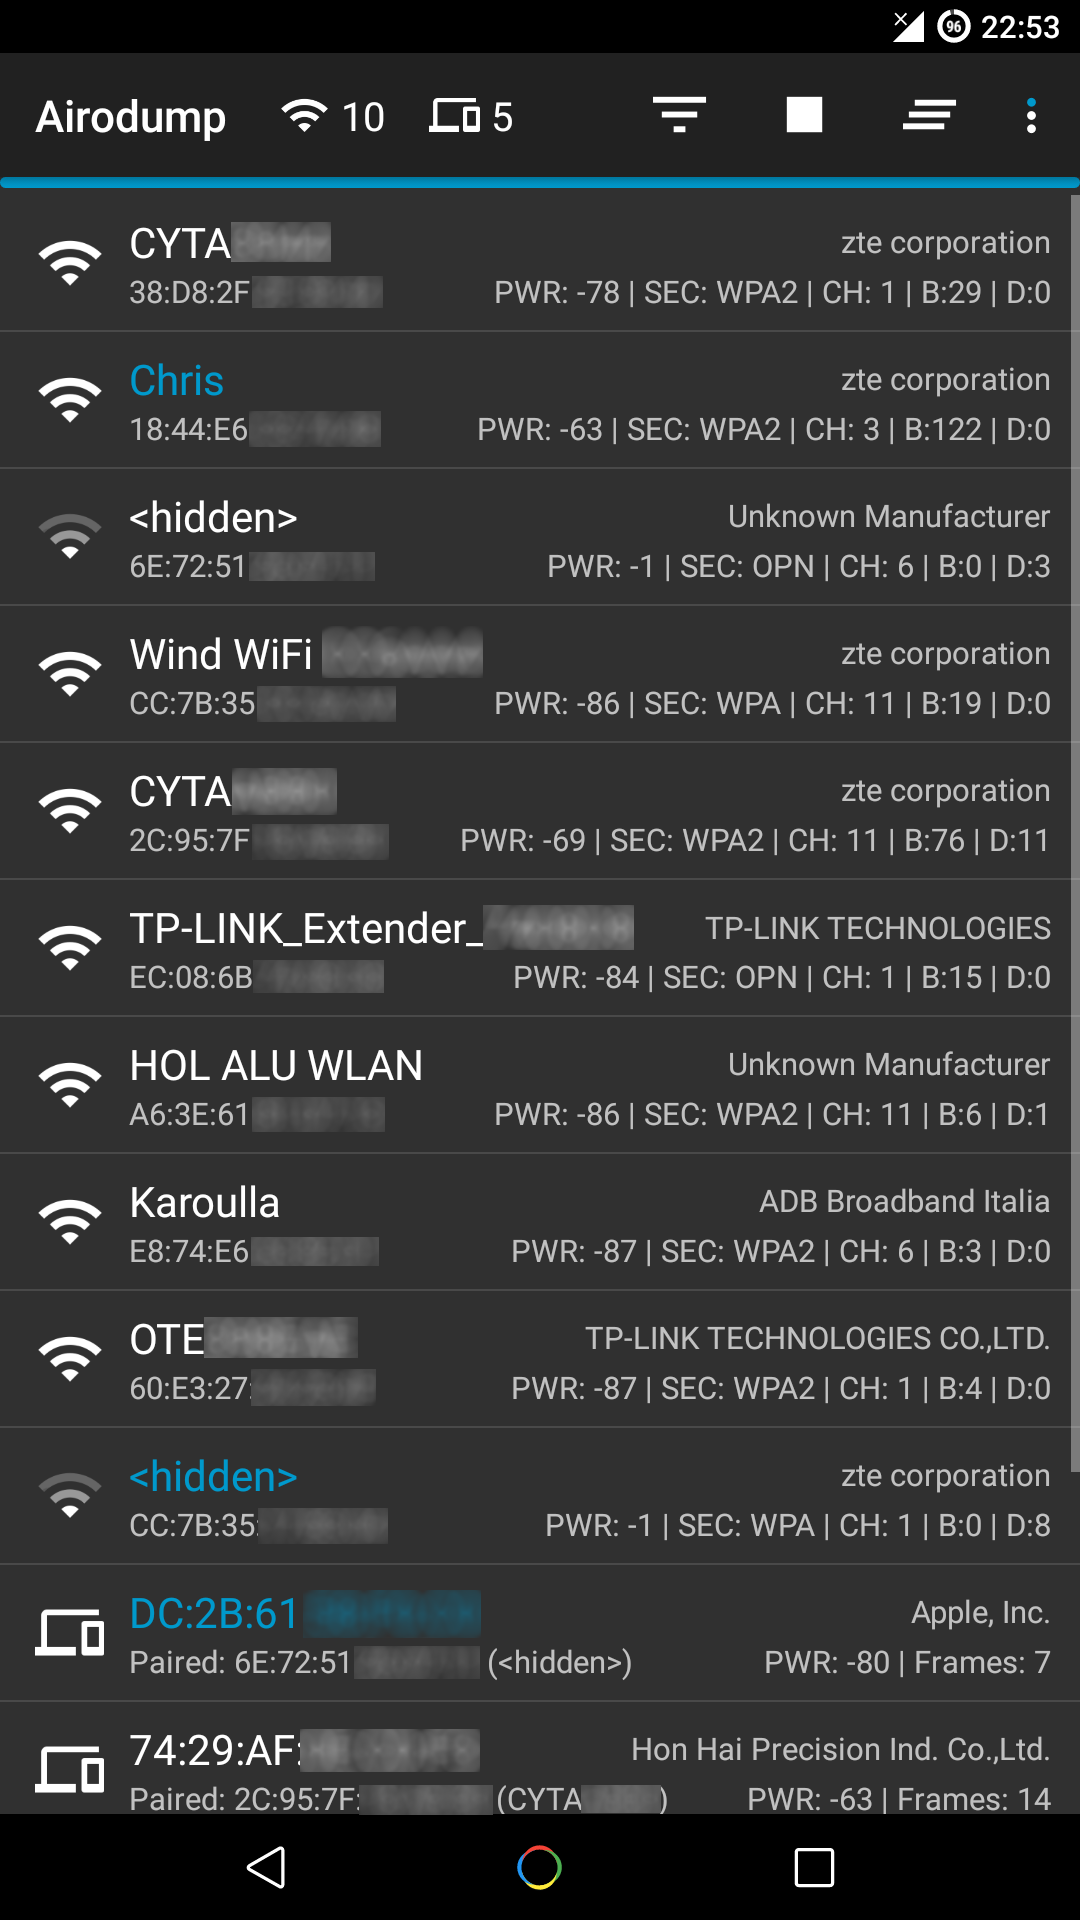 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 camsshaft/ionstack-s22-cve-2026-43499
Android kernel exploit for Samsung Galaxy S22 that gains kernel-domain root via CVE-2026-43499, with SELinux permissive, device-specific kallsyms,…
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
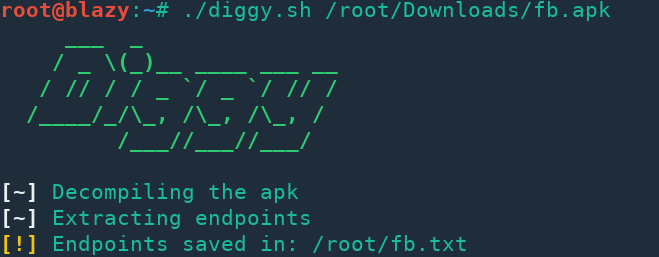 s0md3v/diggy
Extract endpoints from apk files.
 ymh001/meizu21-ghostlock-root
MEIZU 21 locked-bootloader runtime root via CVE-2026-43499 and KernelSU late-load
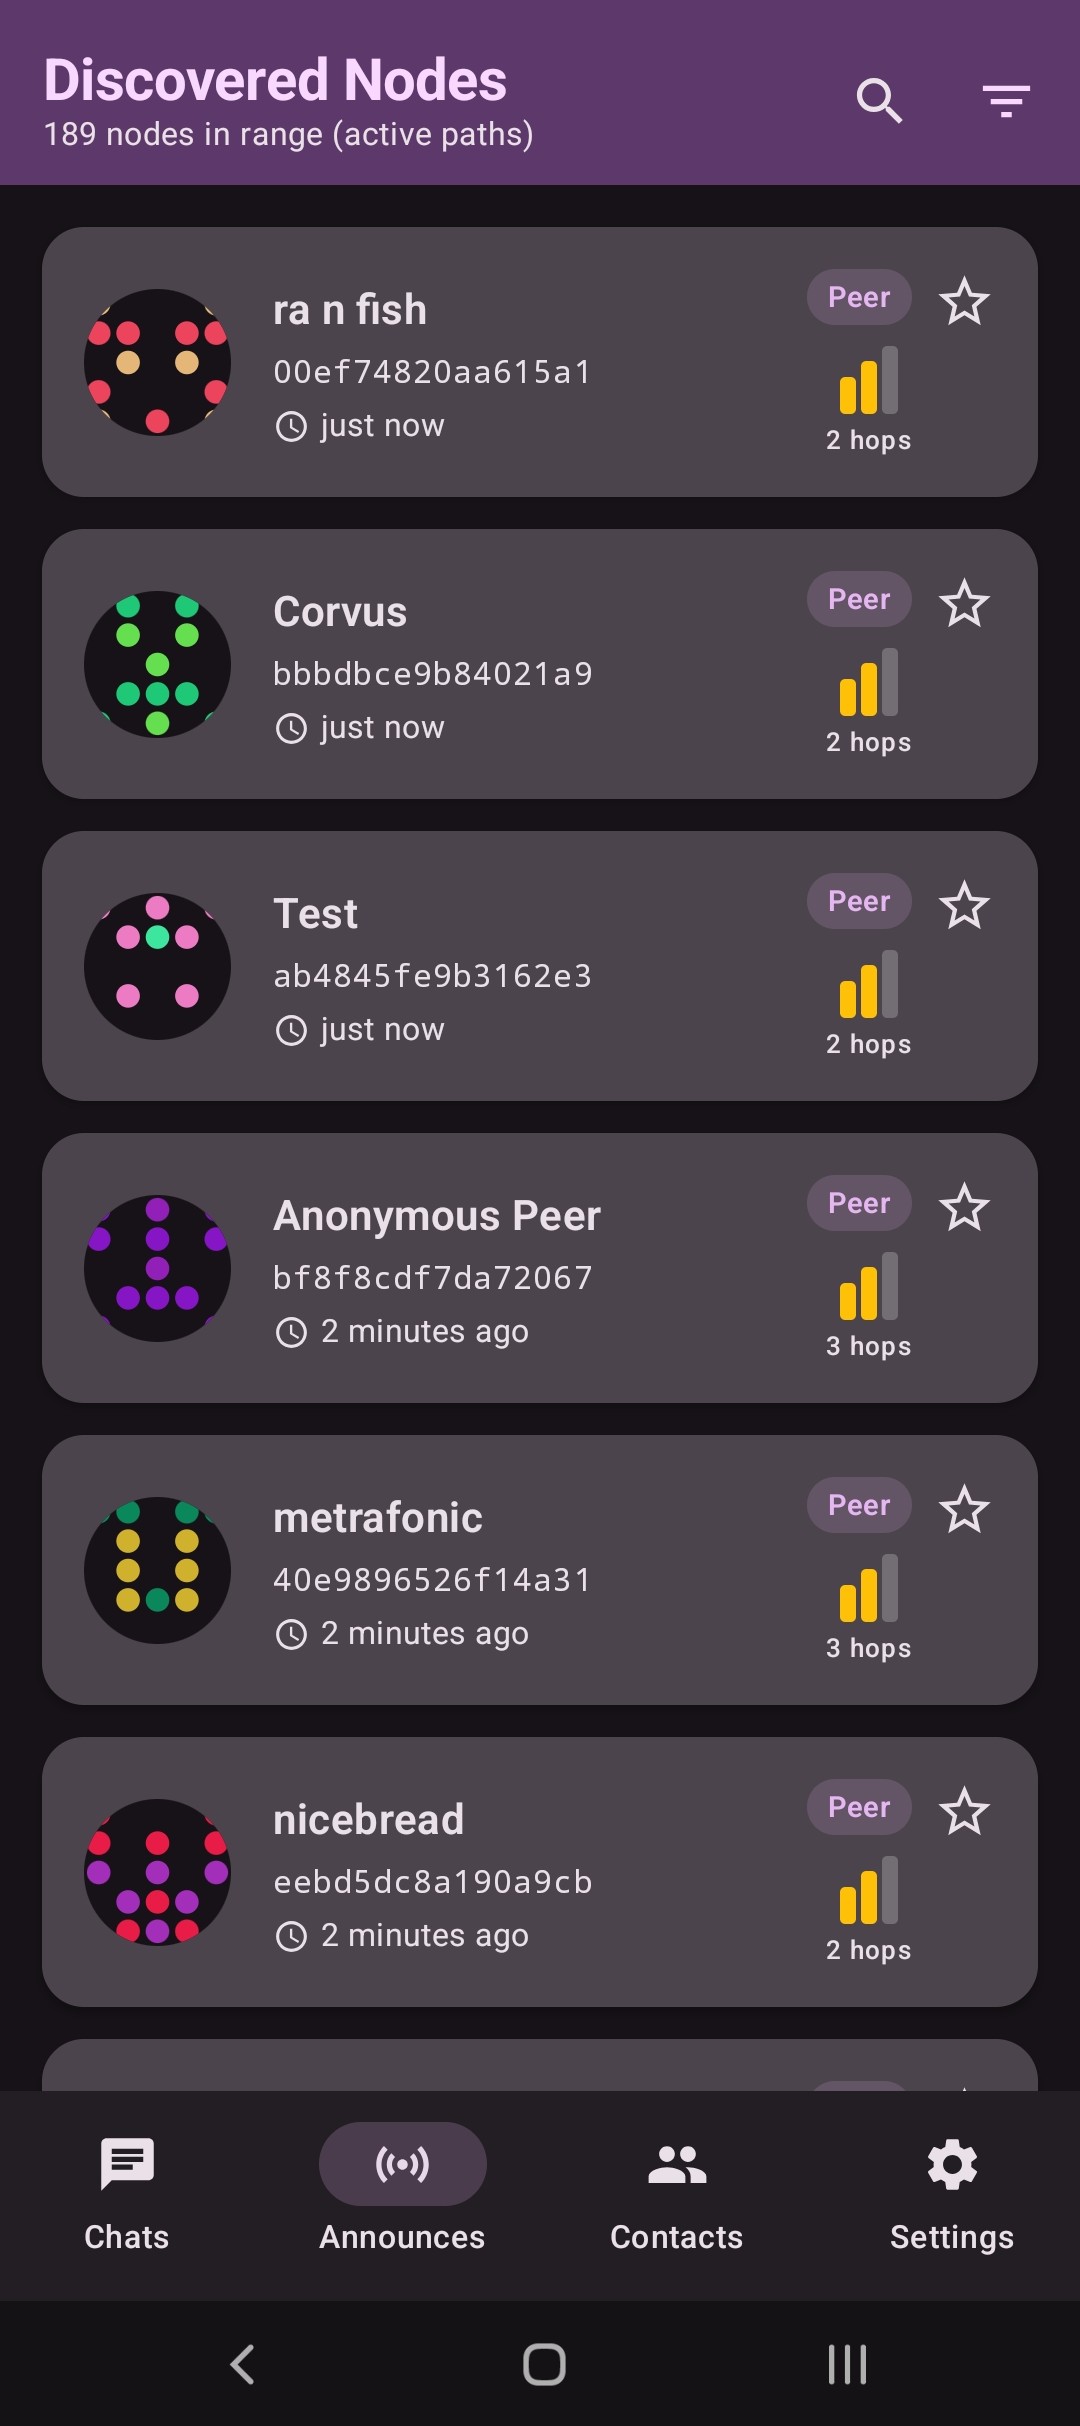 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
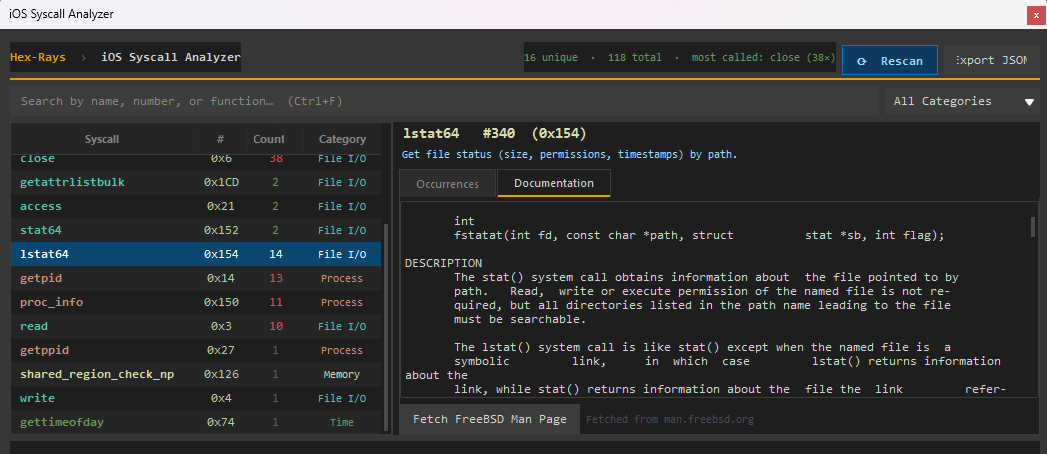 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 gadorach/vankyo-s30-bootloader-unlock
Vankyo MatrixPad S30 (Unisoc SC9863A) — Bootloader unlock via CVE-2022-38694 FDL1 method
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…