
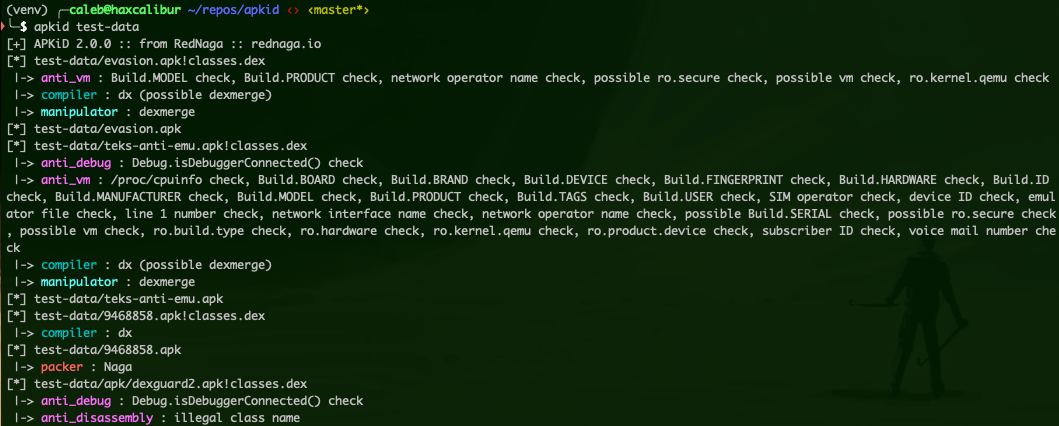
APKiD
 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
android-securitymalware-analysismobile-app-pentesting+3
2.6k26 days ago
rednaga/apkidAndroid Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
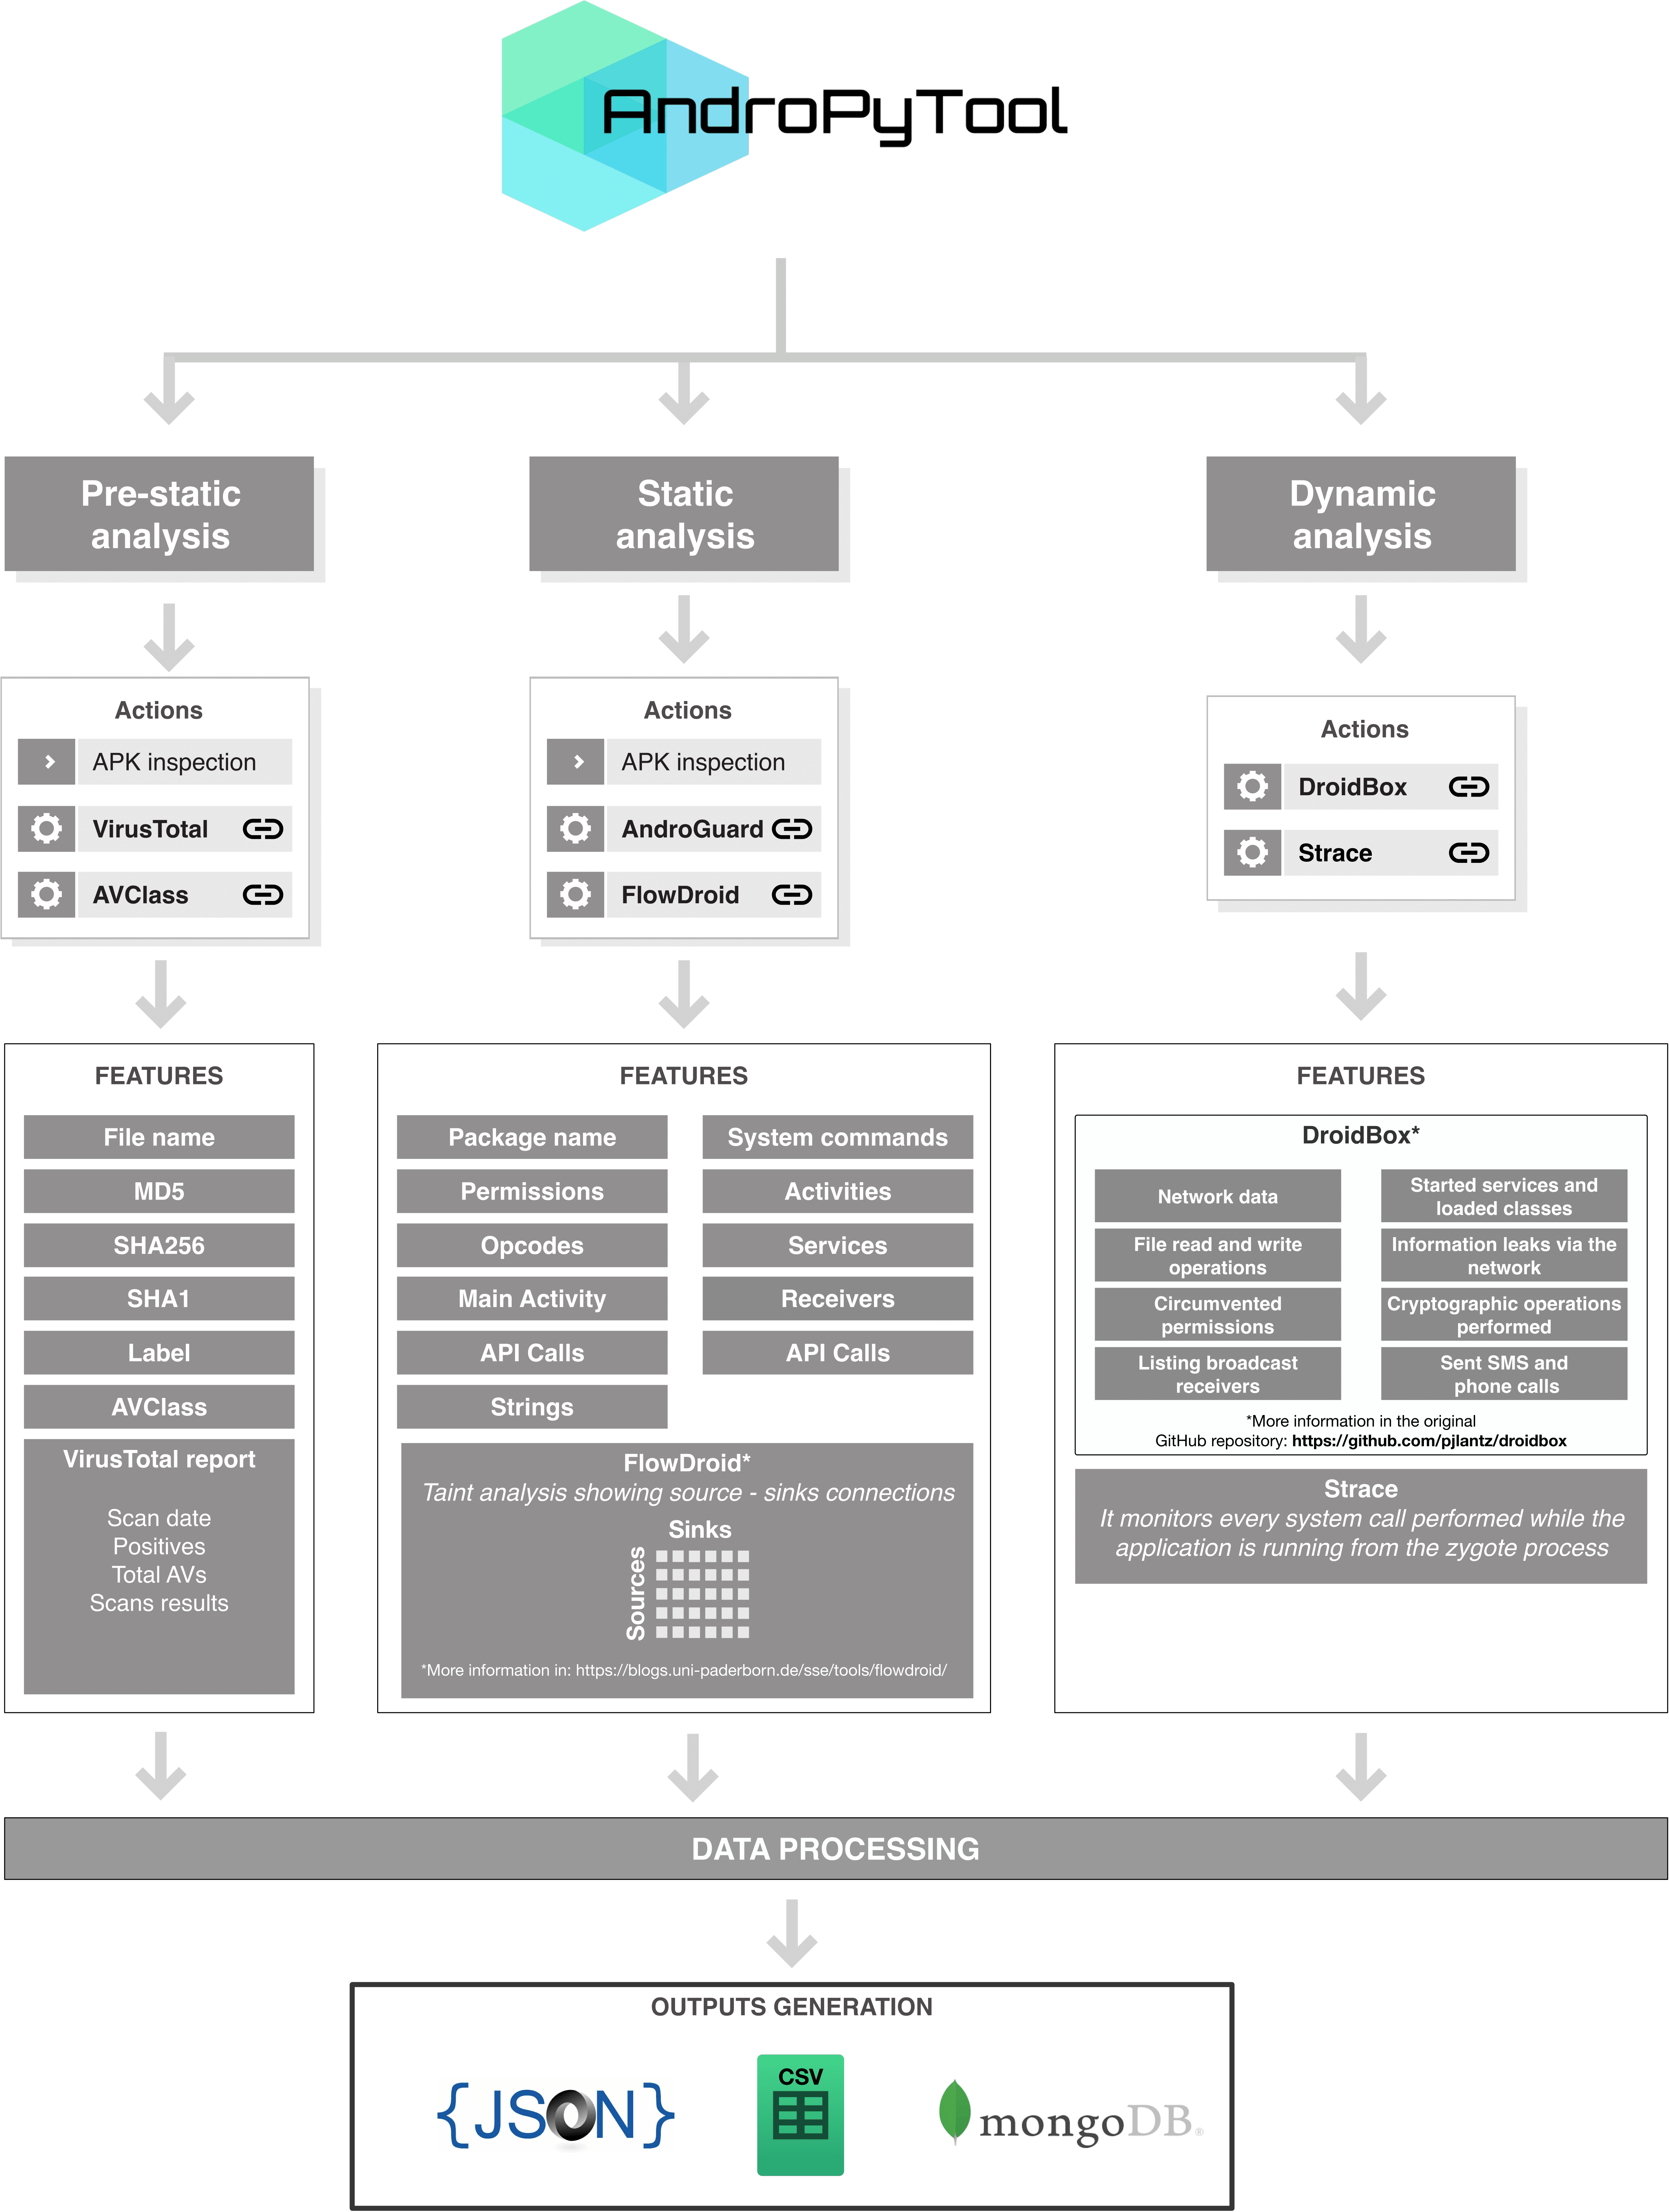 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 chefkissinc/inferno
Apple Silicon device emulator.
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
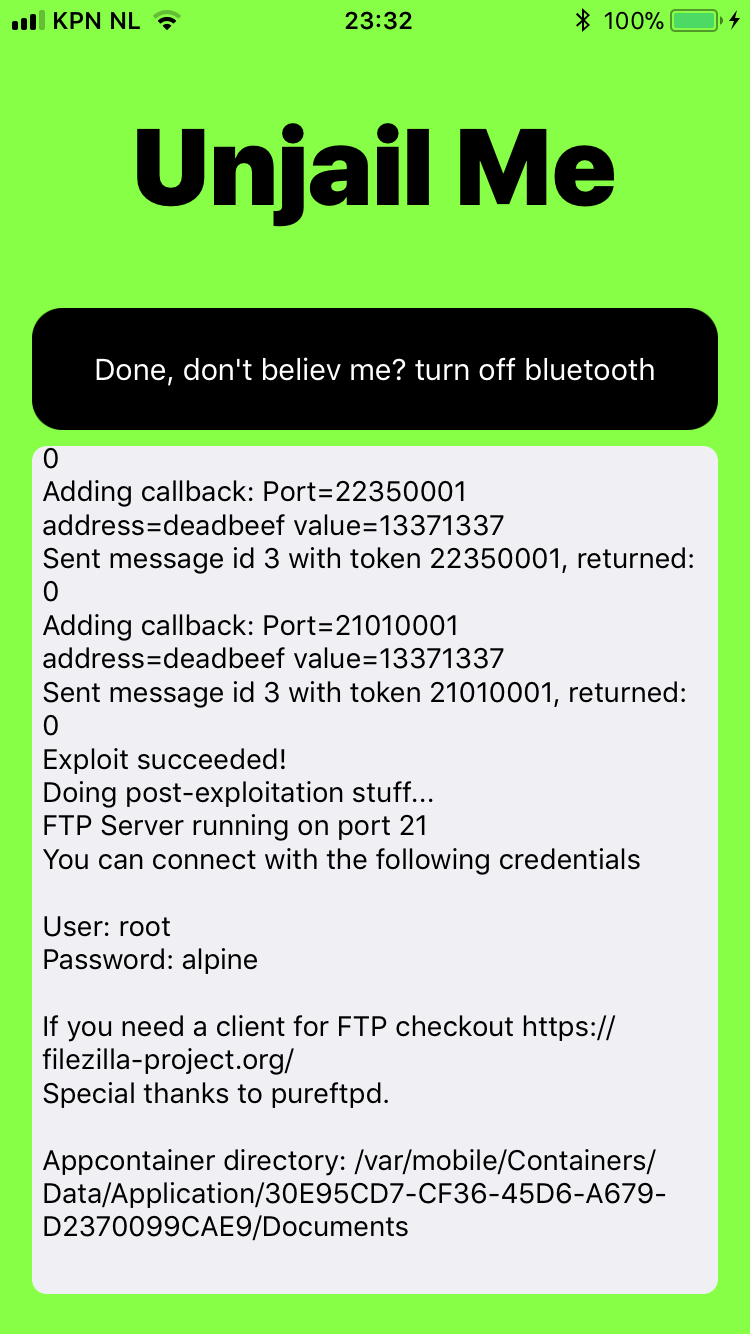 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 bmax121/apatch
The patching of Android kernel and Android system
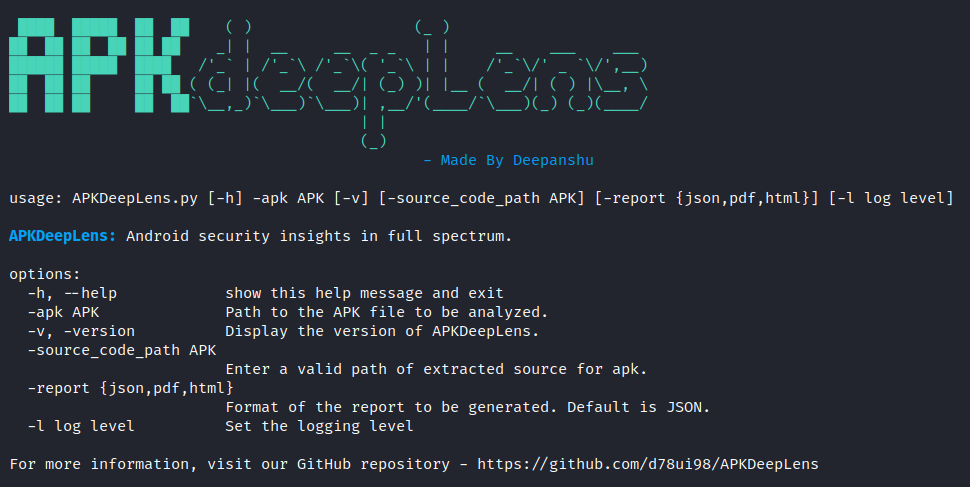 d78ui98/apkdeeplens
Android security insights in full spectrum.
 ifpdz/cve-2025-24104
Technical writeup of CVE-2025-24104: an iOS sandbox escape via symlink validation bypass in backup restoration, enabling arbitrary file reads outside…
 hanakim3945/bl_sbx
itunesstored & bookassetd sbx escape
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…