
FirmWire
 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
binary-analysisdebuggersdynamic-analysis-sandboxing+6
firmwire/firmwireFirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 chichou/vscode-frida
Unofficial frida extension for VSCode
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 leochen-coremind/vmpacker
ARM64 ELF Virtual Machine Protection System
 flankerhqd/vendor-android-cves
Collections of my POCs for android vendor CVEs
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 secmob/pocforcve-2015-1528
I'll submit the poc after blackhat
 star-sg/presentations
Curated collection of offensive security conference slide decks covering kernel and mobile exploitation, VM/container escapes, and…
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
 nccgroup/ble-replay
BLE-Replay is a Bluetooth Low Energy (BLE) peripheral assessment tool
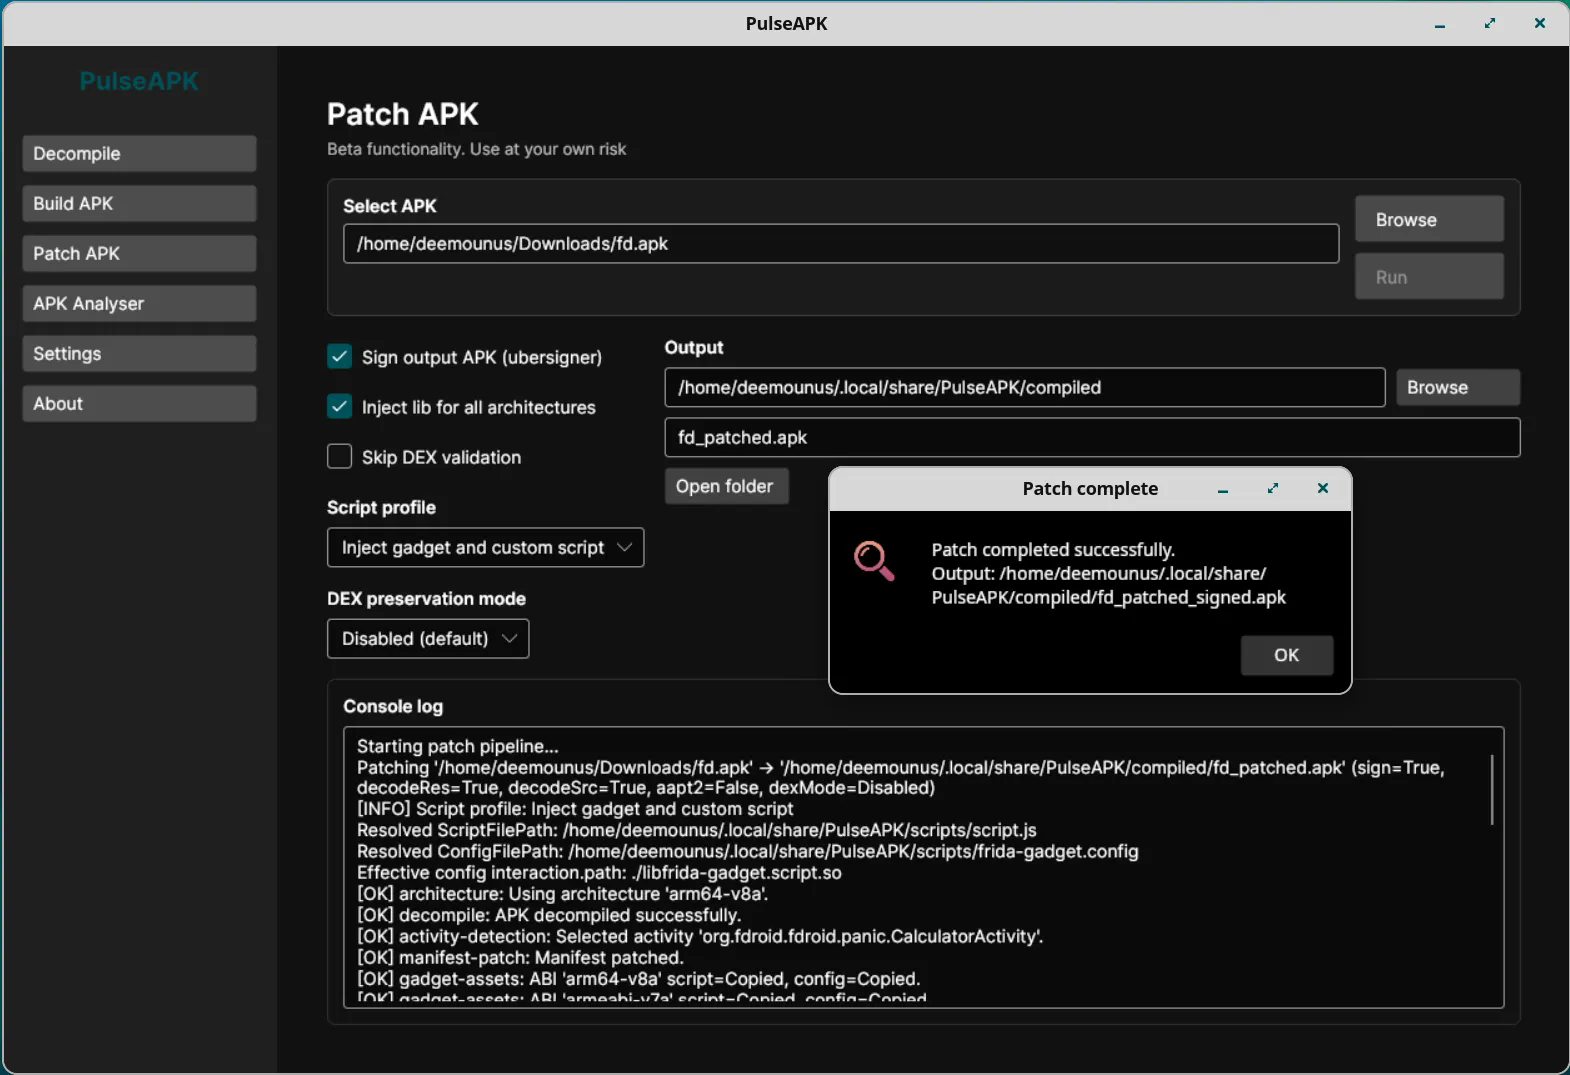 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…