
ArpCut
 fengguan/arpcut
Rooted Android app that scans LAN devices and cuts or restores their network access via ARP spoofing, with OUI vendor lookup, whitelist, and…
android-securityinformation-gatheringmobile-security+5
fengguan/arpcutRooted Android app that scans LAN devices and cuts or restores their network access via ARP spoofing, with OUI vendor lookup, whitelist, and…

 alltechdev/mtk-imei-switcheroo
Read and write IMEI records and WiFi/Bluetooth addresses in MediaTek NVRAM files or partition images. Includes interactive ADB tools for rooted…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 mbeweoo/flash-exploit-defense-system
Comprehensive multi-layer defense system against Adobe Flash CVE exploits (CVE-2012-0754, CVE-2015-xxxx, CVE-2016-xxxx, CVE-2018-xxxx) with browser,…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
 n0c71v3x/cve-2026-78745
Discloses CVE-2026-78745, a remote code execution vulnerability in Android Debug Bridge (ADB) on HiDPT devices, allowing root-level arbitrary code…
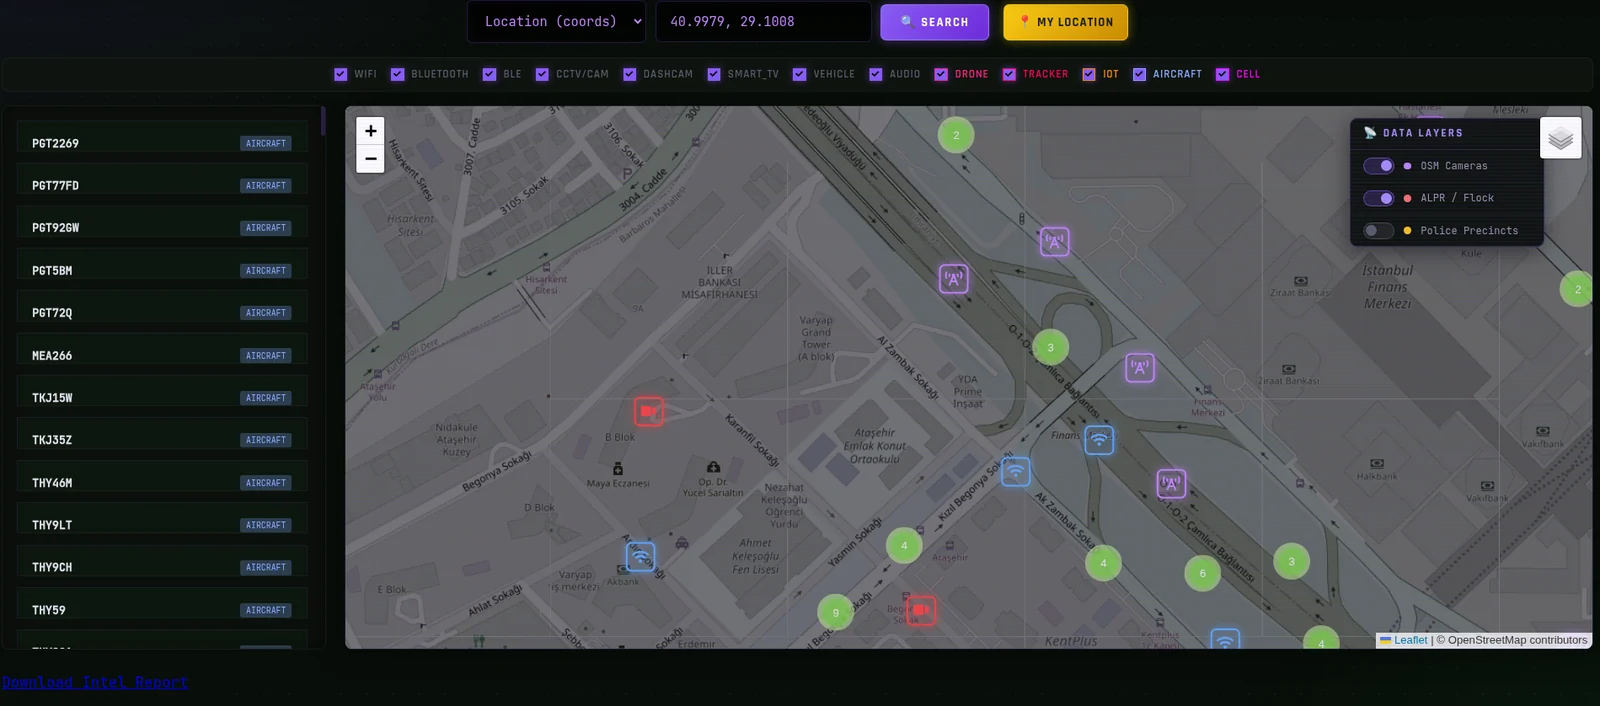 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 rifting/unrestrictedusercreator
Simple script to add a new, unrestricted user on devices with Family Link by abusing CVE-2025-32324 (pre September patch)
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…