
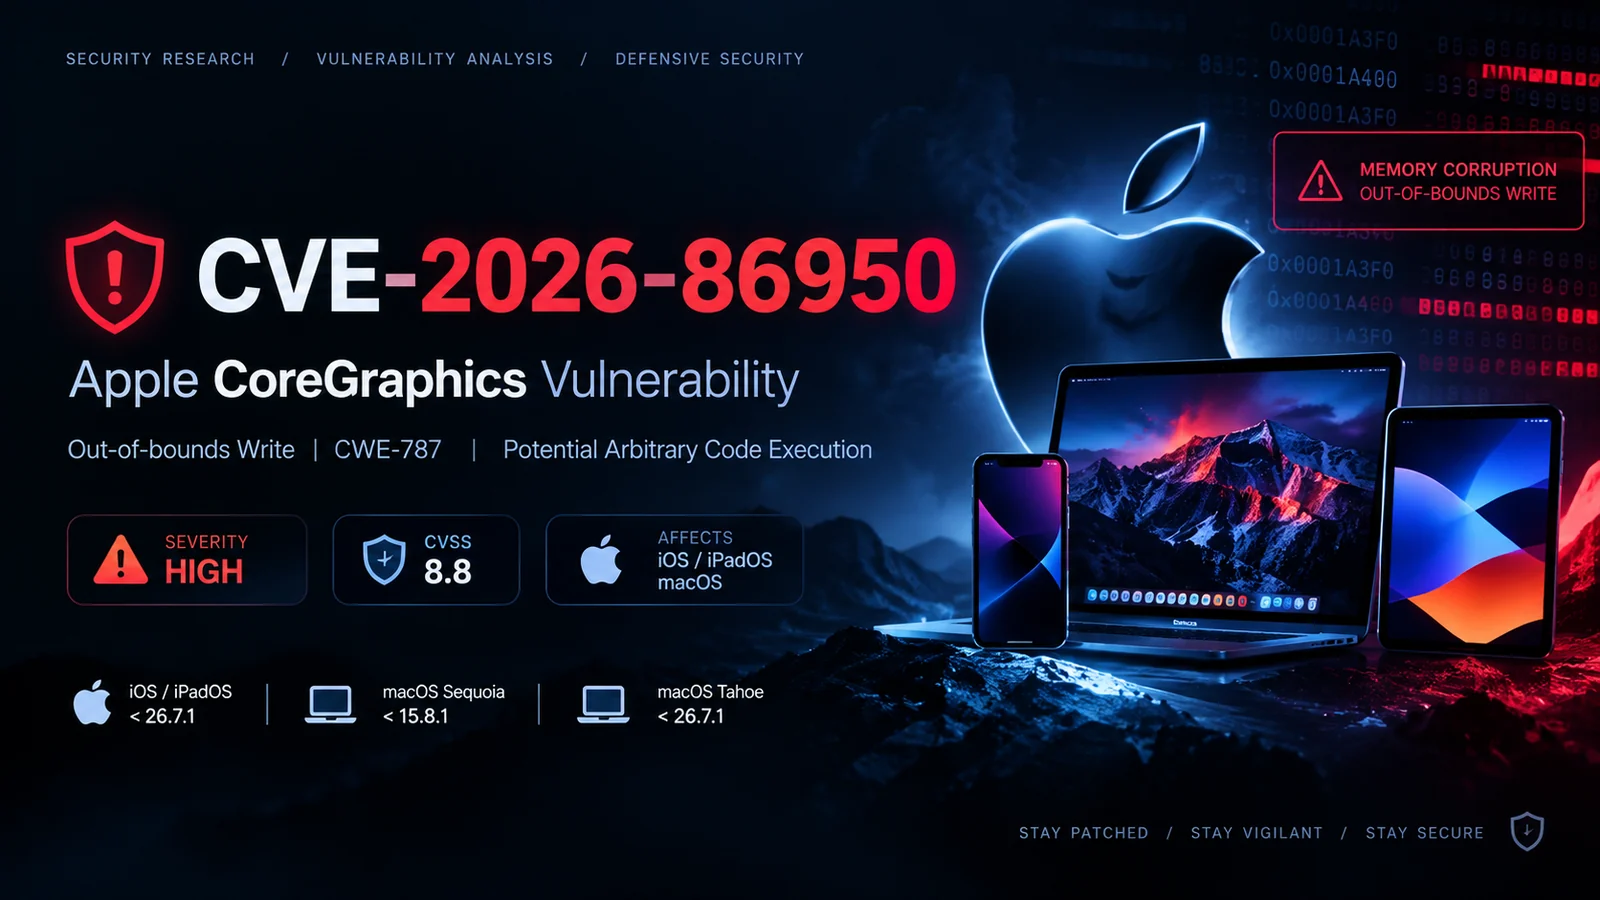
CVE-2026-86950
 0xblackash/cve-2026-86950
Defensive research documentation for CVE-2026-86950, an Apple CoreGraphics out-of-bounds write, covering vulnerability triage, affected versions,…
defensive-toolseducationincident-response+4
0xblackash/cve-2026-86950Defensive research documentation for CVE-2026-86950, an Apple CoreGraphics out-of-bounds write, covering vulnerability triage, affected versions,…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 muhamadrifkii/cve-2026-43499-poco-x3-gt
Proof-of-concept exploit targeting CVE-2026-43499 on the POCO X3 GT Android device, demonstrating the vulnerability and its impact.
 mbeweoo/flash-exploit-defense-system
Comprehensive multi-layer defense system against Adobe Flash CVE exploits (CVE-2012-0754, CVE-2015-xxxx, CVE-2016-xxxx, CVE-2018-xxxx) with browser,…
 mobilehackinglab/cve-2026-28576-poc
Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…
 n0c71v3x/cve-2026-78745
Discloses CVE-2026-78745, a remote code execution vulnerability in Android Debug Bridge (ADB) on HiDPT devices, allowing root-level arbitrary code…
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 bytev0rtex/cve-2026-65330
Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
 devtint/cve-2026-0073
Weaponized proof-of-concept for CVE-2026-0073, an Android adbd authentication bypass enabling zero-click remote root access via Wireless ADB, with…
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…
 enfilade-labs/cve-2026-20687-applejpegdriver-uaf
CVE-2026-20687: AppleJPEGDriver startDecoder Timeout UAF — iOS/macOS kernel vulnerability leading to deferred panic (A19 Pro, iOS 26.3 RC)
 enfilade-labs/cve-2026-20637-applesepkeystore-uaf
CVE-2026-20637: AppleSEPKeyStore Use-After-Free — iOS/macOS kernel vulnerability (patched in 26.4)
 demining/pixnapping-attack-on-android
Pixnapping Attack: Compromising private keys and seed phrases through vulnerability CVE-2025-48561 represents a new critical threat to the Bitcoin…