Android-Forensics-References

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

Android Logs Events And Protobuf Parser

iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

Free hands-on digital forensics labs for students and faculty

Reverse engineering and pentesting for Android applications

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.

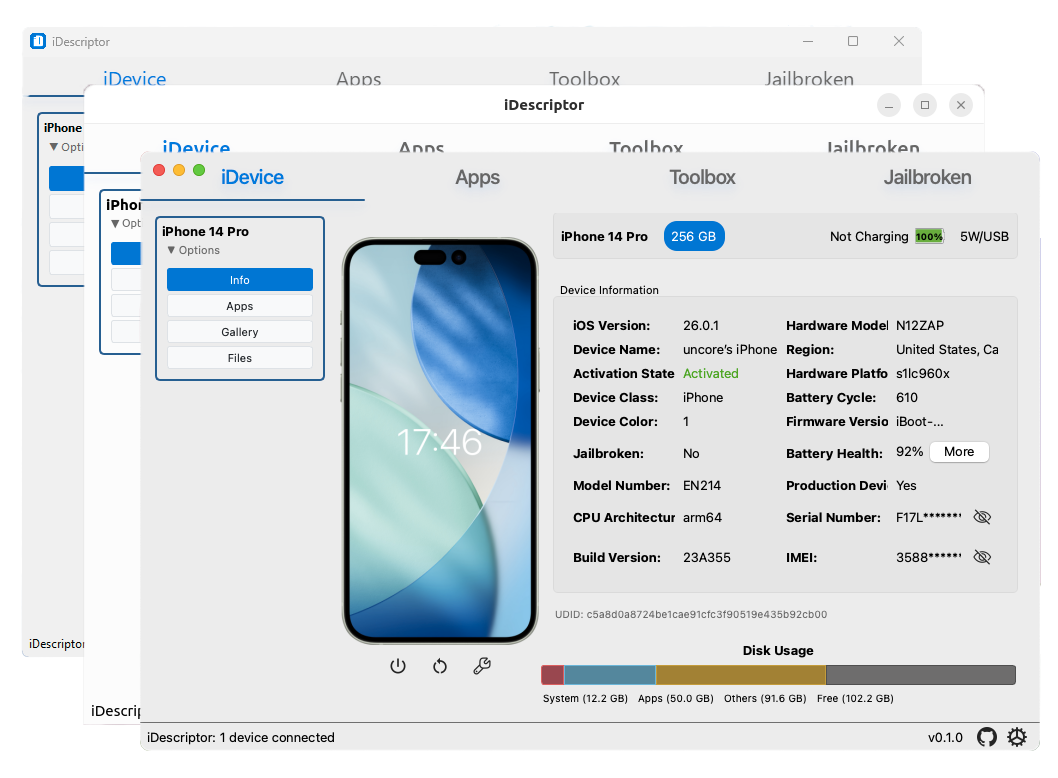
privacy-first, open-source and free idevice management tool written in Rust and Qt

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

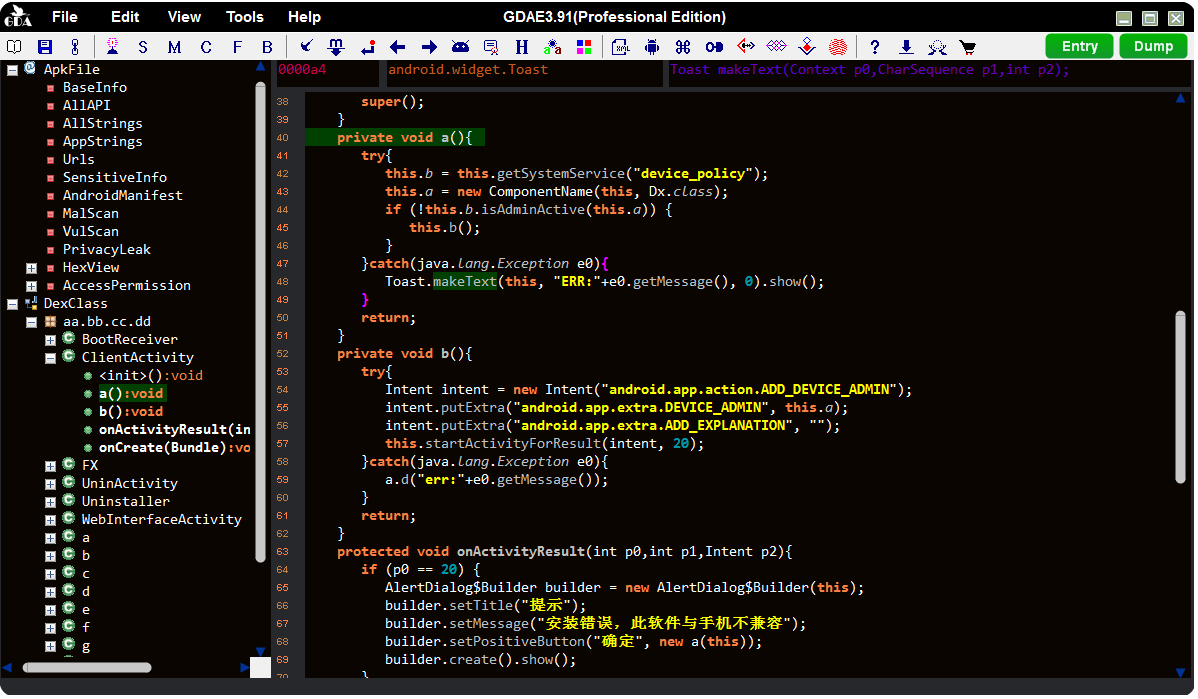
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

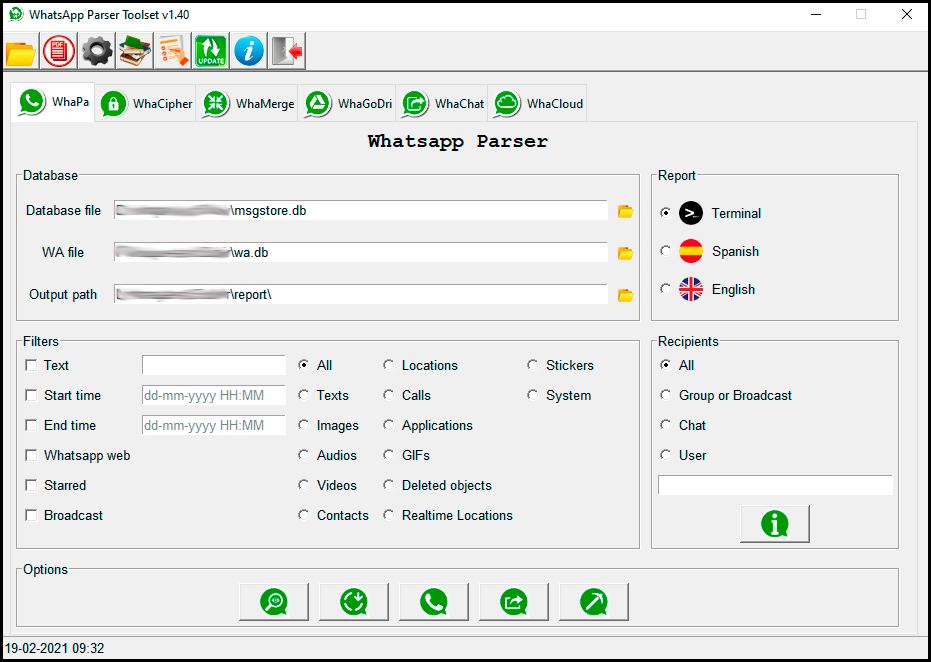
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…