

IPED
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k
sepinf-inc/ipedIPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
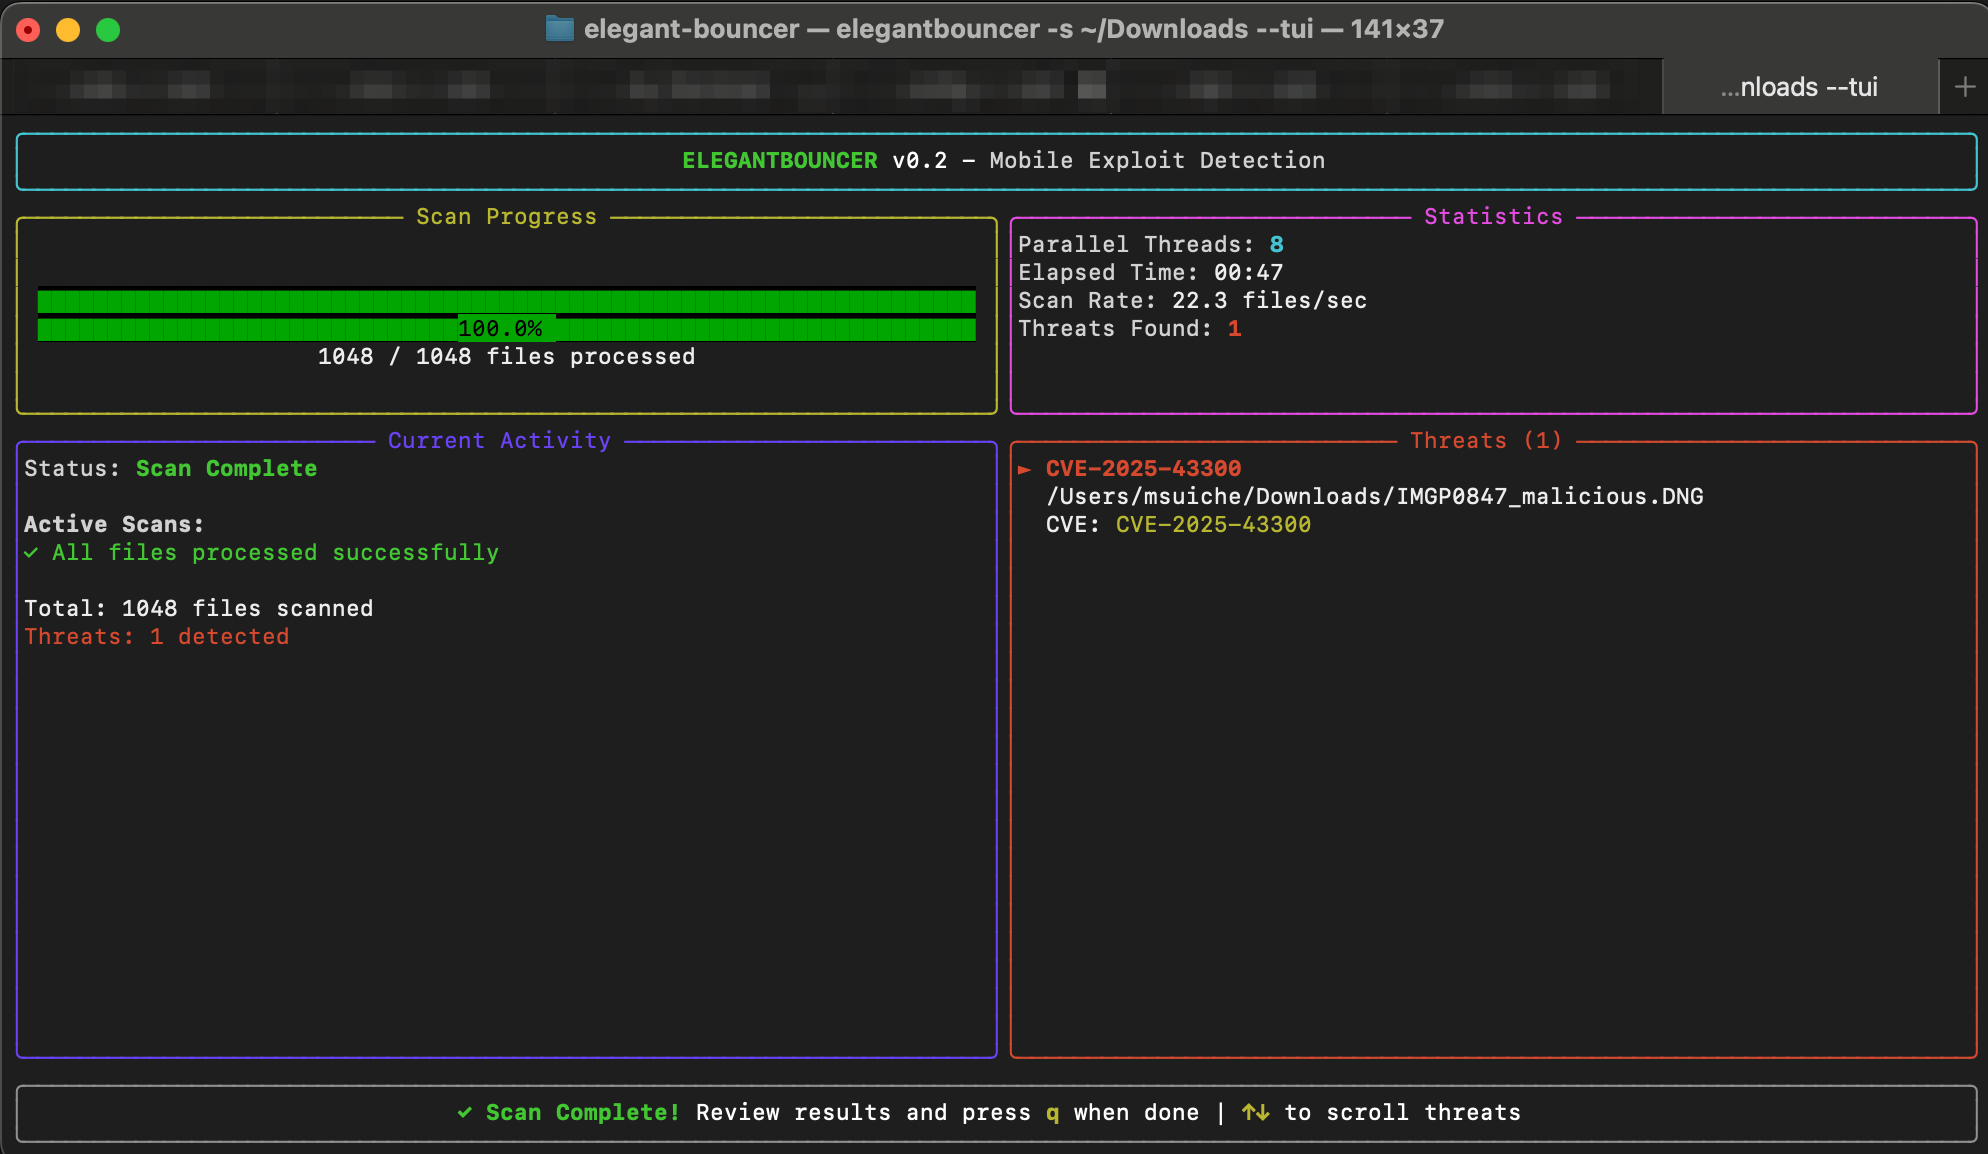 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
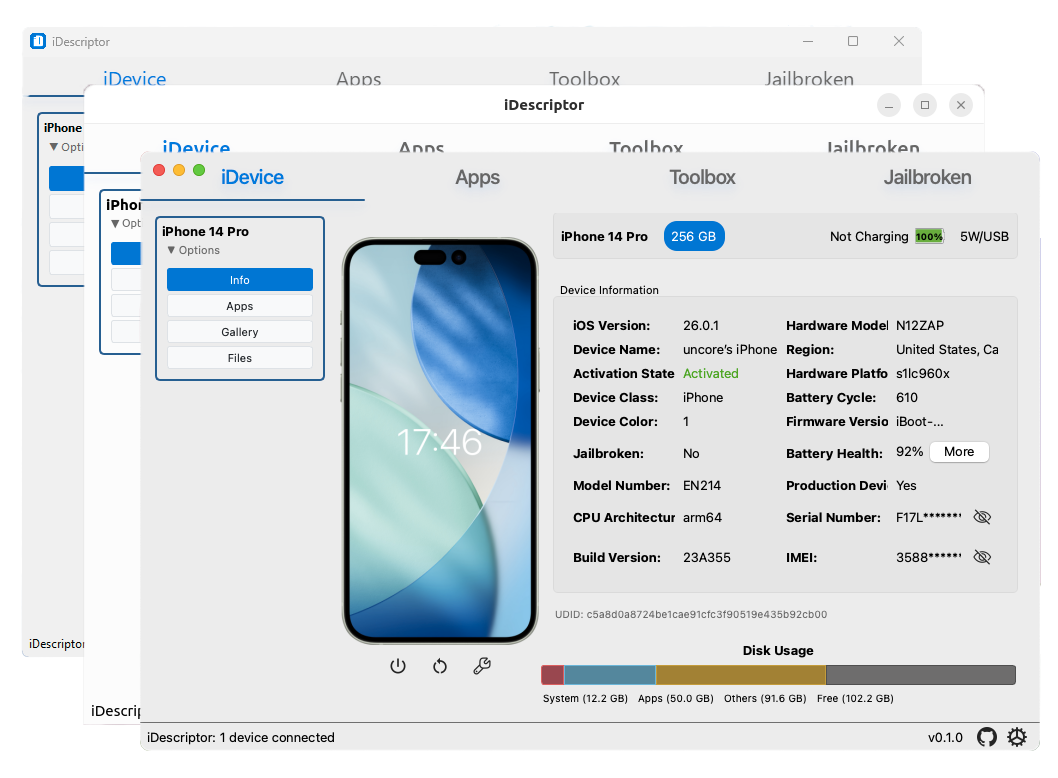 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
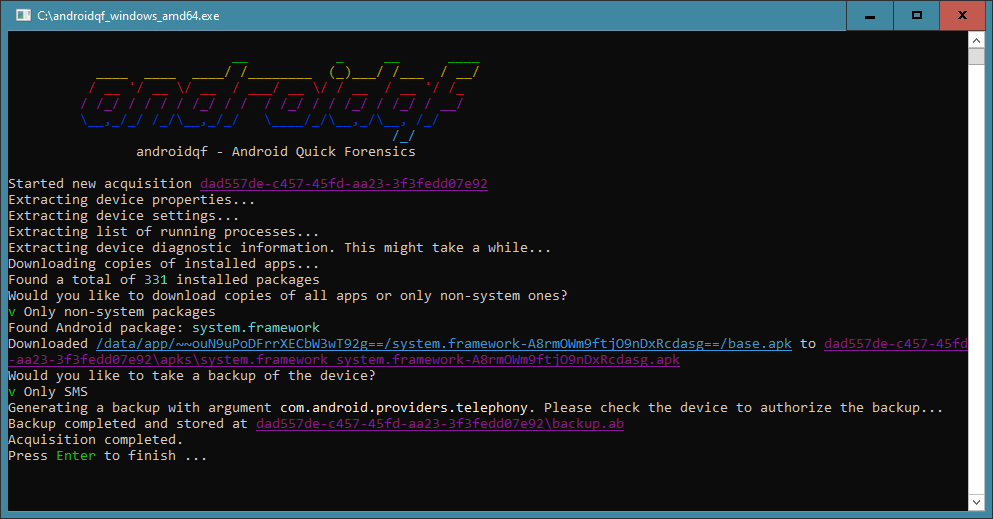 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
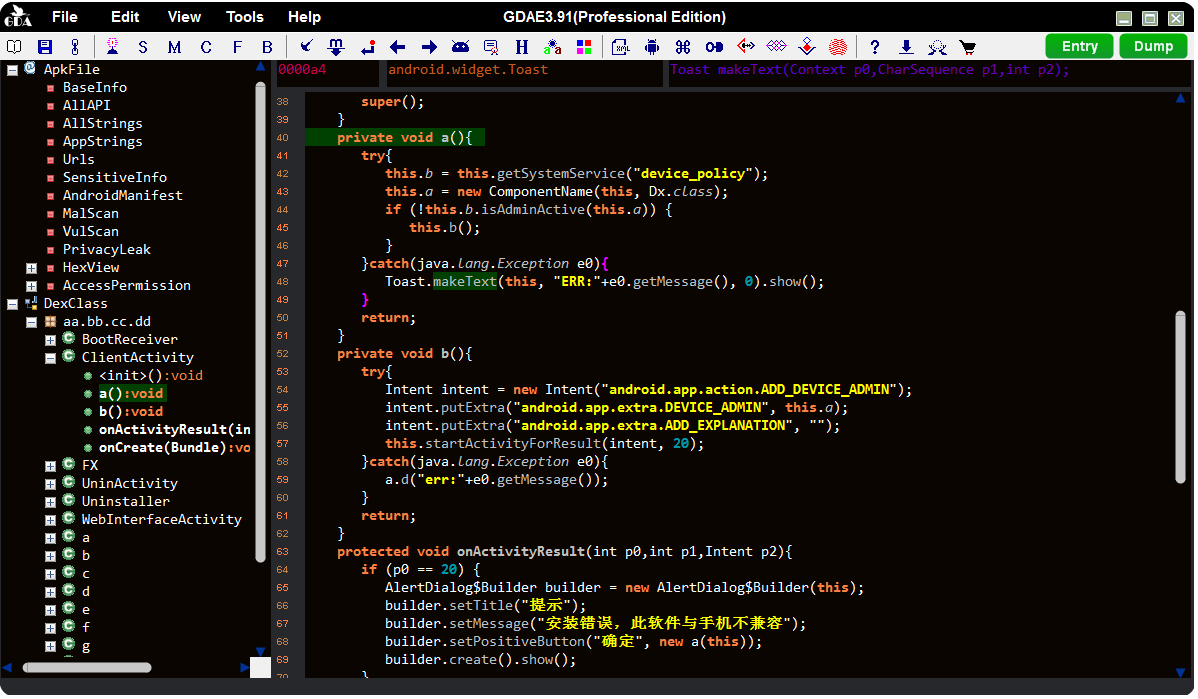 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
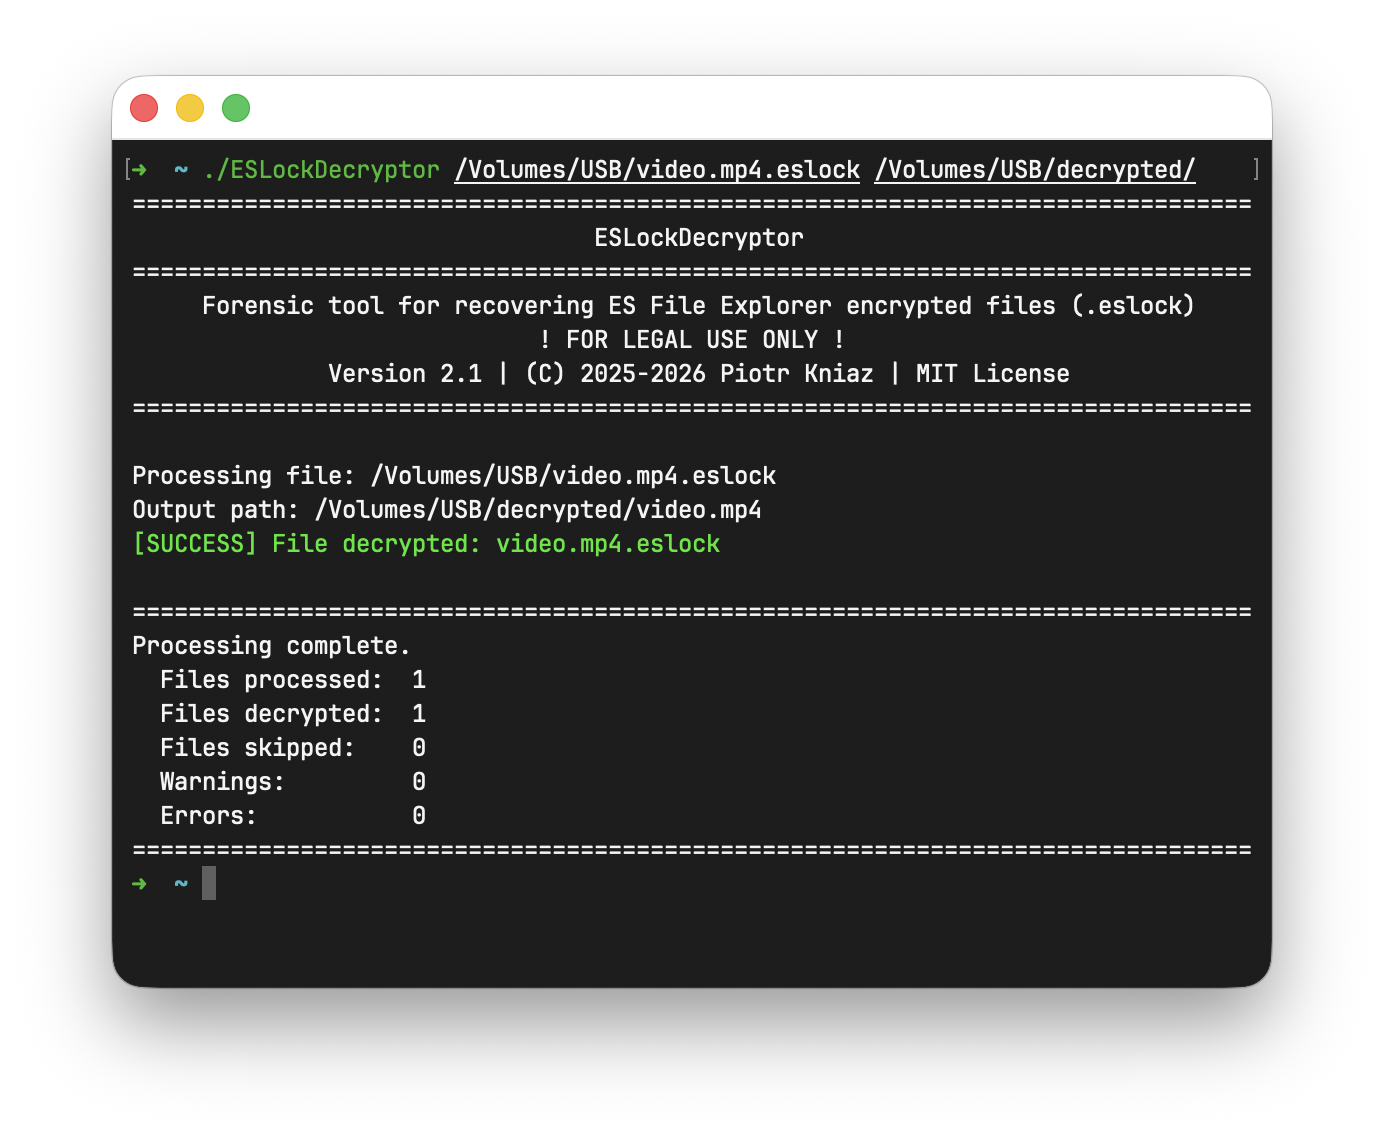 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)