

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
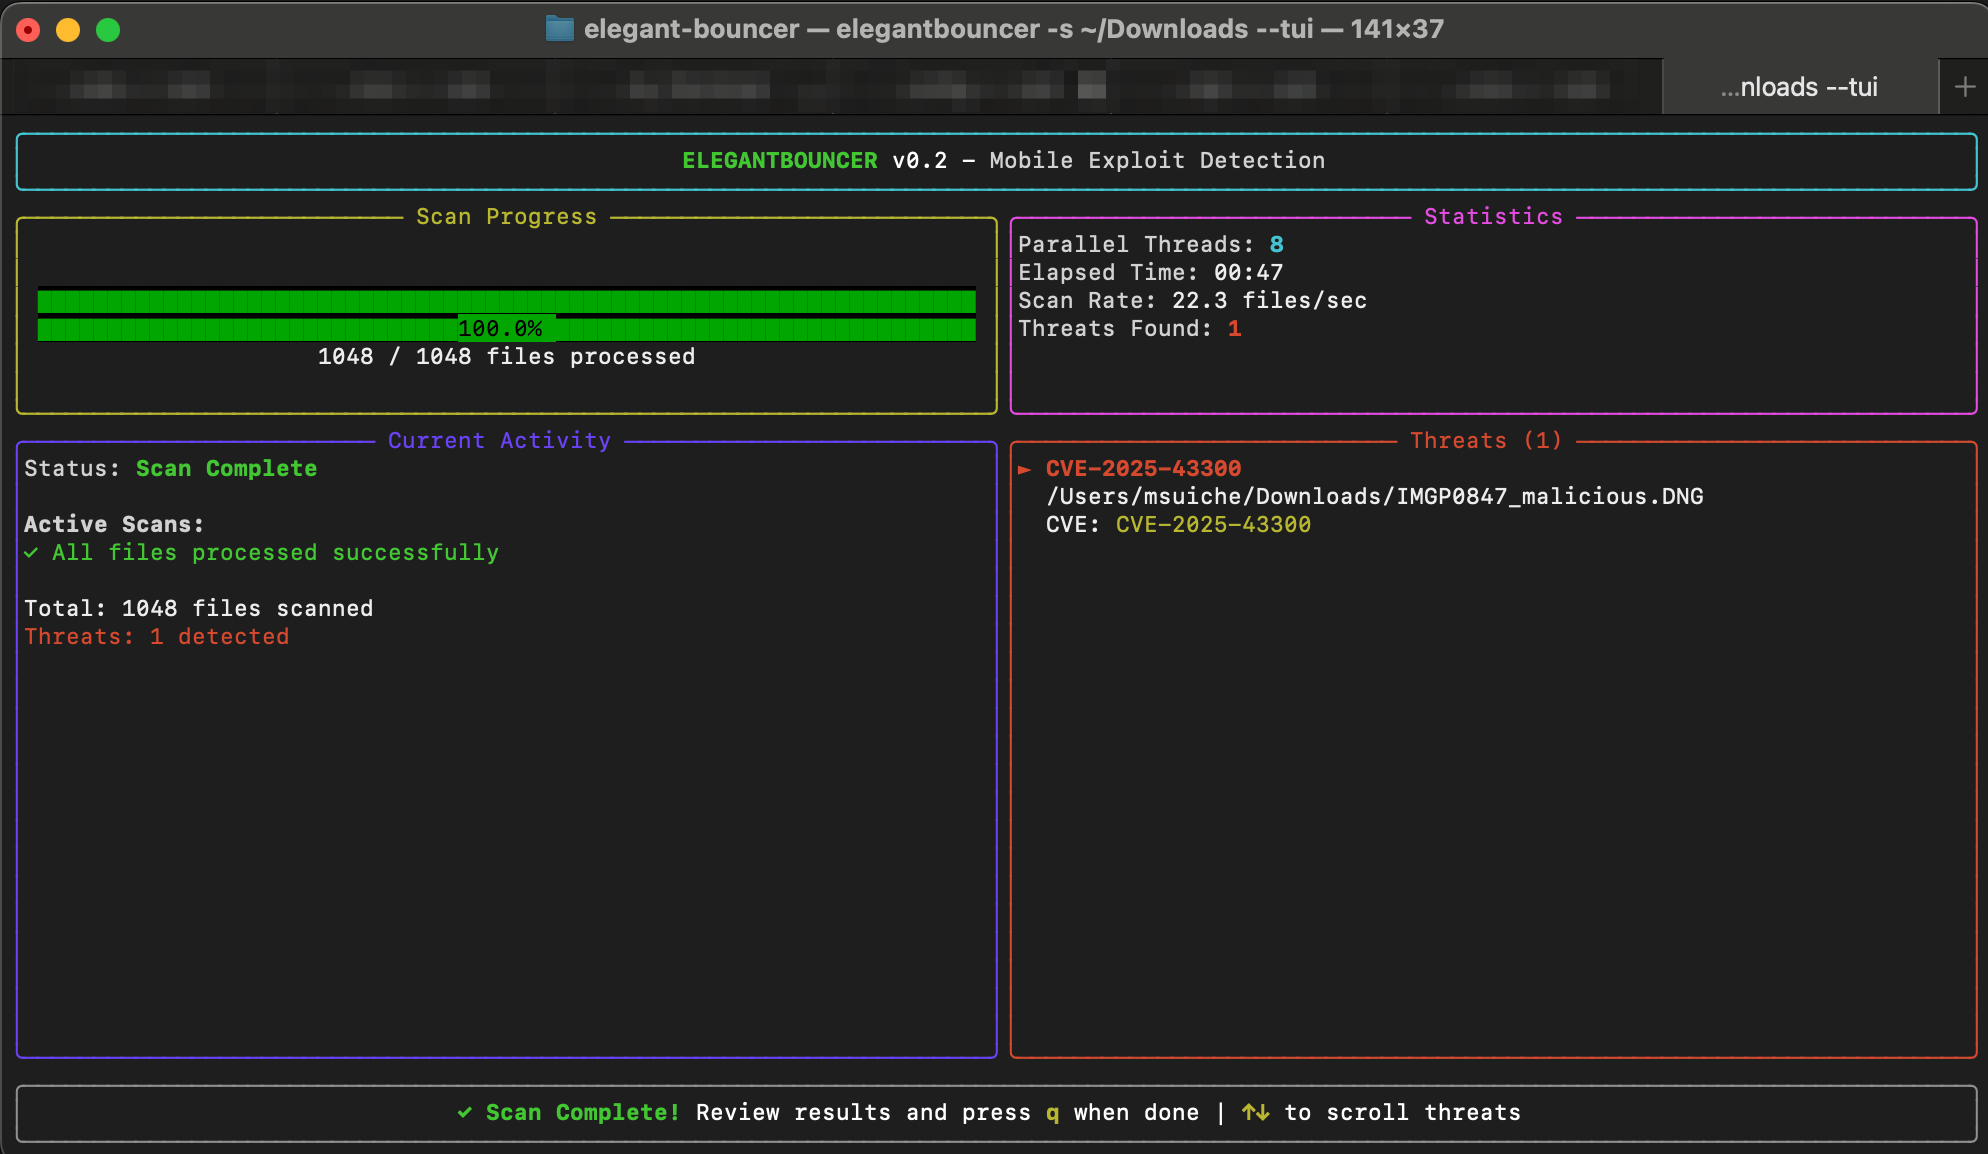 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
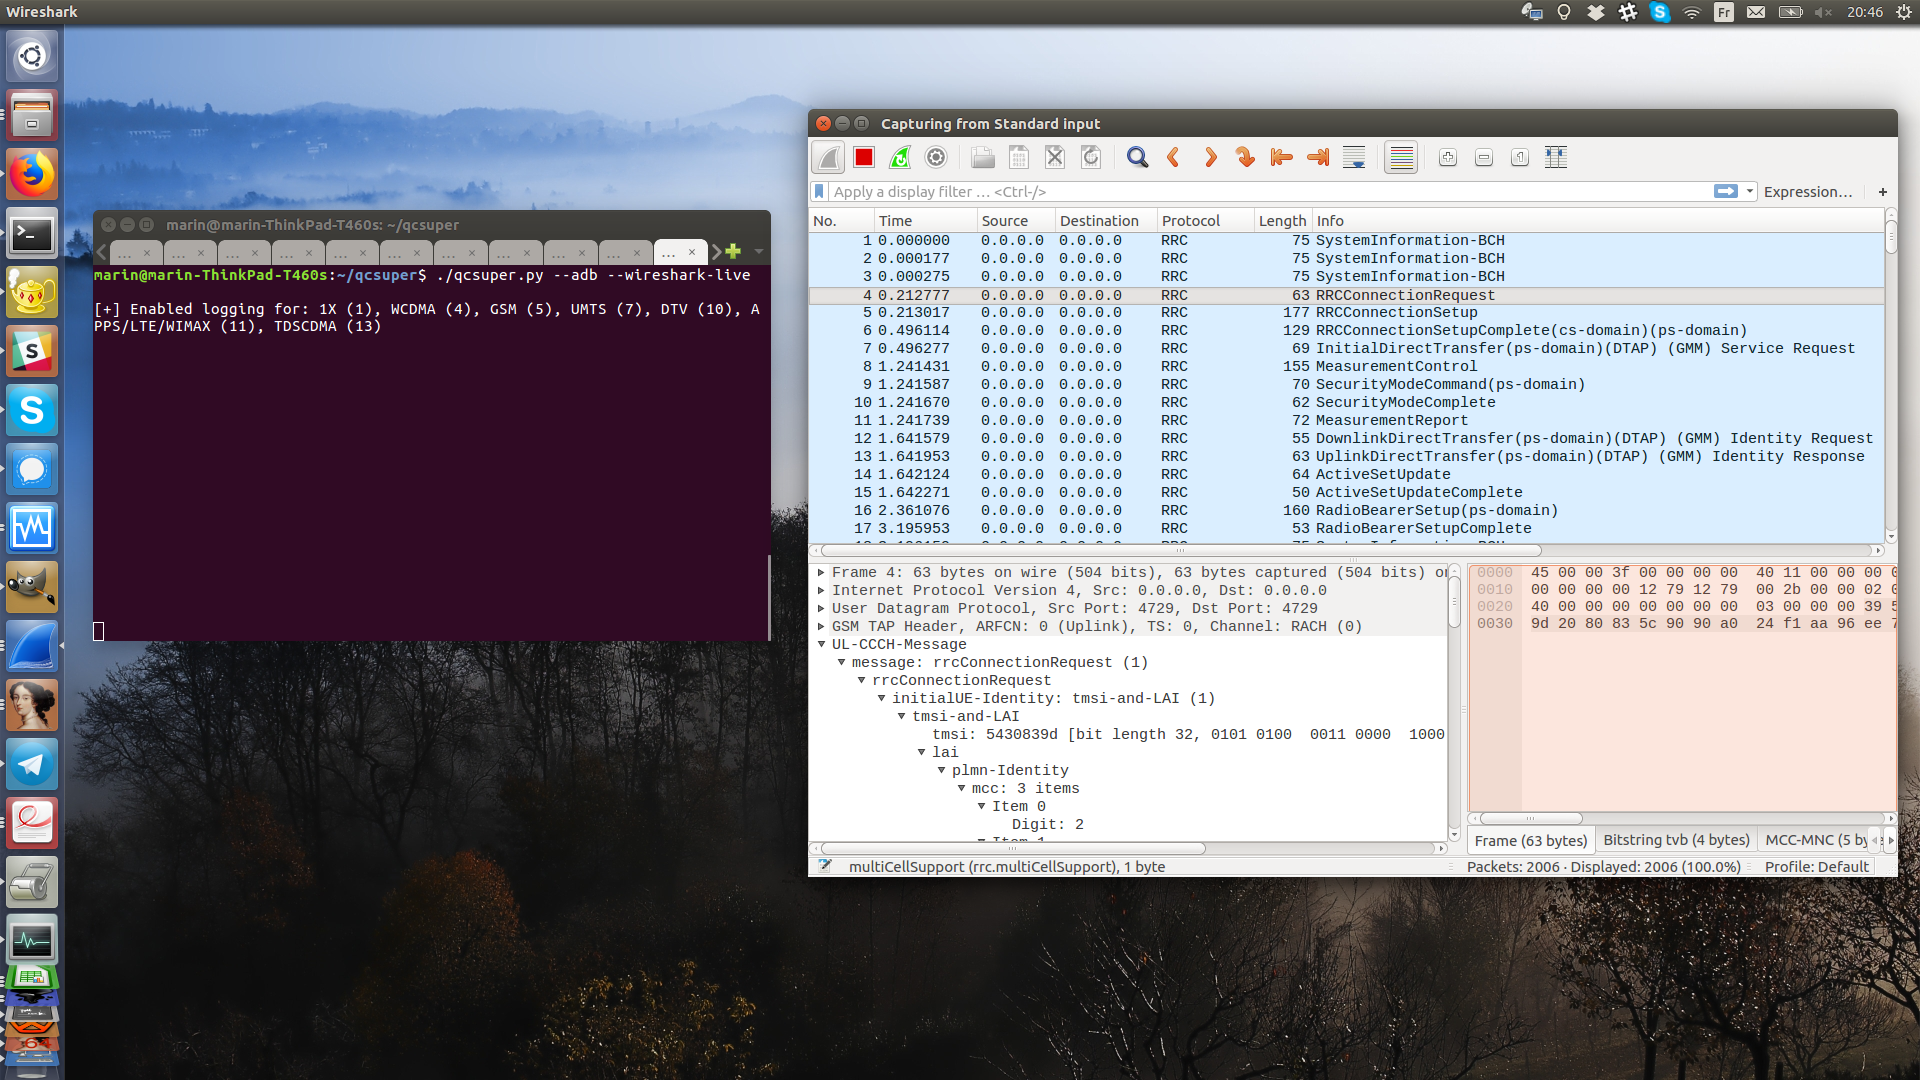 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS