
Zero-Breach-Toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.

Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.

Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…

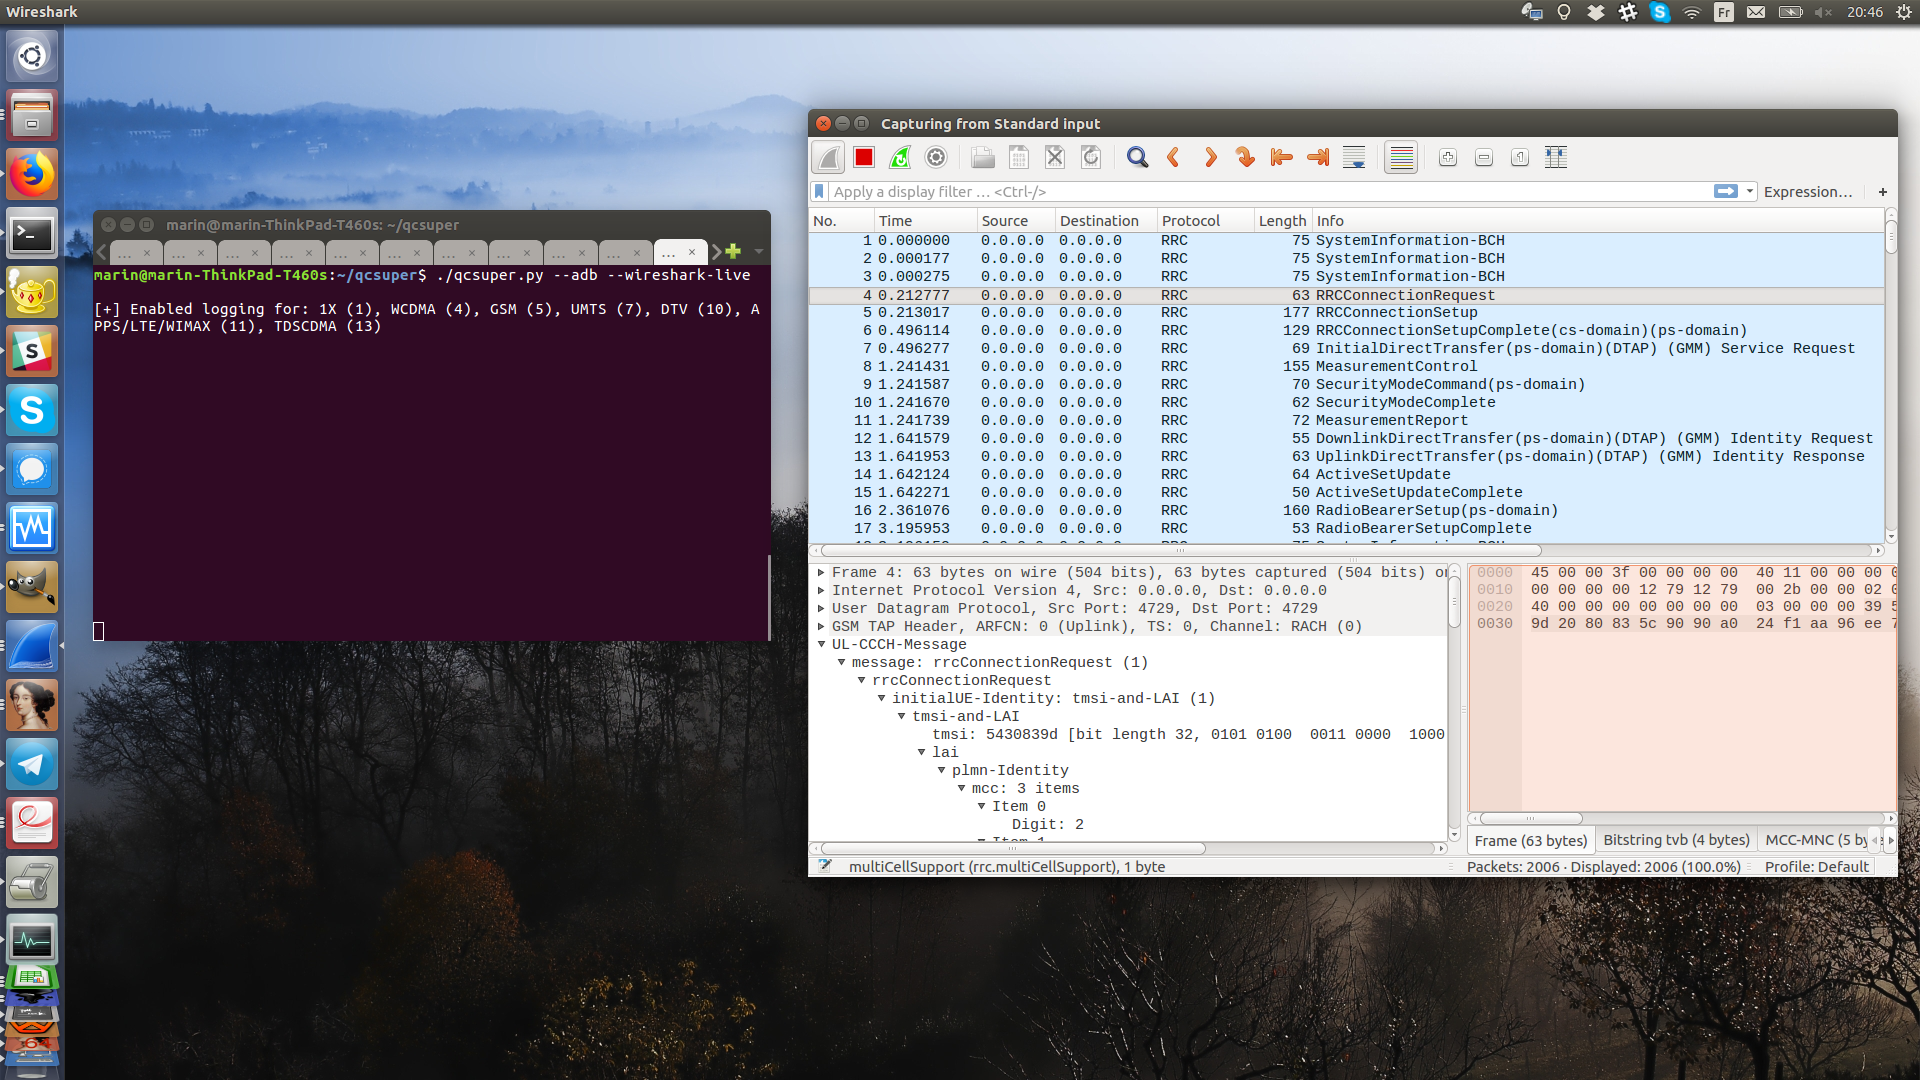
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

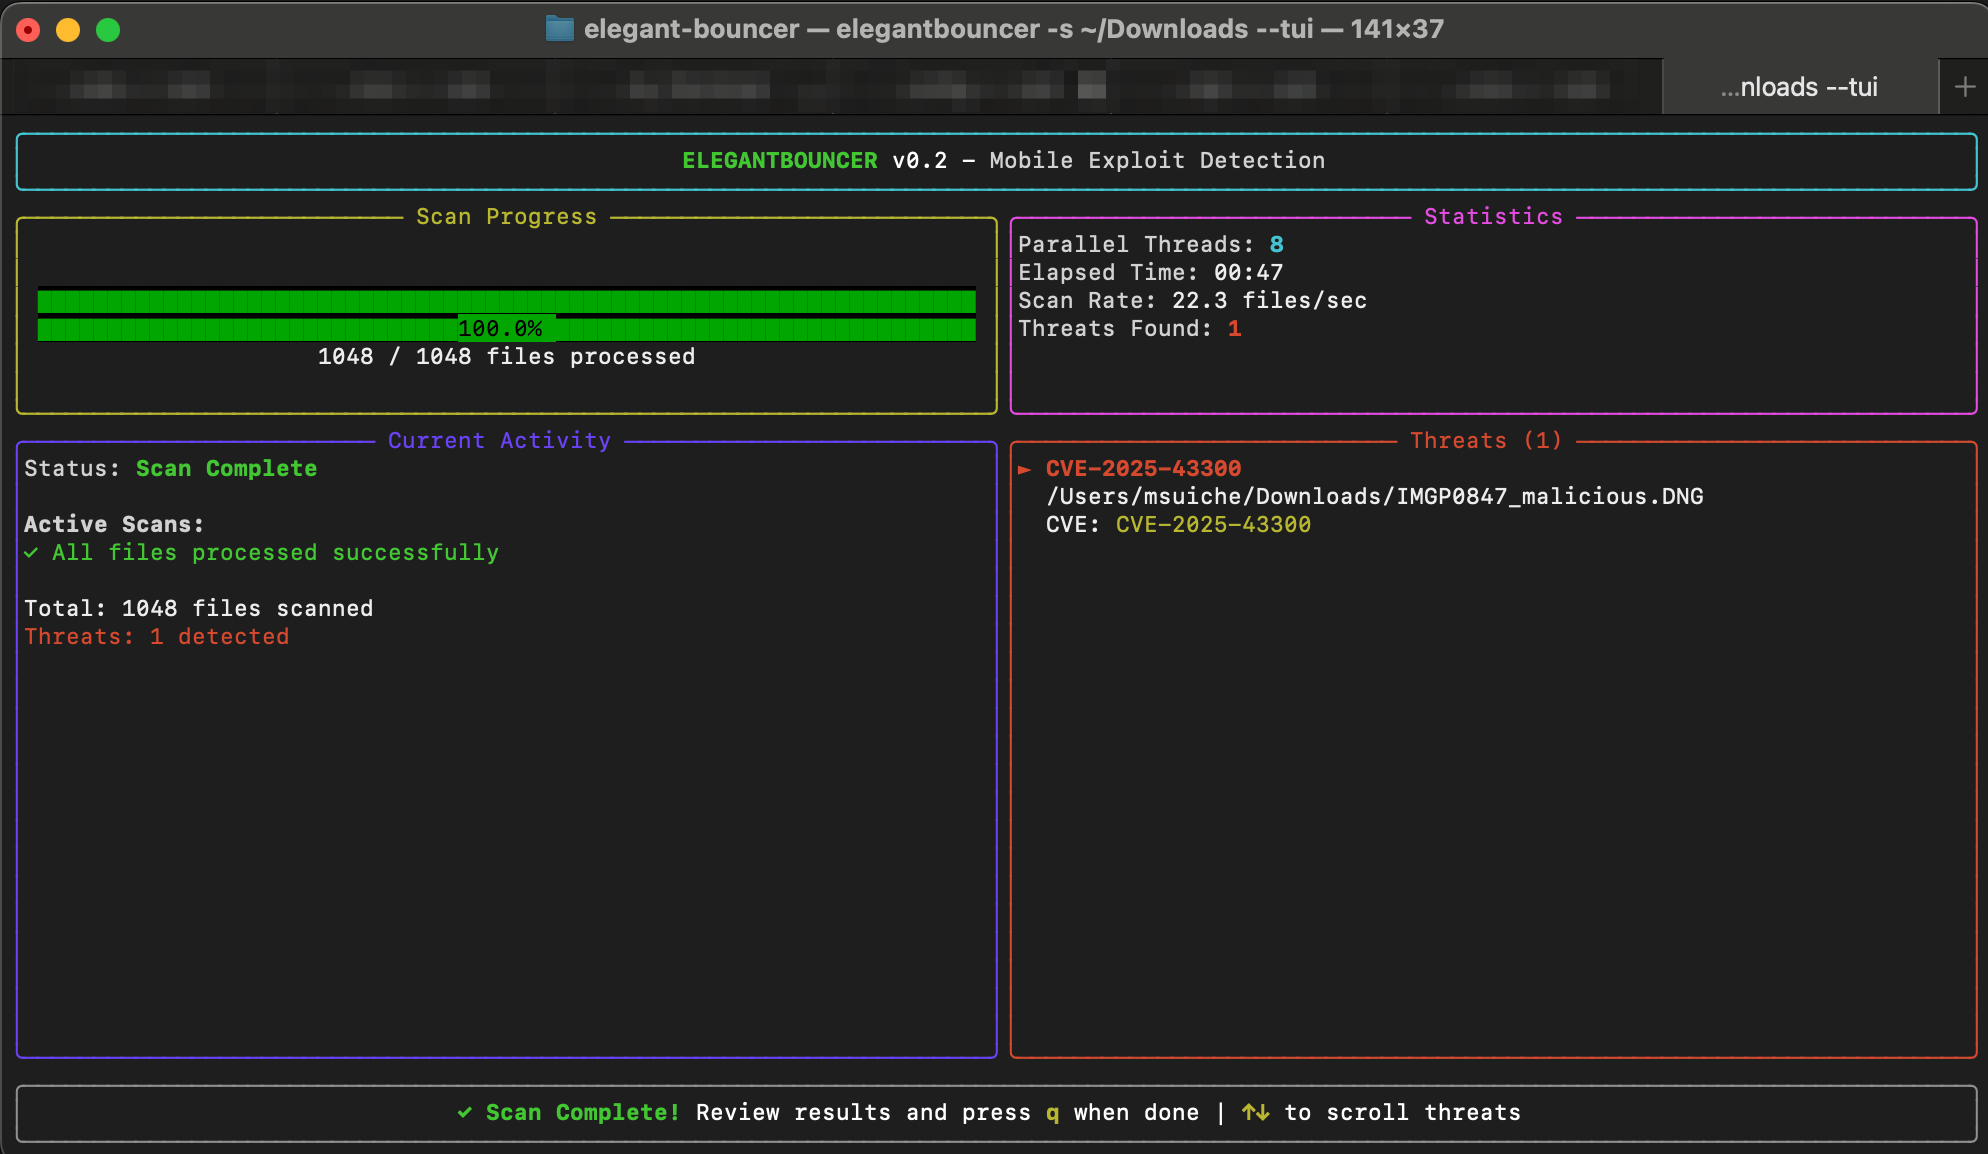
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…

Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.

Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)


Linux Distro for Mobile Security, Malware Analysis, and Forensics

This is the development tree. Production downloads are at:

Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.