Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

Android Logs Events And Protobuf Parser

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

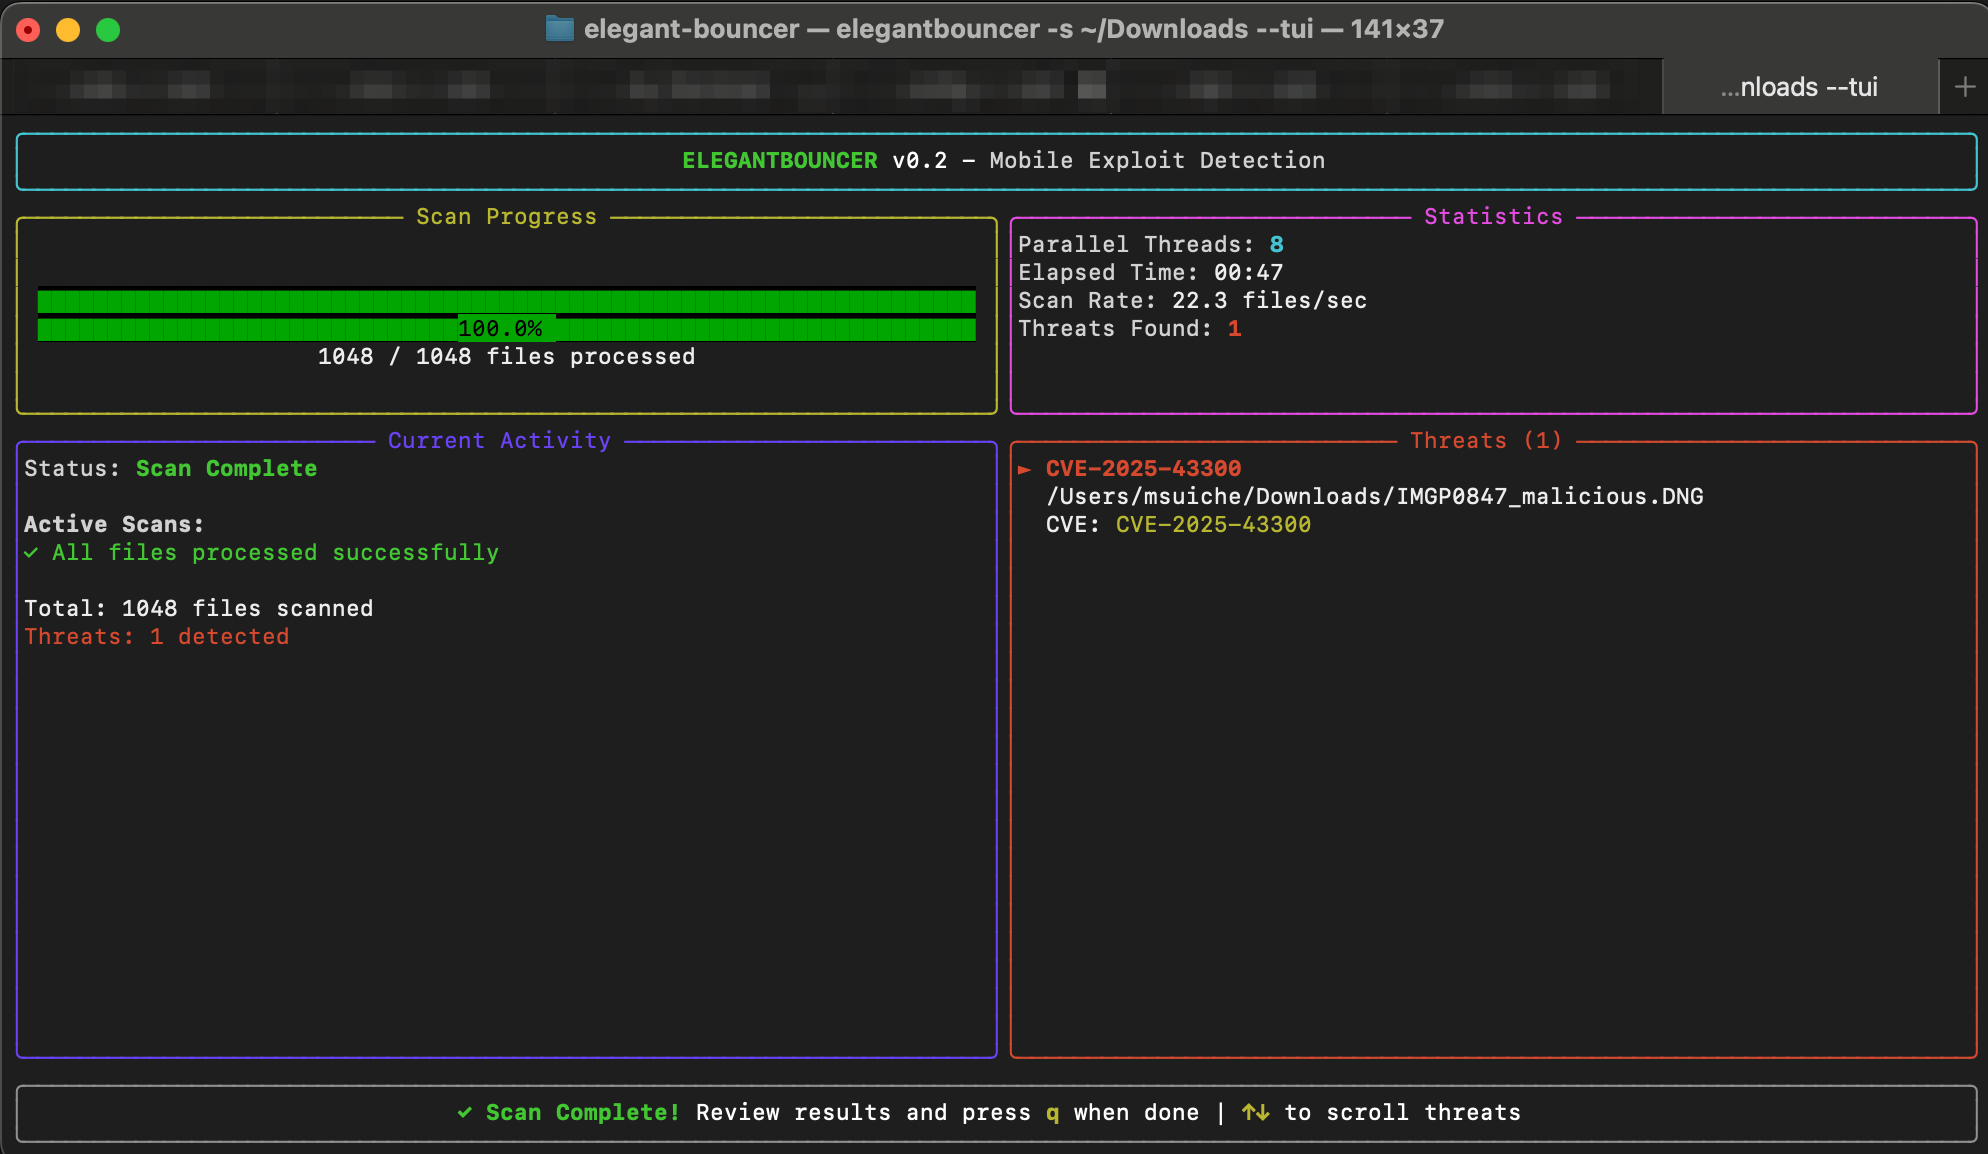
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.

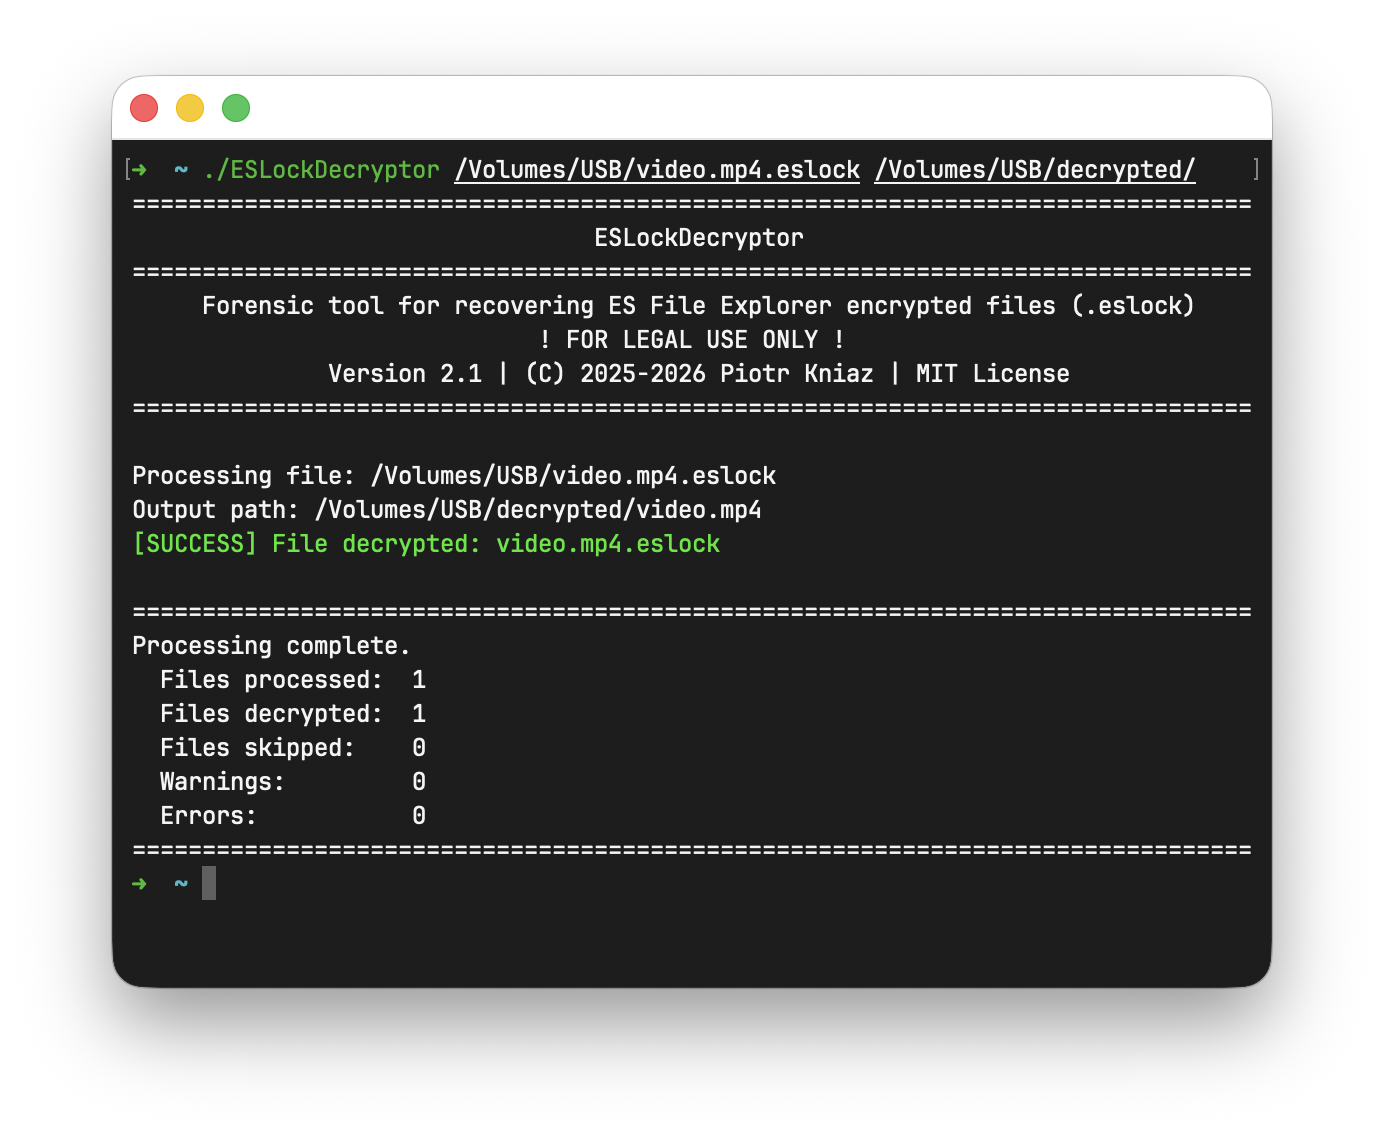
Utility for recovering ES File Explorer encrypted files (.eslock)


Linux Distro for Mobile Security, Malware Analysis, and Forensics


Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.

A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices

iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252