
frida-ios-dump
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
encryption-decryption-toolsios-securitymobile-app-pentesting+4
3.9k
alonemonkey/frida-ios-dumpExtracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

 realitynet/android-forensics-references
Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.
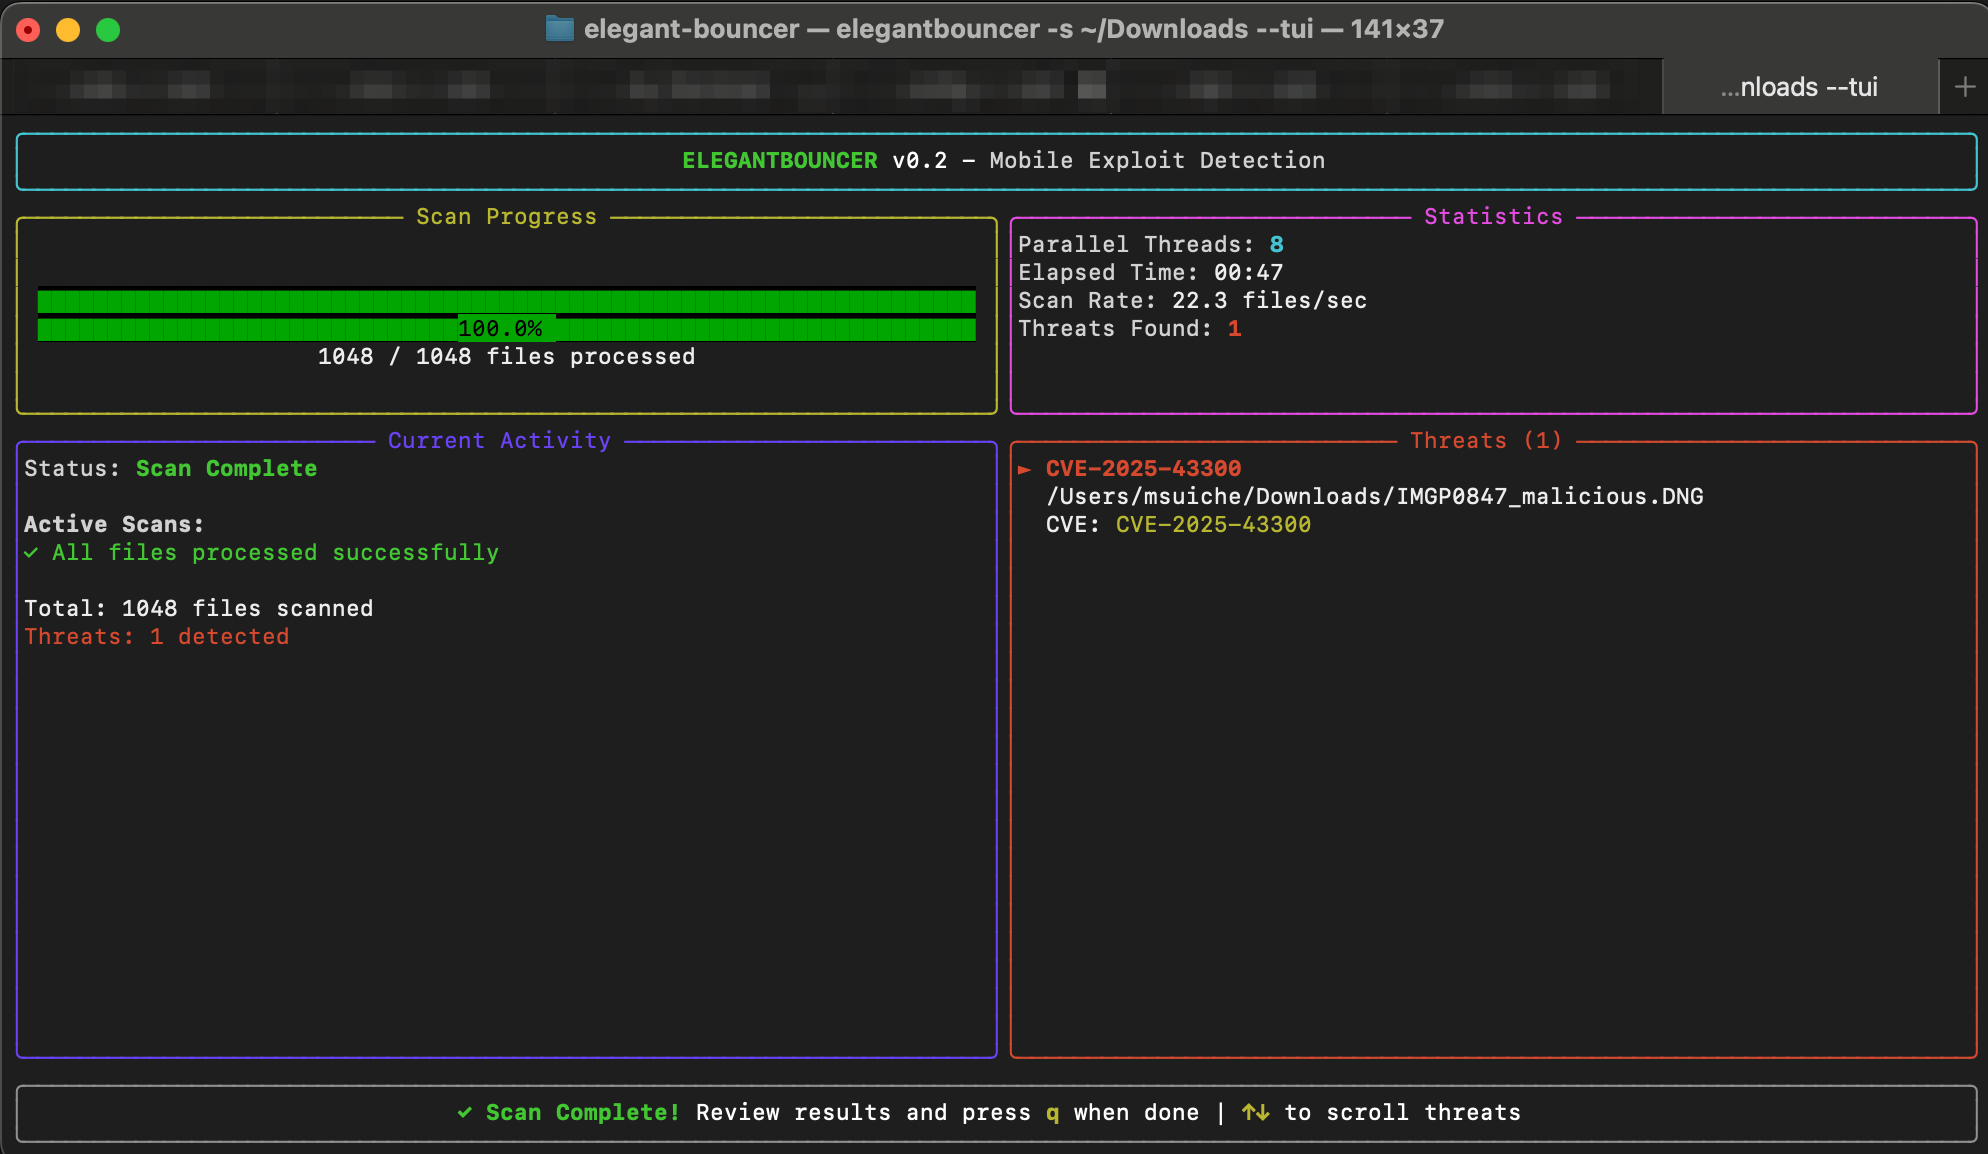 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
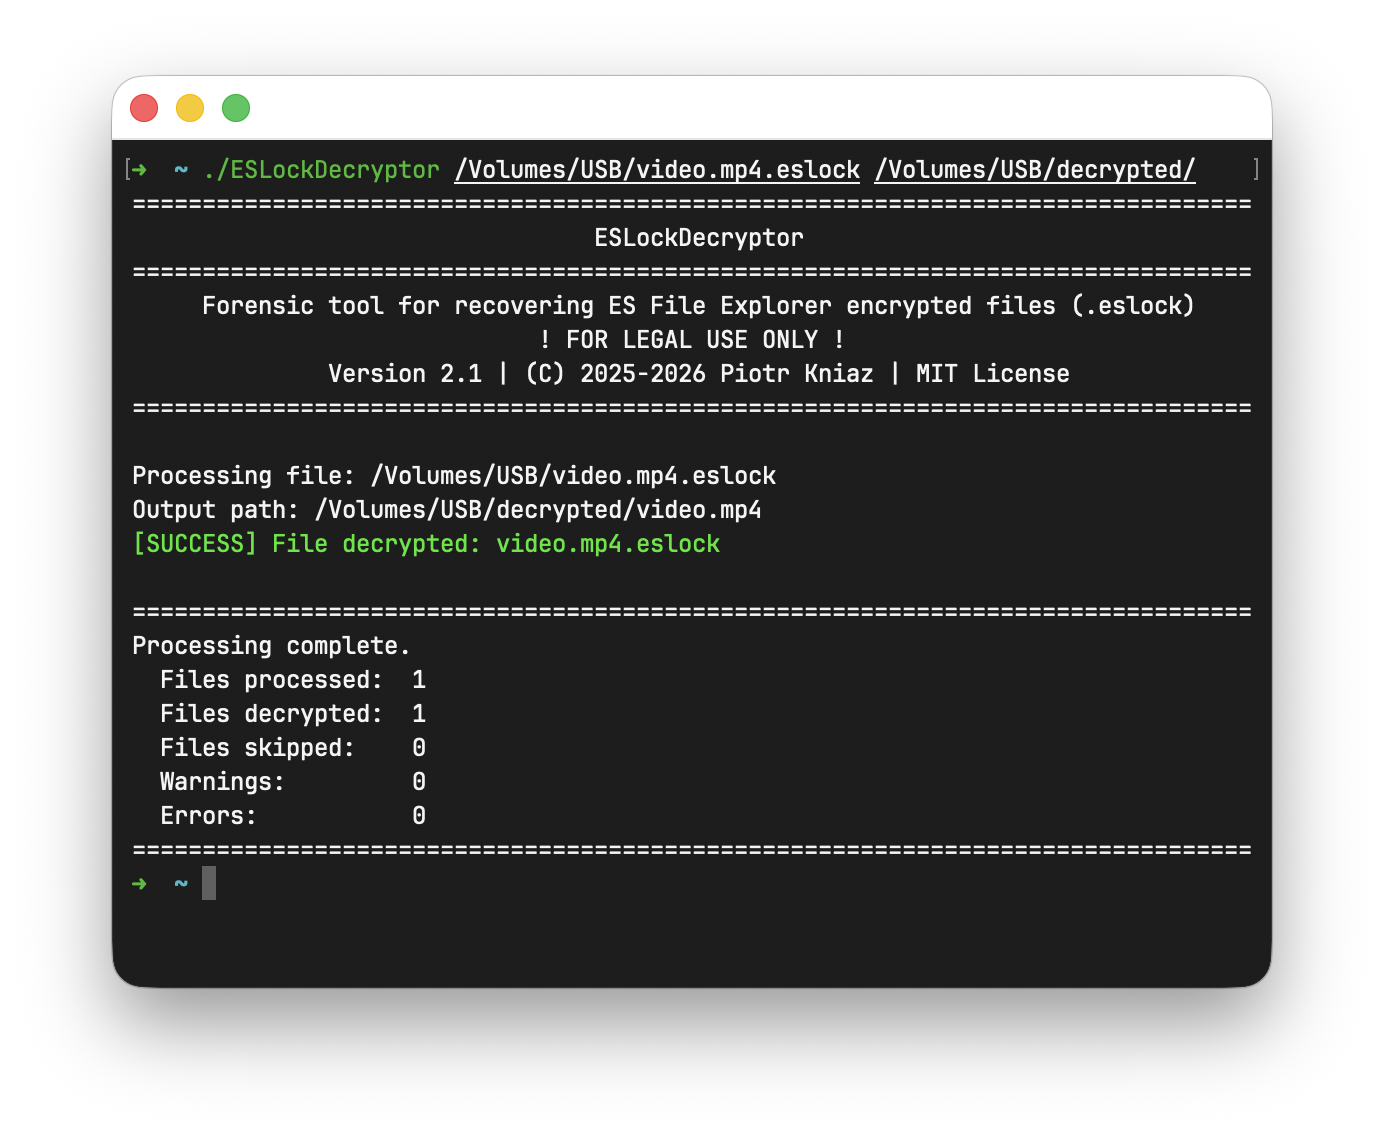 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)

 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
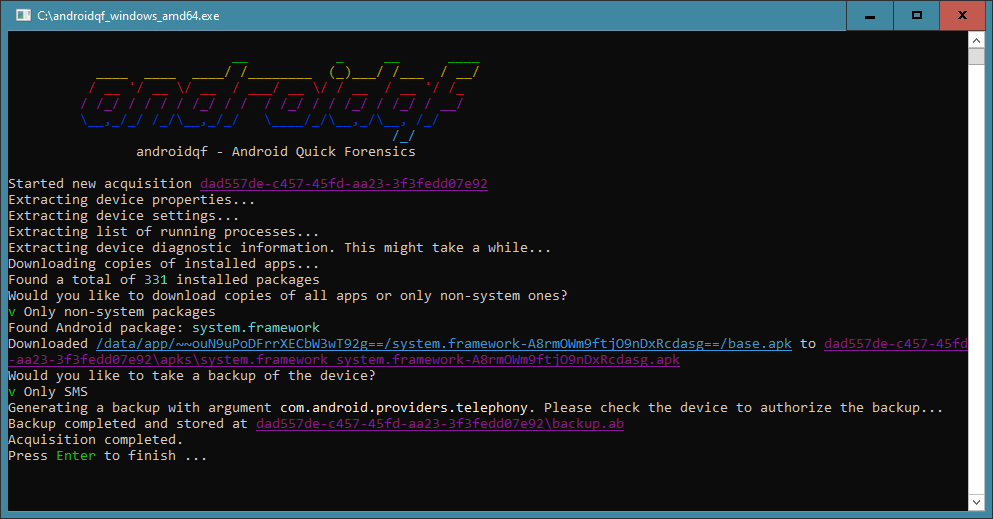 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…