Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

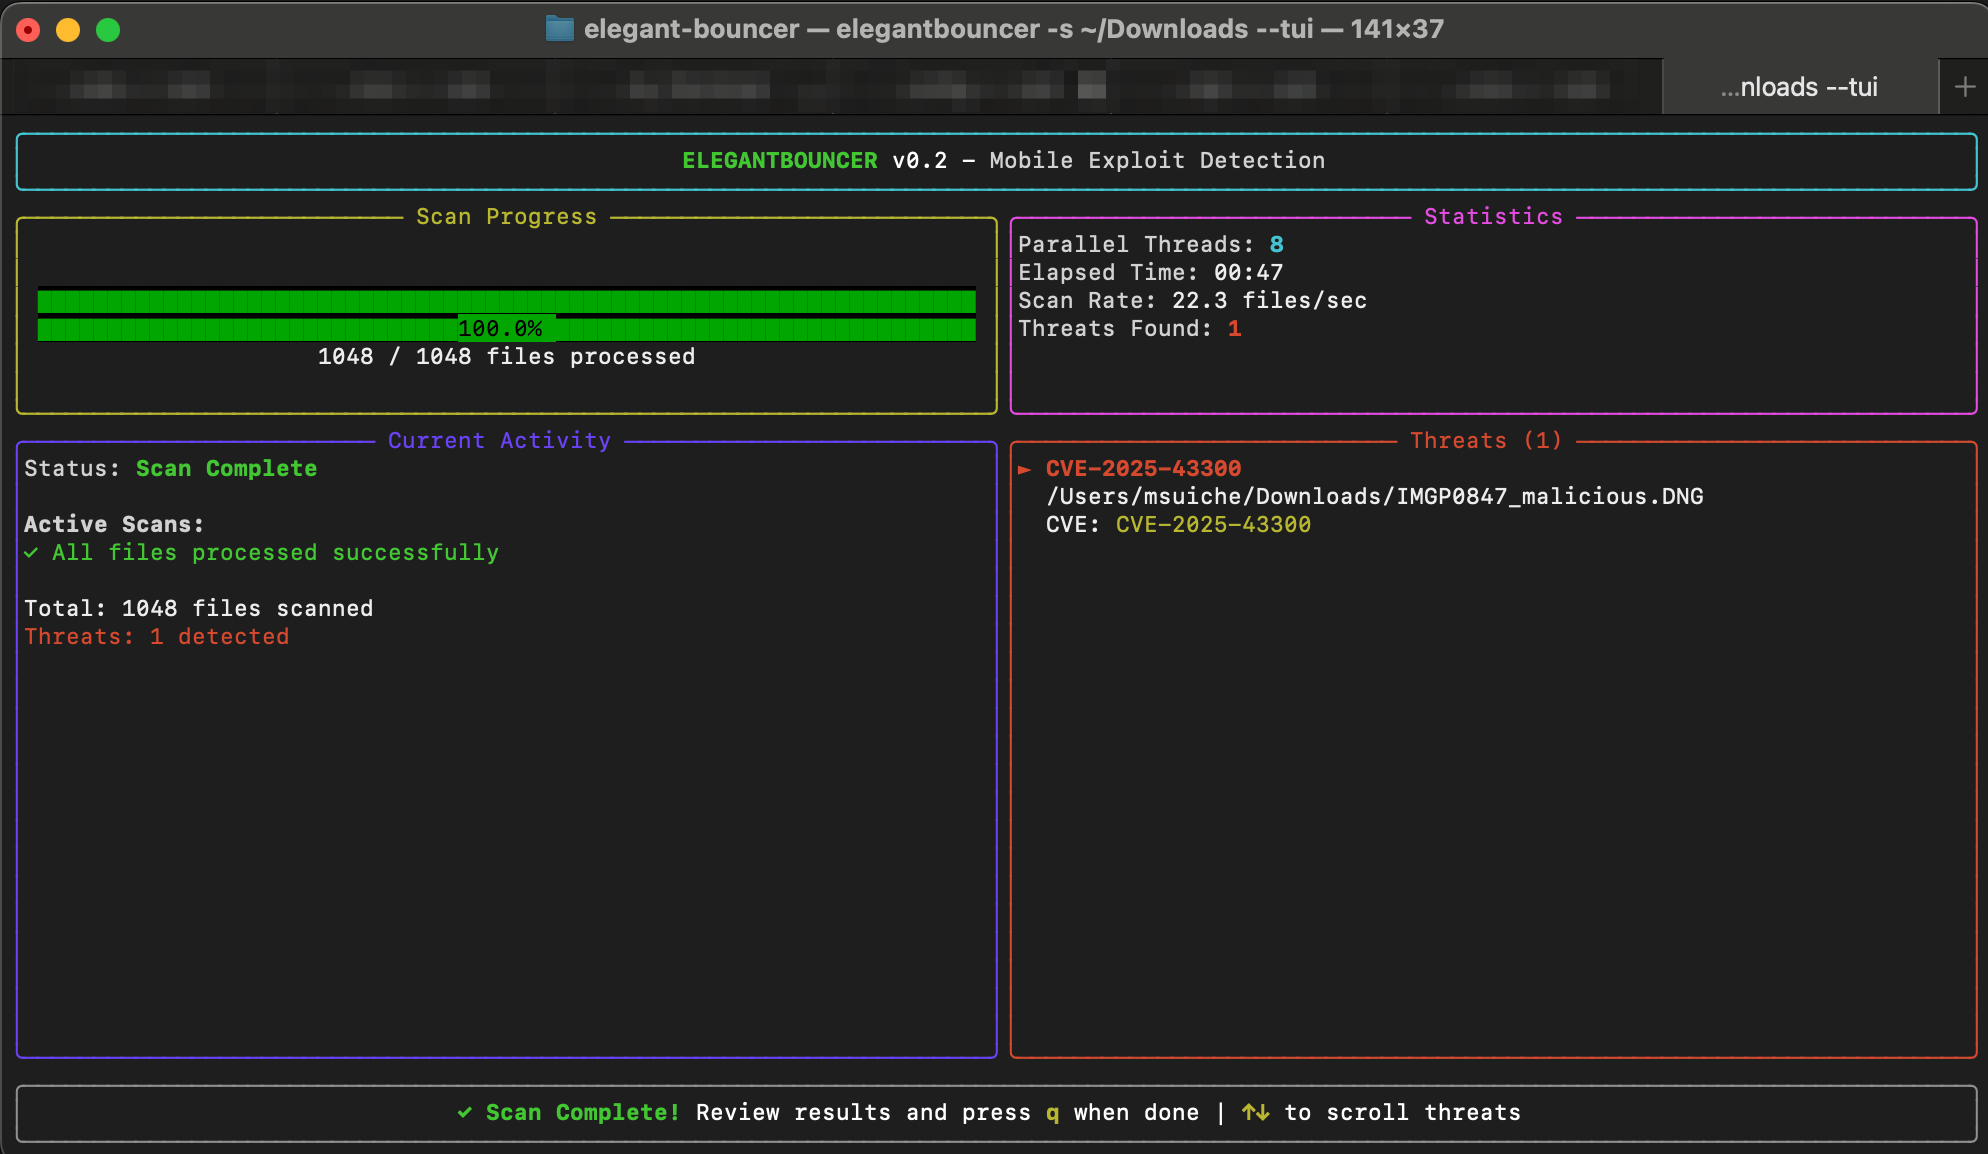
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

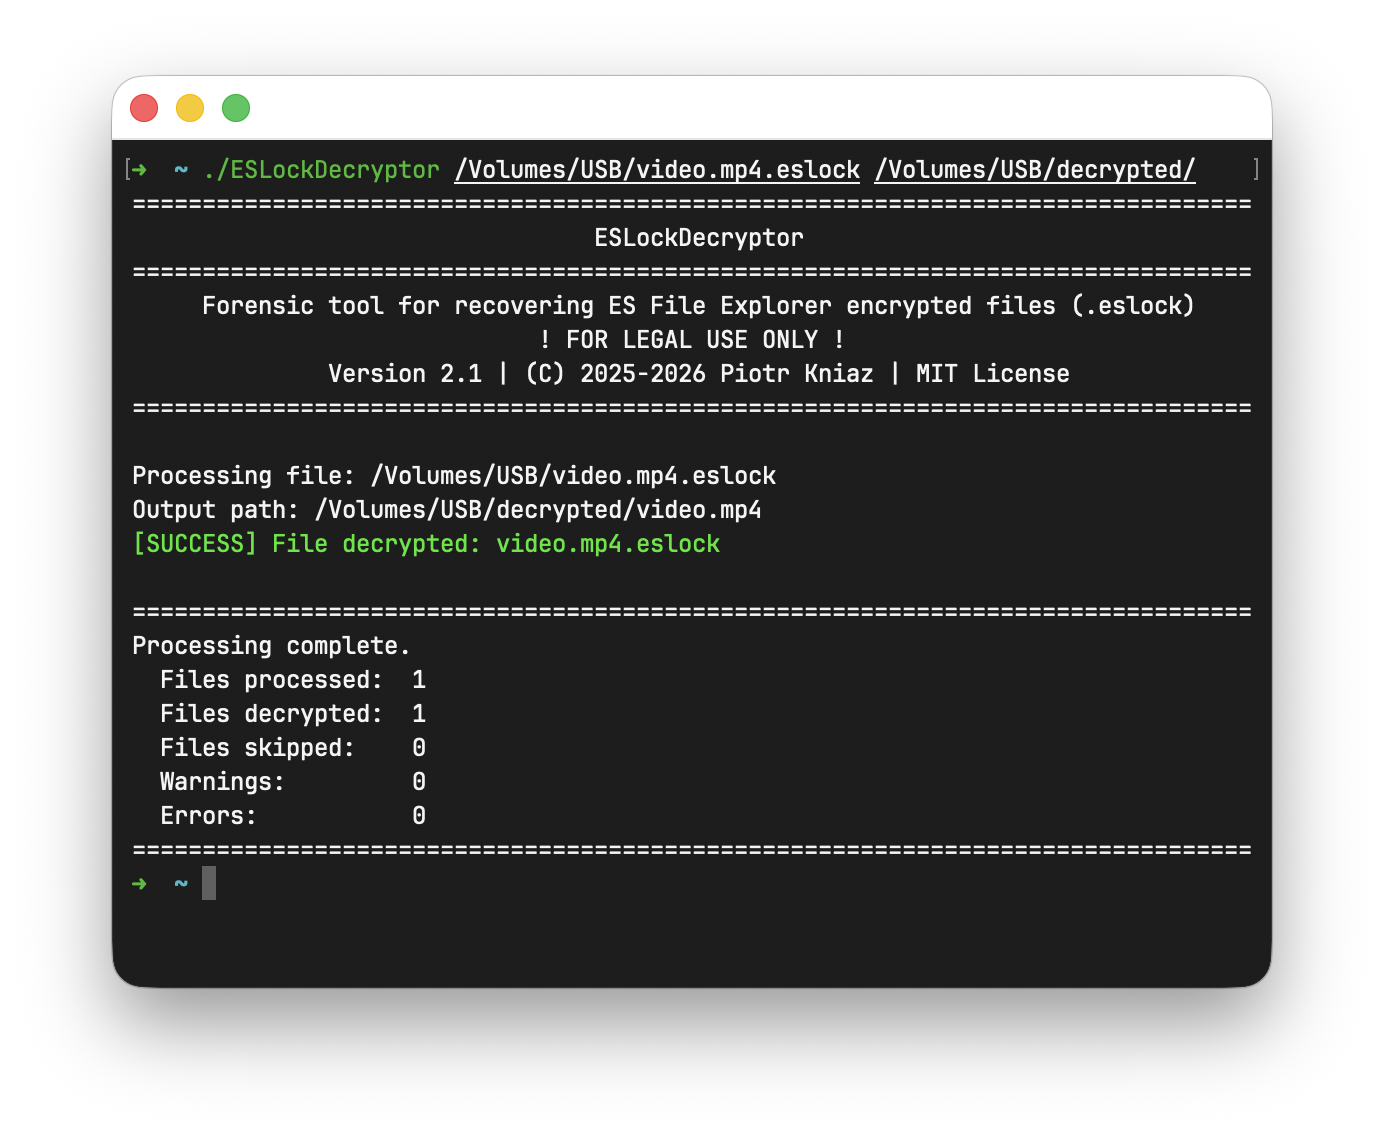
Utility for recovering ES File Explorer encrypted files (.eslock)

This is the development tree. Production downloads are at:


A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices

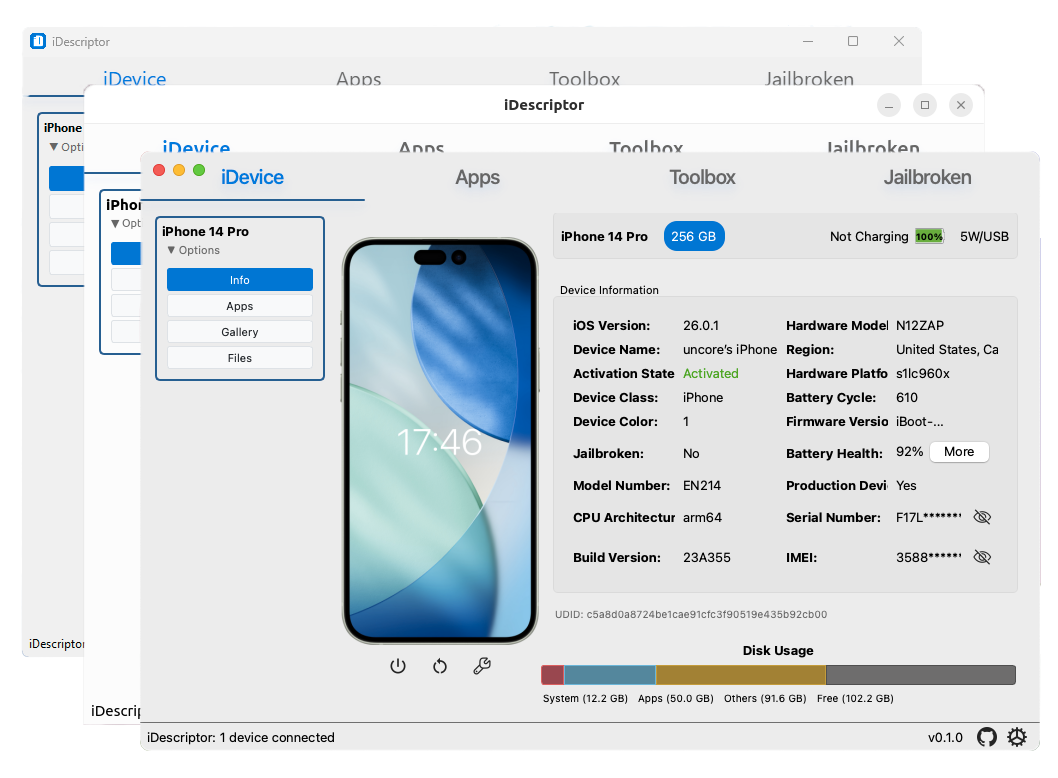
privacy-first, open-source and free idevice management tool written in Rust and Qt

Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.

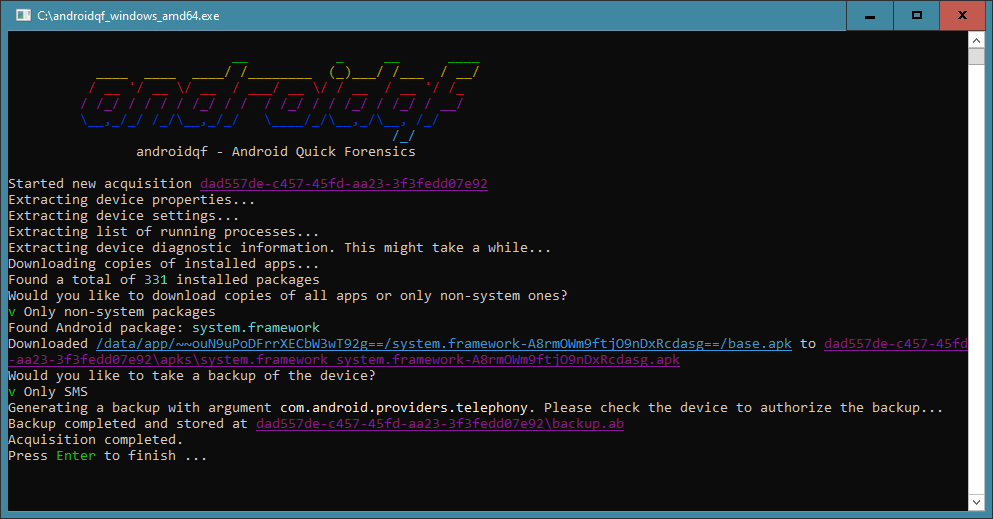
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

A tool for reverse engineering Android apk files

WhatsApp Forensic Tool

Filesystem monitor tool for Linux/Android iOS/macOS